
EnvVisualizer
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
cloud-securityconfiguration-auditingctf+7
1
w4r10ck423/envvisualizerParse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 isaca0315/cve-2026-44578-next-js-ssrf
este laboratorio puede estar bien o mal esta el pruebas pero debe funcionar preguntale a la IA hahah
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
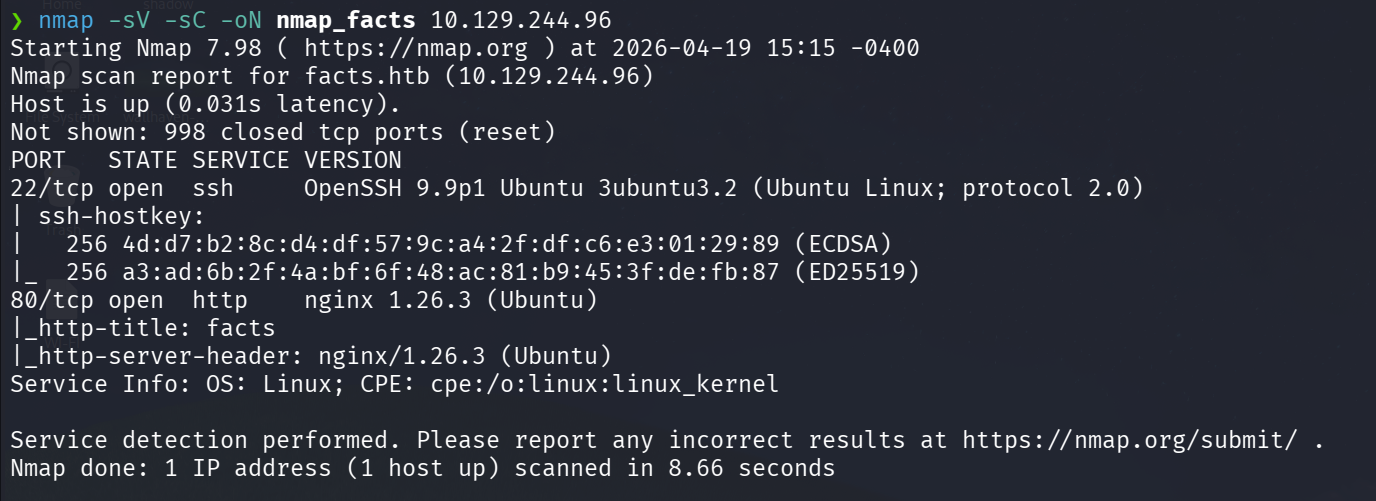 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 farhanashrafdev/90daysofcybersecurity
Structured 90-day cybersecurity study plan with daily tasks covering Network+, Security+, Linux, Python, traffic analysis, cloud security, and…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 threatradarai/trai-001-critical-rce-vulnerability-in-apache-parquet-cve-2025-30065-simulation
A CVSS 10.0-rated vulnerability in the parquet-avro Java module allows remote code execution via unsafe deserialization when parsing schemas. Tracked…