

f8x
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
cloud-securityctfdevsecops+7
ffffffff0x/f8x红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.

 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 eurogig/jankybank
Simple Java Front and Back end with bad log4j version featuring CVE-2021-44228
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 jwsly12/cve-2025-66034-htb-ctf
Exploit for VariaType HTB machine leveraging XML injection in fontTools to achieve RCE via PHP reverse shell payload in .designspace metadata.
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
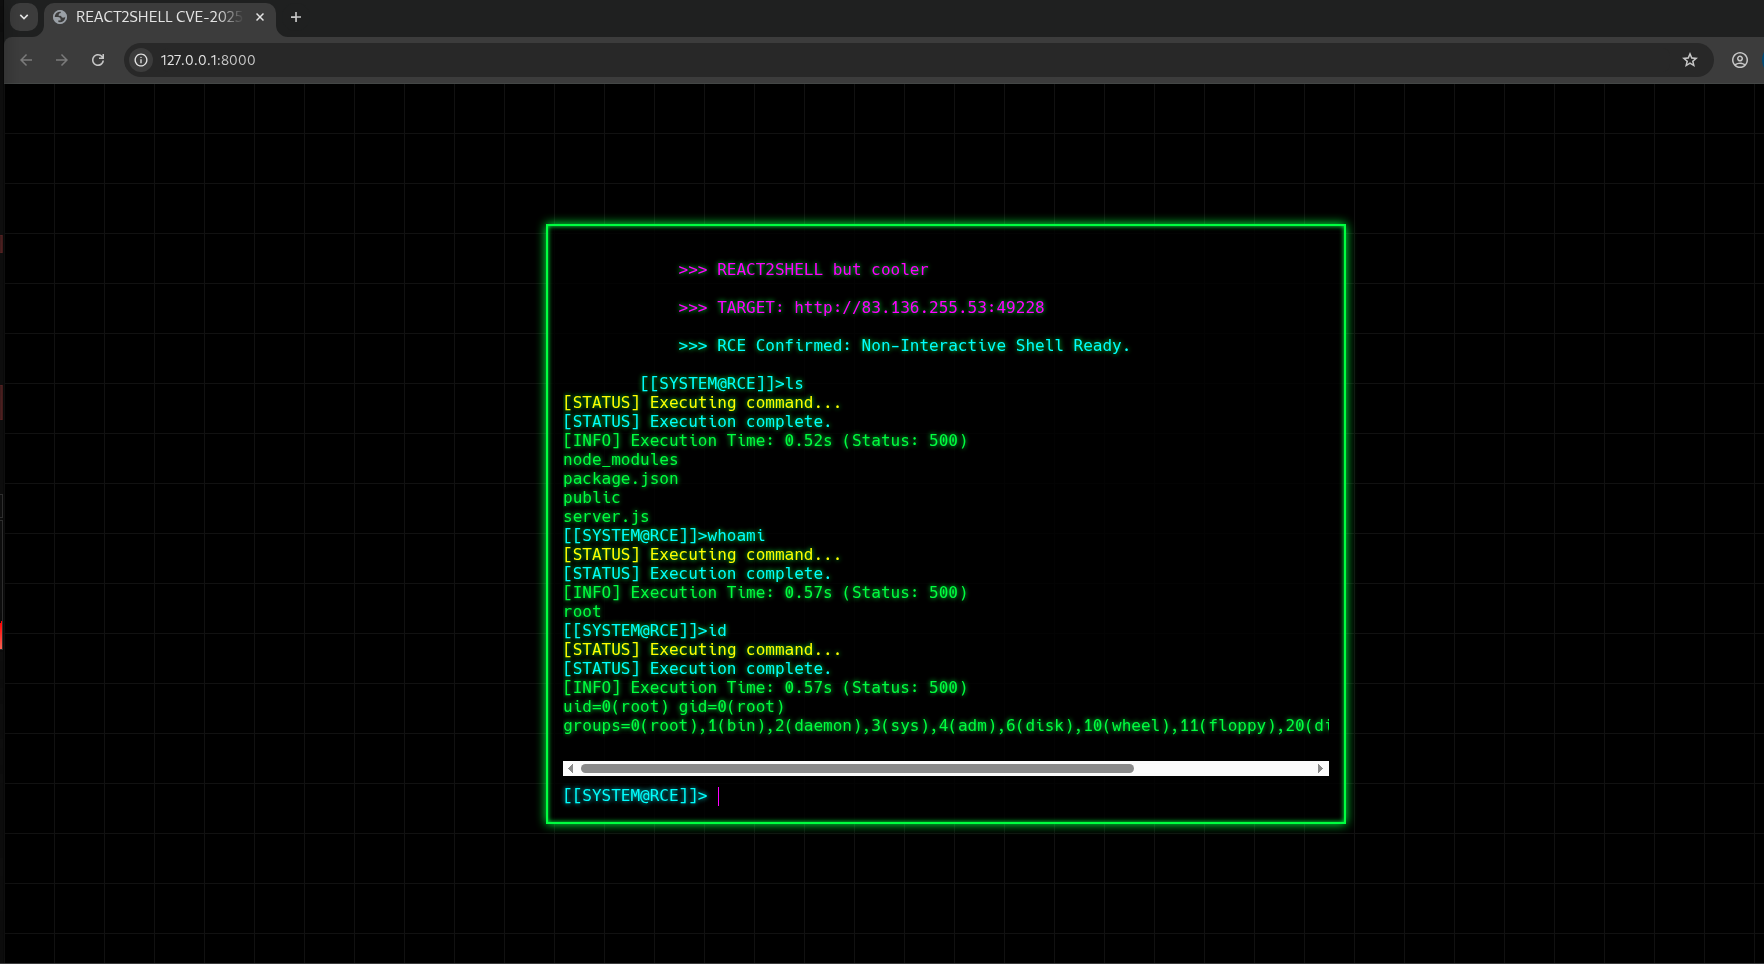 raivenlockdown/web-cli_rce_react2shell
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…