
GoFileX
 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
ctfinformation-gatheringpassword-attacks+5
abraxas/gofilexWordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
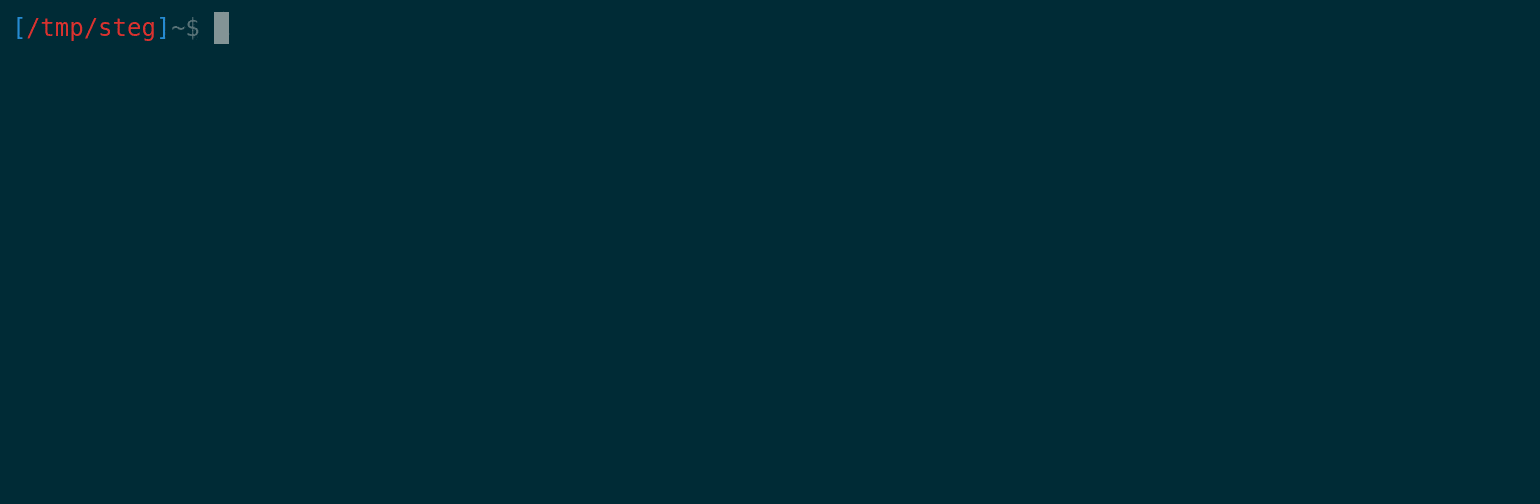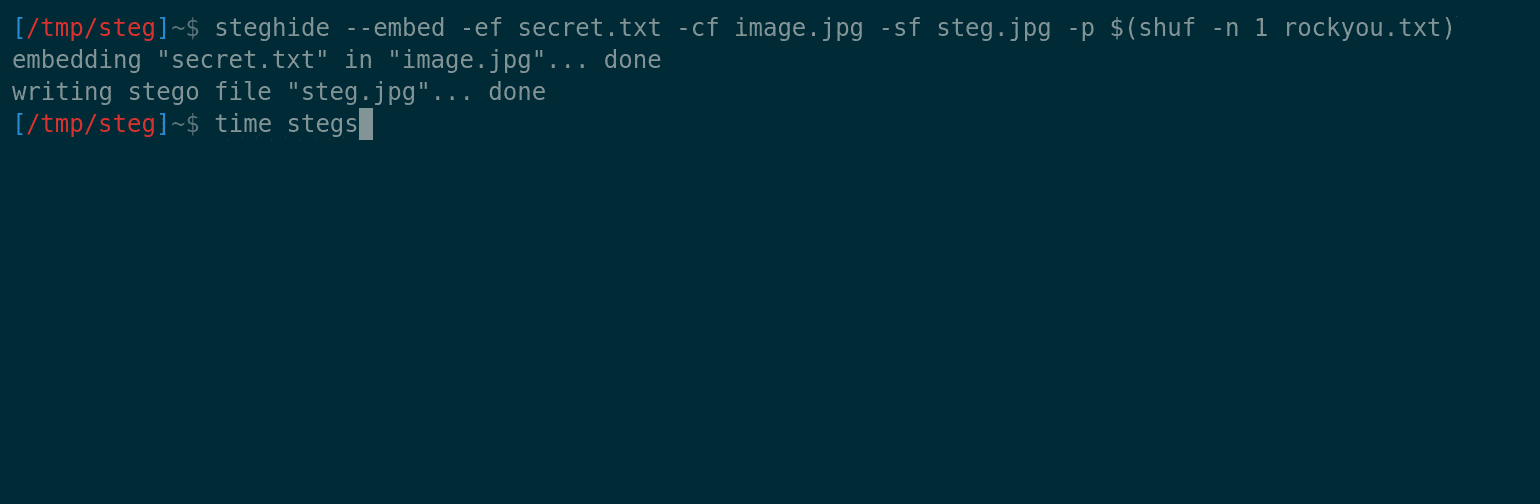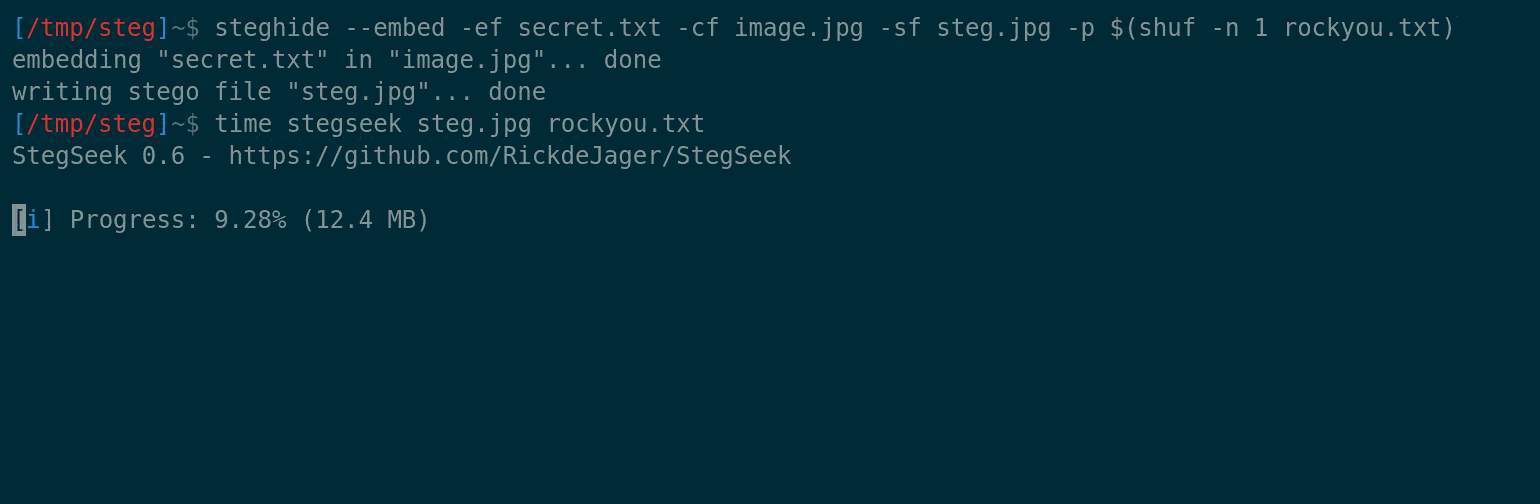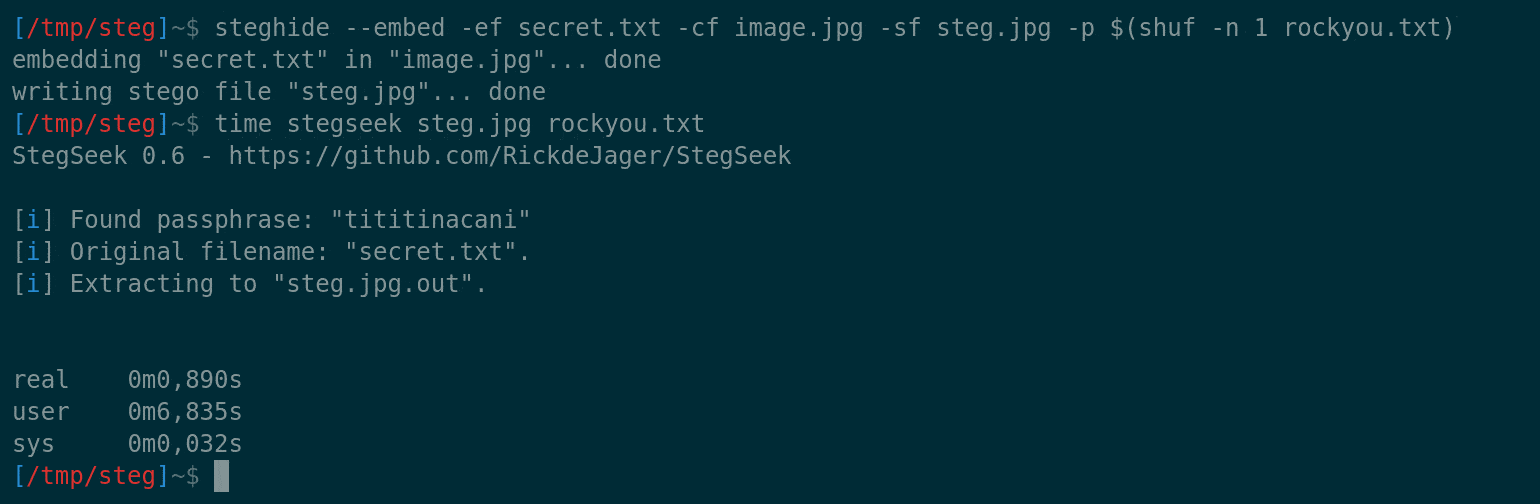 rickdejager/stegseek
:zap: Worlds fastest steghide cracker, chewing through millions of passwords per second :zap:
 r4ygm/stegbrute
Fast Steganography bruteforce tool written in Rust useful for CTF's
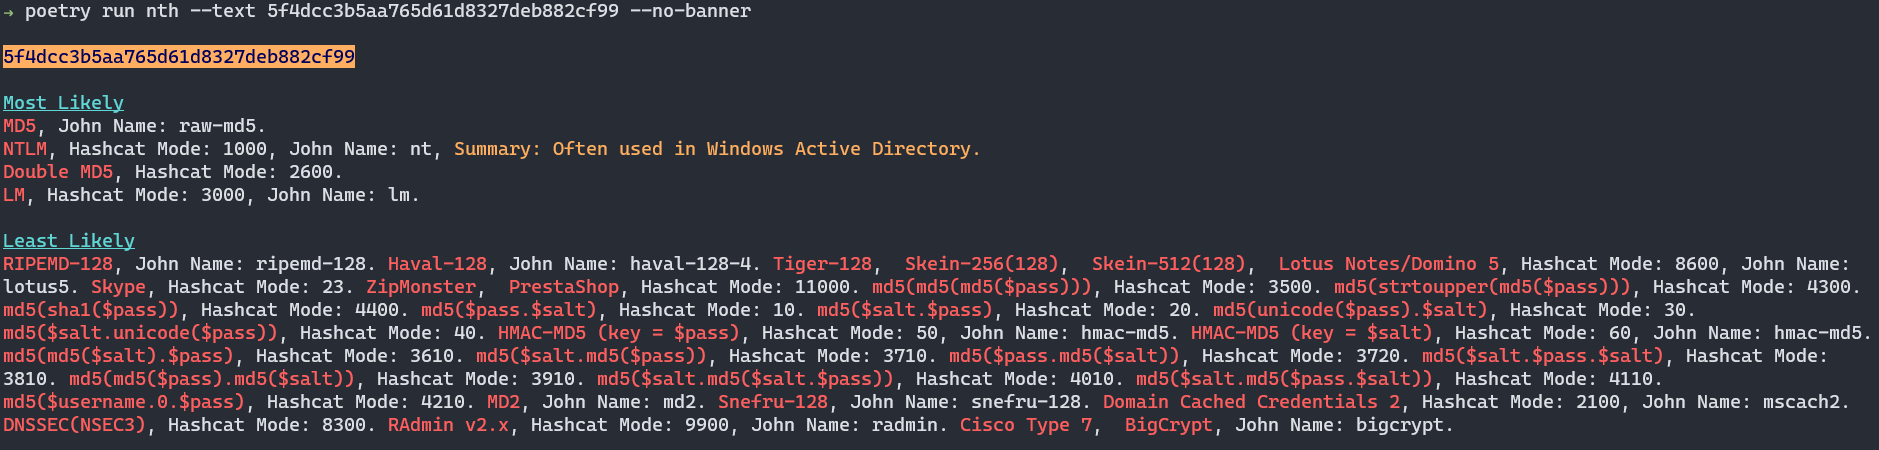 bee-san/name-that-hash
Identify 300+ hash types instantly via CLI or web app. Prioritizes popular hashes, provides summaries, and integrates with HashCat and John the…
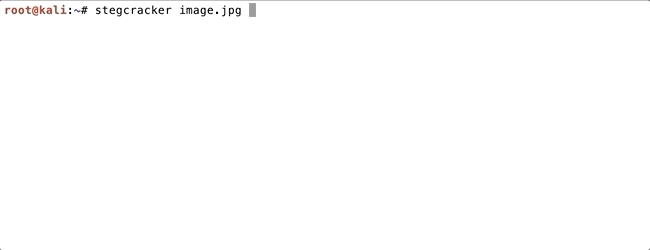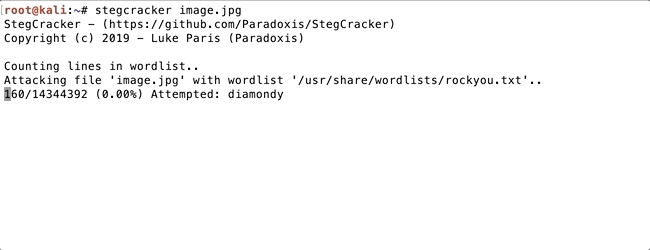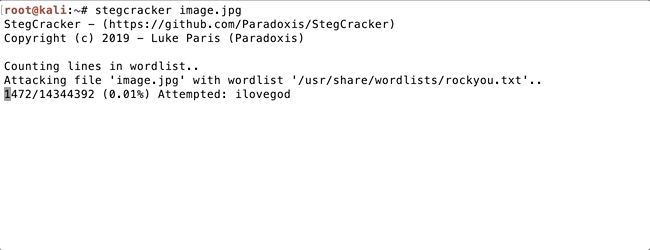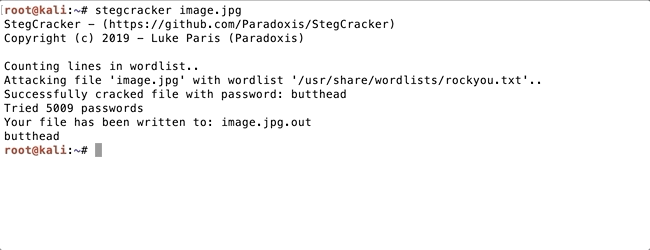 paradoxis/stegcracker
Steganography brute-force utility to uncover hidden data inside files
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
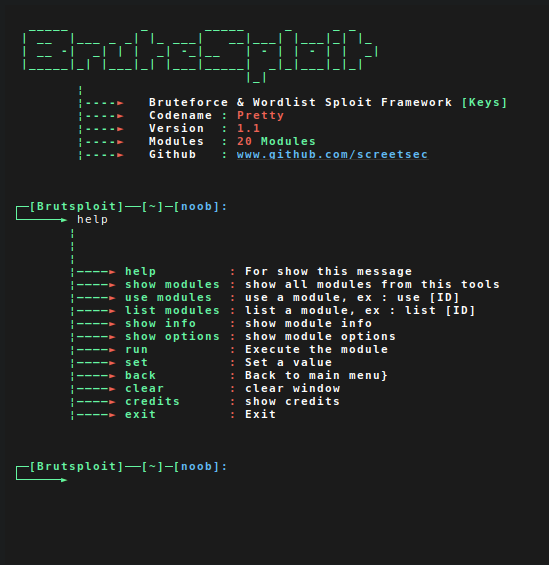 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 k4m4/dcipher-cli
🔓Crack hashes using online rainbow & lookup table attack services, right from your terminal.
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
 k4m4/dcipher
Decipher hashes using online rainbow & lookup table attack services.
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 m0d0ri205/wargame-turkey_in_2
CTF wargame platform featuring Unicode bypass exploitation (CVE-2015-9238), flag file segmentation, brute force delay, and password hashing for…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 sabbu143s/cve_2020_35848
CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…