spectrIDA-Reverse_Engineering_Stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…

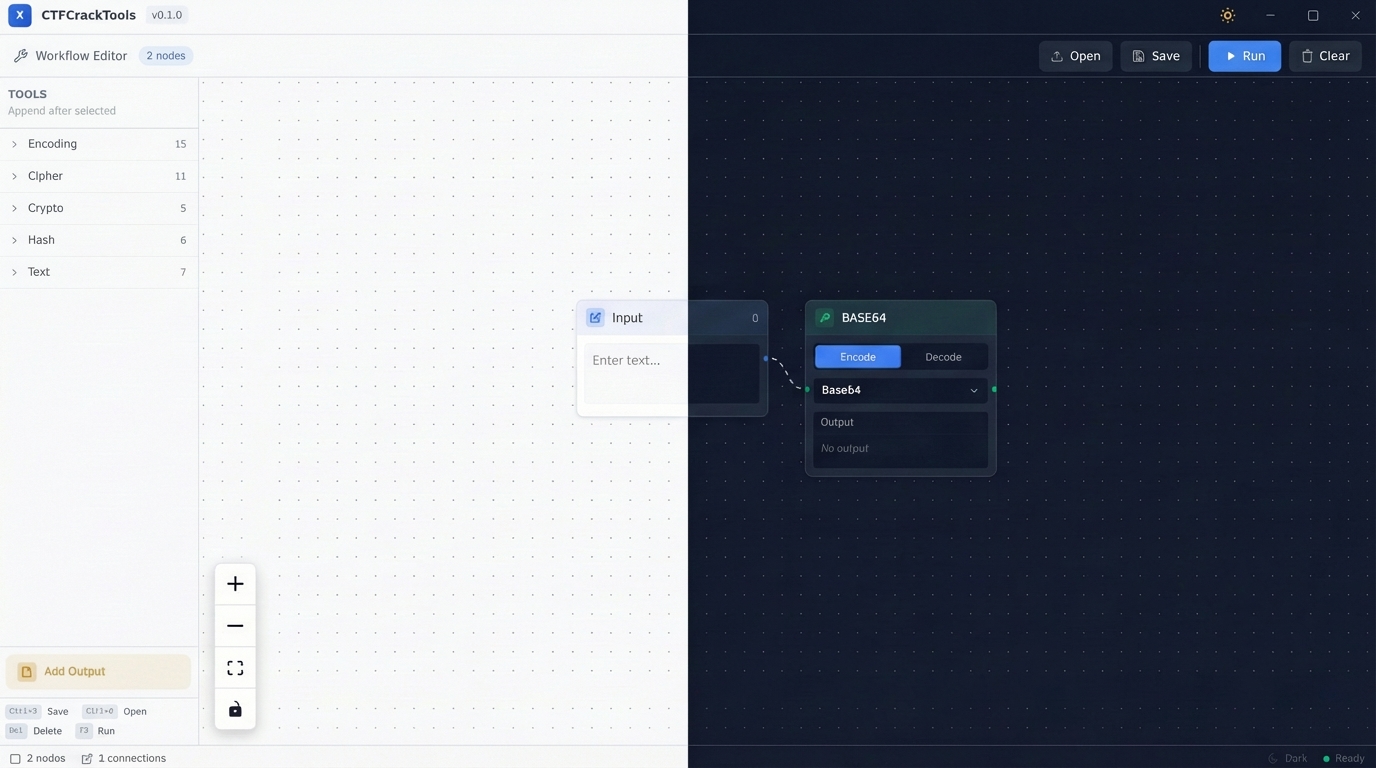
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…

KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…

TryHackMe Dirty Frag (CVE-2026-43284) — Linux LPE writeup

Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…

Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…

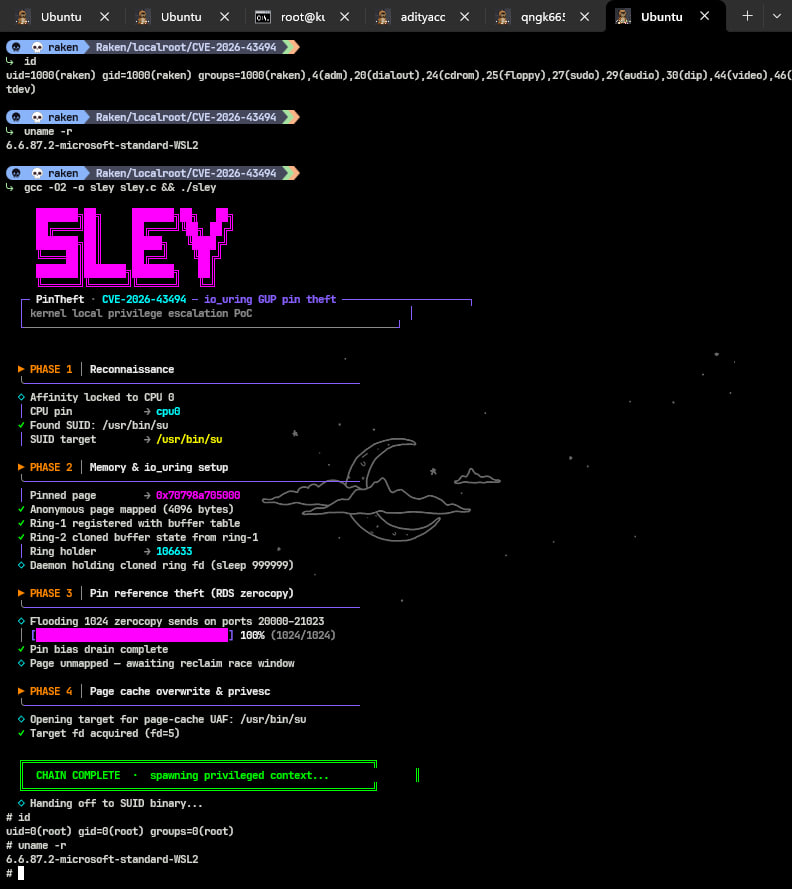
Proof-of-concept for CVE-2026-43494 (PinTheft): Linux kernel local privilege escalation exploiting an RDS zerocopy reference-count bug with io_uring…

Educational case study and exploit development walkthrough for CVE-2022-0185, a Linux kernel heap-based buffer overflow enabling local privilege…

CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab

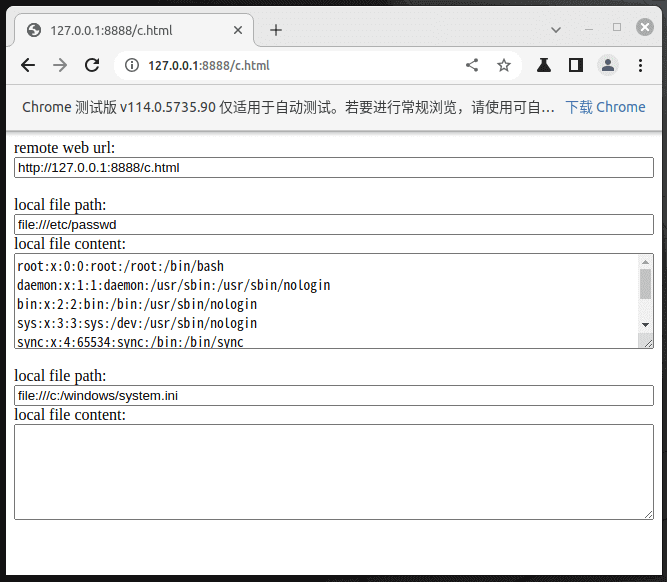
[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.

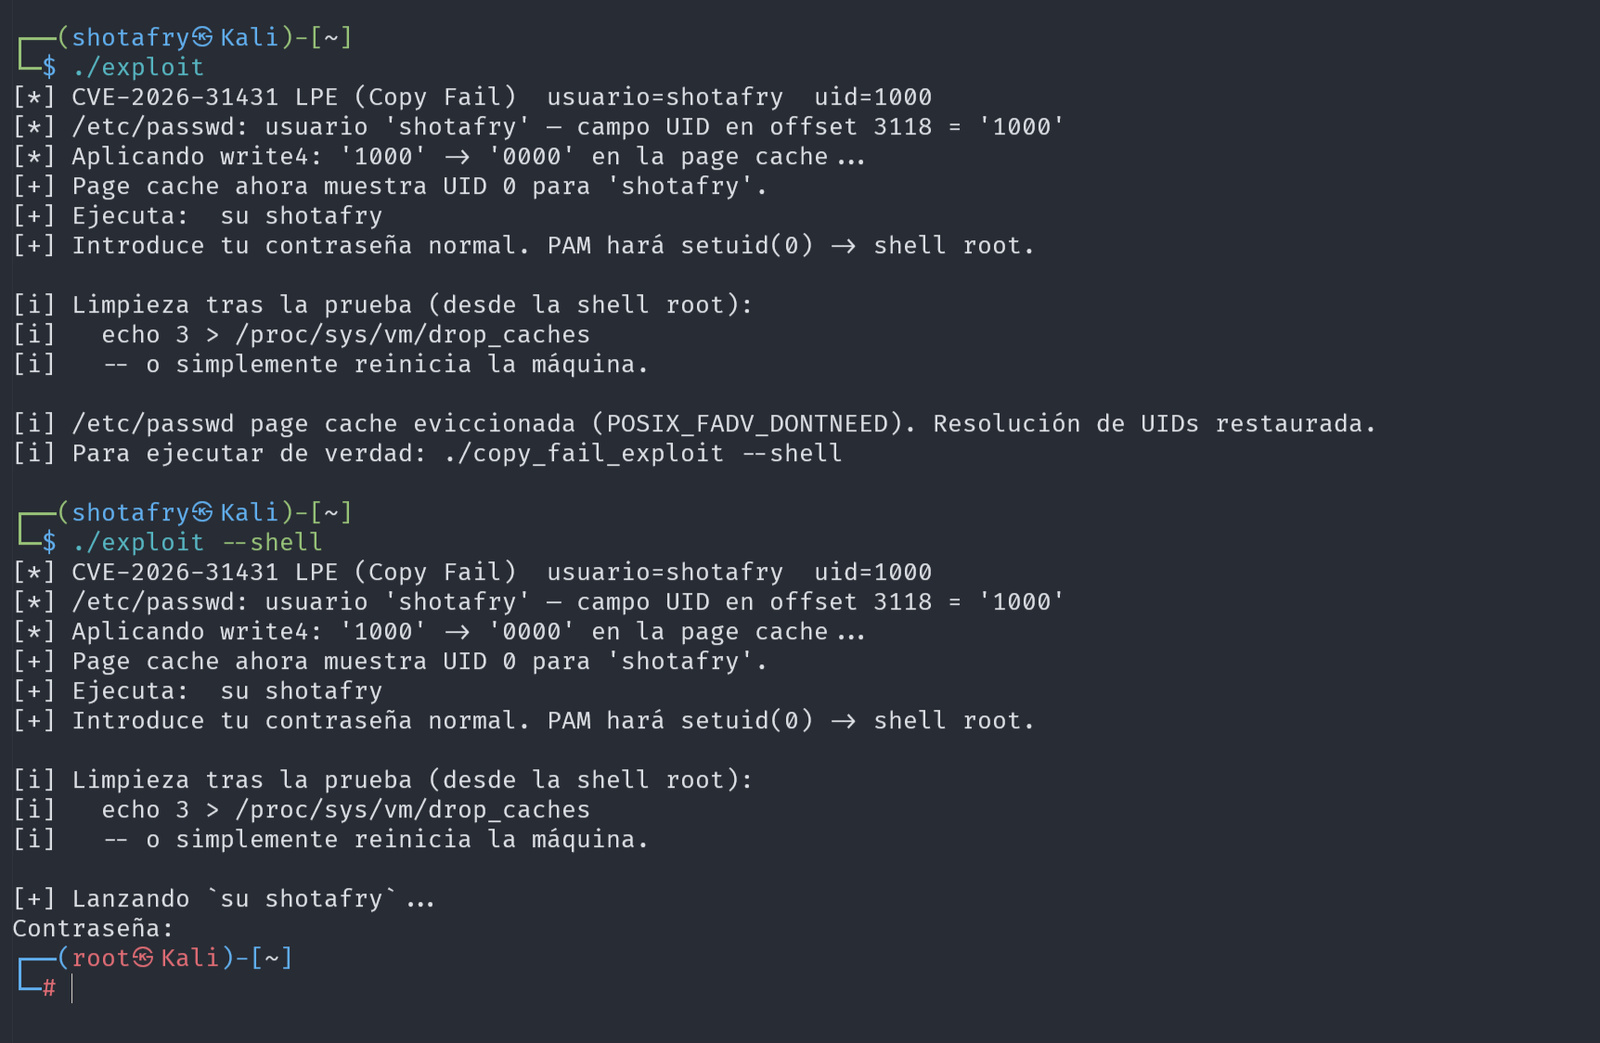
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…

Educational PoC and analysis of CVE-2021-4034 (PwnKit) local privilege escalation vulnerability in polkit's pkexec, with a Docker-based lab for…

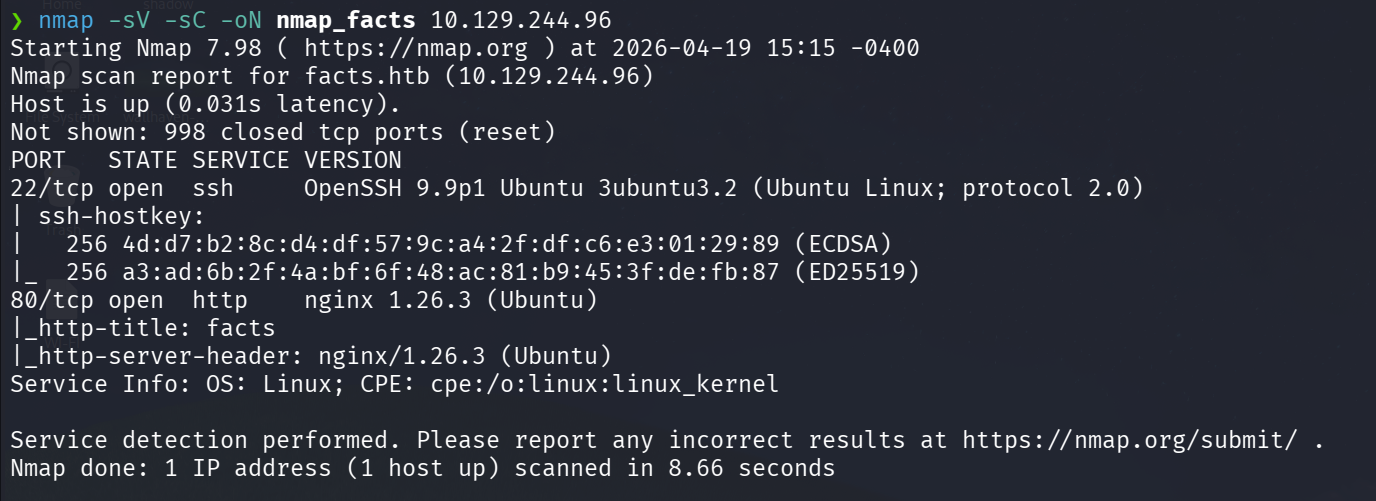
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc

Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…

Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…

Linux kernel TLS subsystem exploit for CVE-2024-58239, achieving privilege escalation via a double-free vulnerability in tcp_rcv_state_process.…