
 apsdehal/awesome-ctf
A curated list of CTF frameworks, libraries, resources and softwares
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
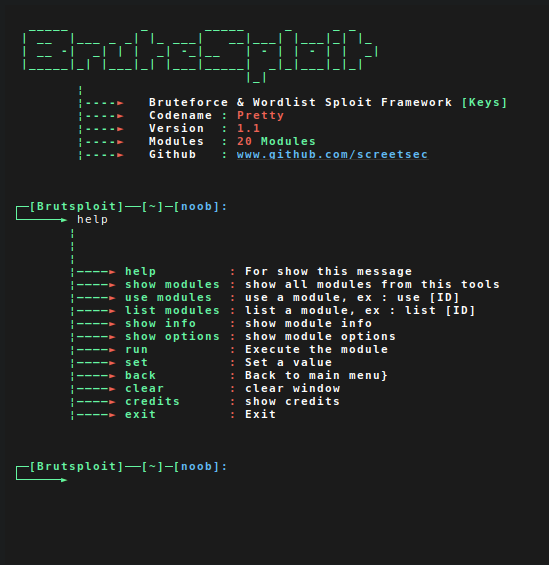 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 juice-shop/multi-juicer
Host and manage multiple Juice Shop instances for security trainings and Capture The Flags
 crixpwn/cve-2026-8389
Technical analysis and proof-of-concept exploit for CVE-2026-8389, a SpiderMonkey BaselineJIT type confusion vulnerability in Firefox, demonstrated…
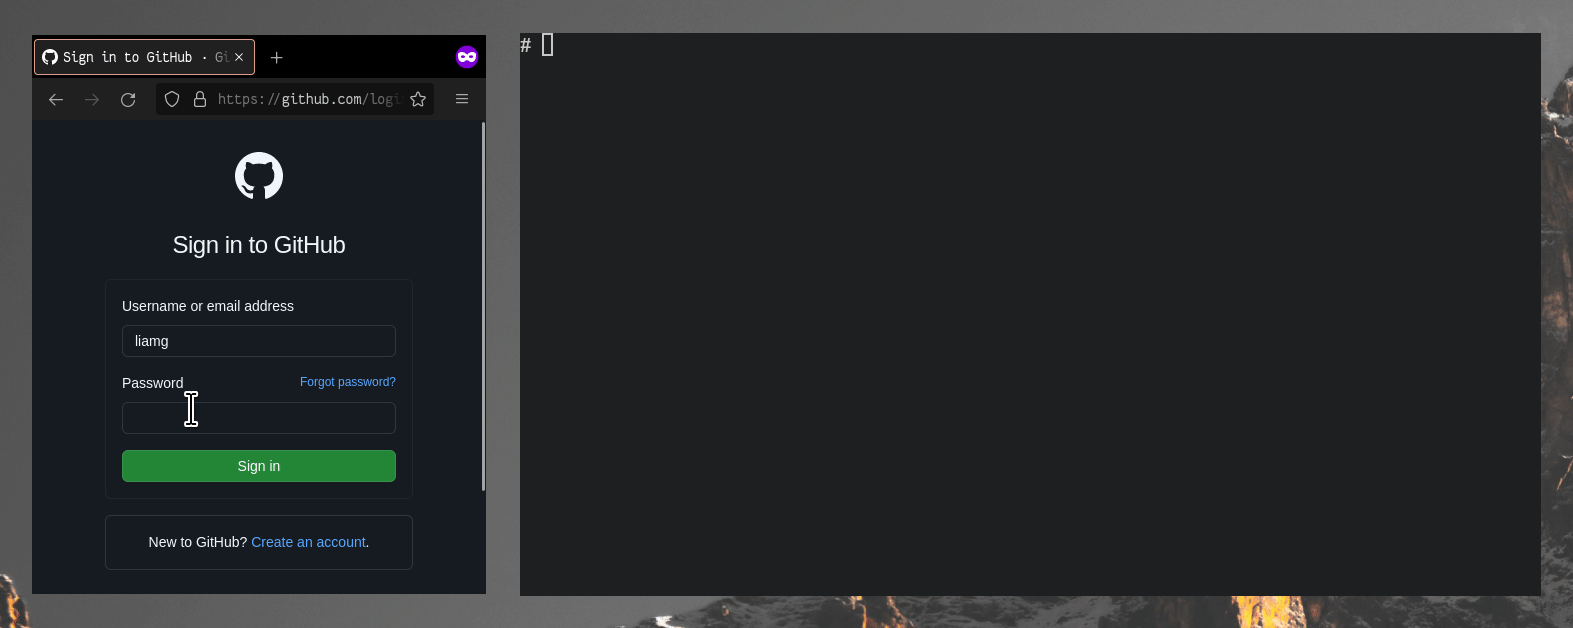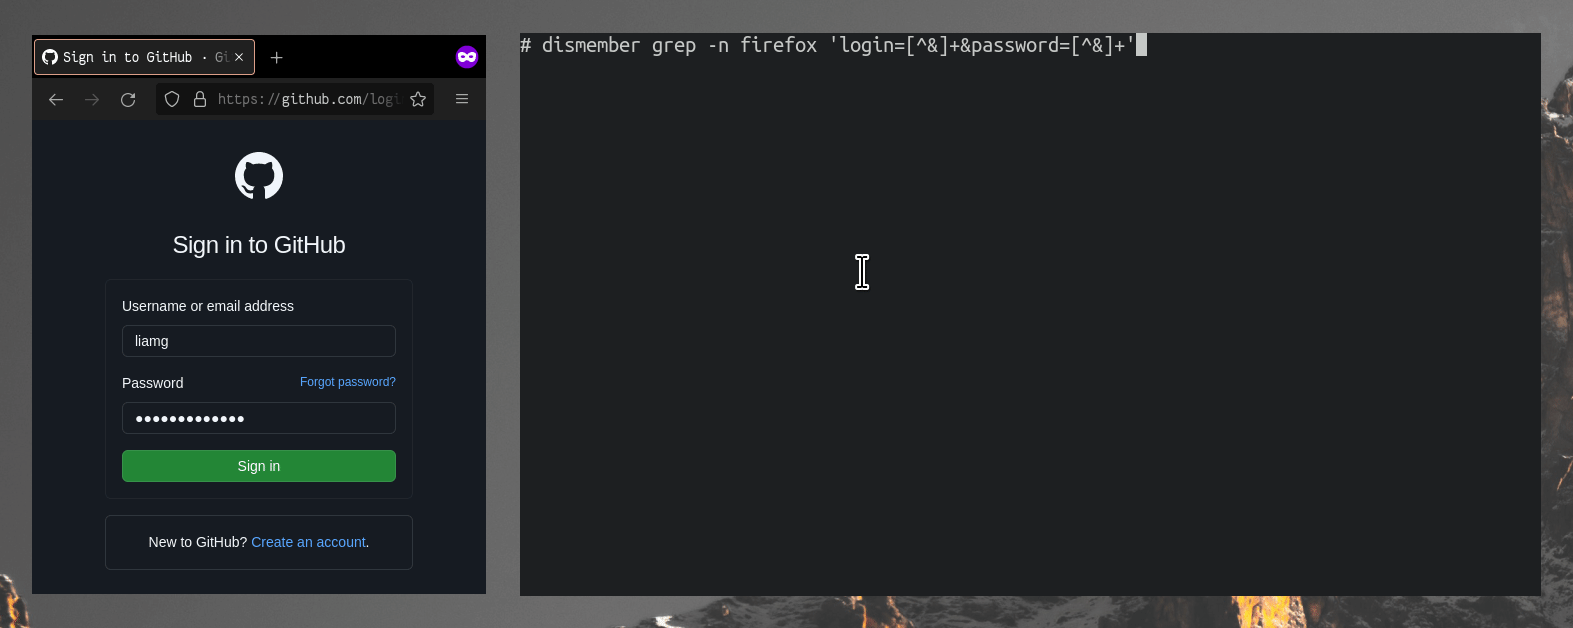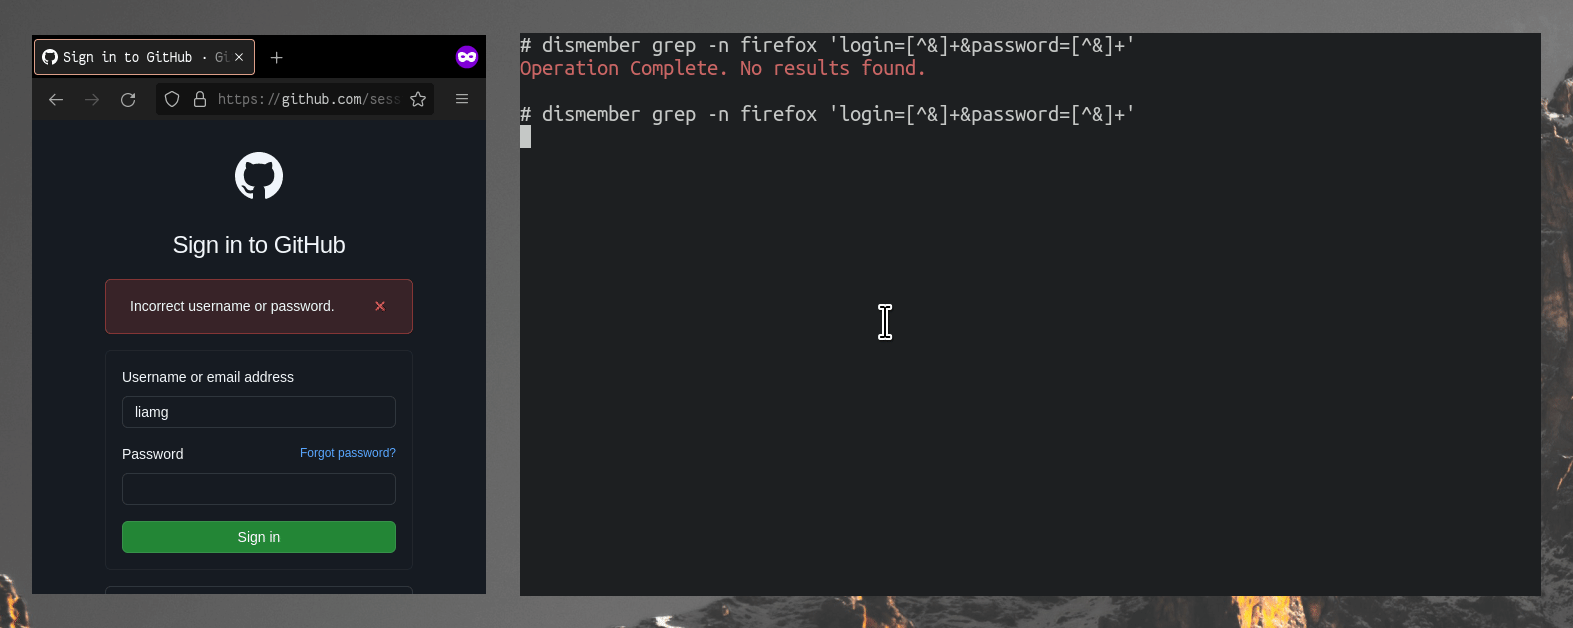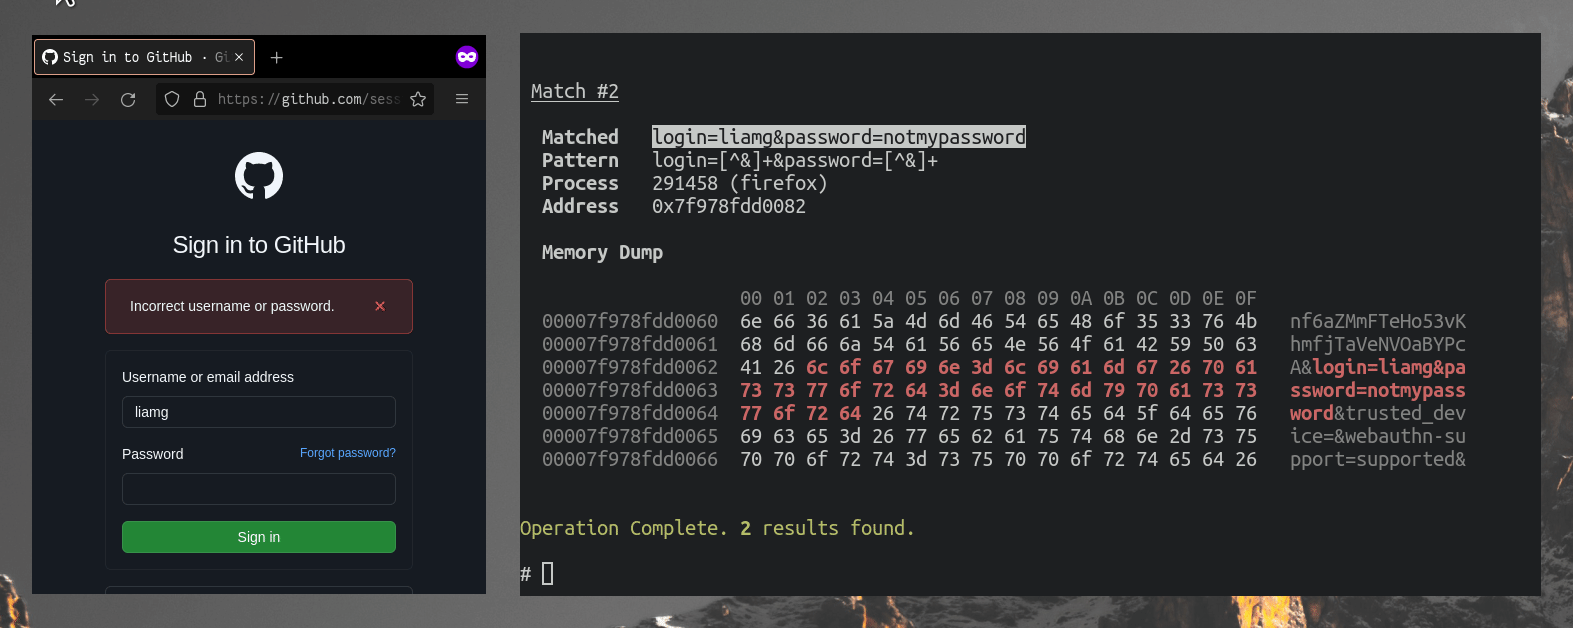 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.
 kaxm23/rust-cve-2025-55182-scanner
powerfull rust cve-2025-55182-scanner used for ctf & ethical purpose only
 diego-altf4/pwnctftool
Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…
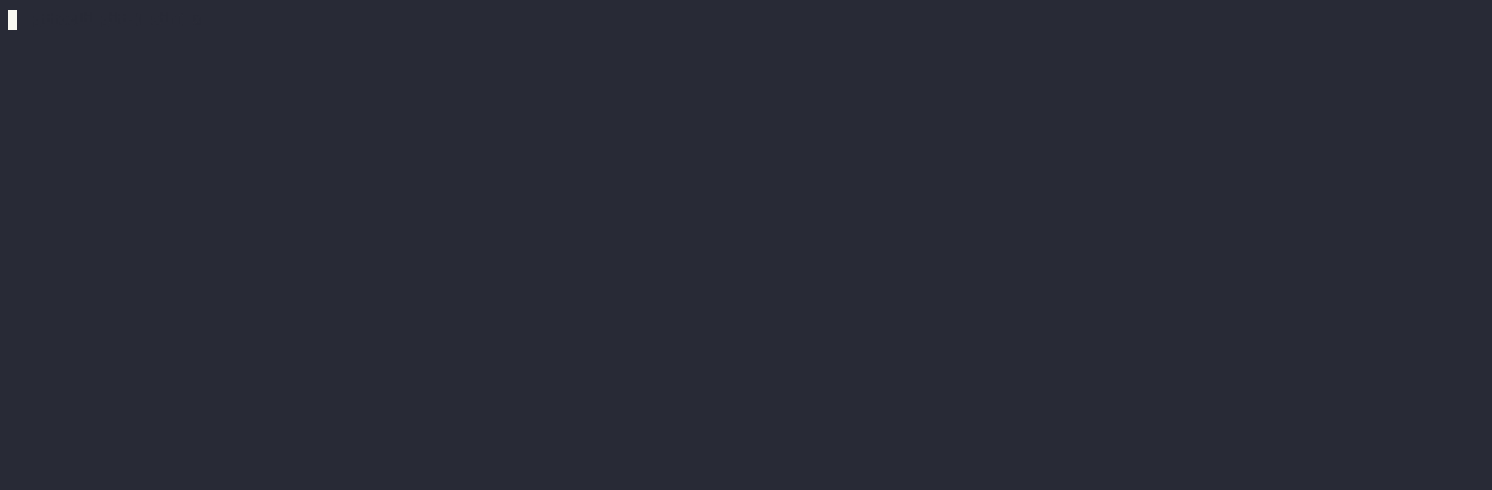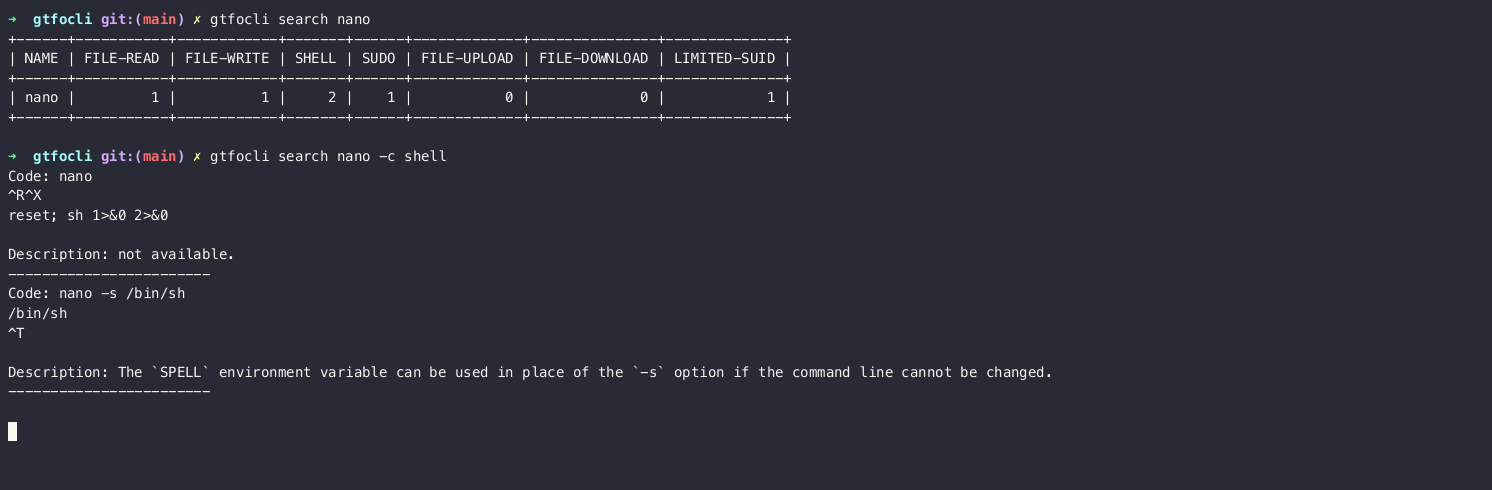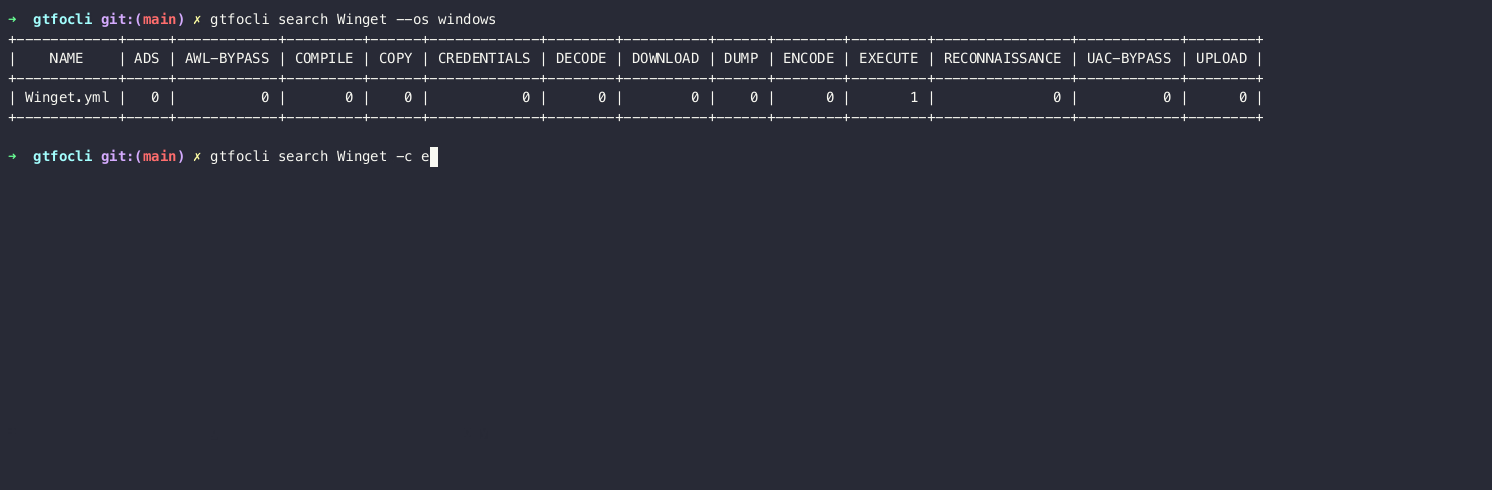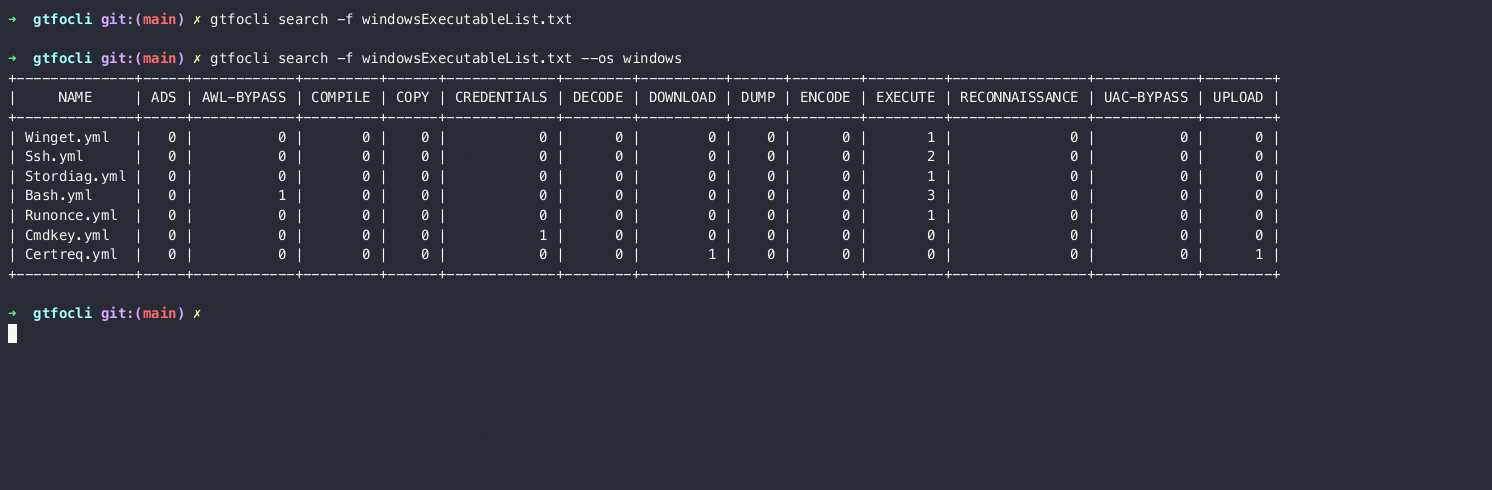 cmd-tools/gtfocli
GTFO Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.
 natteesetobol/cve-2018-15133-lavel-expliot
"Lavel Exploit CVE-2018-15133 is a powerful exploit that allows attackers to gain unauthorized access to vulnerable systems. This exploit was…
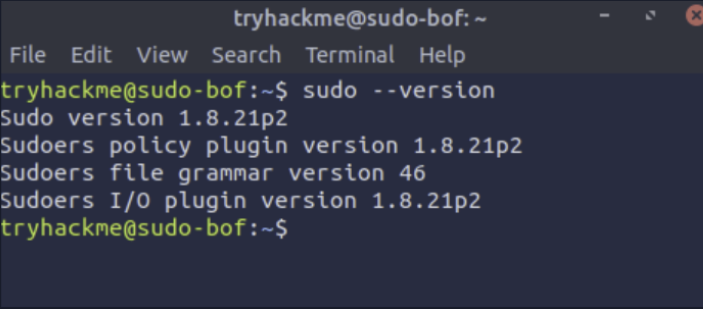 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits