
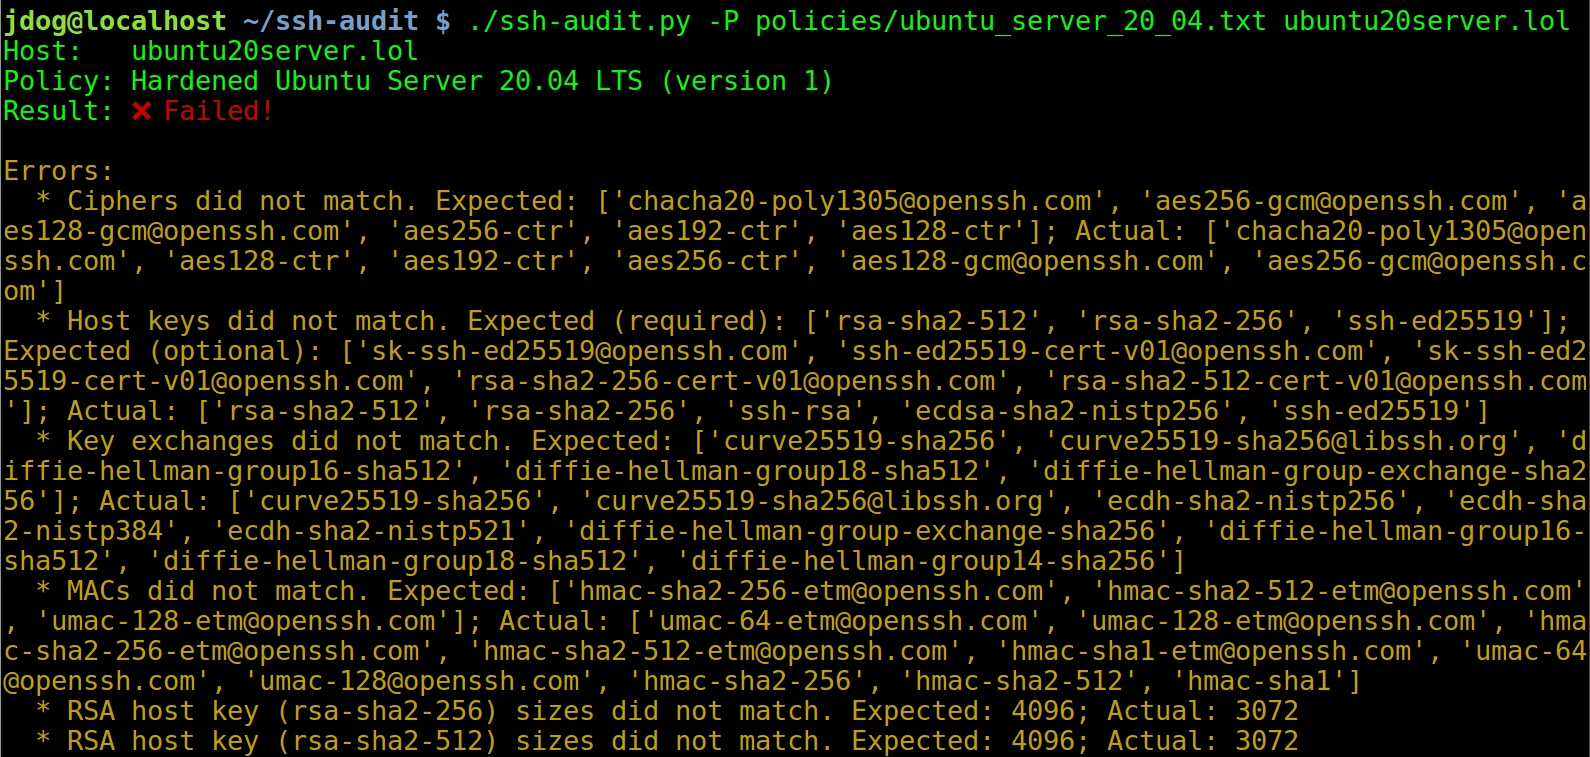
ssh-audit
 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
configuration-auditingcryptographyinformation-gathering+6
4.3k
jtesta/ssh-auditSSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 dnsviz/dnsviz
Analyzes DNS delegation and DNSSEC security by probing resolvers and authoritative servers, then validating, diagnosing, and visualizing zone…
 mozilla/cipherscan
A very simple way to find out which SSL ciphersuites are supported by a target.
 idov31/cronos
PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
 noxxi/p5-ssl-tools
Perl scripts for SSL/TLS analysis: check protocol and cipher support, verify certificates, test OCSP, and detect Heartbleed across SMTP, HTTPS, and…
 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 nicmx/fort-validator
RPKI Relying Party and RTR server that validates BGP route origin authorizations and serves validated data to routers over the RTR protocol.
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
 soufianecyber/quantum-safe-migration
Enterprise-grade toolkit to audit and migrate legacy infrastructure to hybrid post-quantum cryptography (PQC).
 nsacyber/detect-cve-2017-15361-tpm
Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 winslowe/cve-2024-4309-analysis
BGT-Pentest-LAB Final Project: Xiaomi HyperOS System Updater OTA Signature Verification Bypass (CVE-2024-4309) Deep Analysis.

 mrash/fwknop
Single Packet Authorization > Port Knocking
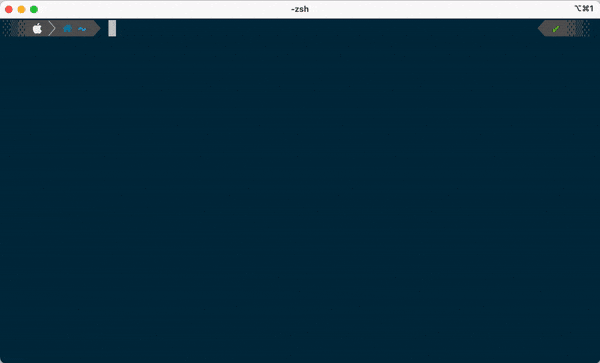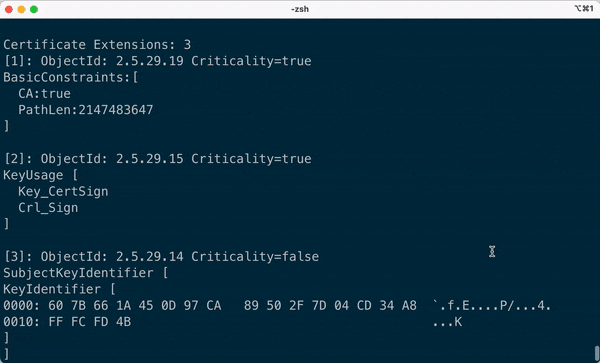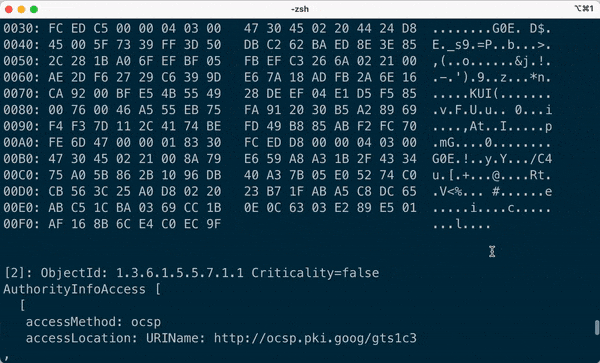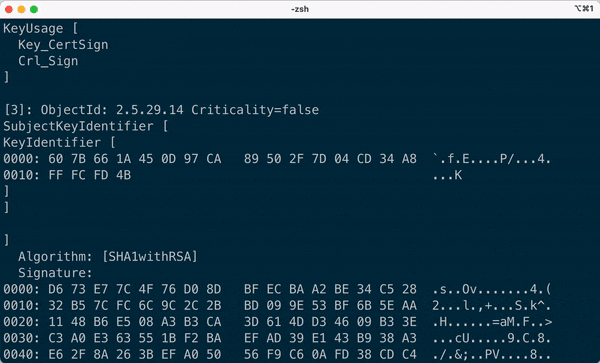 hakky54/certificate-ripper
🔐 A CLI tool to extract server certificates