PublicSafe
 roxanne_ardary/publicsafe
Client-side browser extension providing AES-256-GCM encryption, X25519 key exchange, Ed25519 signatures, and zero-knowledge key management for secure…
authenticationcryptographyencryption-decryption-tools+1
roxanne_ardary/publicsafeClient-side browser extension providing AES-256-GCM encryption, X25519 key exchange, Ed25519 signatures, and zero-knowledge key management for secure…

 compasssecurity/samlraider
SAML2 Burp Extension
 dhondta/python-codext
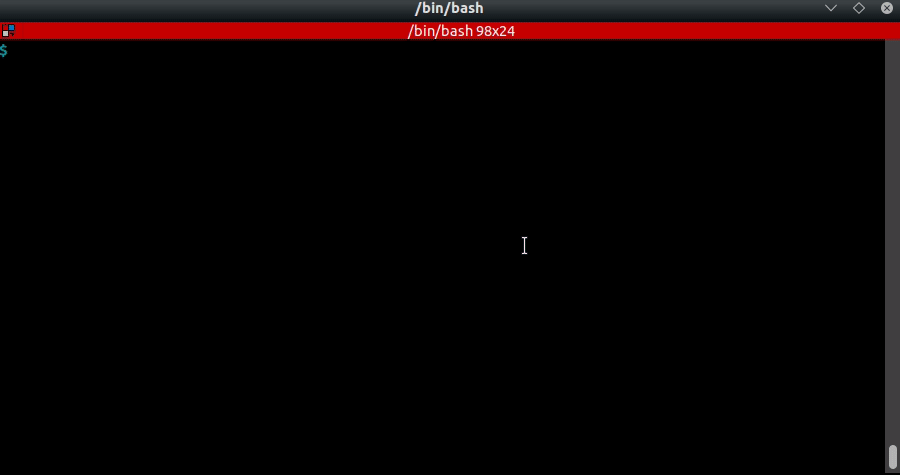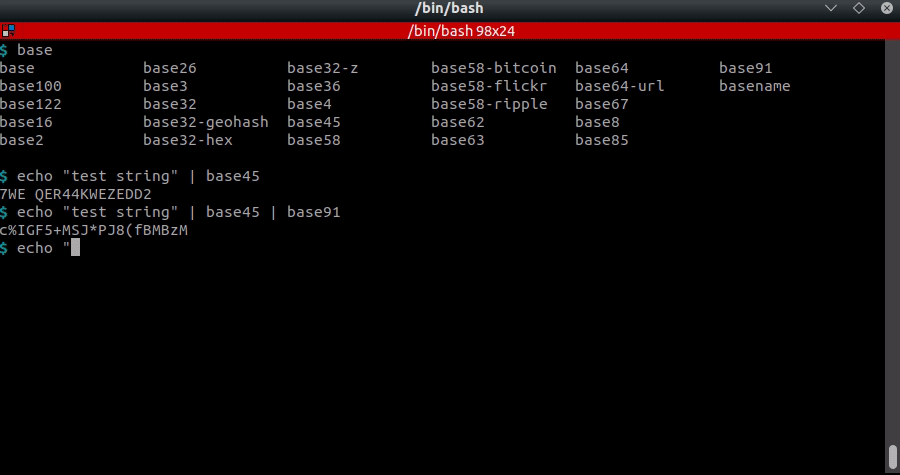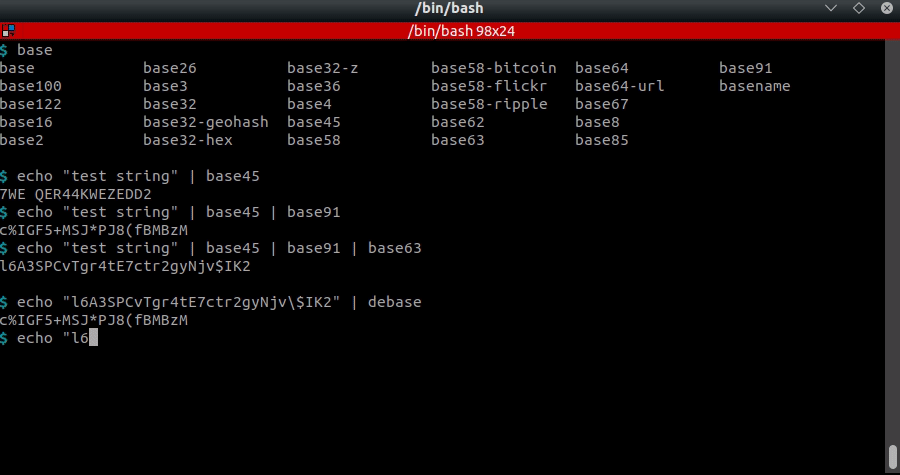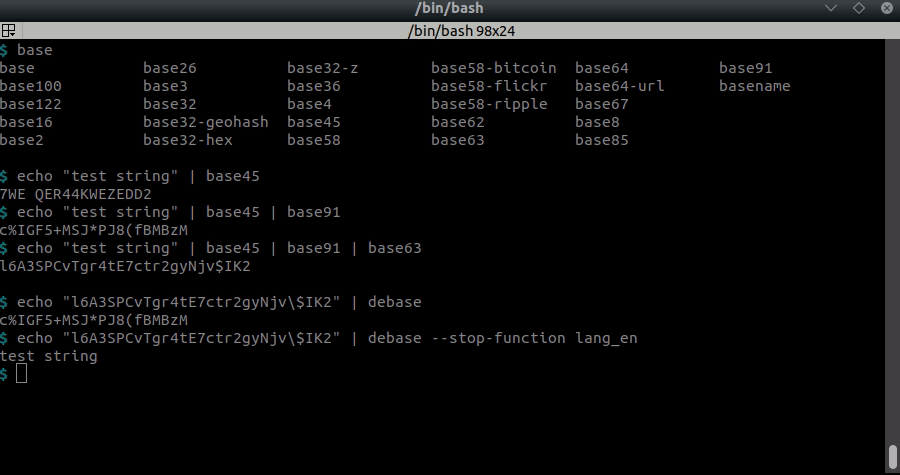
Python codecs extension featuring CLI tools for encoding/decoding anything
 toddmaustin/mojo-v
RISC-V ISA extension for hardware-enforced secret computation using ML-KEM-512 key encapsulation and SIMON-128 encryption, enabling data-oblivious…
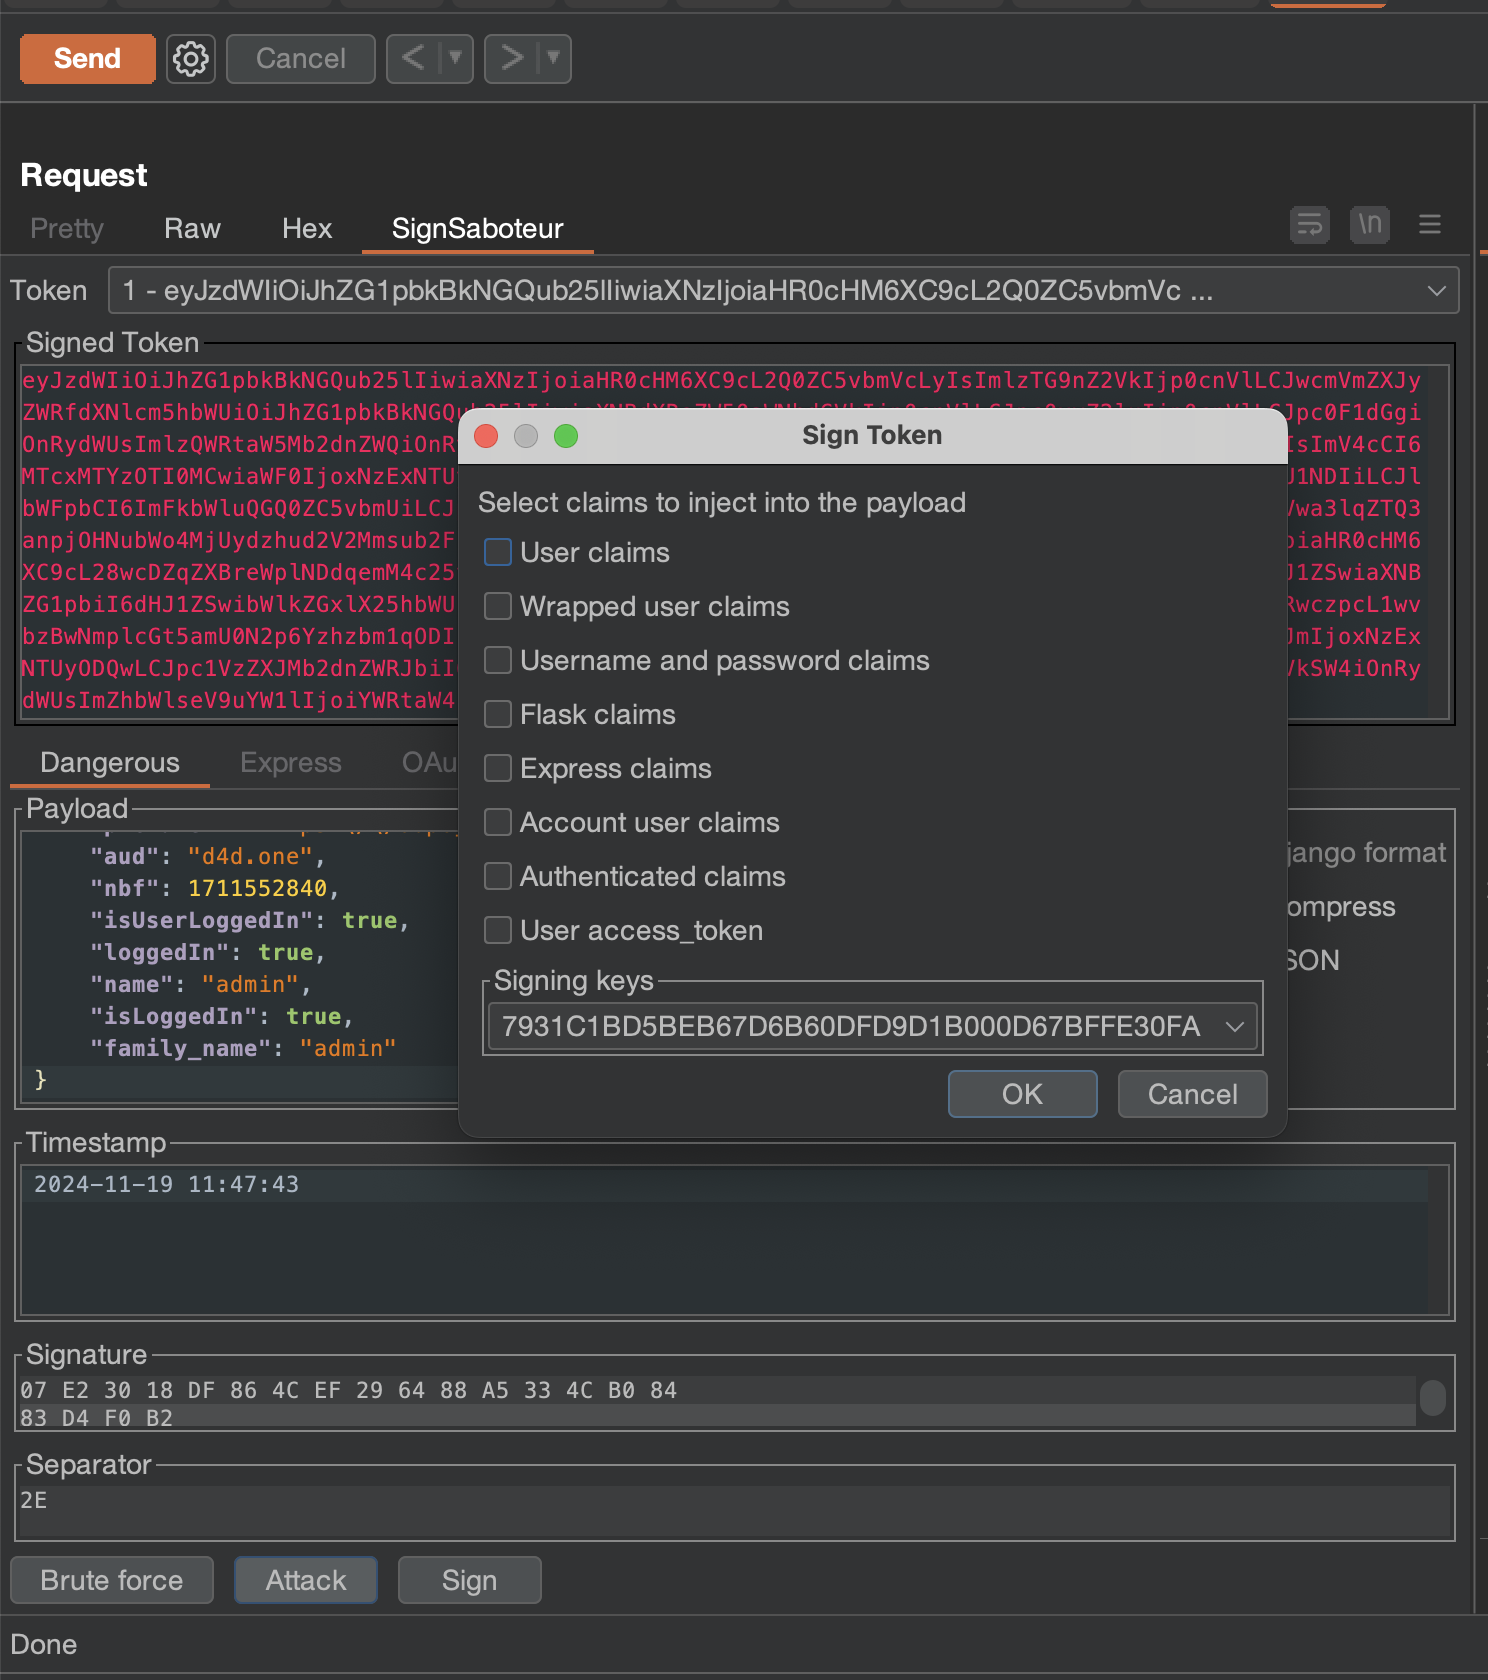 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
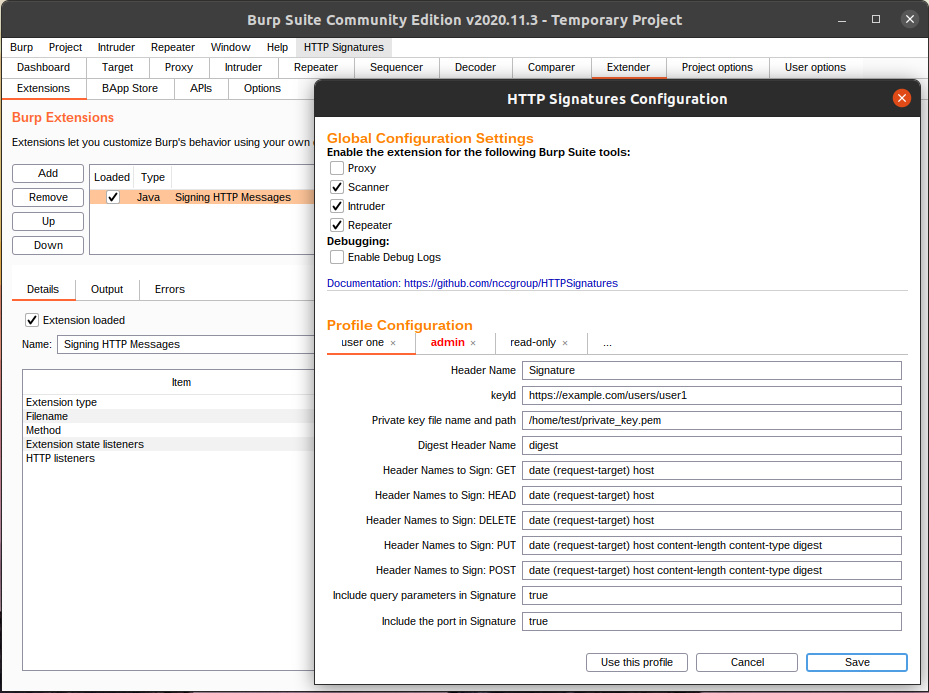 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 am-i-being-pwned/pgp-tools
Open-source browser extension for PGP encryption, decryption, and signing. Rust/WASM engine with WebAuthn PRF unlock, Argon2id password protection,…
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
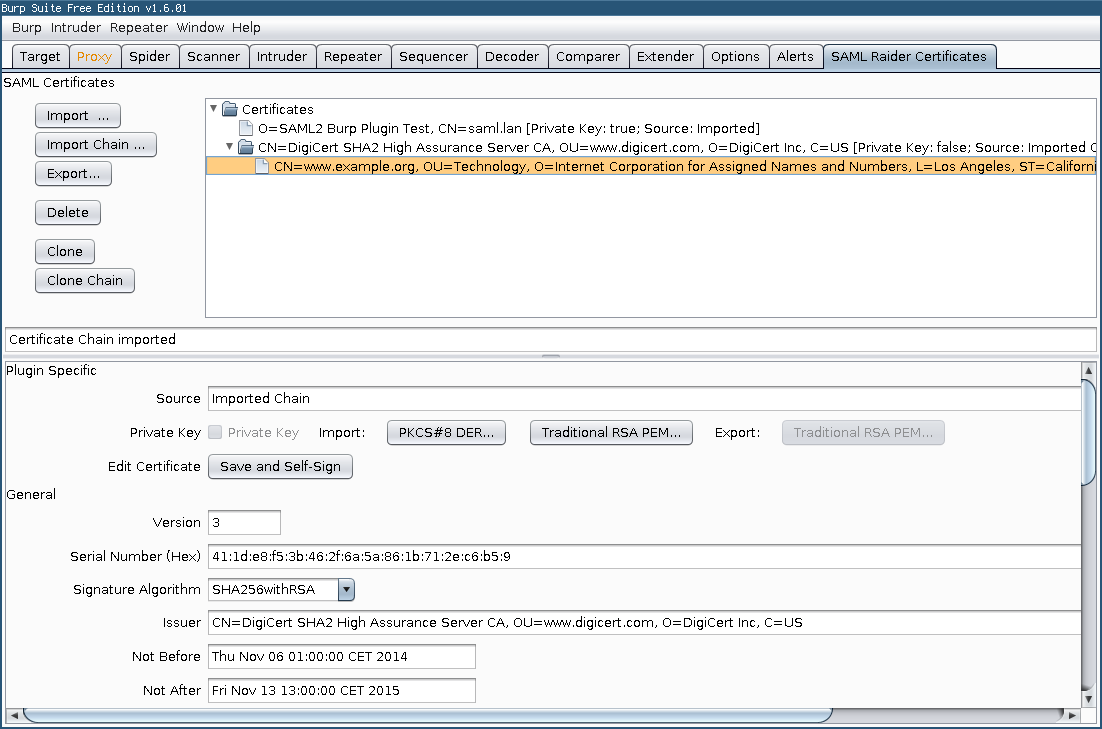 lindi2/samlraider
SAML2 Burp Extension
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 indrajeetmp11/heartbleed-poc-exploit-script
This Python PoC script detects the Heartbleed vulnerability (CVE-2014-0160) by performing a TLS handshake with heartbeat extension and sending a…
 ohexa/py_trustwallet_wasm
(CVE-2023-31290) Trust Wallet Core before 3.1.1, as used in the Trust Wallet browser extension before 0.0.183, allows theft of funds because the…
 jonathanwilbur/cve-2019-5010
CVE-2019-5010 Exploit PoC - Python Denial of Service via Malformed X.509v3 Extension
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 d-xuan/cve-2024-52510
Proof-of-concept exploit for CVE-2024-52510 demonstrating signature bypass in Nextcloud's E2EEv2 protocol, enabling server-side decryption of…