
 am-i-being-pwned/pgp-tools
Open-source browser extension for PGP encryption, decryption, and signing. Rust/WASM engine with WebAuthn PRF unlock, Argon2id password protection, and zeroized memory.

Open-source browser extension for PGP & AGE encryption and decryption.
Built with Rust/WebAssembly. Private keys never touch the JS heap unless they have to.




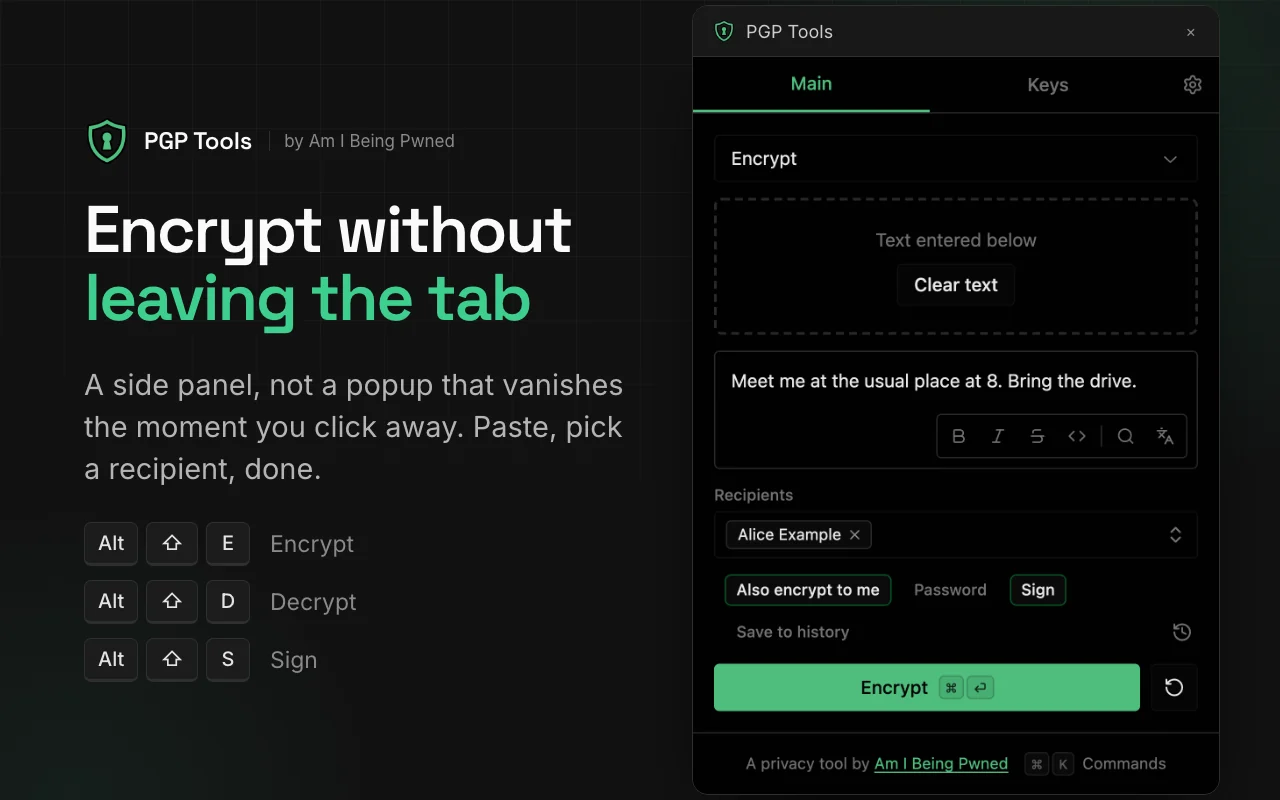
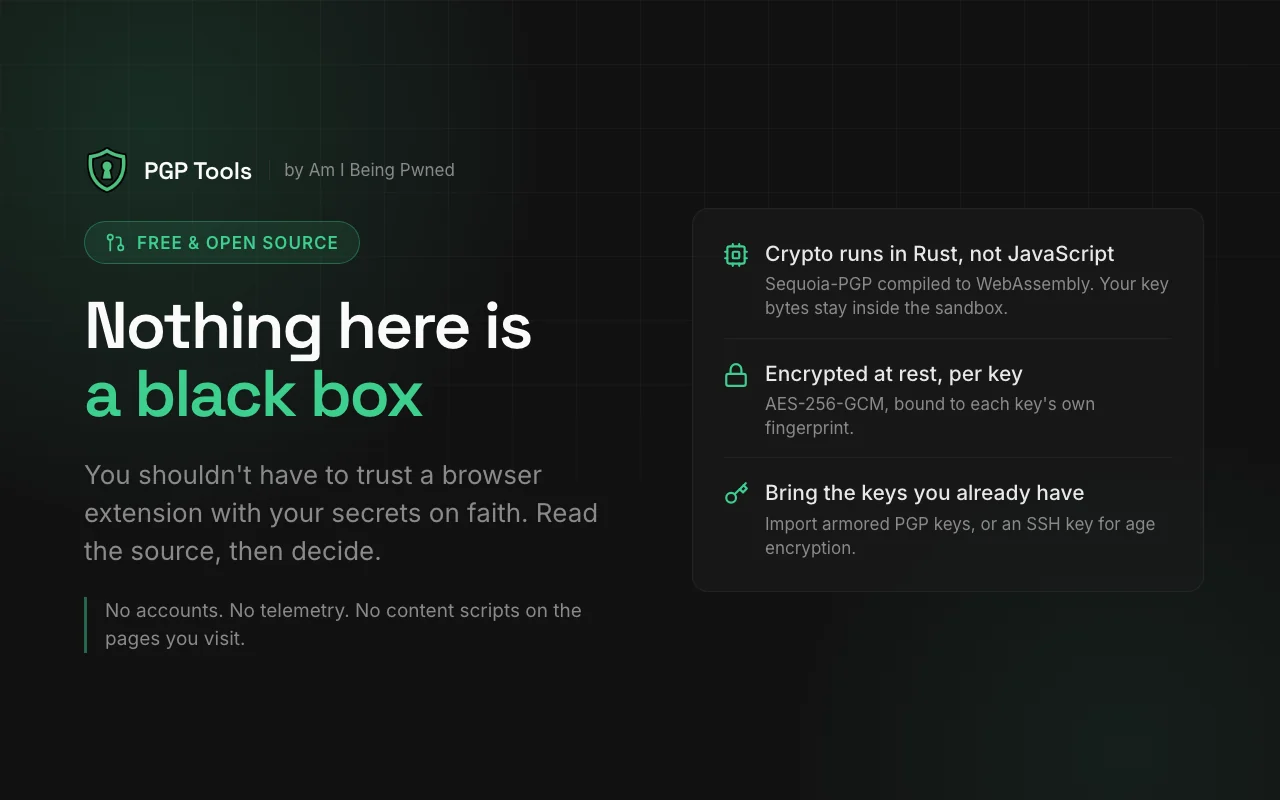
Open source and transparent. Most PGP browser extensions are closed source. You shouldn't trust a black box with your secrets.
Crypto runs in WASM, not JavaScript. All PGP operations run in a Rust/Sequoia-PGP WebAssembly sandbox. JS holds only an opaque integer handle to your key - the actual bytes live in WASM linear memory and are zeroized on drop. Private keys briefly pass through JS during generation and import before being encrypted and stored.
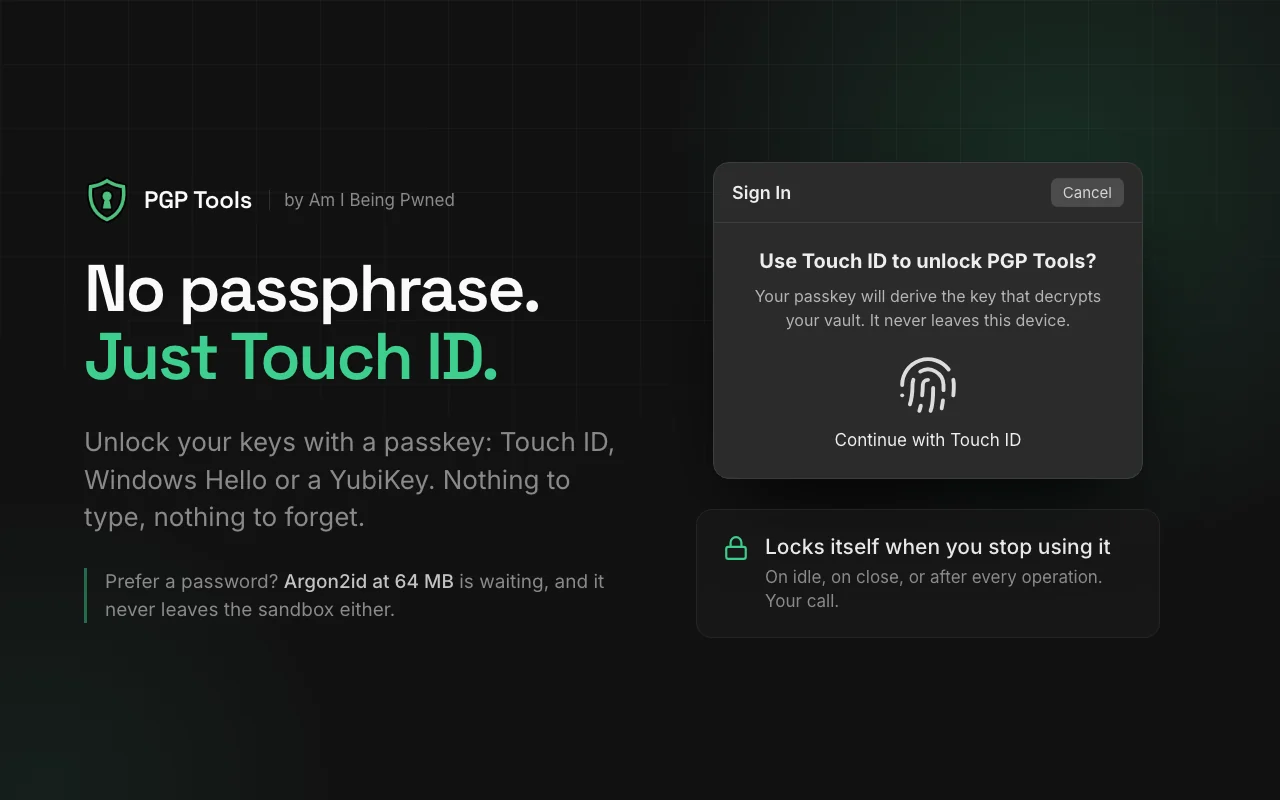
Passkey unlock. Protect keys with WebAuthn PRF - unlock with Touch ID, Face ID, Windows Hello, or a YubiKey instead of a password. The PRF output is combined with a stored secret via HKDF-SHA256, and the entire unlock flow runs in WASM.
Argon2id for passwords. 64 MB memory, 3 iterations - GPU brute-force resistant. The KDF, decryption, and key storage all happen in WASM. Password bytes are zeroed on both sides immediately after use.
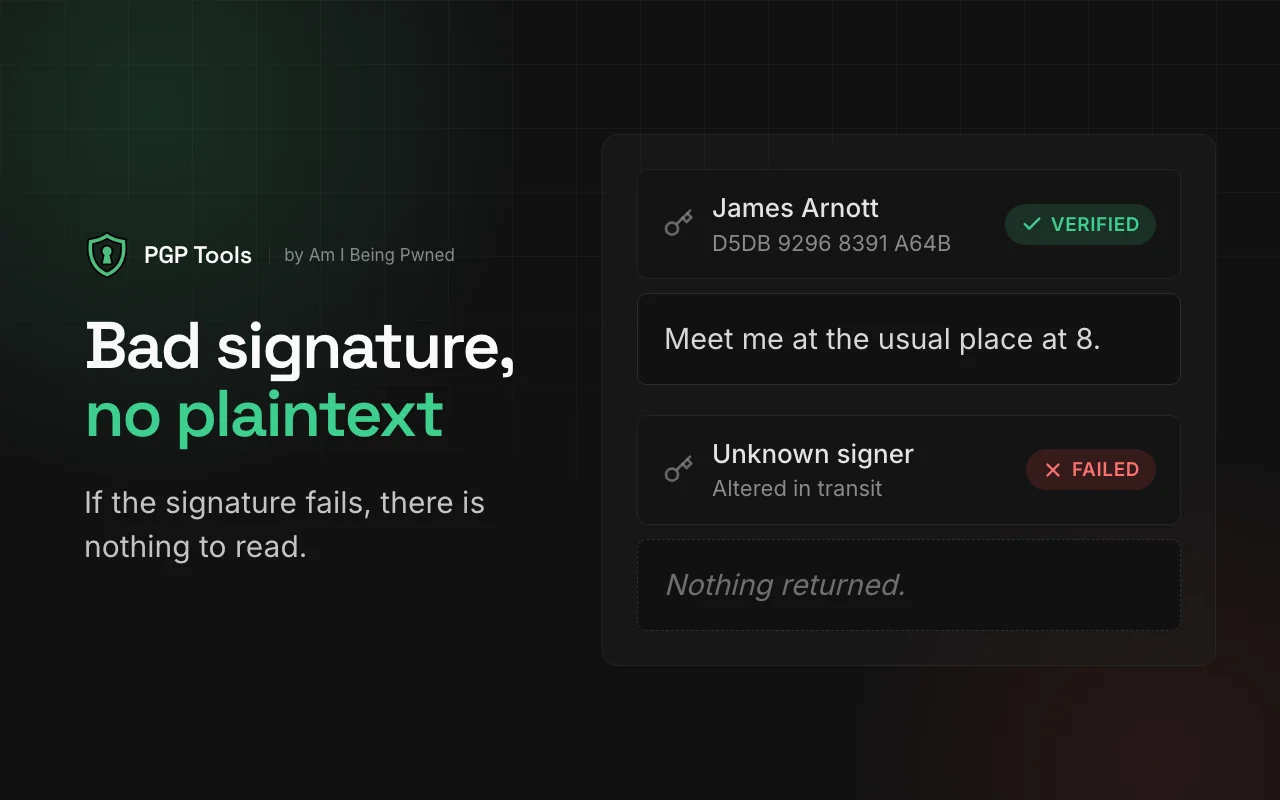
Atomic decrypt + verify. Plaintext and signature result are returned together in a single packed response. Bad signature = no plaintext returned. No TOCTOU window.
Zeroization everywhere. zeroize crate on all stored keys and intermediates (Rust). Uint8Array.fill(0) on passwords, PRF outputs, and derived keys (JS). WASM memory isn't GC'd, so zeroization is deterministic.
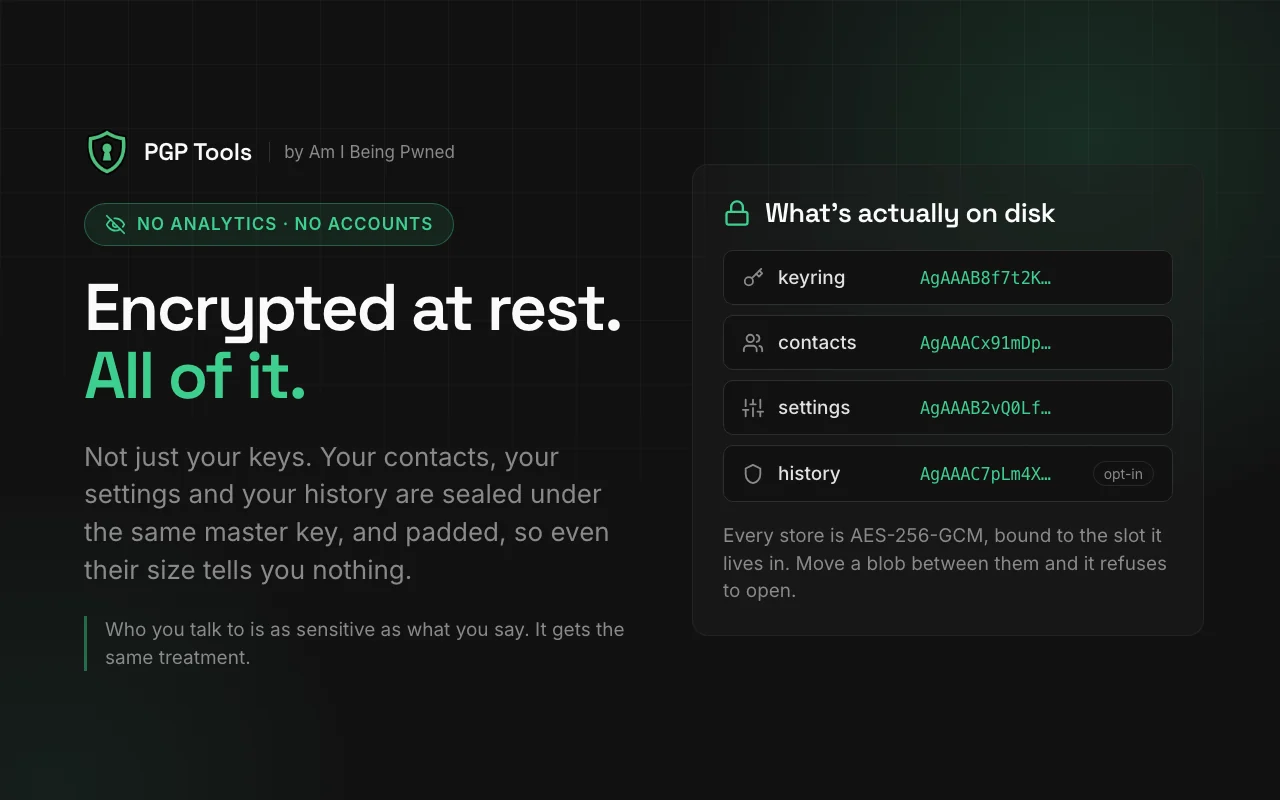
Per-key AAD. Each private key is encrypted with AES-256-GCM using Additional Authenticated Data bound to its fingerprint. Swapping blobs between key slots fails.
 |
 |
 |
 |
.crx) for the Web Store's Verified CRX Uploads (optional; off by default)ssh-ed25519 or ssh-rsa key and encrypt/decrypt age files (binary or armored), cross-checked against the Go age CLI. Import only (the app never generates SSH keys); encrypt/decrypt only (age has no signing). Native age1… keys are out of scope, and ECDSA, DSA and FIDO sk-* keys are rejected





