

testssl.sh
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
cryptographynetwork-securitypenetration-testing+2
testssl/testssl.shTesting TLS/SSL encryption anywhere on any port
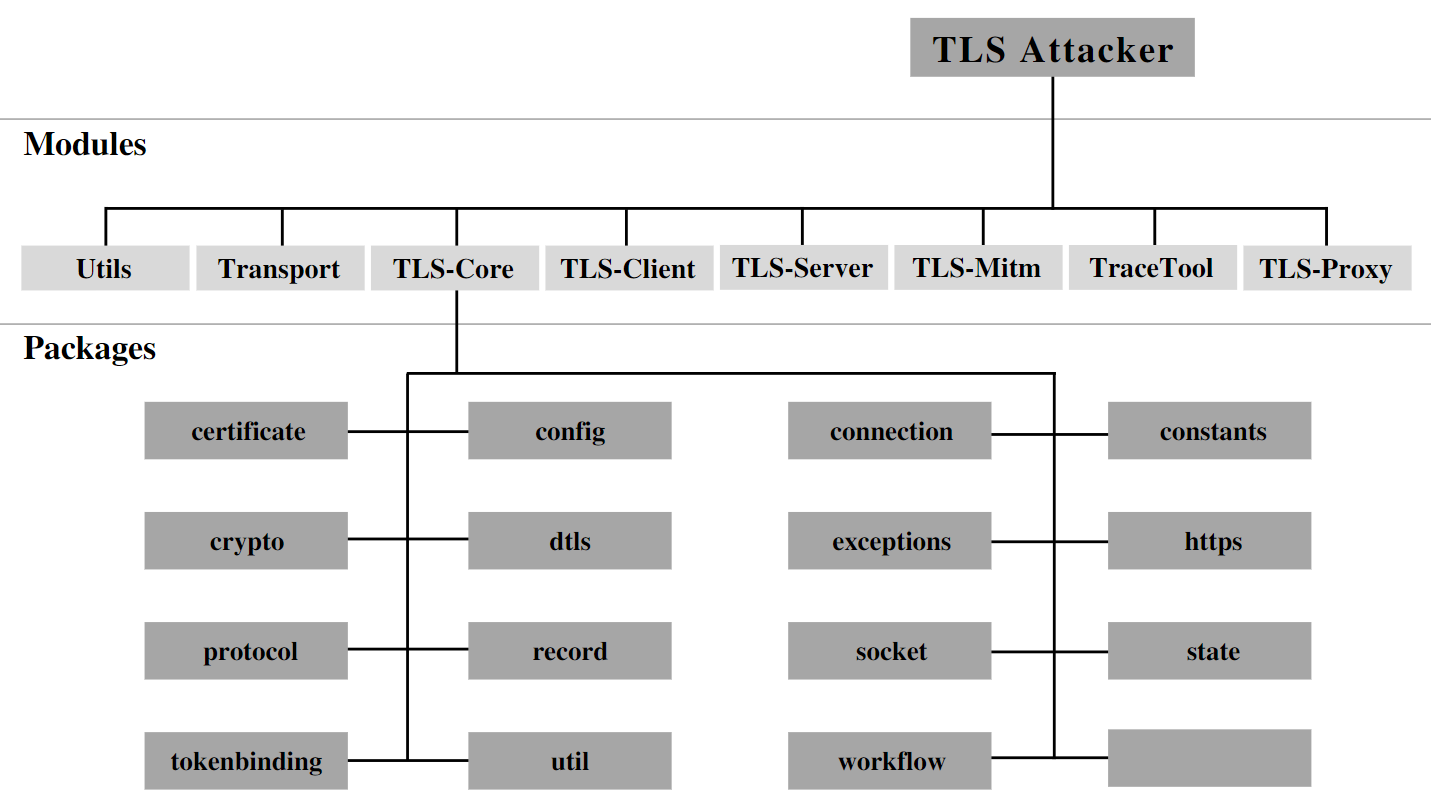 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…
 secretnonempty/cve-2014-0224
Go-based MITM exploit demo for OpenSSL CVE-2014-0224 (CCS Injection) targeting RC4-SHA cipher, with server/client proxy setup for testing TLS…
 dheatattack/dheater
Proof-of-concept denial-of-service tool that enforces Diffie-Hellman ephemeral key exchange over TLS and SSH to saturate server CPU, implementing…
 xyplex3/redteamcoin
Red Team Coin for crypto-mining operations.
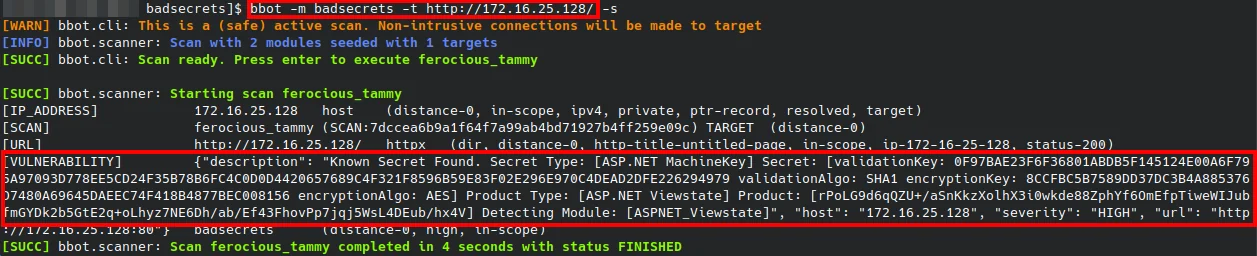 irsdl/crapsecrets
A library for detecting known secrets across many web frameworks
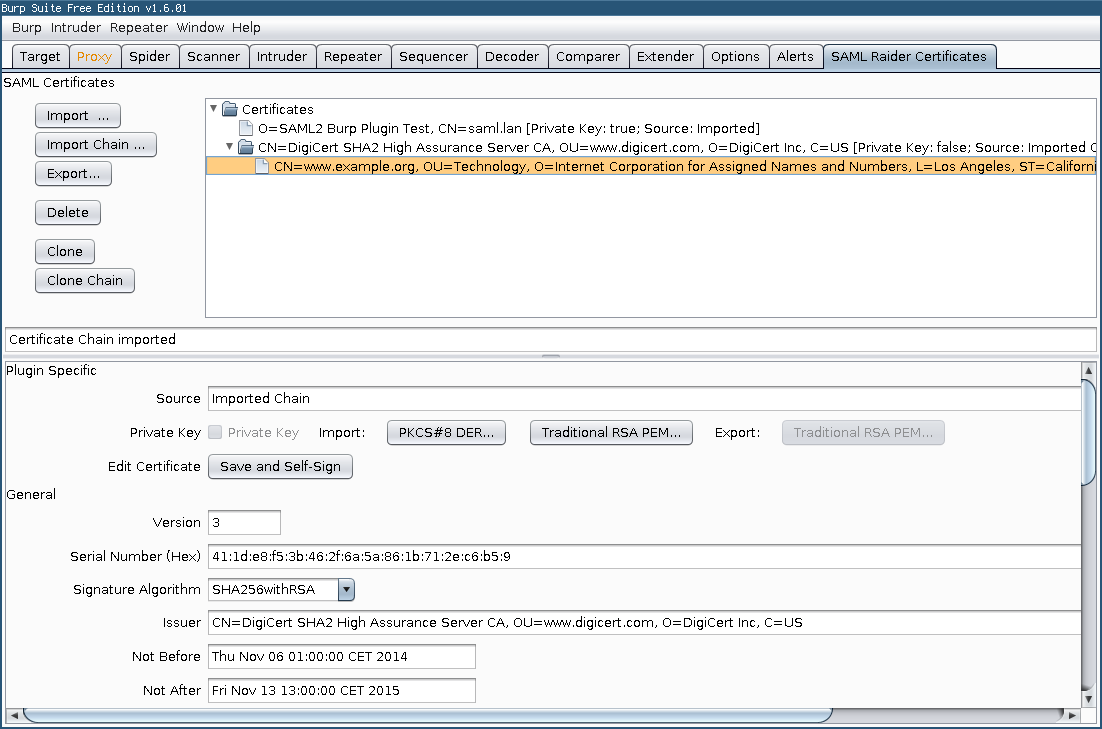 lindi2/samlraider
SAML2 Burp Extension
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
 filosottile/heartbleed
A checker (site and tool) for CVE-2014-0160
 gentilkiwi/kekeo
A little toolbox to play with Microsoft Kerberos in C
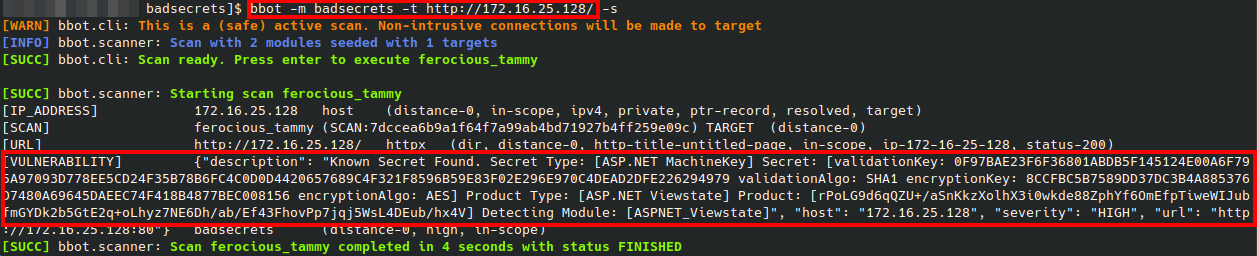 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 owasp/o-saft
O-Saft - OWASP SSL advanced forensic tool
 tls-attacker/tls-scanner
Automated TLS server and client configuration scanner for pentesters and researchers. Evaluates cipher suites, protocol versions, and security…
 iangcarroll/cookiemonster
Decodes and unsigns vulnerable session cookies from Django, Flask, Laravel, Express, and JWT frameworks. Supports HMAC-based decoders, base64…
 nfc-tools/milazycracker
Mifare Classic Plus - Hardnested Attack Implementation for SCL3711 LibNFC USB reader
 bdenneu/cve-2022-33679
One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
 lekensteyn/pacemaker
Heartbleed (CVE-2014-0160) client exploit