
CVE-2026-13447
 abraxas/cve-2026-13447
Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…
authenticationcryptographyexploitation+5
abraxas/cve-2026-13447Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…
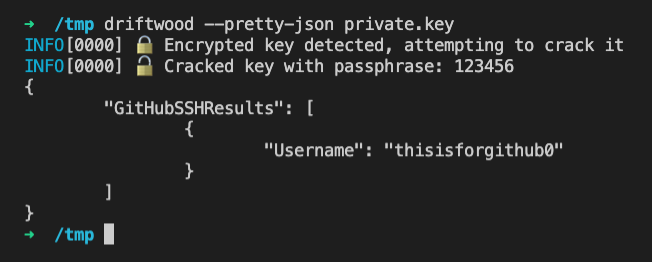 trufflesecurity/driftwood
Private key usage verification
 disley15-collab/bigint-buffer-js
Pure-JS drop-in for [email protected] without the vulnerable native binding (CVE-2025-3194)
 paradoxis/stegcracker
Steganography brute-force utility to uncover hidden data inside files
 thrilokh-q123/cve-2025-23134_fixes_code
The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().
 artsbykriss/profanity-verifier
Provable check for CVE-2022-40769: does an EOA's private key lie in the Profanity-reachable key space?
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…
 b0lbas/chpwd
Secure CLI password manager (Argon2id + AES-256-GCM)
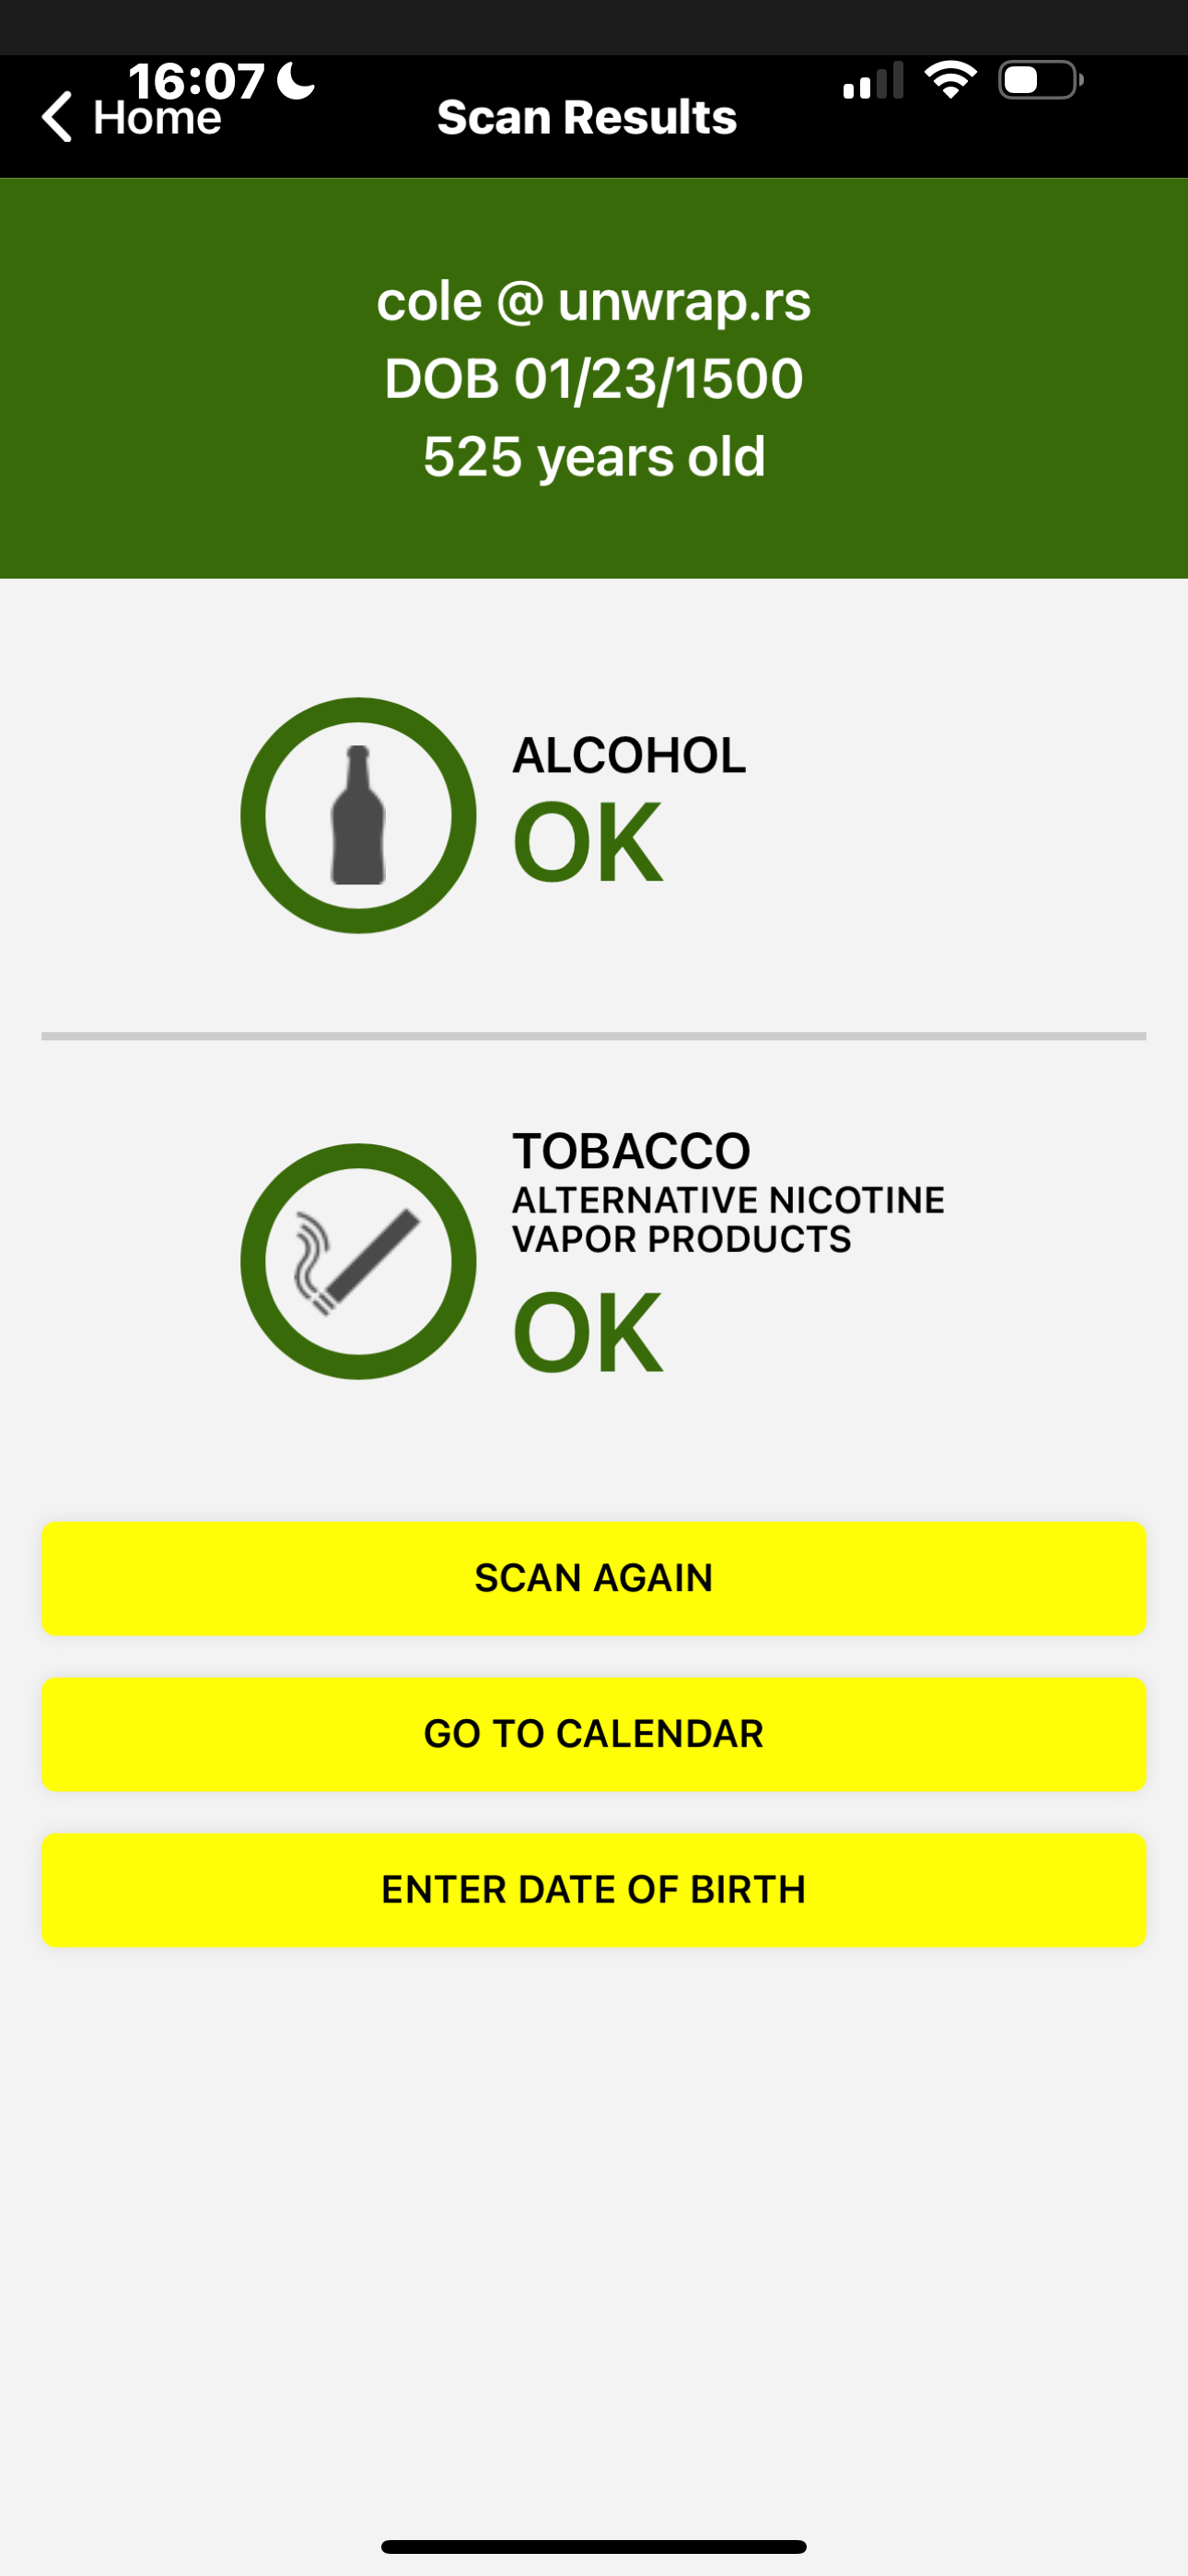 coleleavitt/aamva-pdf417-vulnerability-research
Research into systemic PDF417 validation vulnerabilities in AAMVA-compliant ID systems (CVE-2025-31336, CVE-2025-31337, scr1841160)
 matthiasbe/secuimag3a
Exploit of the CVE-2016-1494 allowing to forge signatures of RSA keys with low exponents
 zendframework/zend-crypt
Cryptographic component from Zend Framework
 orange-cyberdefense/haiti
🔑 A CLI tool to identify the hash type of a given hash.
 robindavid/lsb-steganography
Python program to steganography files into images using the Least Significant Bit.