

SAMLRaider
 lindi2/samlraider
SAML2 Burp Extension
authenticationcryptographyidentity-access-management+4
37 years ago
lindi2/samlraiderSAML2 Burp Extension
 george0papasotiriou/cve-2026-8080-dkim-signature-verification-bypass-header-canonicalization-flaw-
Simulated Python demonstration of CVE-2026-8080 DKIM verification bypass, showing how non-compliant header canonicalization lets attackers inject…
 yoanndqr/cve-2020-0601
CurveBall CVE exploitation
 uziii2208/cve-2026-96760
Authlib 1.7.2: Signature Verification Bypass - General JSON JWS Accepts Unsigned Payload when `signatures` is Empty
 xaxis/bitcoin-security
Educational study of Bitcoin key entropy: weak-RNG wallet enumeration (Milk Sad / CVE-2023-39910 class) vs. the infeasibility of brute-forcing a good…
 disley15-collab/bigint-buffer-js
Pure-JS drop-in for [email protected] without the vulnerable native binding (CVE-2025-3194)
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 nserser/lr-webpki
Reference implementation of LR+ post-quantum authentication over WebPKI CA context, with corpus pipeline, reconstruction, evaluation, and provenance…
 jas502n/xbootencodepwd
github xboot-x encode password
 d-xuan/cve-2024-52510
Proof-of-concept exploit for CVE-2024-52510 demonstrating signature bypass in Nextcloud's E2EEv2 protocol, enabling server-side decryption of…
 owasp/secureml
SecureML - Securing and Watermarking AL models
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…

 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 cryptoadvocate/dcsgonefwbsp
The firmware board support package home of the Circuit Crafters first electronic badge project.
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
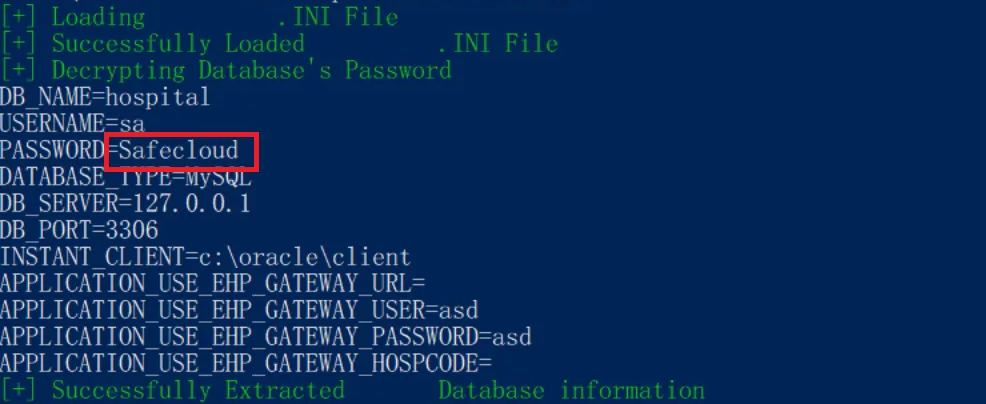 safecloudth/cve-2024-53522
Proof-of-concept exploit for CVE-2024-53522, demonstrating decryption of HOSxP XE database credentials using a static hard-coded private key-IV.
 kinryulabs/rootpacket-cve-2026-31431
Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…
