

CVE-2022-33679
 bdenneu/cve-2022-33679
One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
authenticationcryptographyexploitation+2
415
bdenneu/cve-2022-33679One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
 jofpin/temcrypt
Evolutionary encryption framework based on scalable complexity over time
 screetsec/imr0t
imR0T: Send a quick message with simple text encryption to your whatsapp contact and protect your text by encrypting and decrypting, basically in…
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
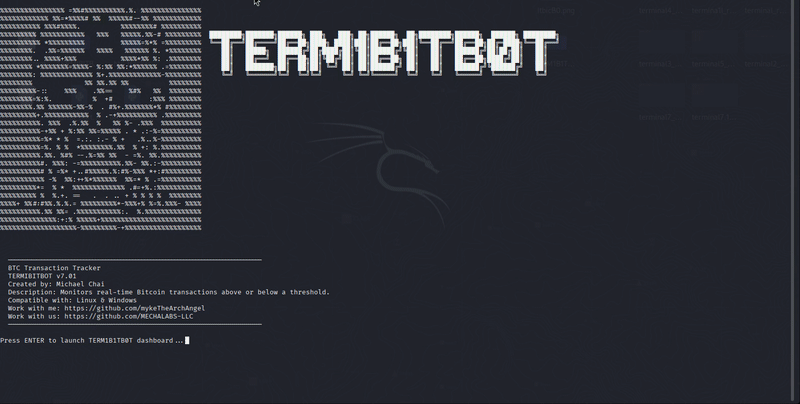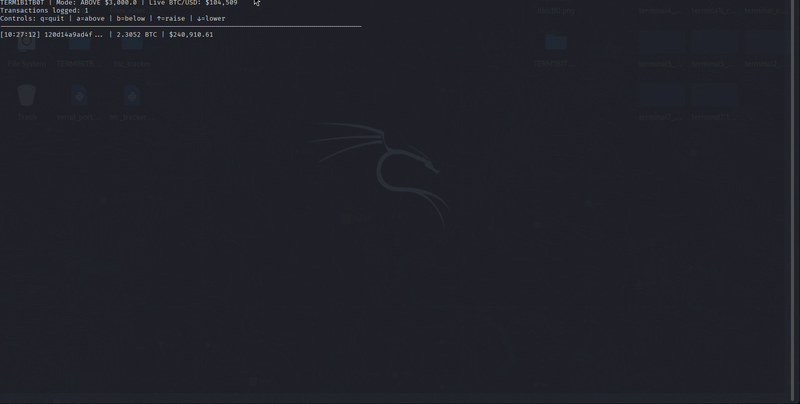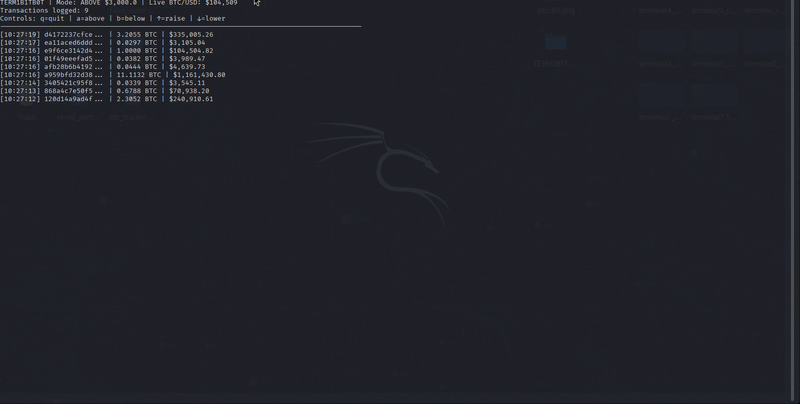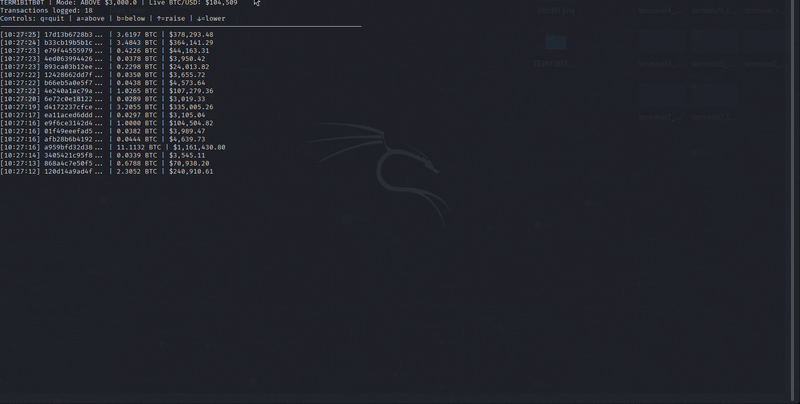 mykethearchangel/term1b1tb0t
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.
 dedellix/mut-bc-ss-01
Mutation testing on X.509 Certificate Validation IN OpenSSL v.1.1.1h, based on CVE-2021-3450.
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
 zakyhermawan/simple-sweet32
Simplified Version of Cryptography Attack based on Birthday Paradox: Sweet32 (CVE-2016-2183)
 0xxon/cve-2020-0601-utils
C++ based utility to check if certificates are trying to exploit CVE-2020-0601
 joelbts/cve-2020-0601_poc
Demonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
 project-oak/oak
Meaningful control of data in distributed systems.
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
 rek7/descrypt-cpu-collision-cracker
DEScrypt CPU Collision Cracker
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
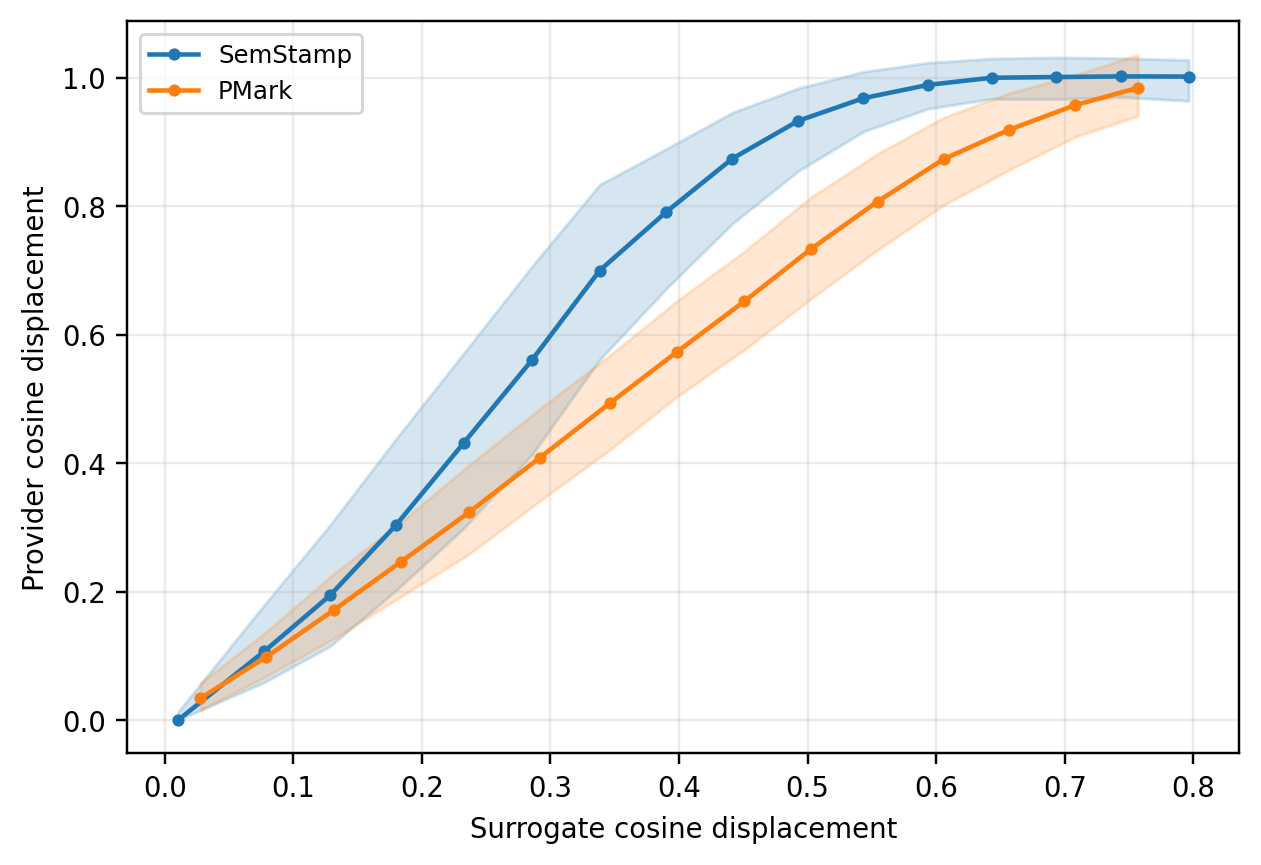 d-diaa/swordstamp
Semantic Watermarking with Order-Robust Detection over Sub-sentence Units
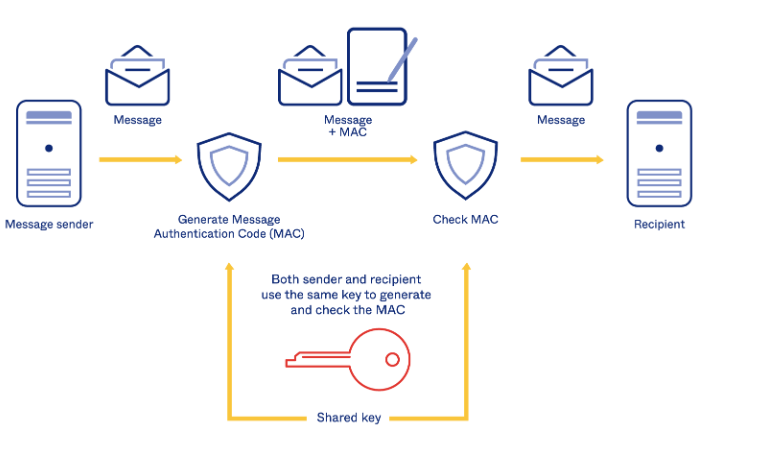 password123456/about-hmac
HMAC Implementation Example and Explanation