
wolfssl
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
cloud-securitycryptographyembedded-systems-security+6
3.0k
wolfssl/wolfsslThe wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 mrash/fwknop
Single Packet Authorization > Port Knocking
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 donctl/sandy
Release of the sandy framework.
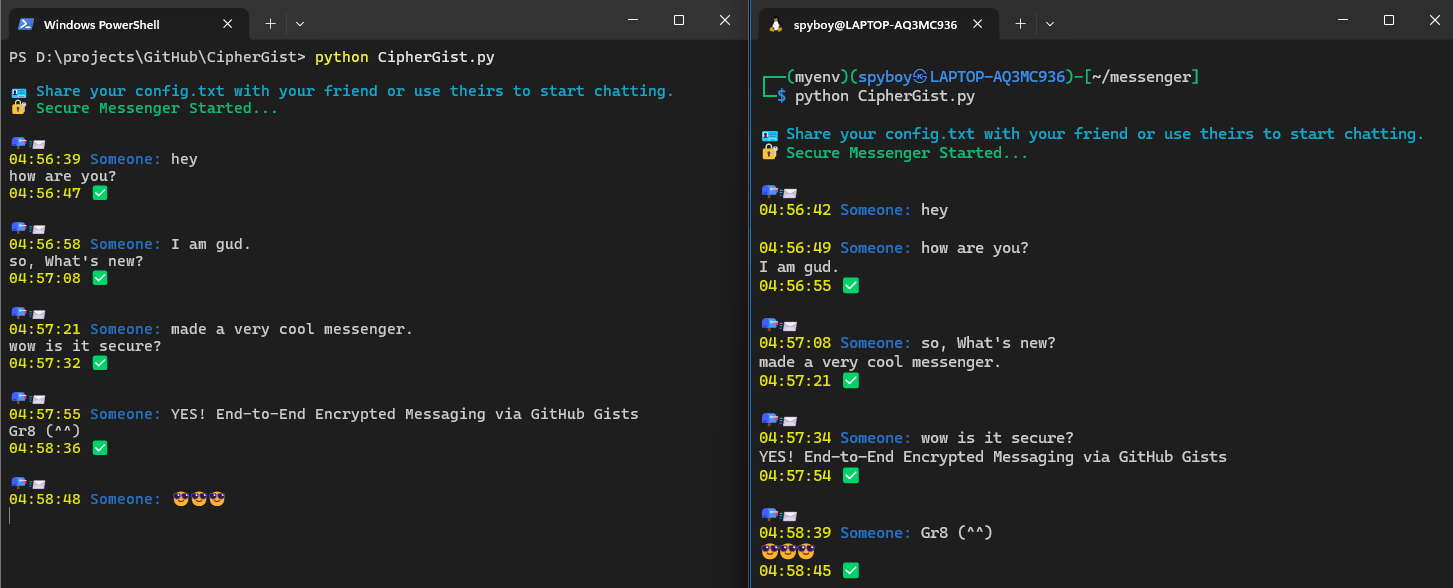 spyboy-productions/ciphergist
End-to-End Encrypted Messaging via GitHub Gists
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 spiderlabs/twsl2011-007_ios_code_workaround
Workaround for the vulnerability identified by TWSL2011-007 or CVE-2008-0228 - iOS x509 Certificate Chain Validation Vulnerability
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
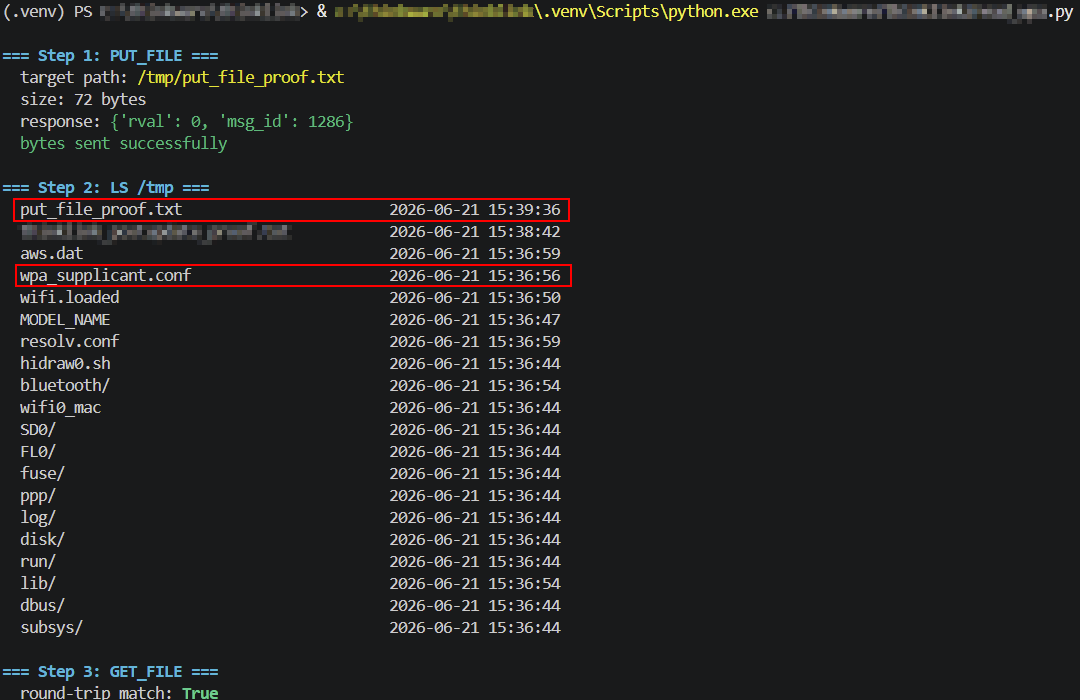 turretsec/disclosure-thinkware-u3000
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 winslowe/cve-2024-4309-analysis
BGT-Pentest-LAB Final Project: Xiaomi HyperOS System Updater OTA Signature Verification Bypass (CVE-2024-4309) Deep Analysis.
 577industries/aegisgraph
AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…