
jfrog-openssl-tools
 jfrog/jfrog-openssl-tools
Python utilities to check whether a TLS server requires client certificates and to scan local ELF binaries for vulnerable OpenSSL 3.x code linked to…
binary-analysiscryptographyinformation-gathering+3
16
jfrog/jfrog-openssl-toolsPython utilities to check whether a TLS server requires client certificates and to scan local ELF binaries for vulnerable OpenSSL 3.x code linked to…
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 isec-tugraz/cjag
C implementation of a cache-based jamming agreement that establishes a cross-VM cache covert channel between co-located virtual machines for research…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 cohesity/secadvisory
Vendor security advisory repository documenting Cohesity product vulnerabilities, including CVE-2019-11242 vCenter TLS certificate validation flaw,…
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
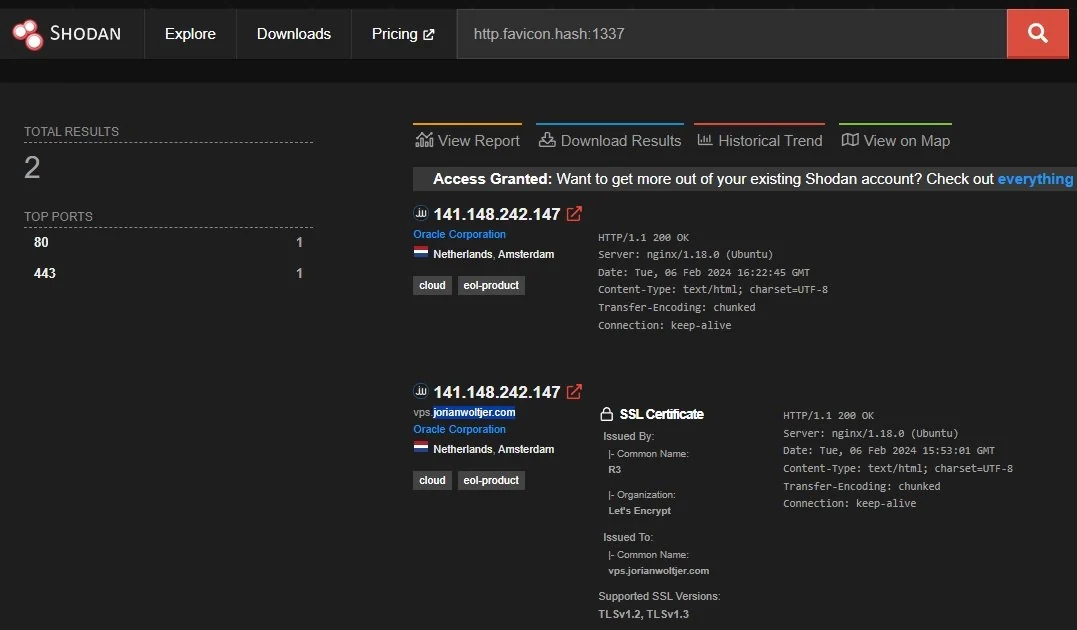 jorianwoltjer/shodan-favicon-preimage
Generate a favicon that results in any target hash on Shodan
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
 abhinavagarwal07/scadapack-secure-lock-poc
Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 demining/pixnapping-attack-on-android
Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…
 dulieno/cve-2026-26012
Proof-of-concept exploit for CVE-2026-26012, a broken access control in Vaultwarden that allows any organization member to enumerate and decrypt all…