CVE-2025-6325_CVE-2025-6327

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

A script to search, scrape and scan for Apache Log4j CVE-2021-44228 affected files using Google dorks

Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.

Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…

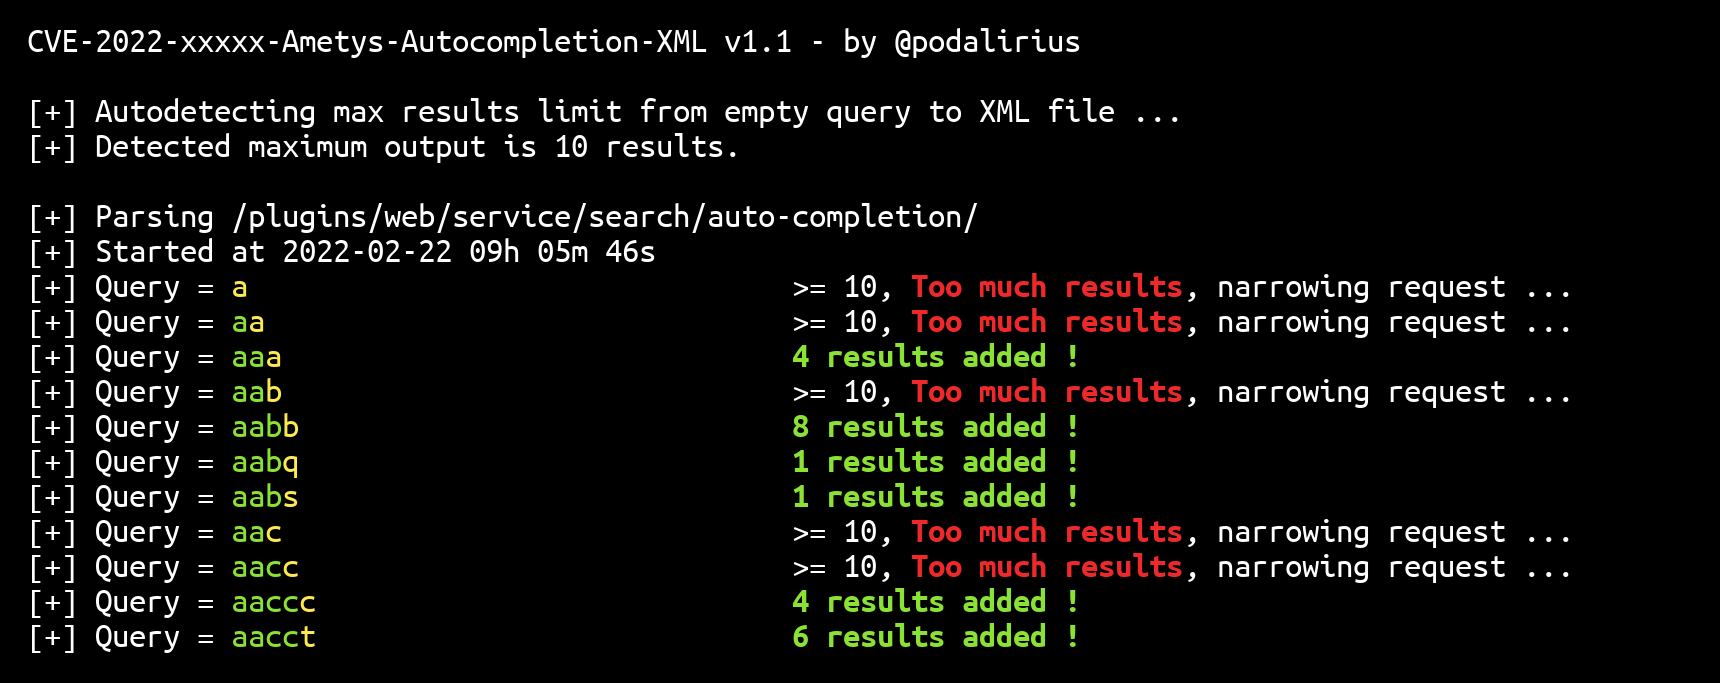
A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.

A short scraper looking for a POC of CVE-2024-49112

WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证

Exploit tool for CVE-2024-39722, a model existence disclosure vulnerability in Ollama. Performs version checks, crawls official model library, and…

Exploit for CVE-2018-20555: automated discovery and takeover of Twitter accounts via leaked API keys in vulnerable Social Network Tabs WordPress…

Proof-of-concept exploit demonstrating SSRF vulnerabilities in Firecrawl web scraper (CVE-2024-56800, CVE-2025-57818) with self-hosted setup and…

Google search crawler that collects URLs vulnerable to Apache Struts2 S2-045 (CVE-2017-5638) using configurable keywords and proxy support.

Automated detection & exploitation of critical PHP vulnerabilities (CVE-2024-4577 bypass, CVE-2025-14177, CVE-2025-14180, CVE-2025-14178)

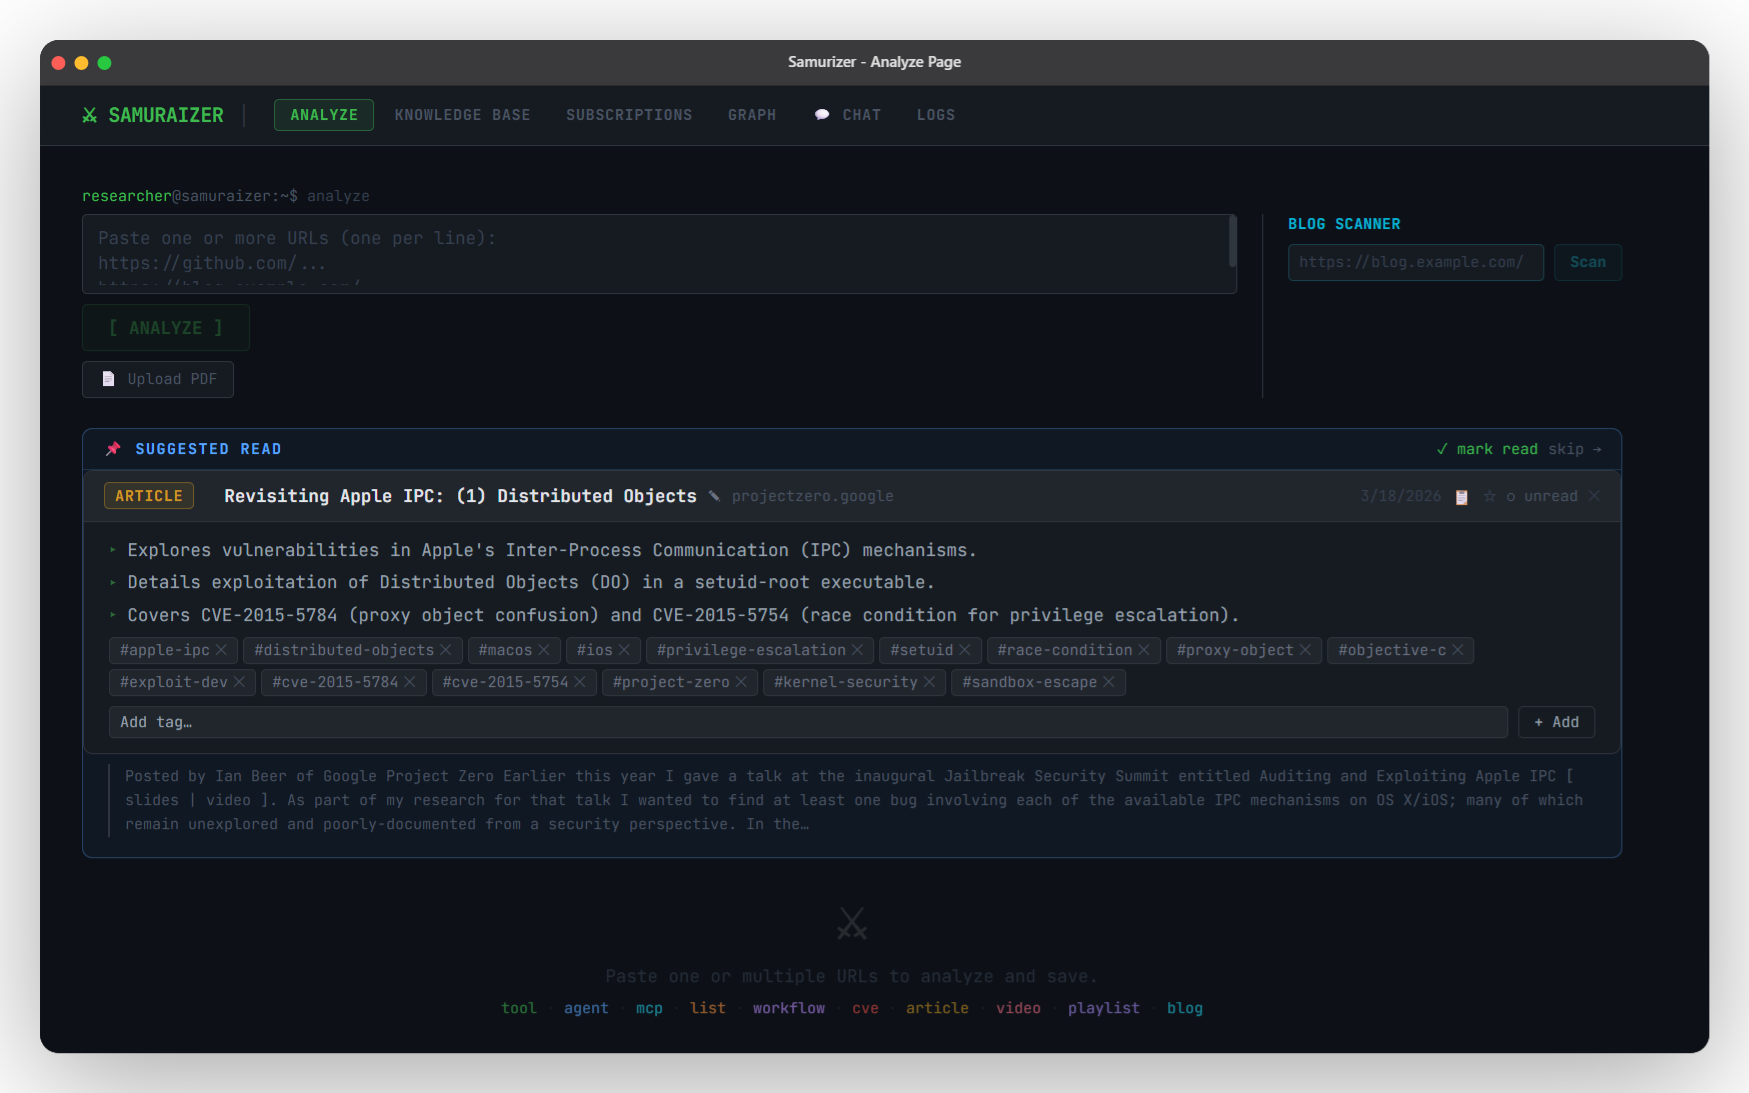
NotebookLM on steroids — purpose-built for security researchers.

Passive recon & attack surface mapper — zero requests sent

Automatic SQL injection and database takeover tool

Advanced dork Search & Mass Exploit Scanner

The Prime Cross Site Request Forgery (CSRF) Audit and Exploitation Toolkit.