CVE-2025-6325_CVE-2025-6327

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…

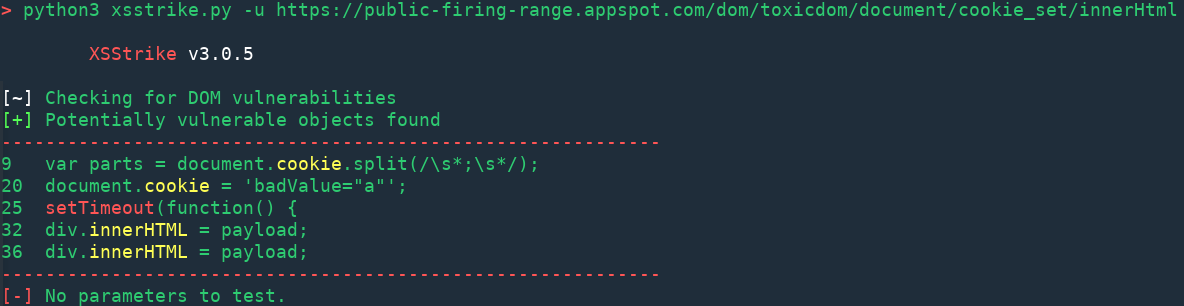
Web vulnerability scanner written in Python3

Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.

A collection oneliner scripts for bug bounty

A flexible internet crawler used for scanning technologies, instances and vulnerabilities worldwide across the internet.

CVE-2015-6668, relacionada con el plugin WP Job Manager para WordPress (versiones ≤ 0.7.25).

Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…

Web application security scanner created by lcamtuf for google - Unofficial Mirror

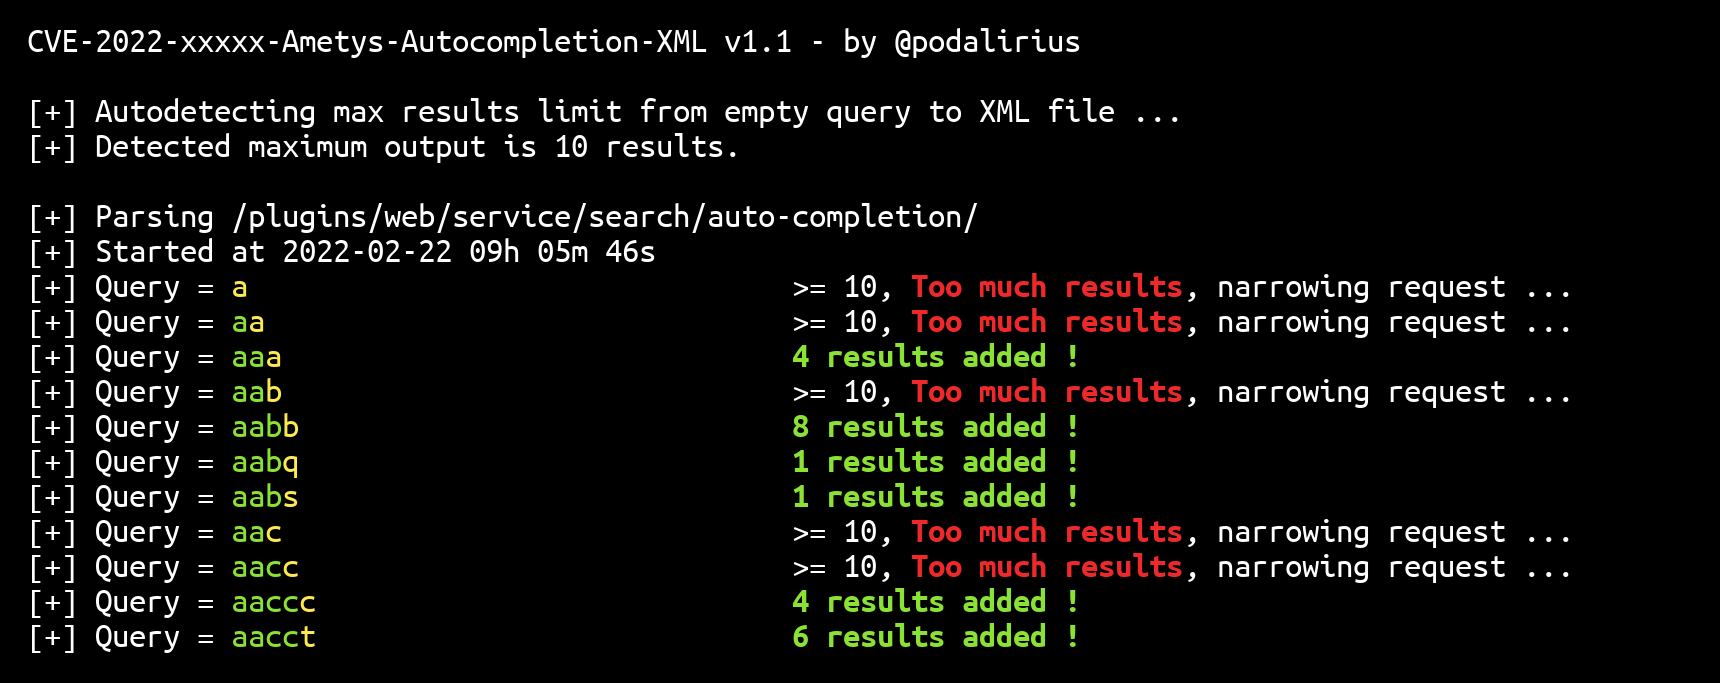
A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.

This is a CVE-2025-29927 Scanner.

Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision


Next generation web scanner

WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

Exploit tool for CVE-2024-39722, a model existence disclosure vulnerability in Ollama. Performs version checks, crawls official model library, and…

A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…