
trawl
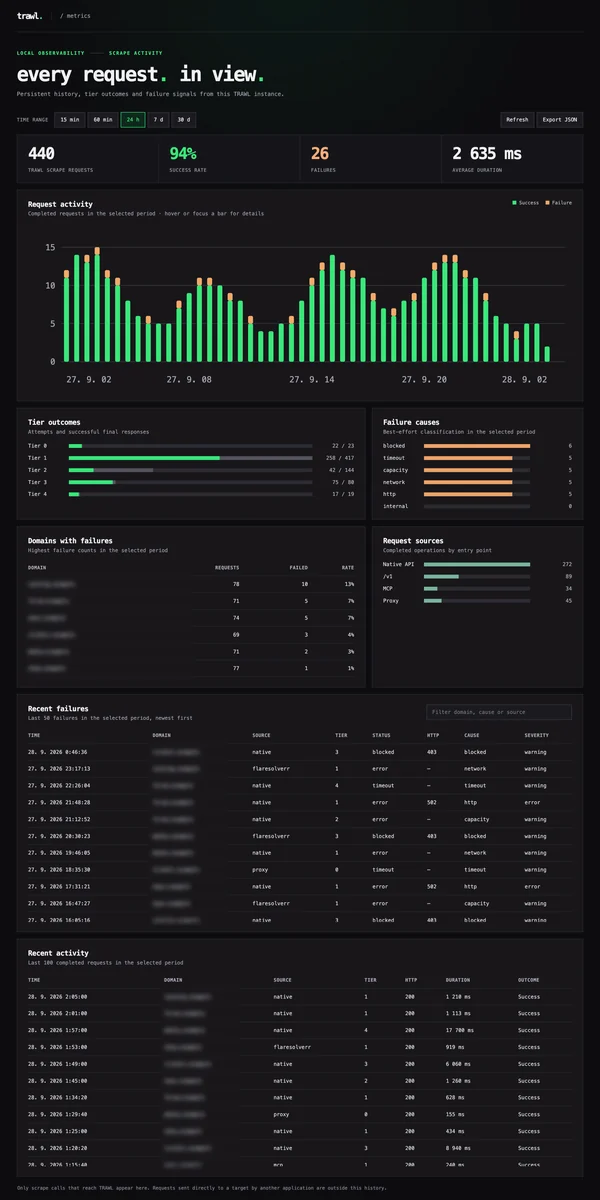
 germondai/trawl
Self-hosted scraping engine — bypasses any JS challenge & captcha: Cloudflare, Turnstile, reCAPTCHA, hCaptcha, GeeTest. FlareSolverr & Byparr…
anti-botcaptcha-bypasscrawler+5
1.1k6 days ago
germondai/trawlSelf-hosted scraping engine — bypasses any JS challenge & captcha: Cloudflare, Turnstile, reCAPTCHA, hCaptcha, GeeTest. FlareSolverr & Byparr…
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 houmanpashaei/cve-2025-29927
This is a CVE-2025-29927 Scanner.
 h4k6/cve-2023-2982-poc
WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证
 cyhe50/cve-2024-56800-poc
Proof-of-concept exploit demonstrating SSRF vulnerabilities in Firecrawl web scraper (CVE-2024-56800, CVE-2025-57818) with self-hosted setup and…
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
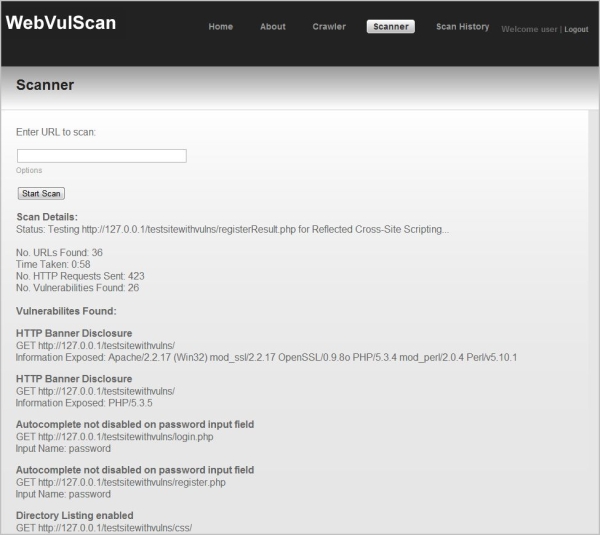 dermotblair/webvulscan
Web Application Vulnerability Scanner.
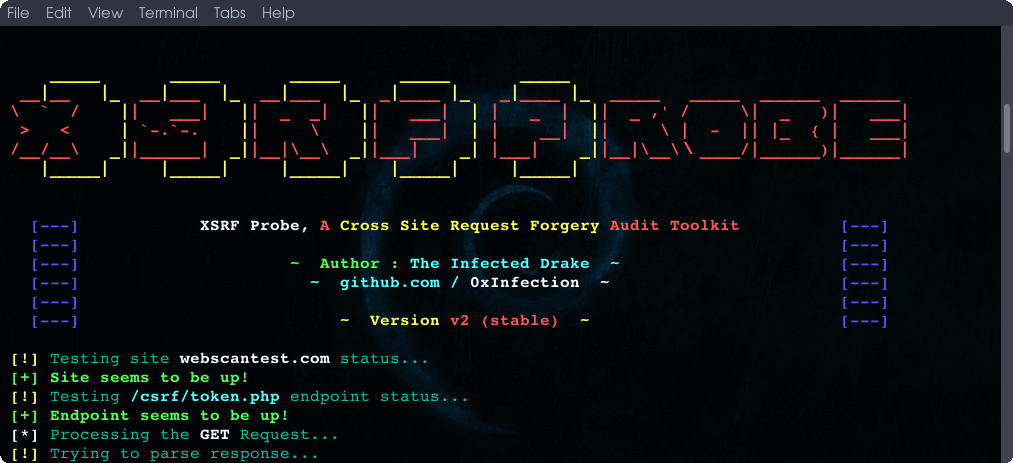 0xinfection/xsrfprobe
The Prime Cross Site Request Forgery (CSRF) Audit and Exploitation Toolkit.
 callforpapers-source/jshole
A JavaScript components vulnerability scanner, based on RetireJS
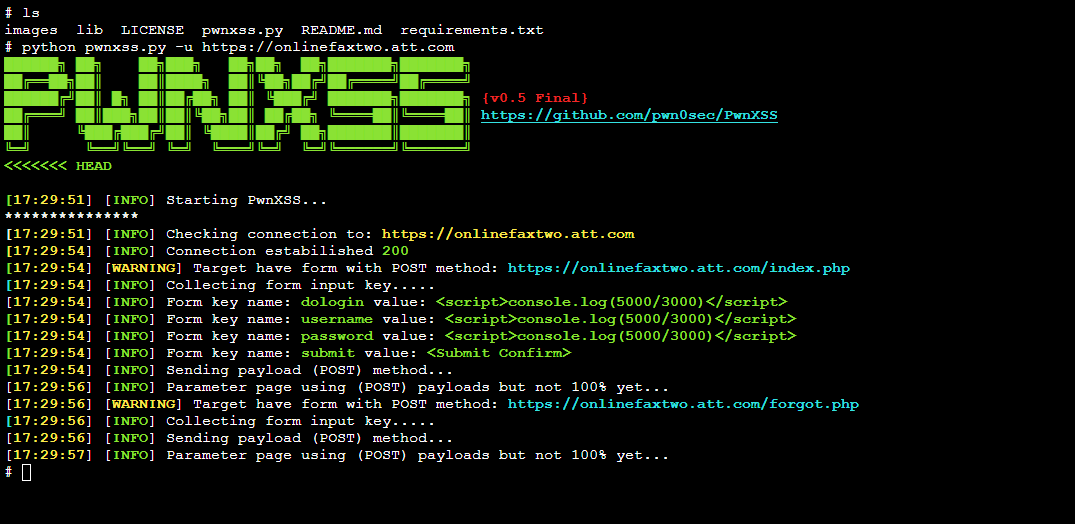 pwn0sec/pwnxss
PwnXSS: Vulnerability (XSS) scanner exploit
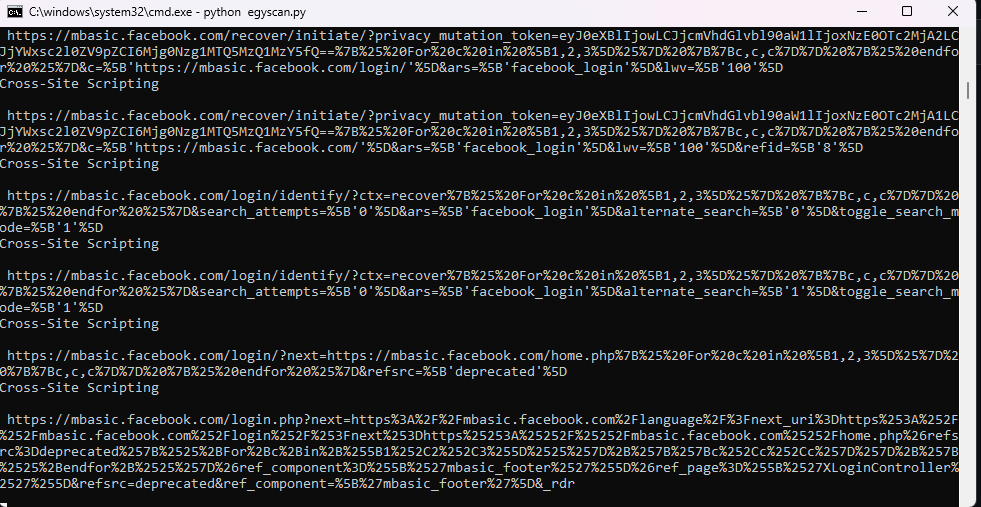 dragonked2/egyscan
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…
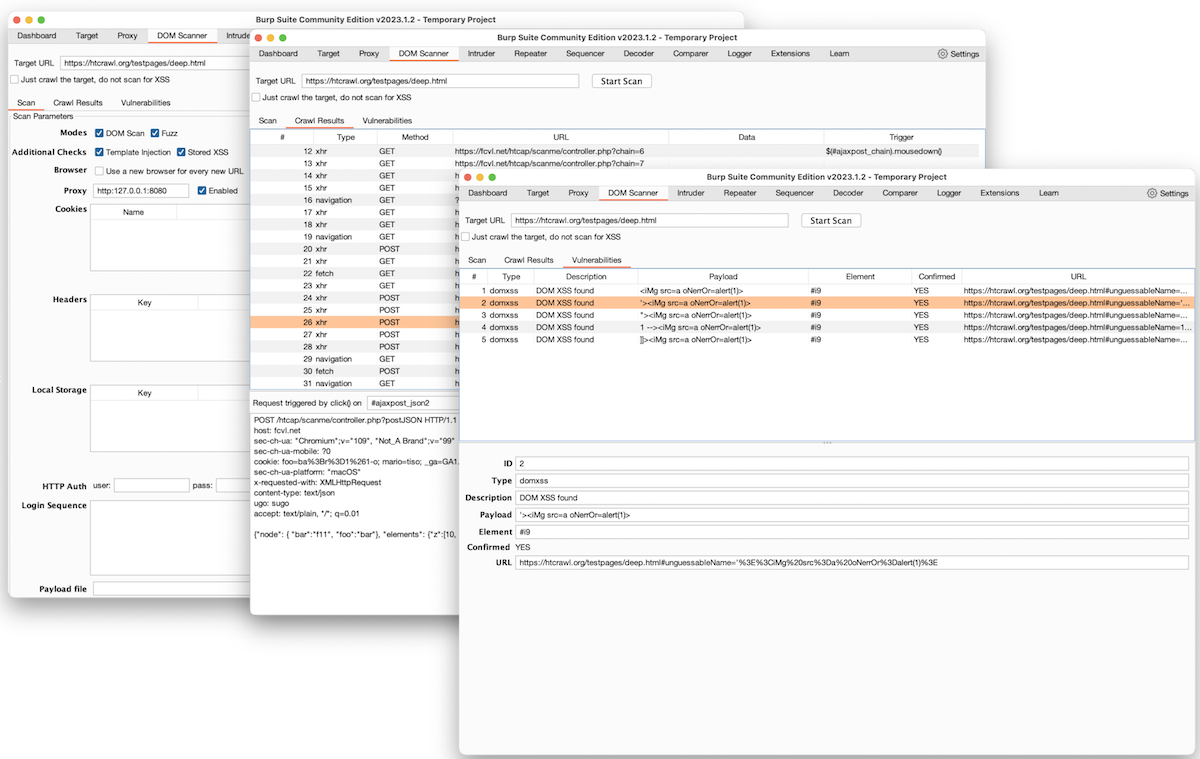 fcavallarin/burp-dom-scanner
Burp Suite's extension to scan and crawl Single Page Applications
 mhmdiaa/second-order
Crawls web applications to detect second-order subdomain takeover vulnerabilities by collecting URLs and matching configurable rules for non-200…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
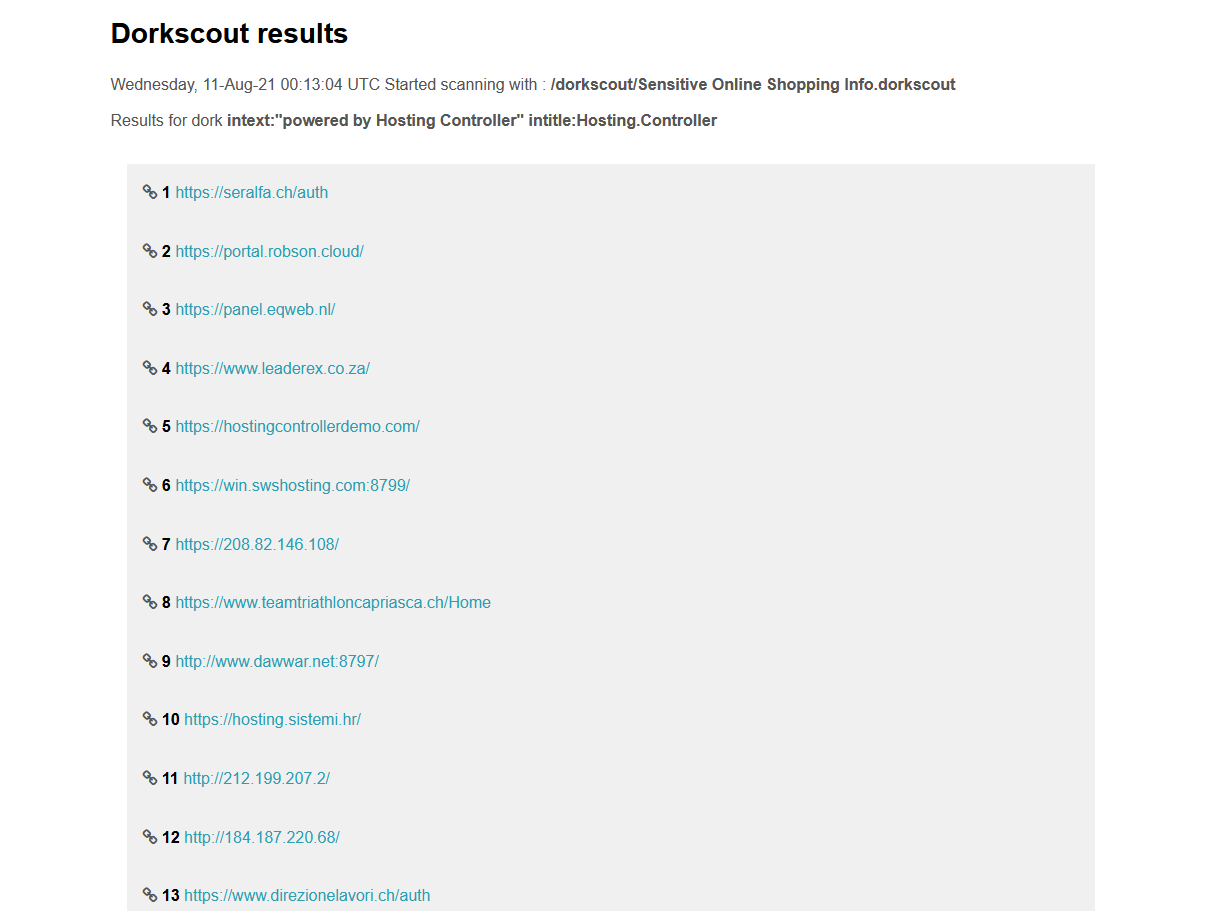 r4ygm/dorkscout
Automated Google dork scanner that fetches exploit-db dork lists and scans targets or the entire internet for vulnerable applications, secret files,…