
Snyk Scan
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
container-securitydevsecopssupply-chain-security+1
snyk/snyk-scanAutomated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
 hmlio/vaas-cve-2014-0160
Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed
 nu11secur1ty/cve-2021-44228-vuln-app
Dockerized vulnerable web application demonstrating the Log4j CVE-2021-44228 remote code execution vulnerability for educational exploitation and…
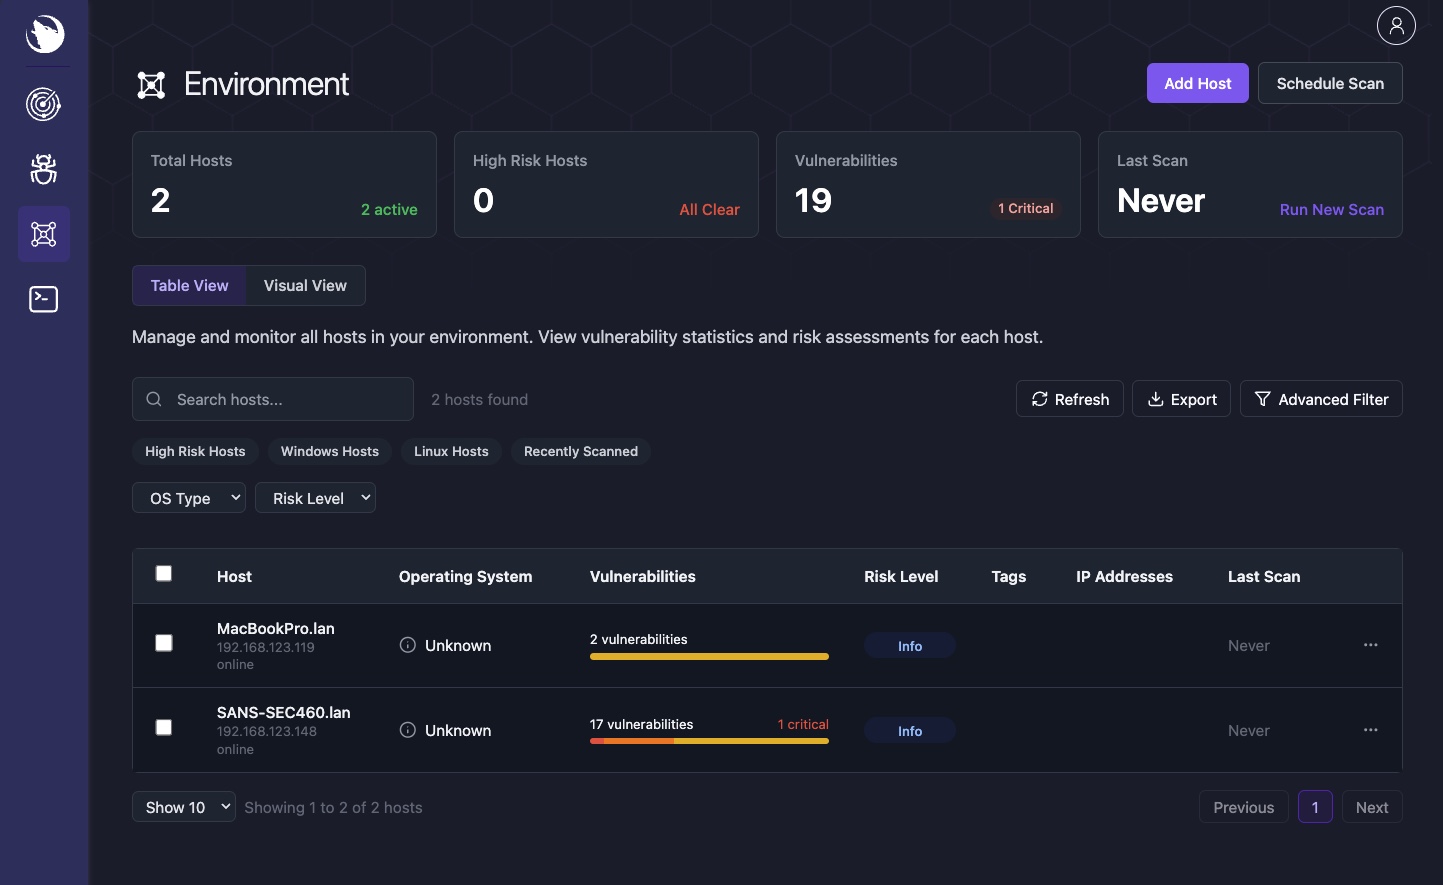 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 tuxotron/cve-2018-11776-docker
Dockerized proof-of-concept exploit for CVE-2018-11776 (Apache Struts2) with a Go-based command execution payload for penetration testing and…
 hackarada/cve-2015-3306
Dockerized exploit environment for CVE-2015-3306 (ProFTPD copy_file_range) with FTP and HTTP services for penetration testing and vulnerability…
 cved-sources/cve-2018-16283
Docker container for CVE-2018-16283, part of a managed vulnerable Docker environment for practicing exploitation and vulnerability analysis.
 cved-sources/cve-2014-6271
Docker container providing a vulnerable environment for CVE-2014-6271 (Shellshock) to practice exploitation and vulnerability analysis in a…
 cved-sources/cve-2018-19207
Docker container providing a vulnerable environment for CVE-2018-19207, designed for practicing exploitation and vulnerability analysis in a…
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 cirocosta/lighty-sqlinj-demo
Educational exploit demonstration of CVE-2014-2323 SQL injection in lighttpd's mod_mysql_vhost, with Docker-based lab for hands-on vulnerability…
 jas9reet/cve-2021-42013-lab
Docker-based lab environment for exploiting Apache HTTP Server 2.4.50 path traversal and RCE vulnerability (CVE-2021-42013) with automated exploit…
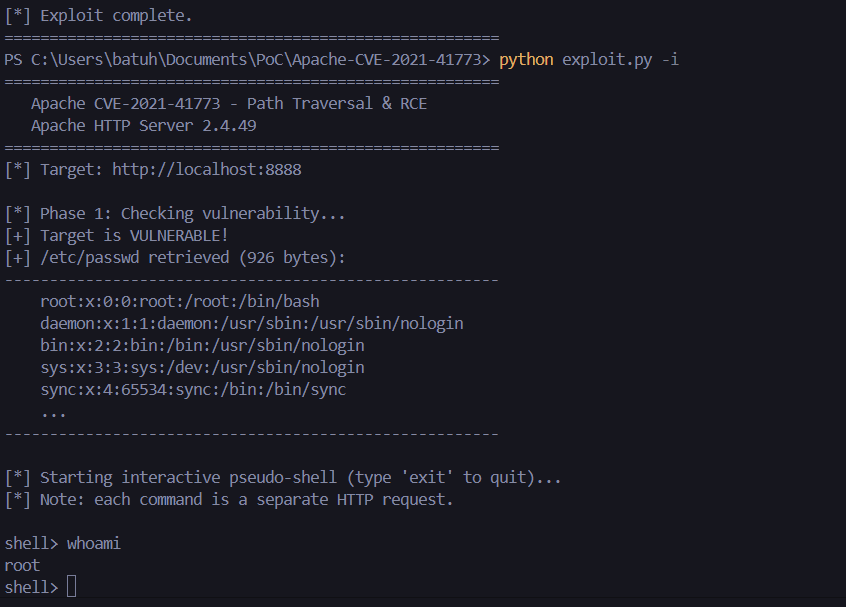 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
 rhbb/cve-2019-13956
Dockerized proof-of-concept exploit for CVE-2019-13956, targeting a web application vulnerability accessible via HTTP on port 8090.
 performant-labs/cve-2024-22262
Proof-of-concept exploit for CVE-2024-22262 in Spring applications, with a Dev Container environment for hands-on vulnerability exploration and…