

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
10.8k1 day ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 rezilion/mi-x
Determine whether your compute is truly vulnerable to a specific vulnerability by accounting for all factors which affect *actual* exploitability…
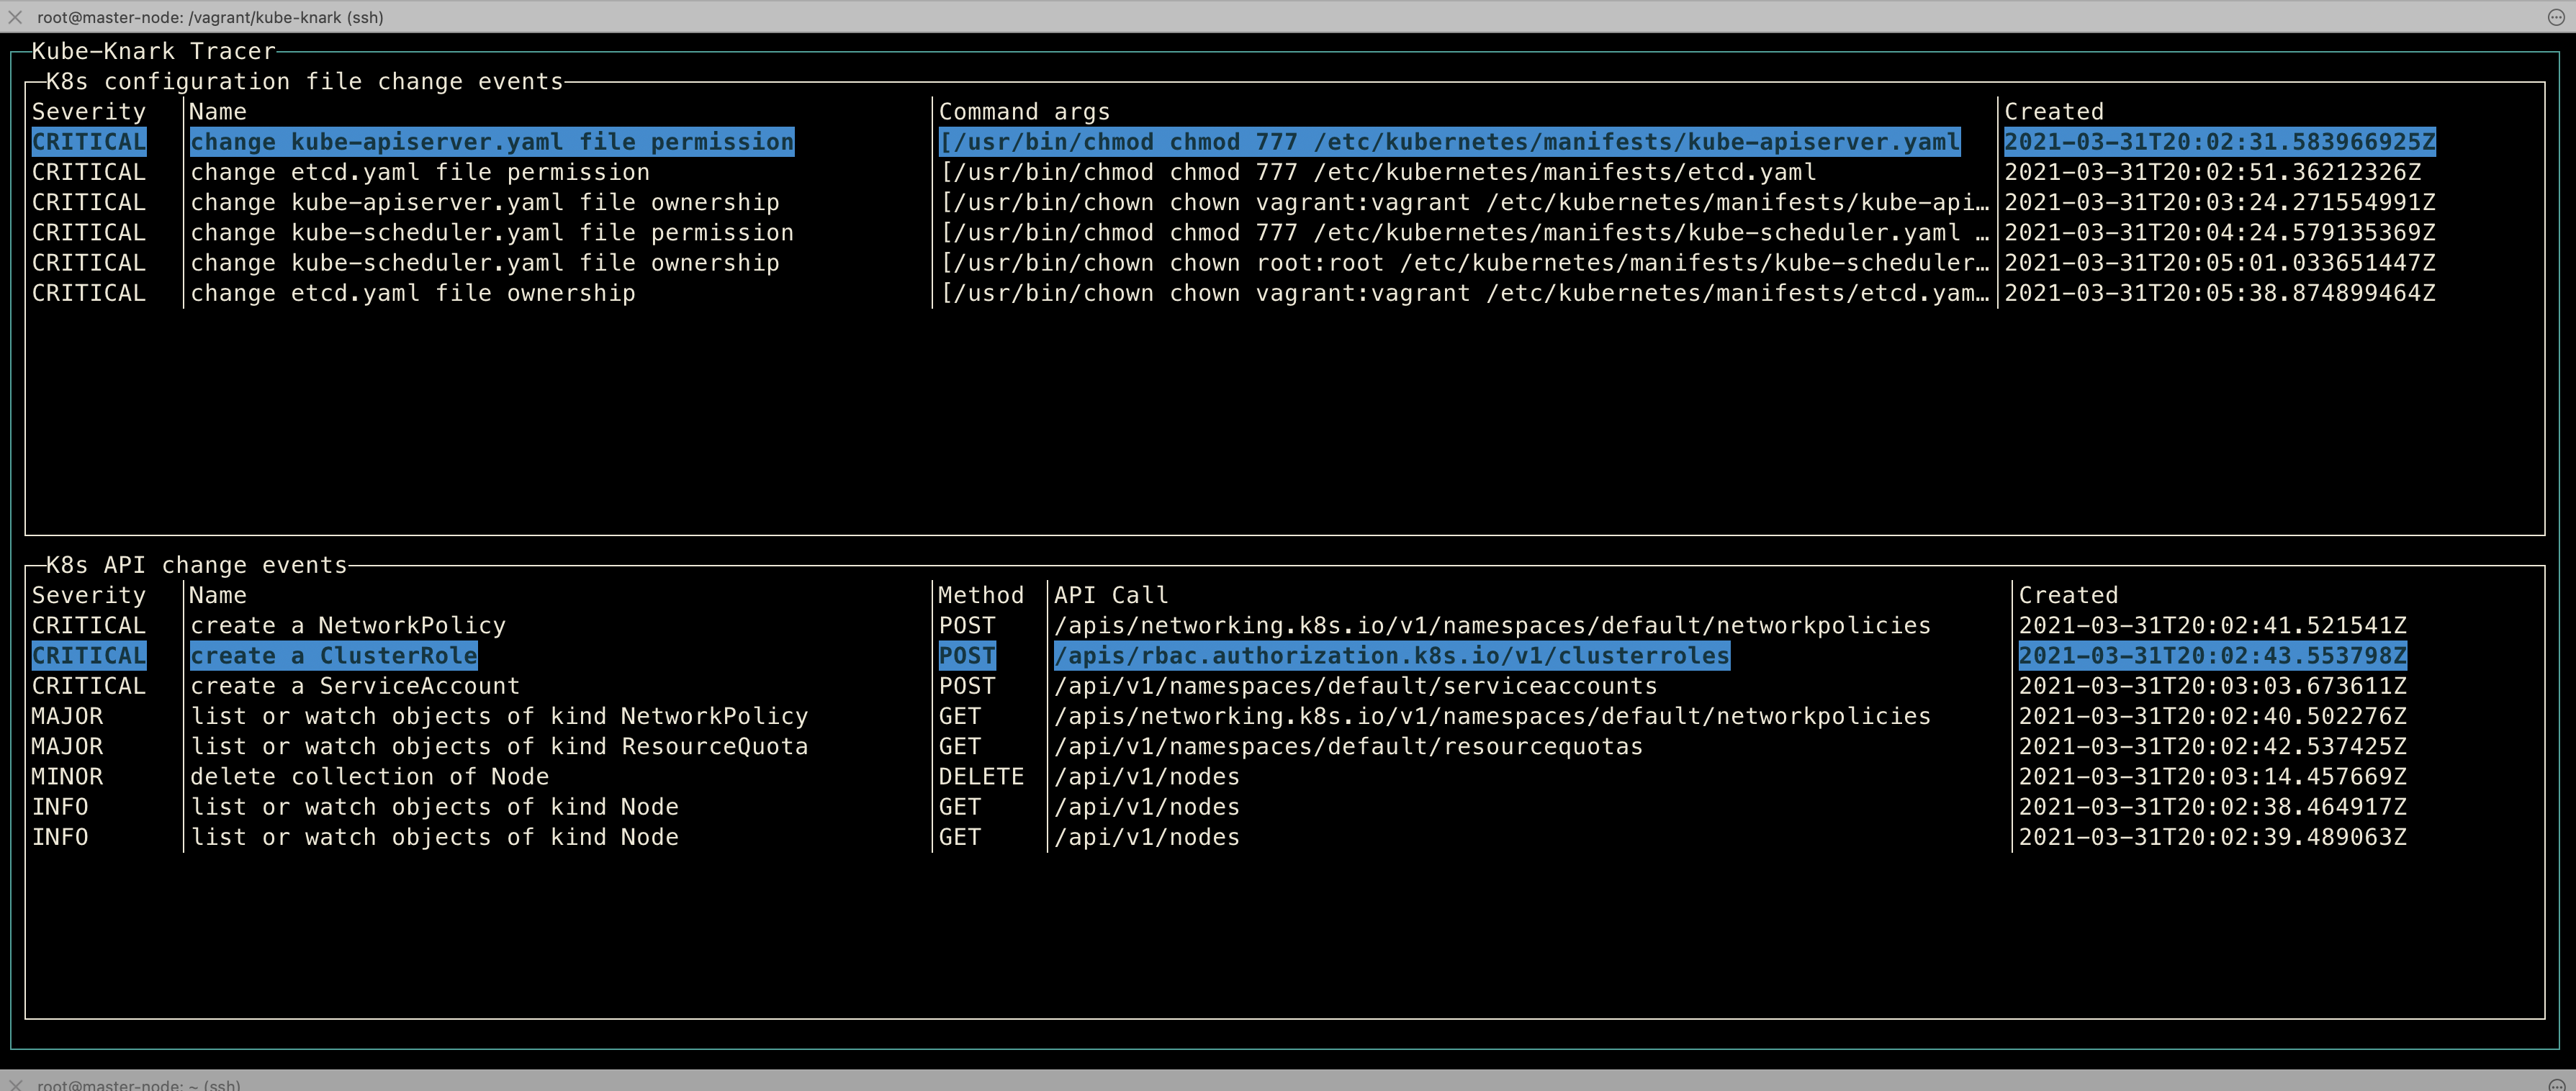 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 cashwilliams/cve-2019-14287-demo
This is a container built for demonstration purposes that has a version of the sudo command which is vulnerable to CVE-2019-14287
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
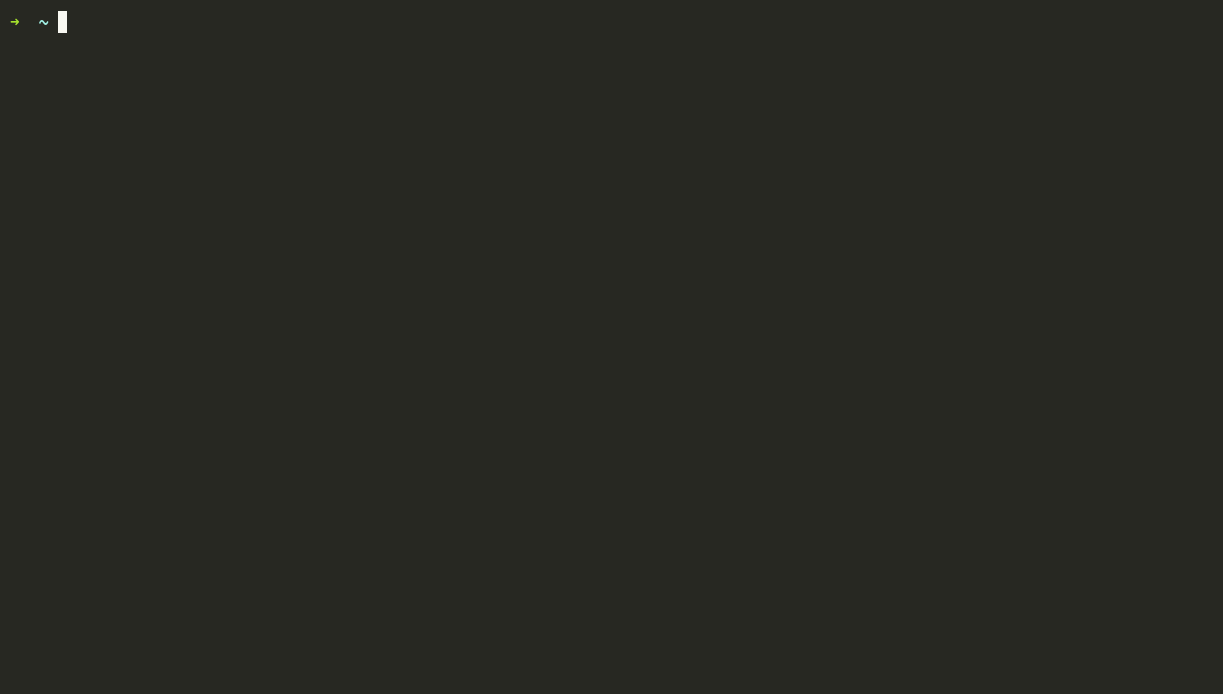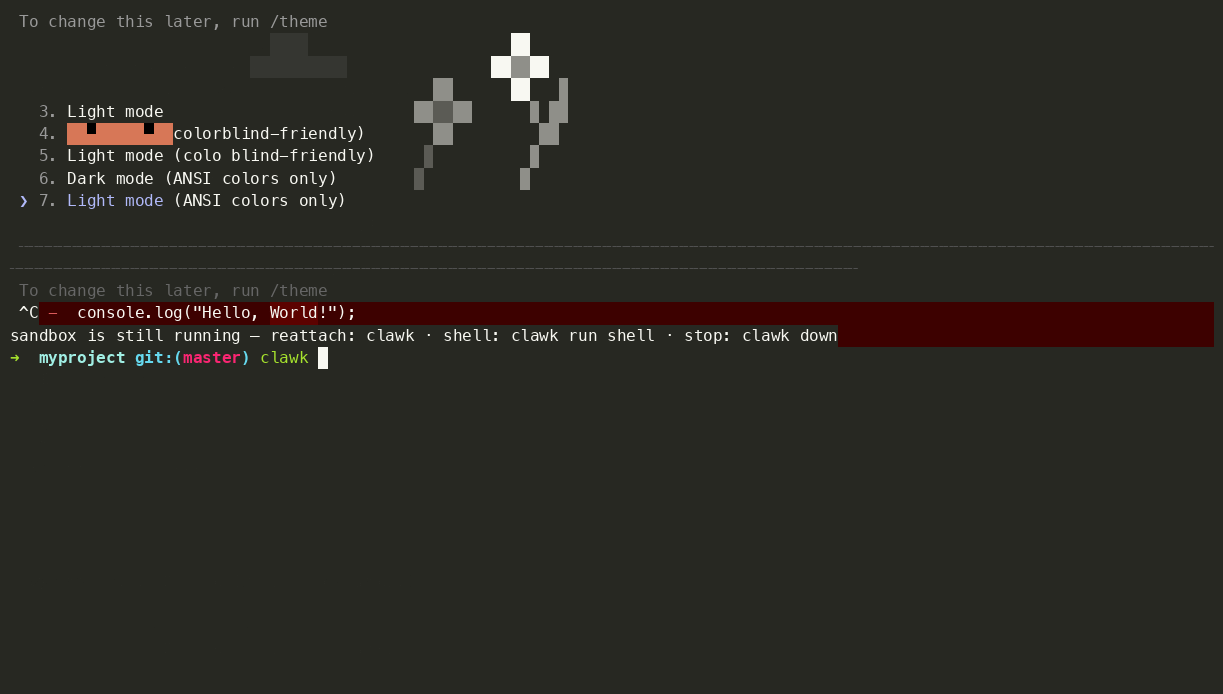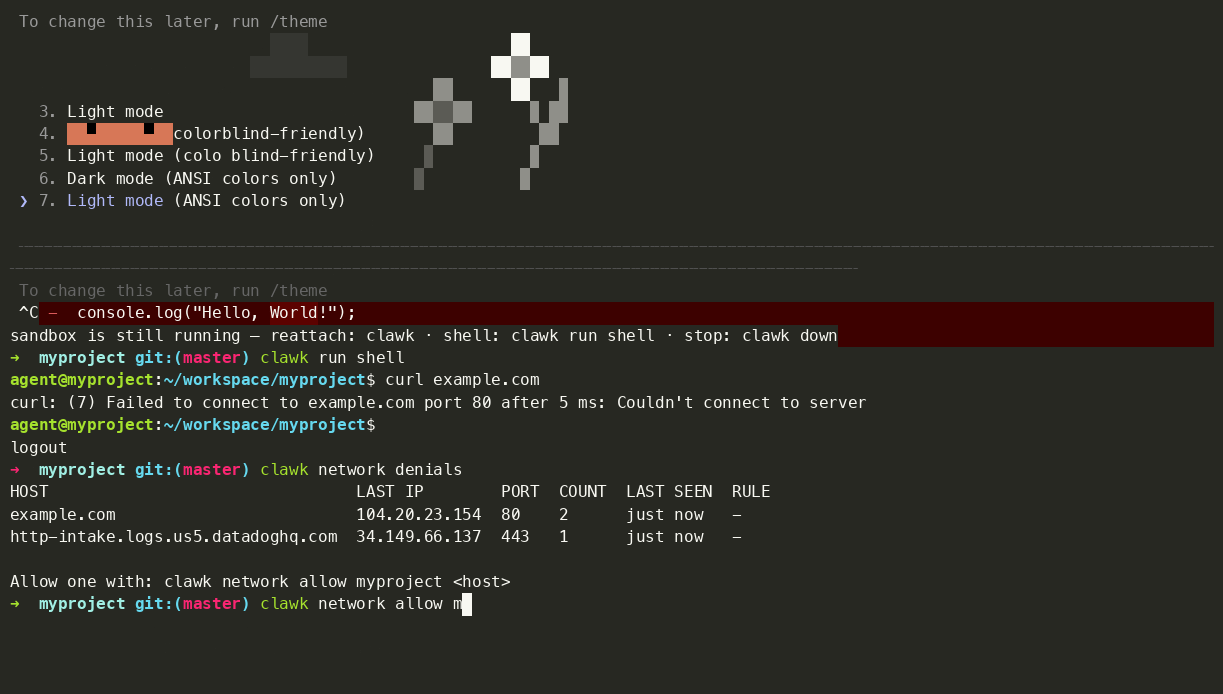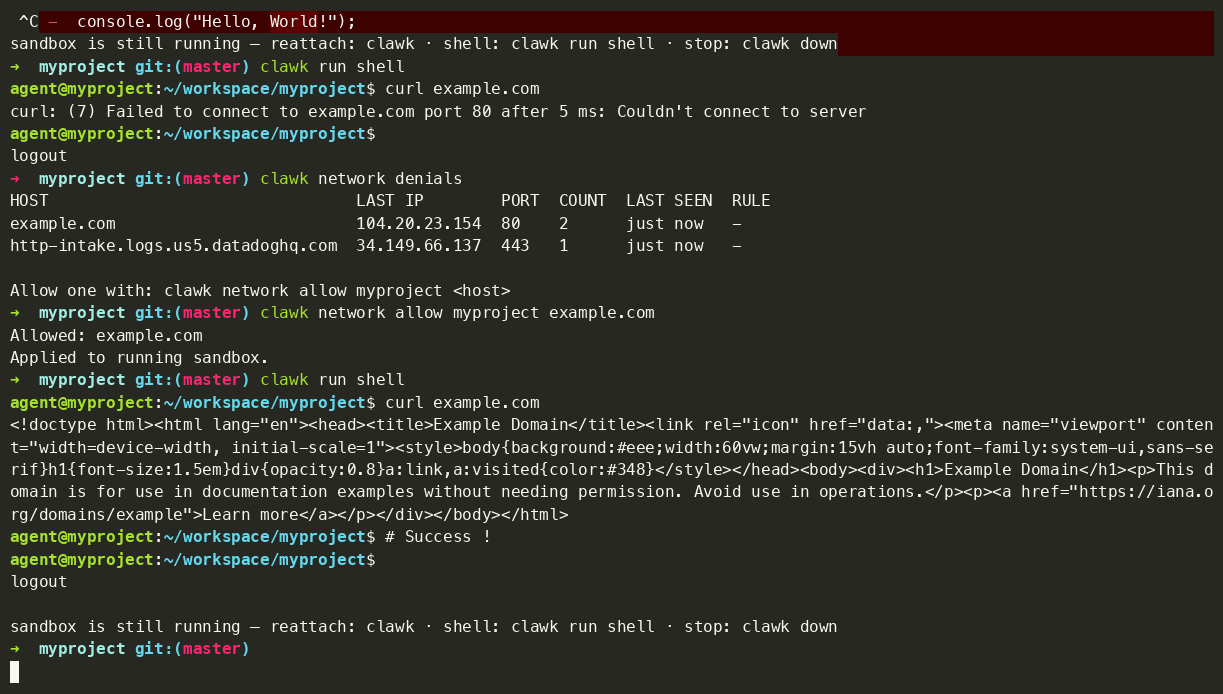 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 liske/needrestart
System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
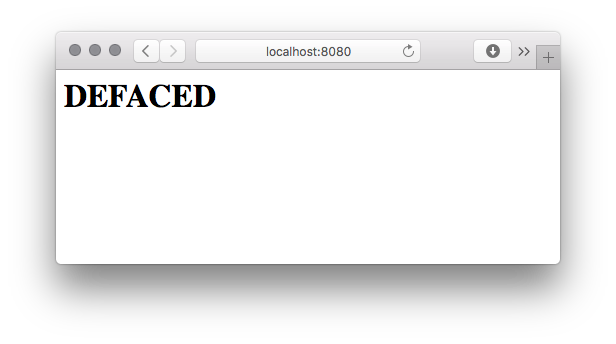 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 opsxcq/exploit-cve-2016-6515
OpenSSH remote DOS exploit and vulnerable container
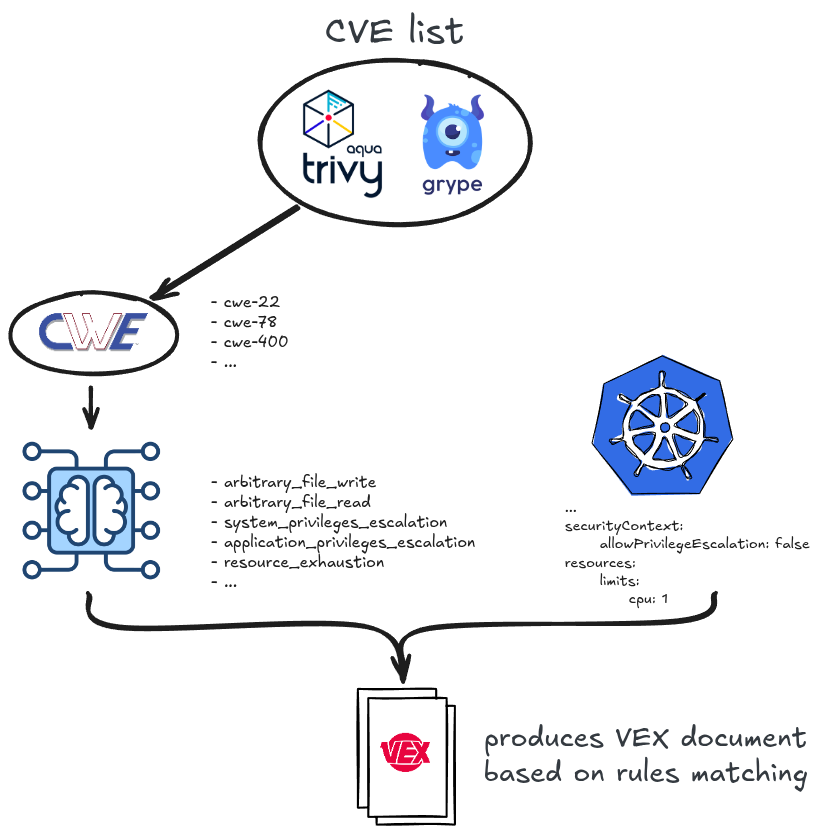 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 opsxcq/exploit-cve-2016-7434
NTPD remote DOS exploit and vulnerable container