
nanoclaw
 nanocoai/nanoclaw
A lightweight alternative to OpenClaw that runs in containers for security. Connects to WhatsApp, Telegram, Slack, Discord, Gmail and other messaging…
ai-securitycloud-securitycontainer-security+4
31.0k
nanocoai/nanoclawA lightweight alternative to OpenClaw that runs in containers for security. Connects to WhatsApp, Telegram, Slack, Discord, Gmail and other messaging…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 blessedrebus/krawl
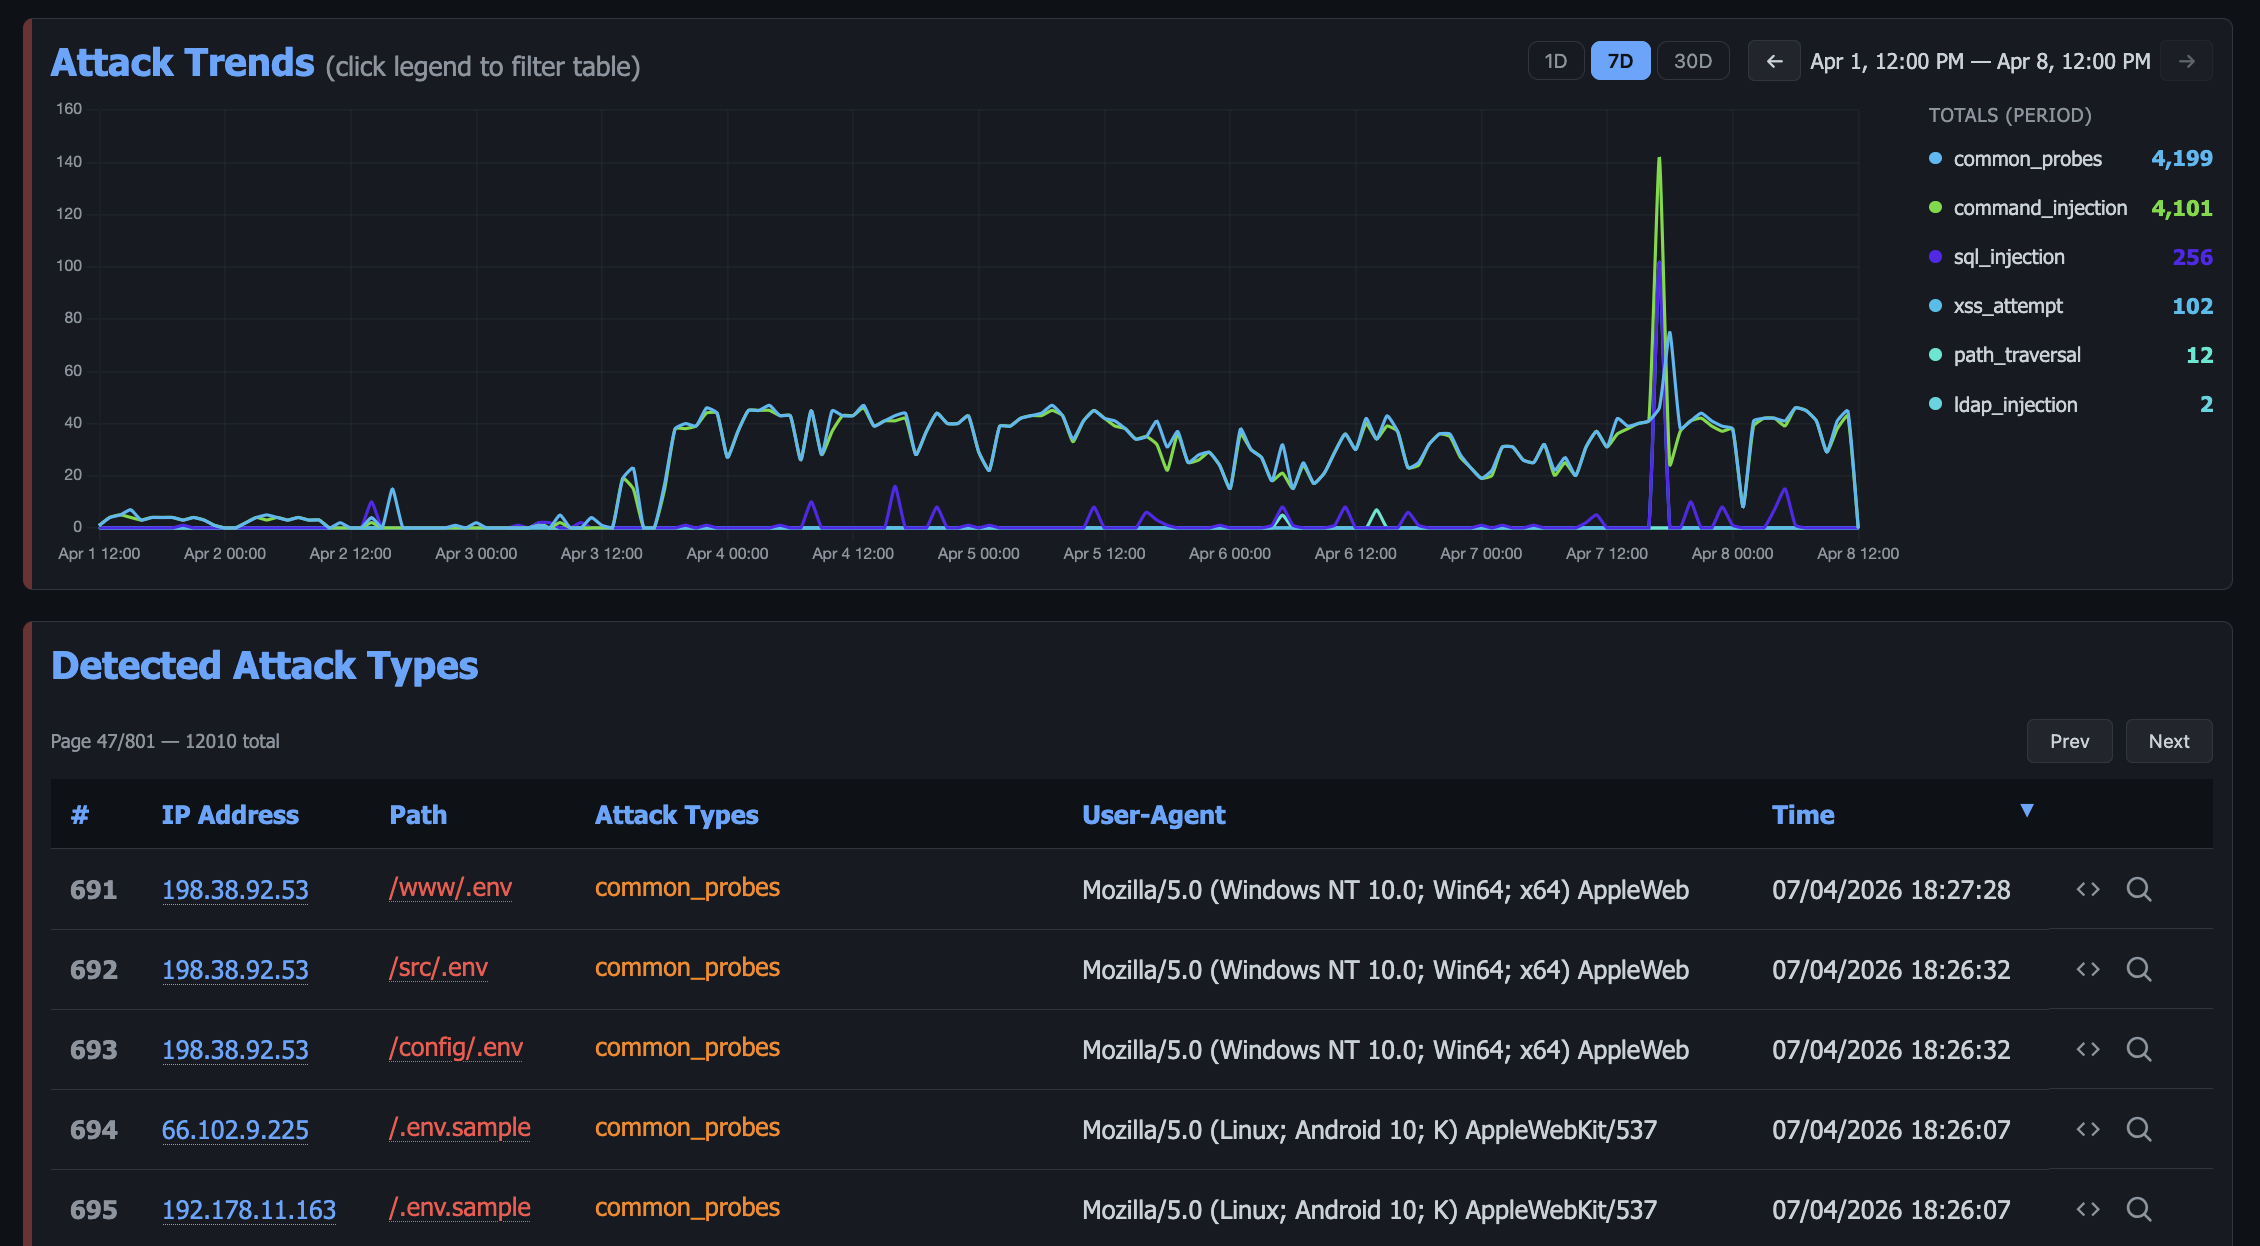
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 afshinm/zerobox
Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
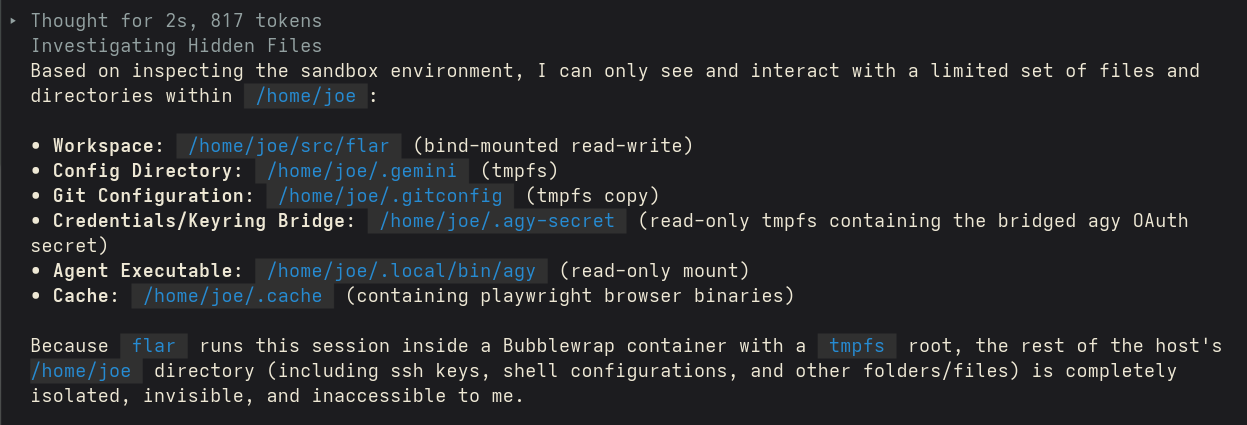 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
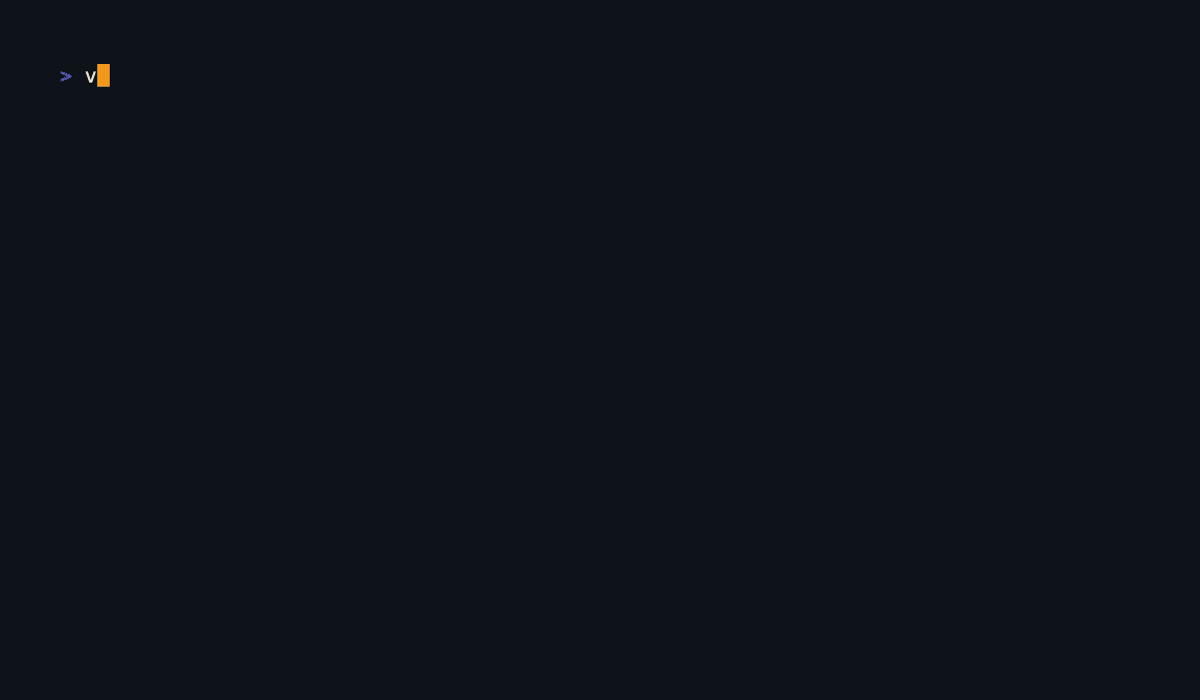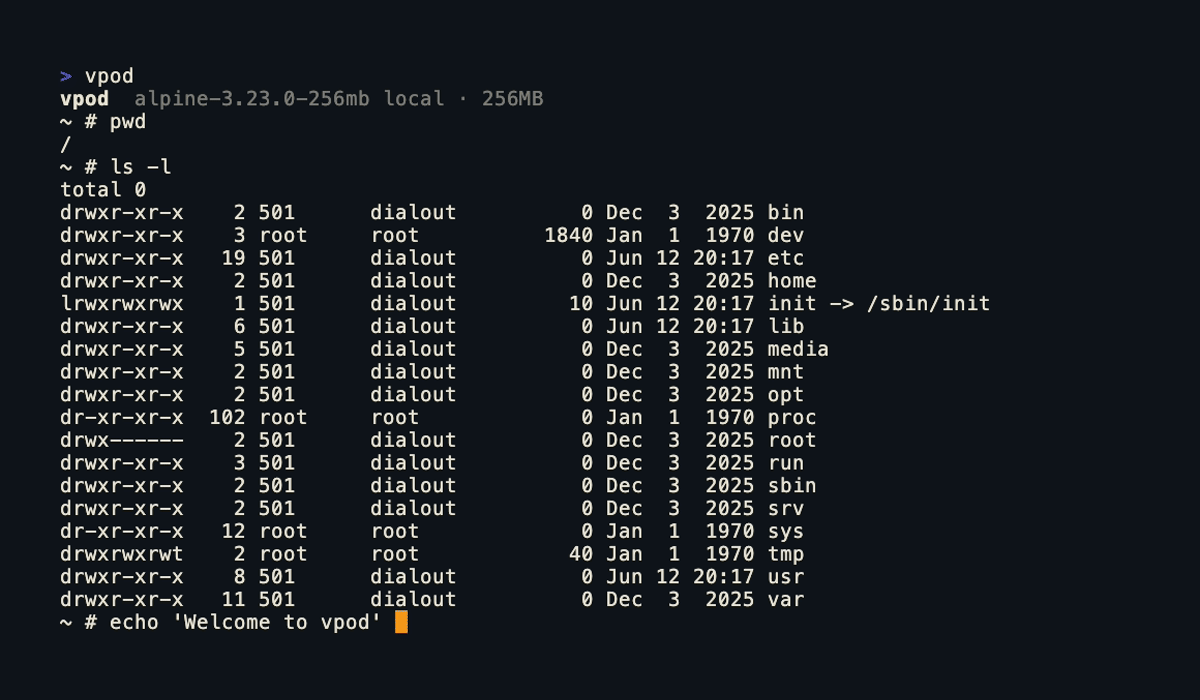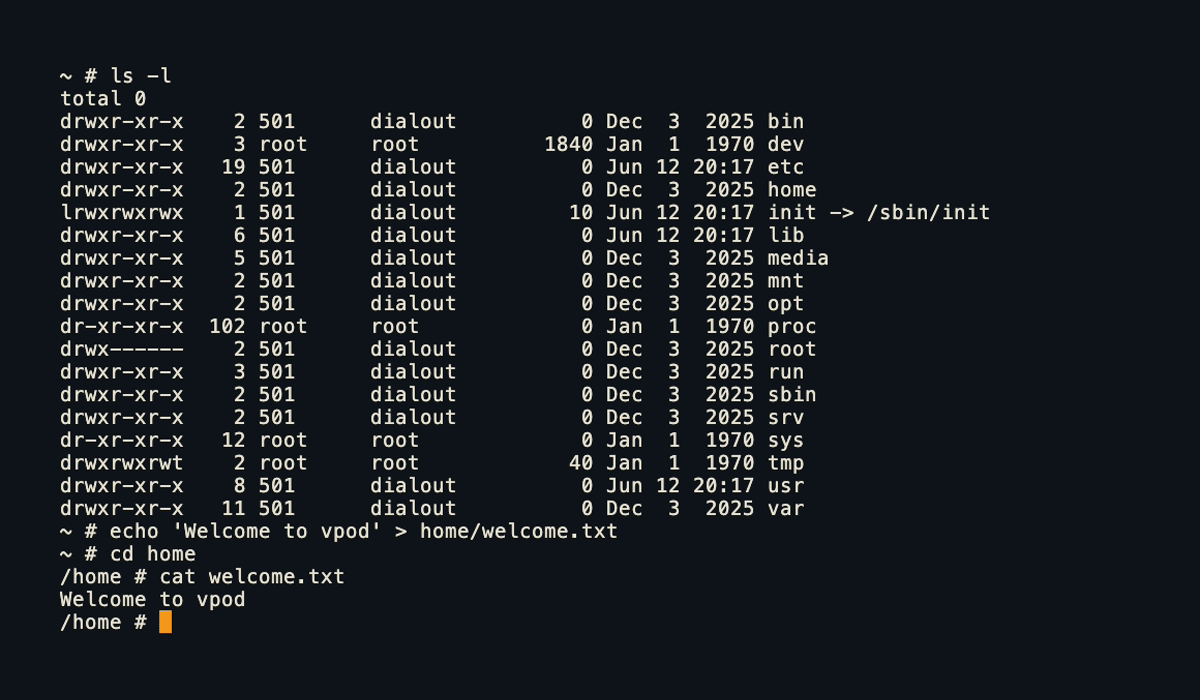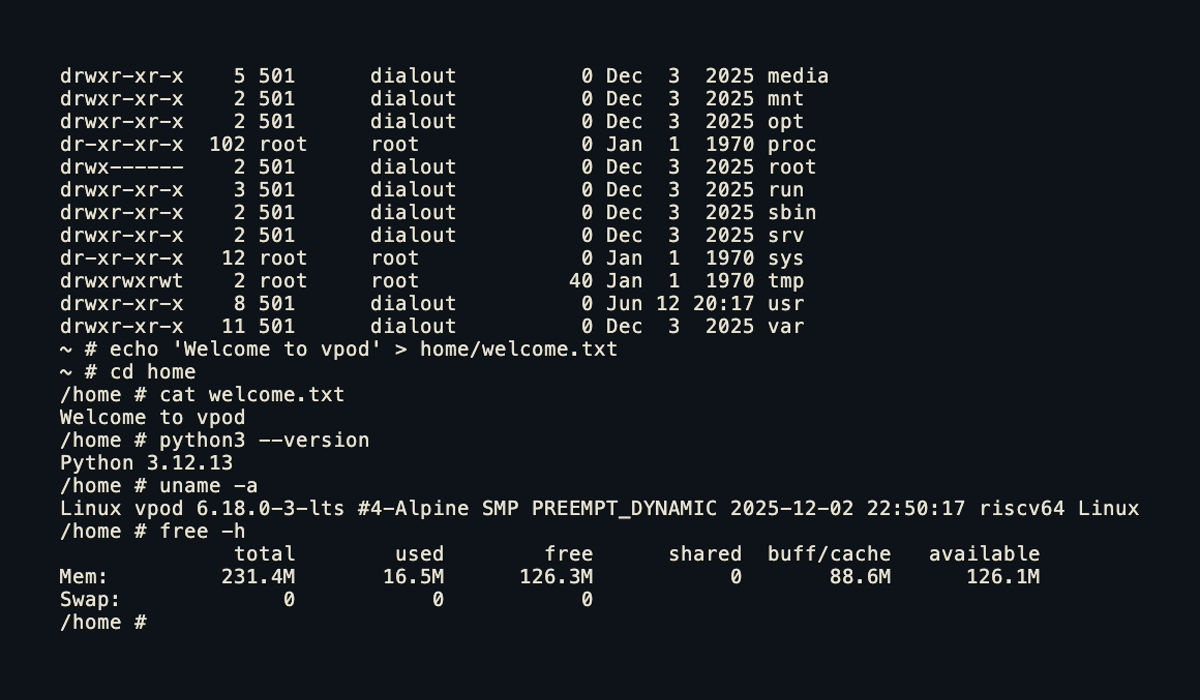 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
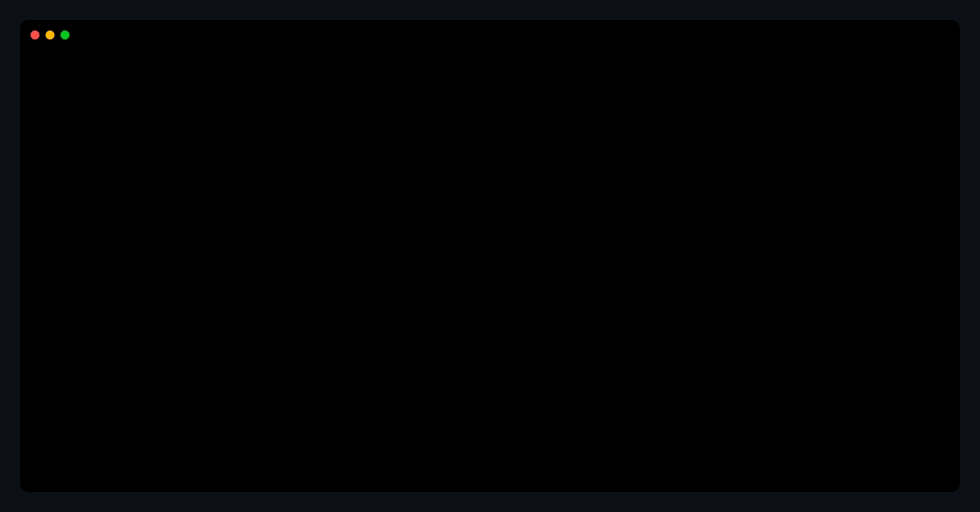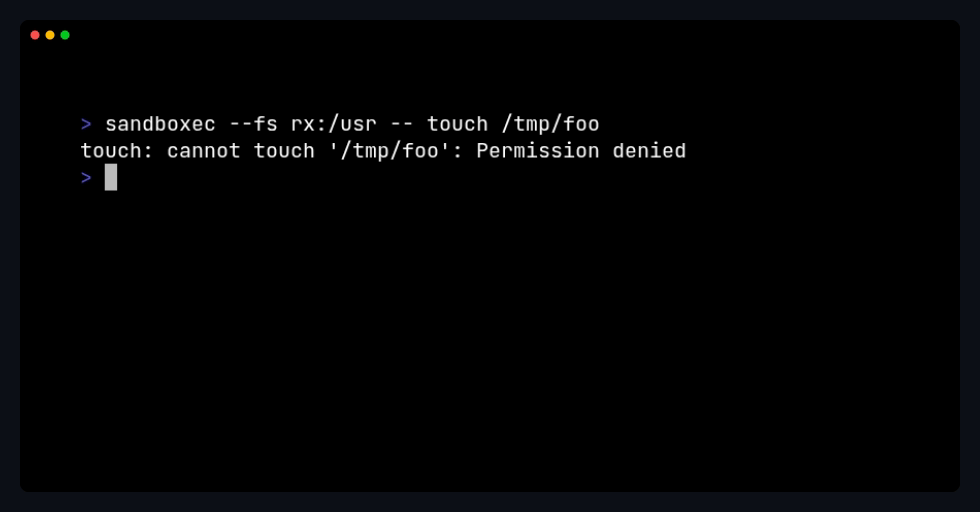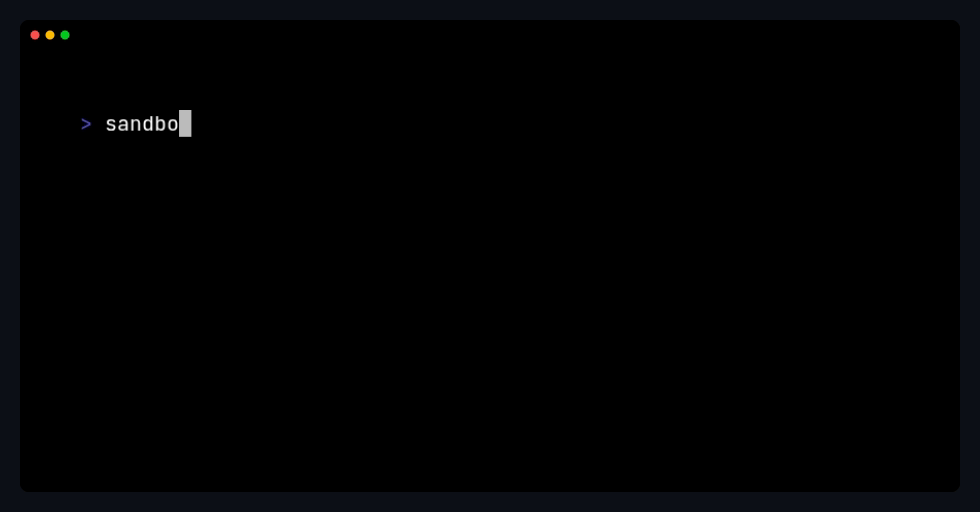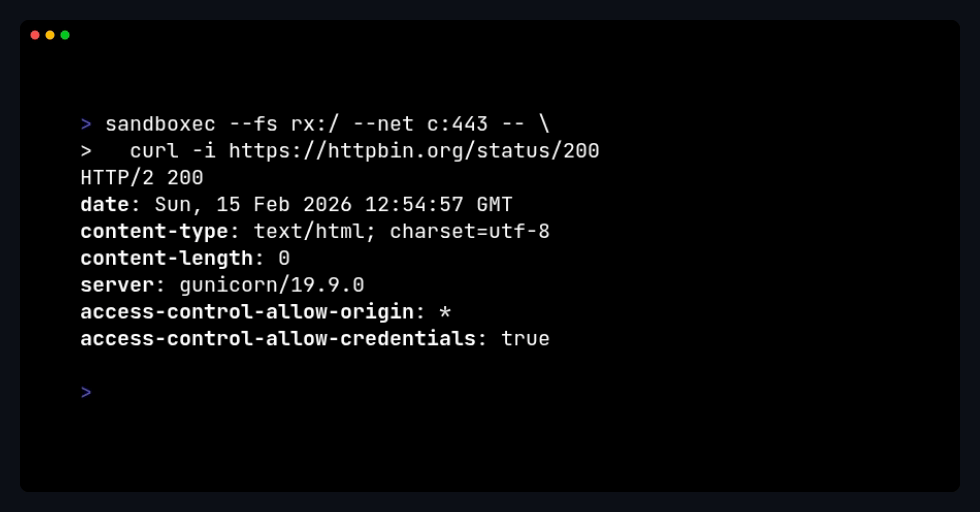 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 mrmahile/massscanning-cve-2025-55182
A lightweight orchestrator and worker scanner setup for running large/continuous scans across split input files. This repository contains…
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 cloudflare/flan
A pretty sweet vulnerability scanner
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 vanigori/cve-2023-38545-sample
Dockerfile containing all the necessary setup files to demo the exploit