
log4shell_sentinel
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
container-securityforensicsincident-response+3
13
ossie-git/log4shell_sentinelA Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
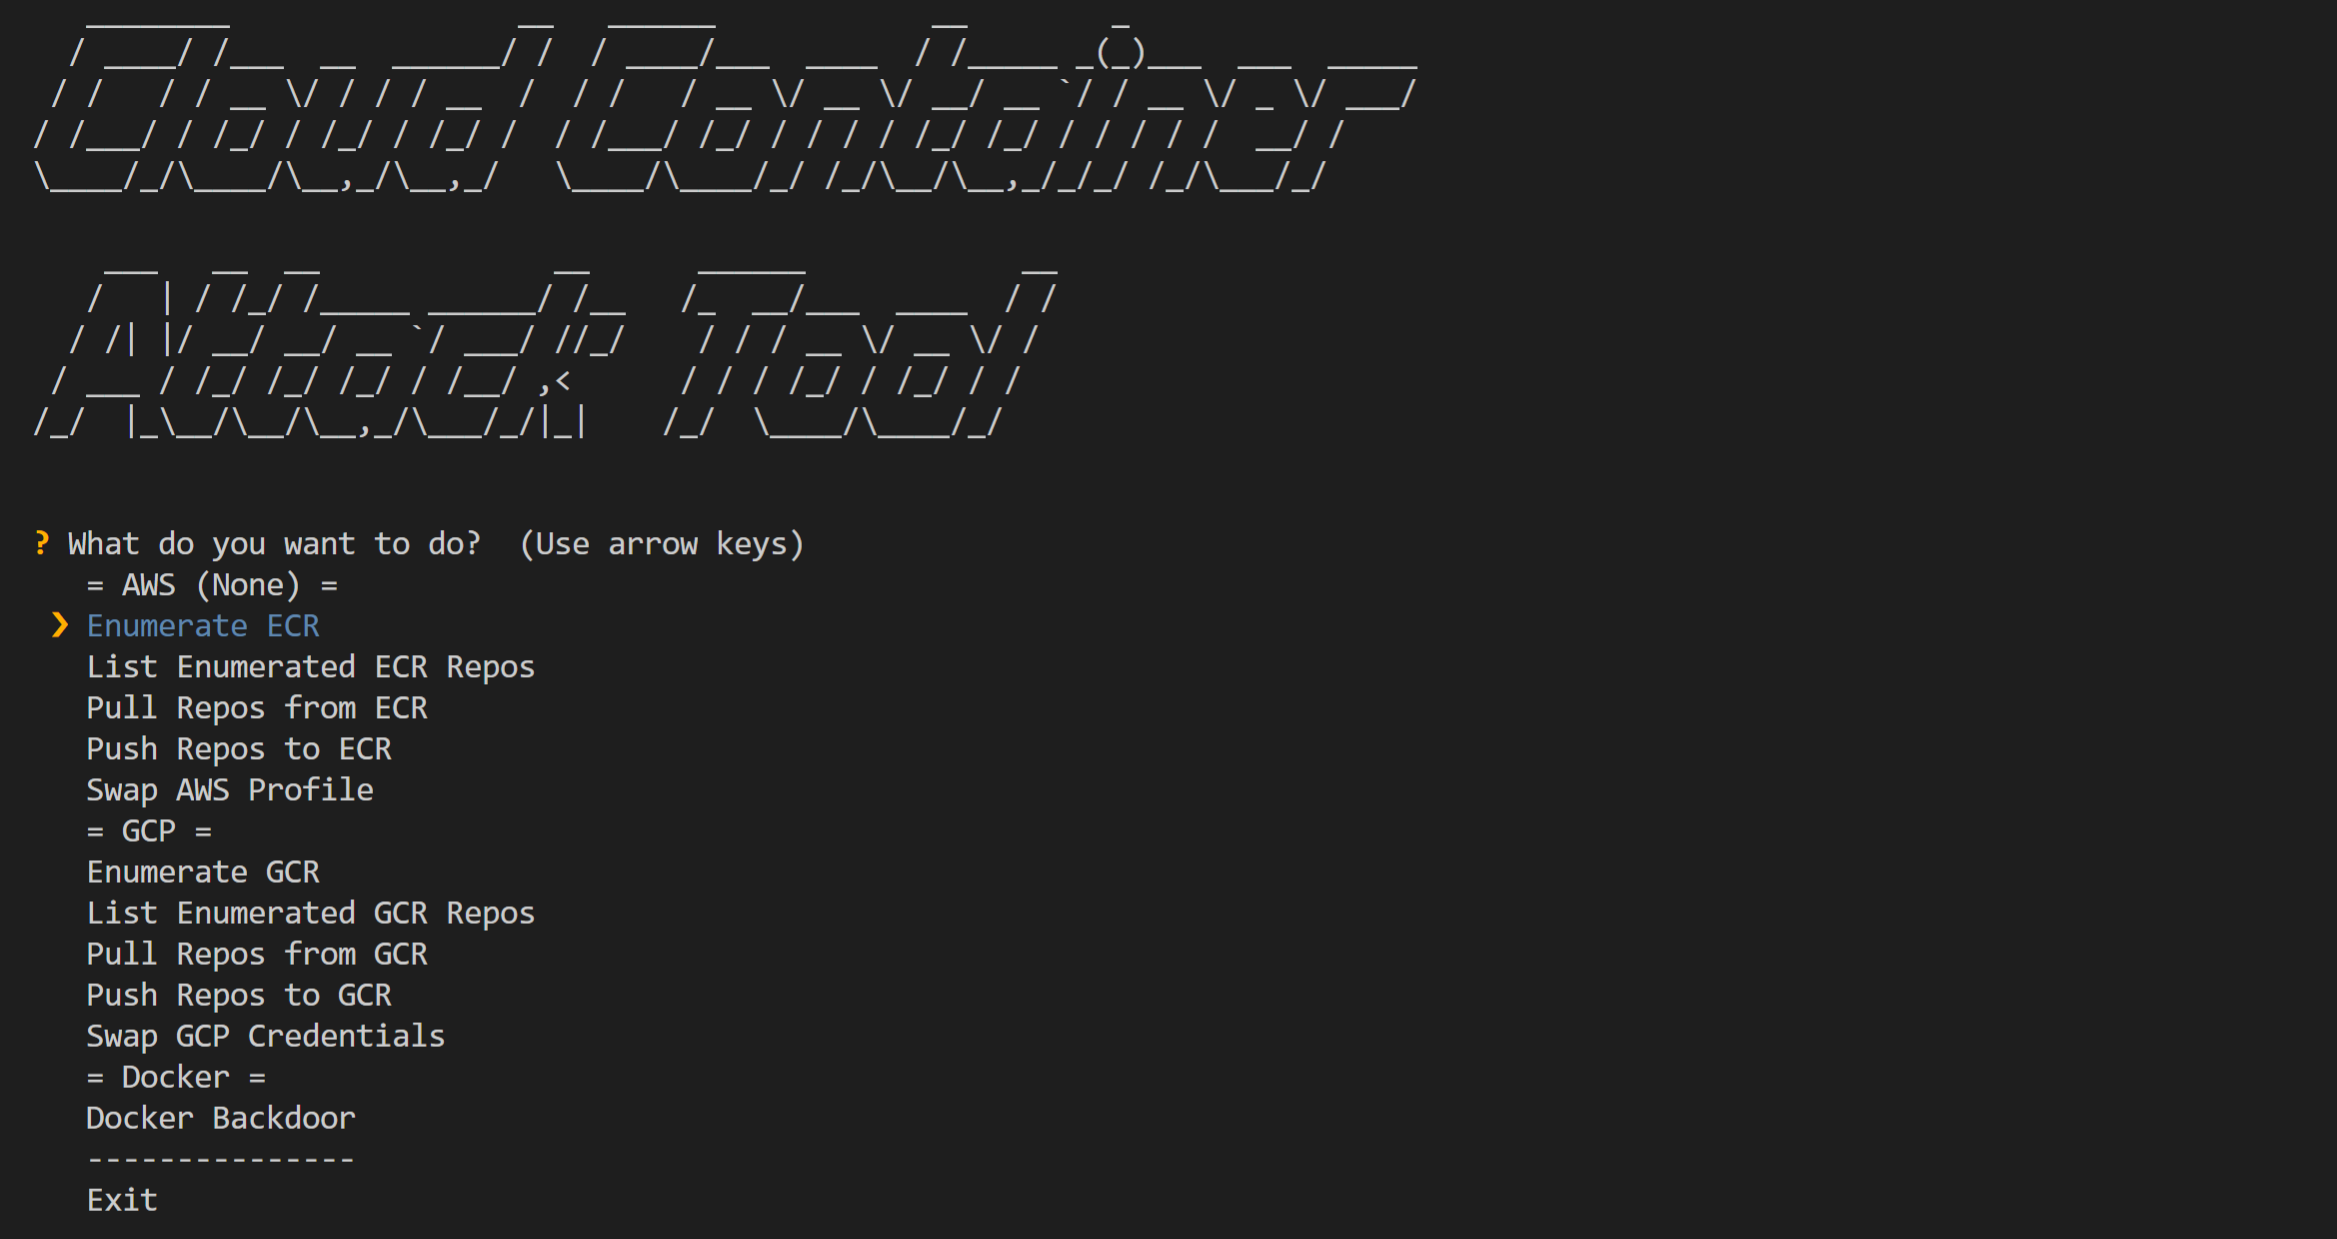 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 cved-sources/cve-2015-8103
Docker container for CVE-2015-8103 exploitation targeting JBoss, part of a vulnerable container management framework for security testing.
 0xbingo/cve-2025-1974
A minimal test tool to help detect annotation injection vulnerabilities in Kubernetes NGINX Ingress controllers. This script sends a crafted…
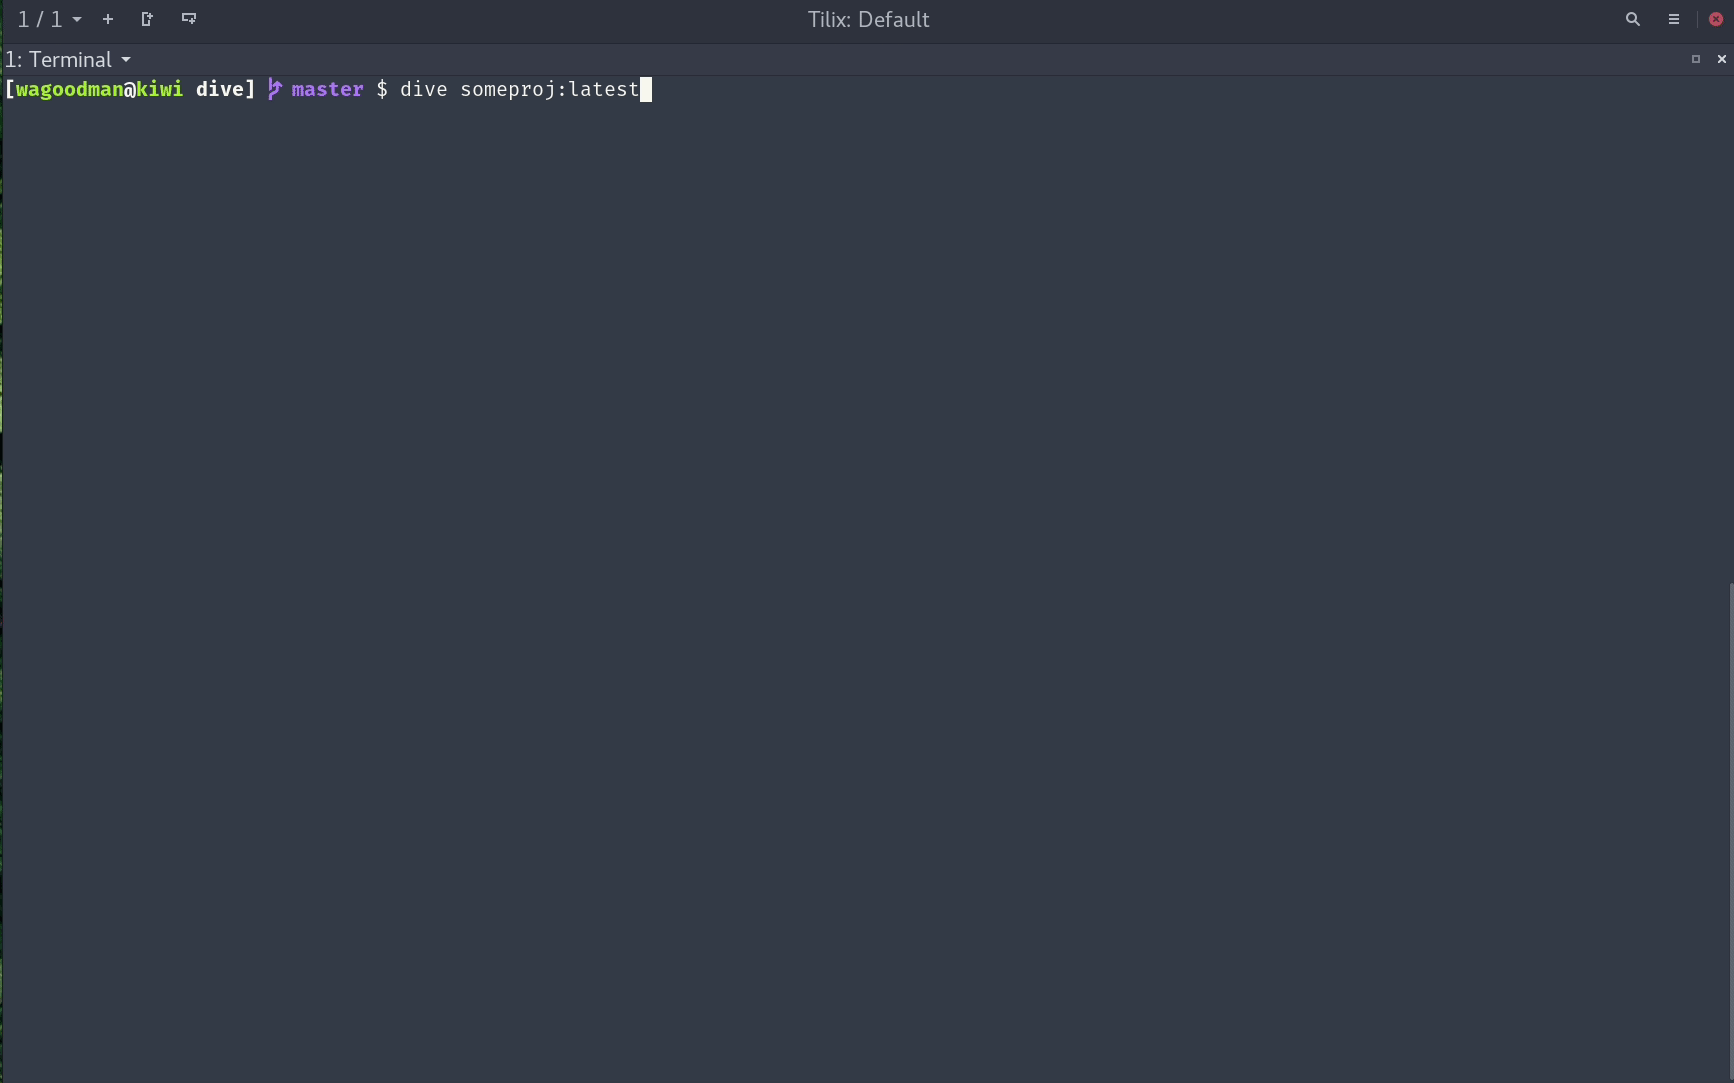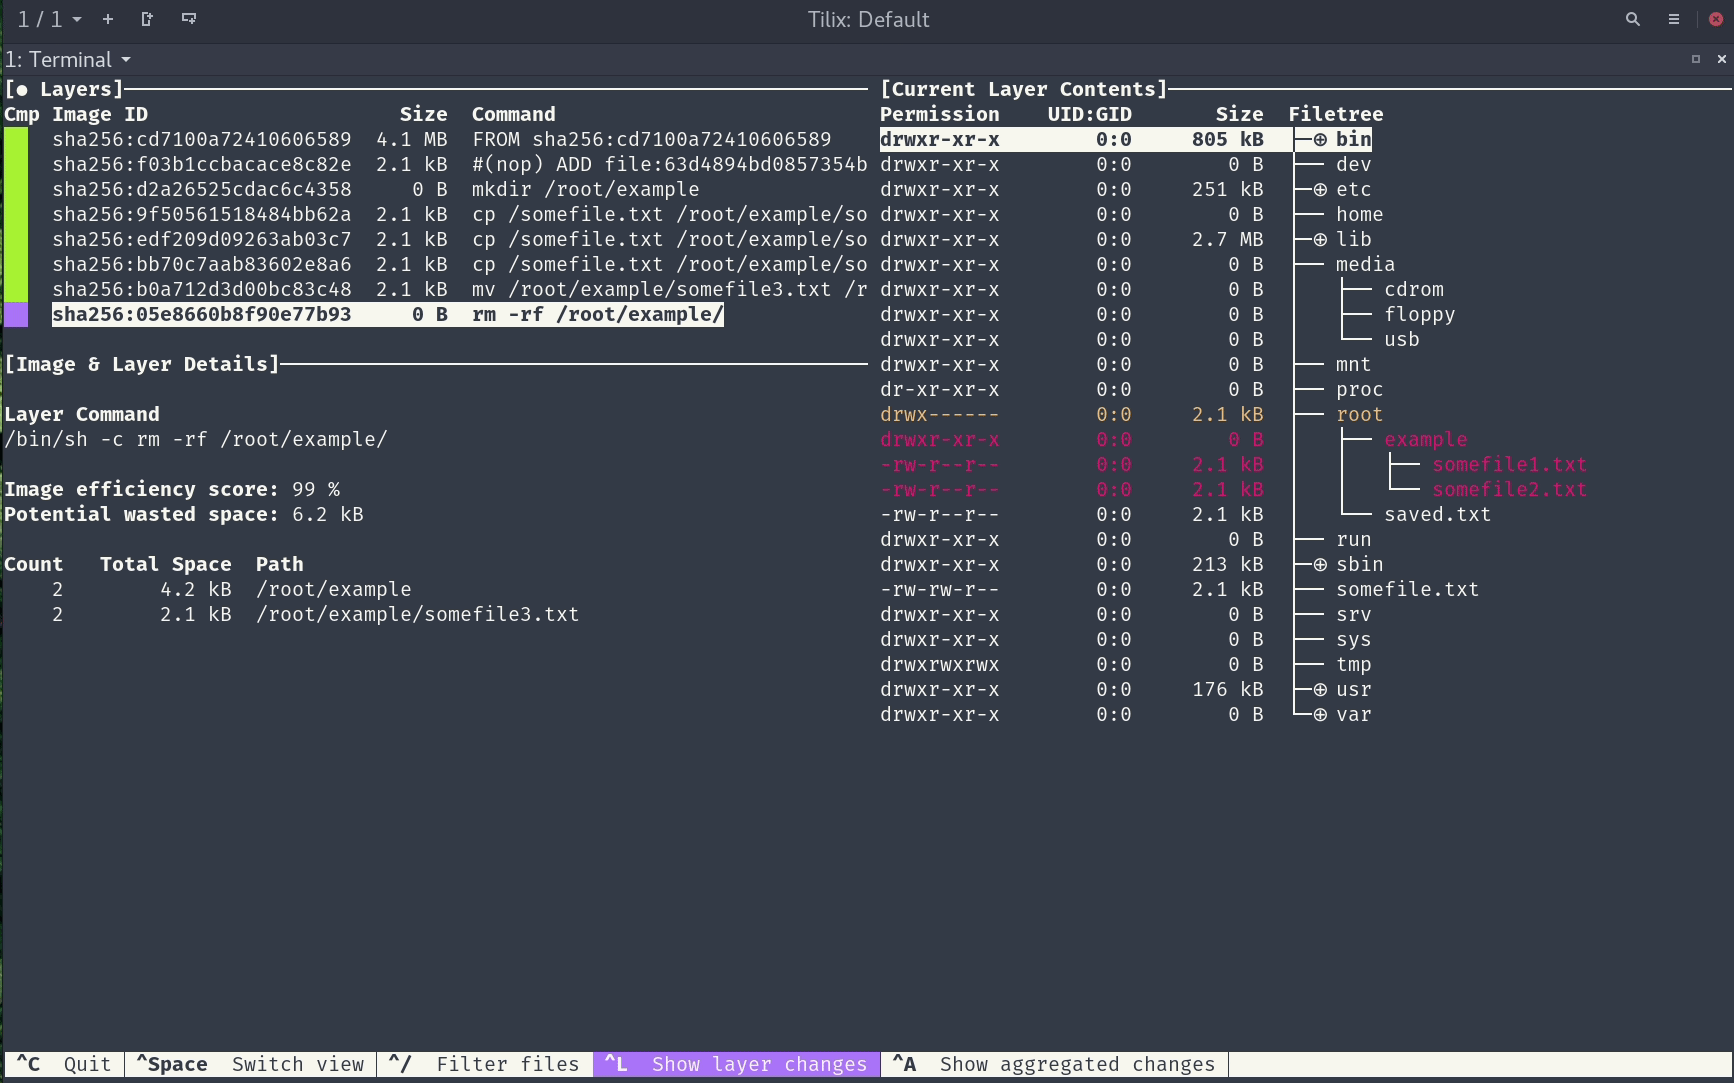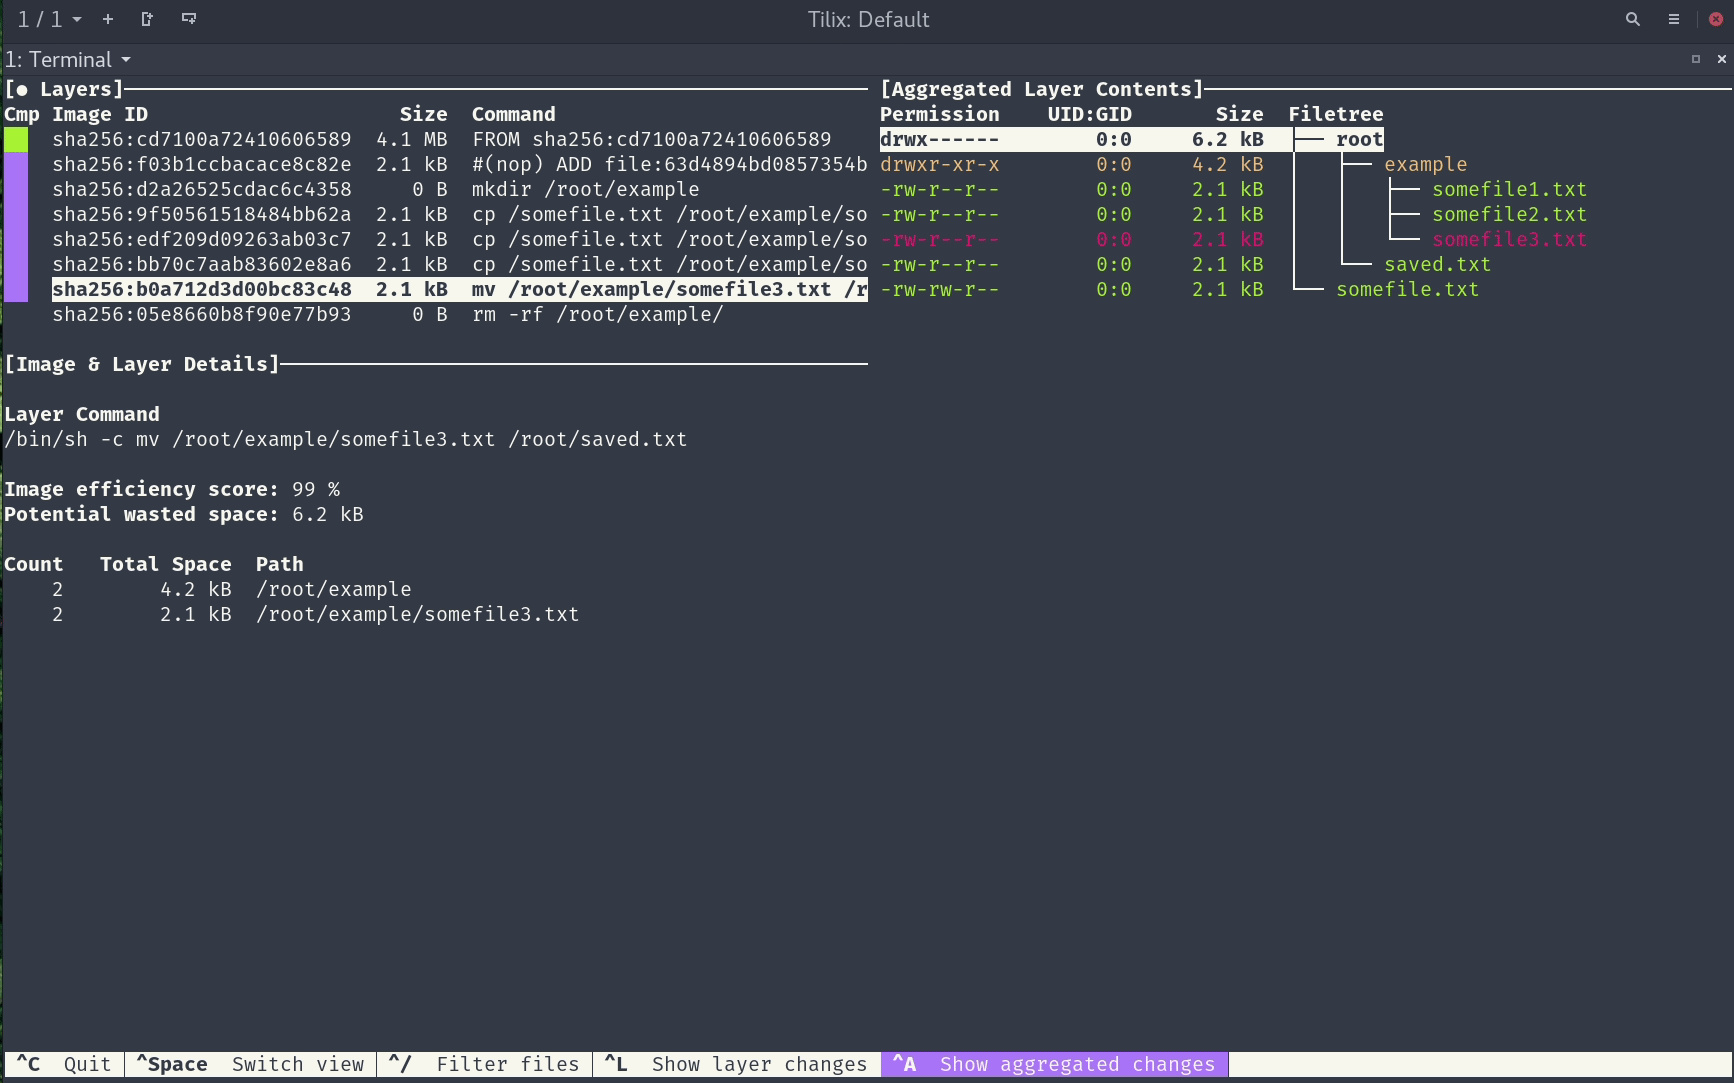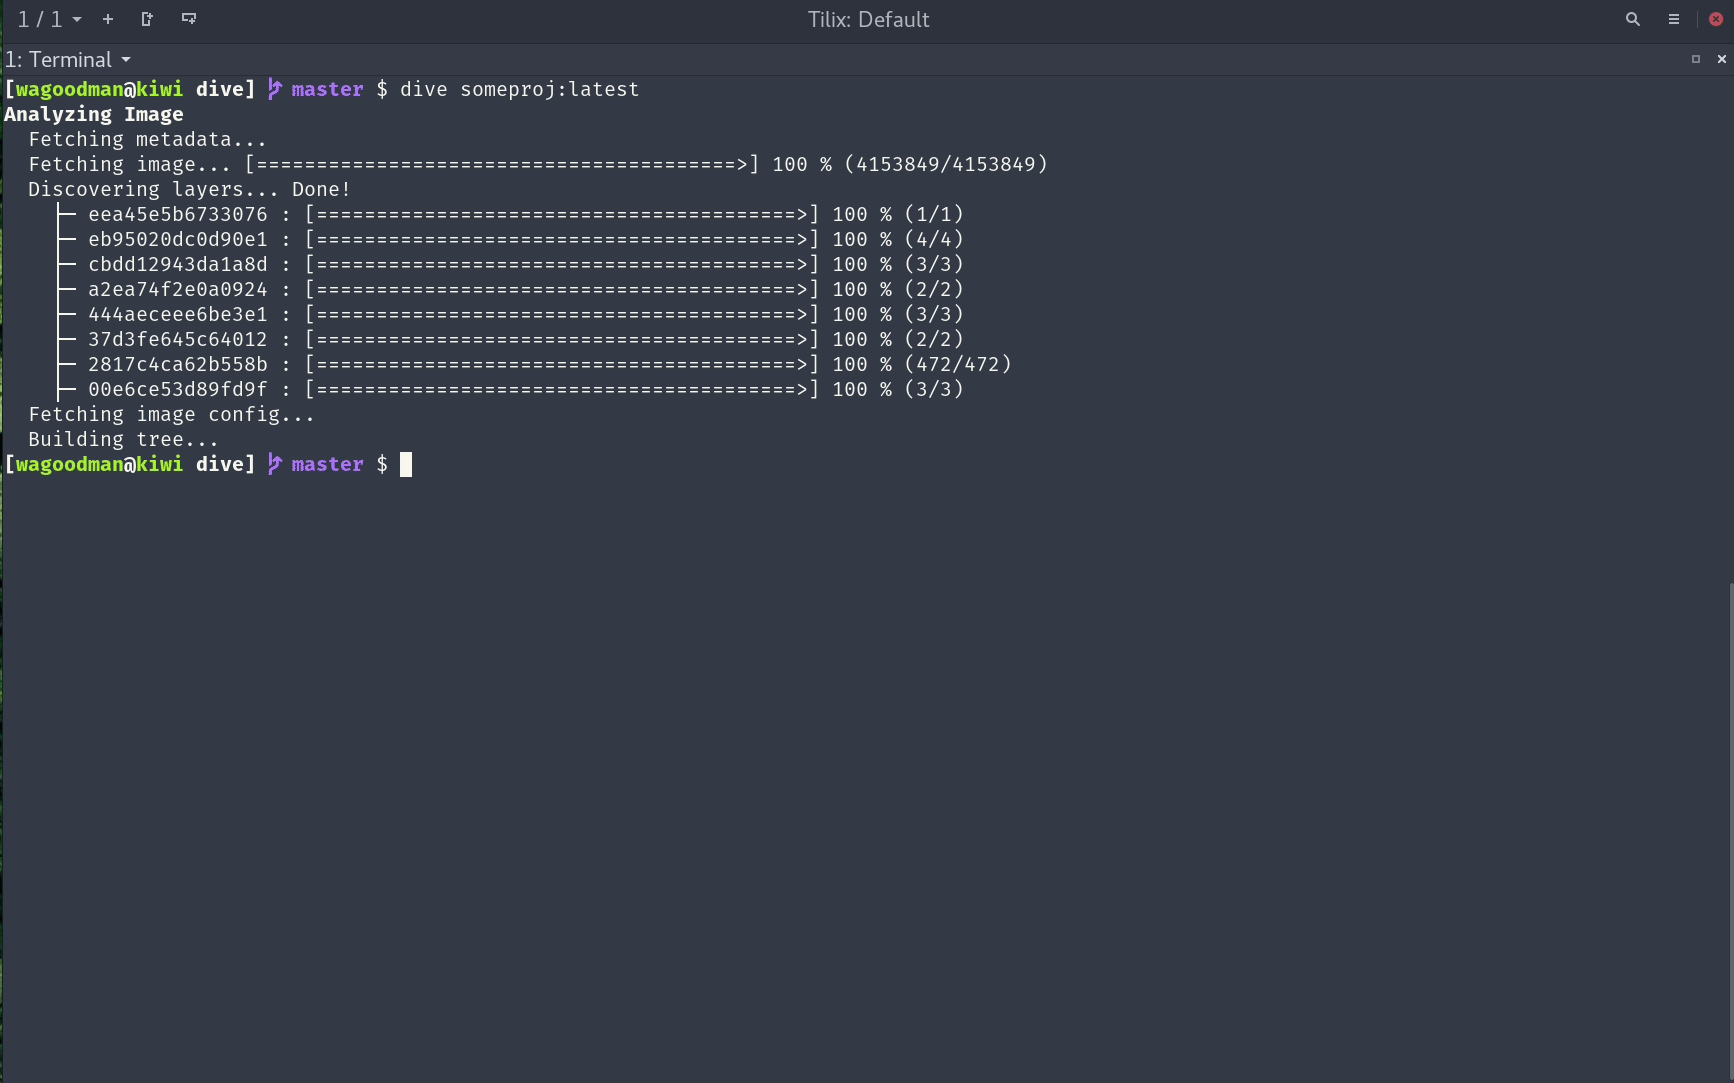 wagoodman/dive
A tool for exploring each layer in a docker image
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
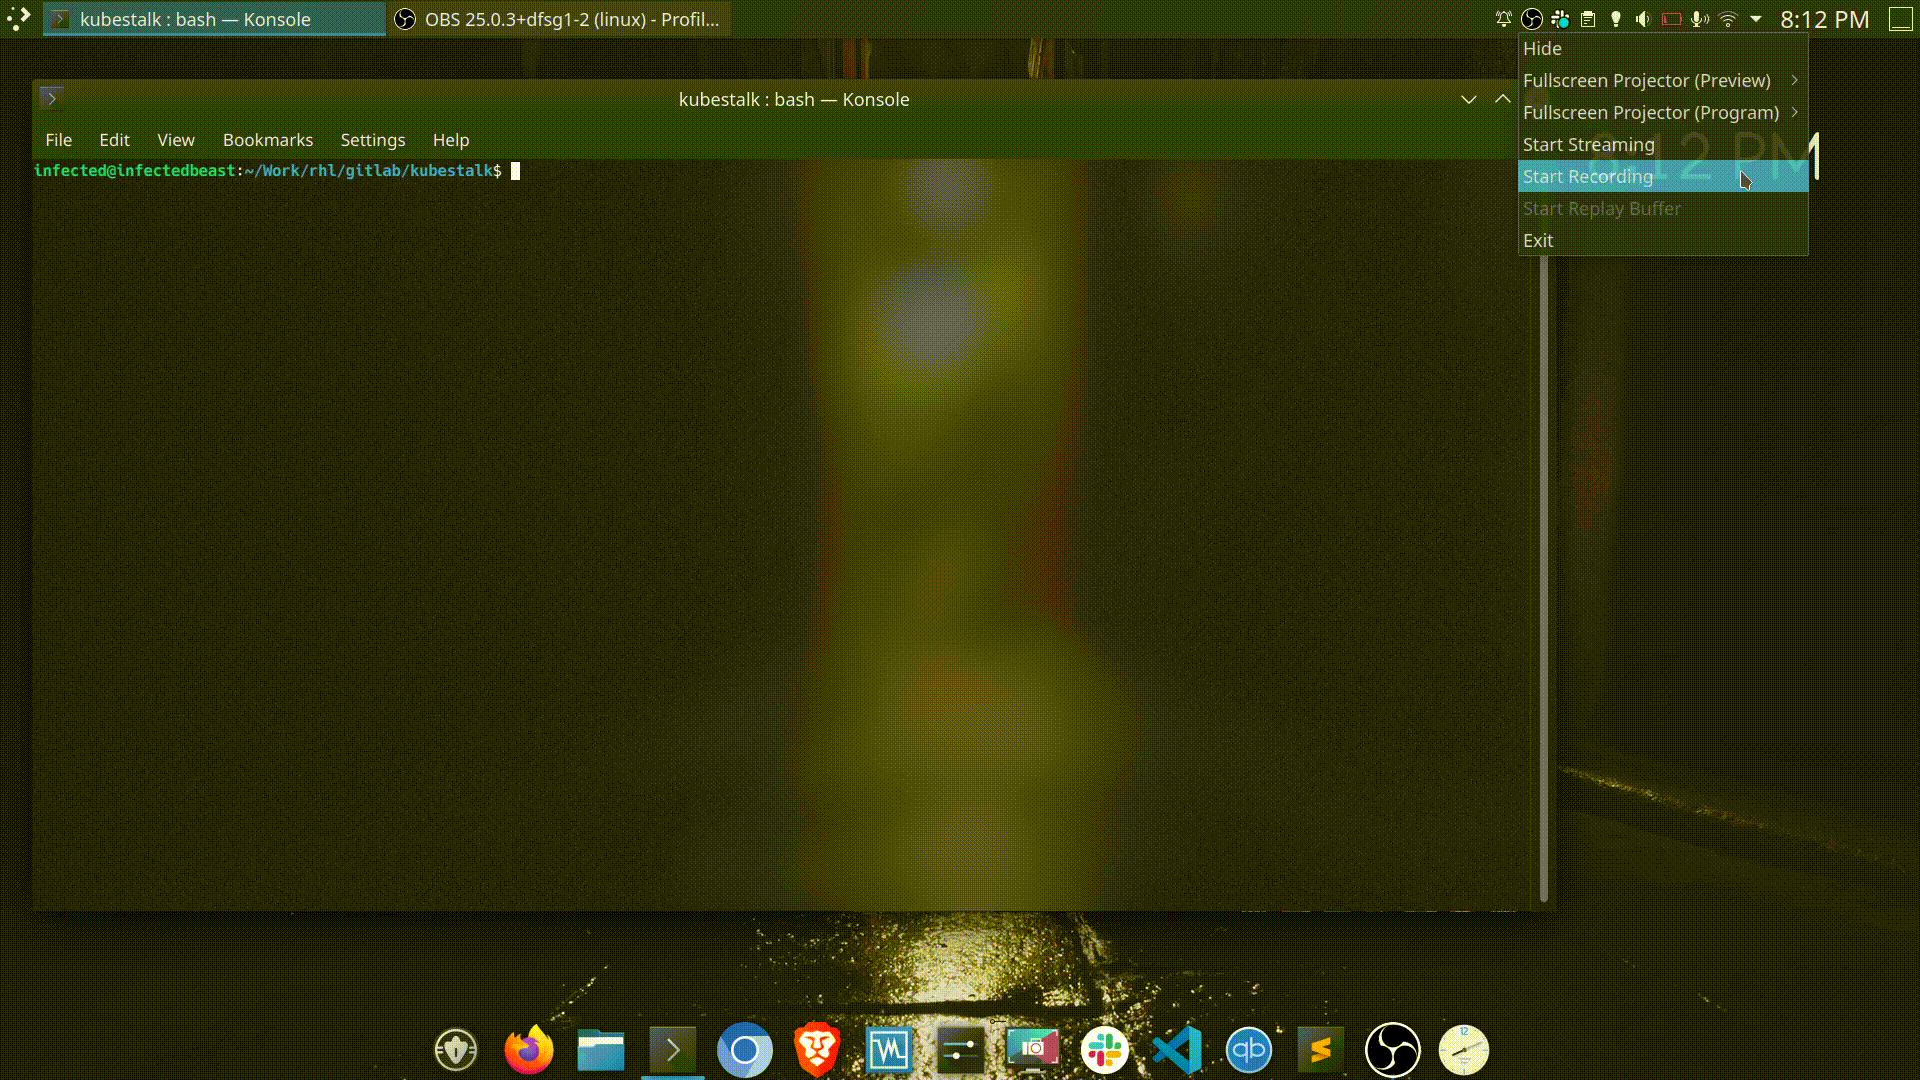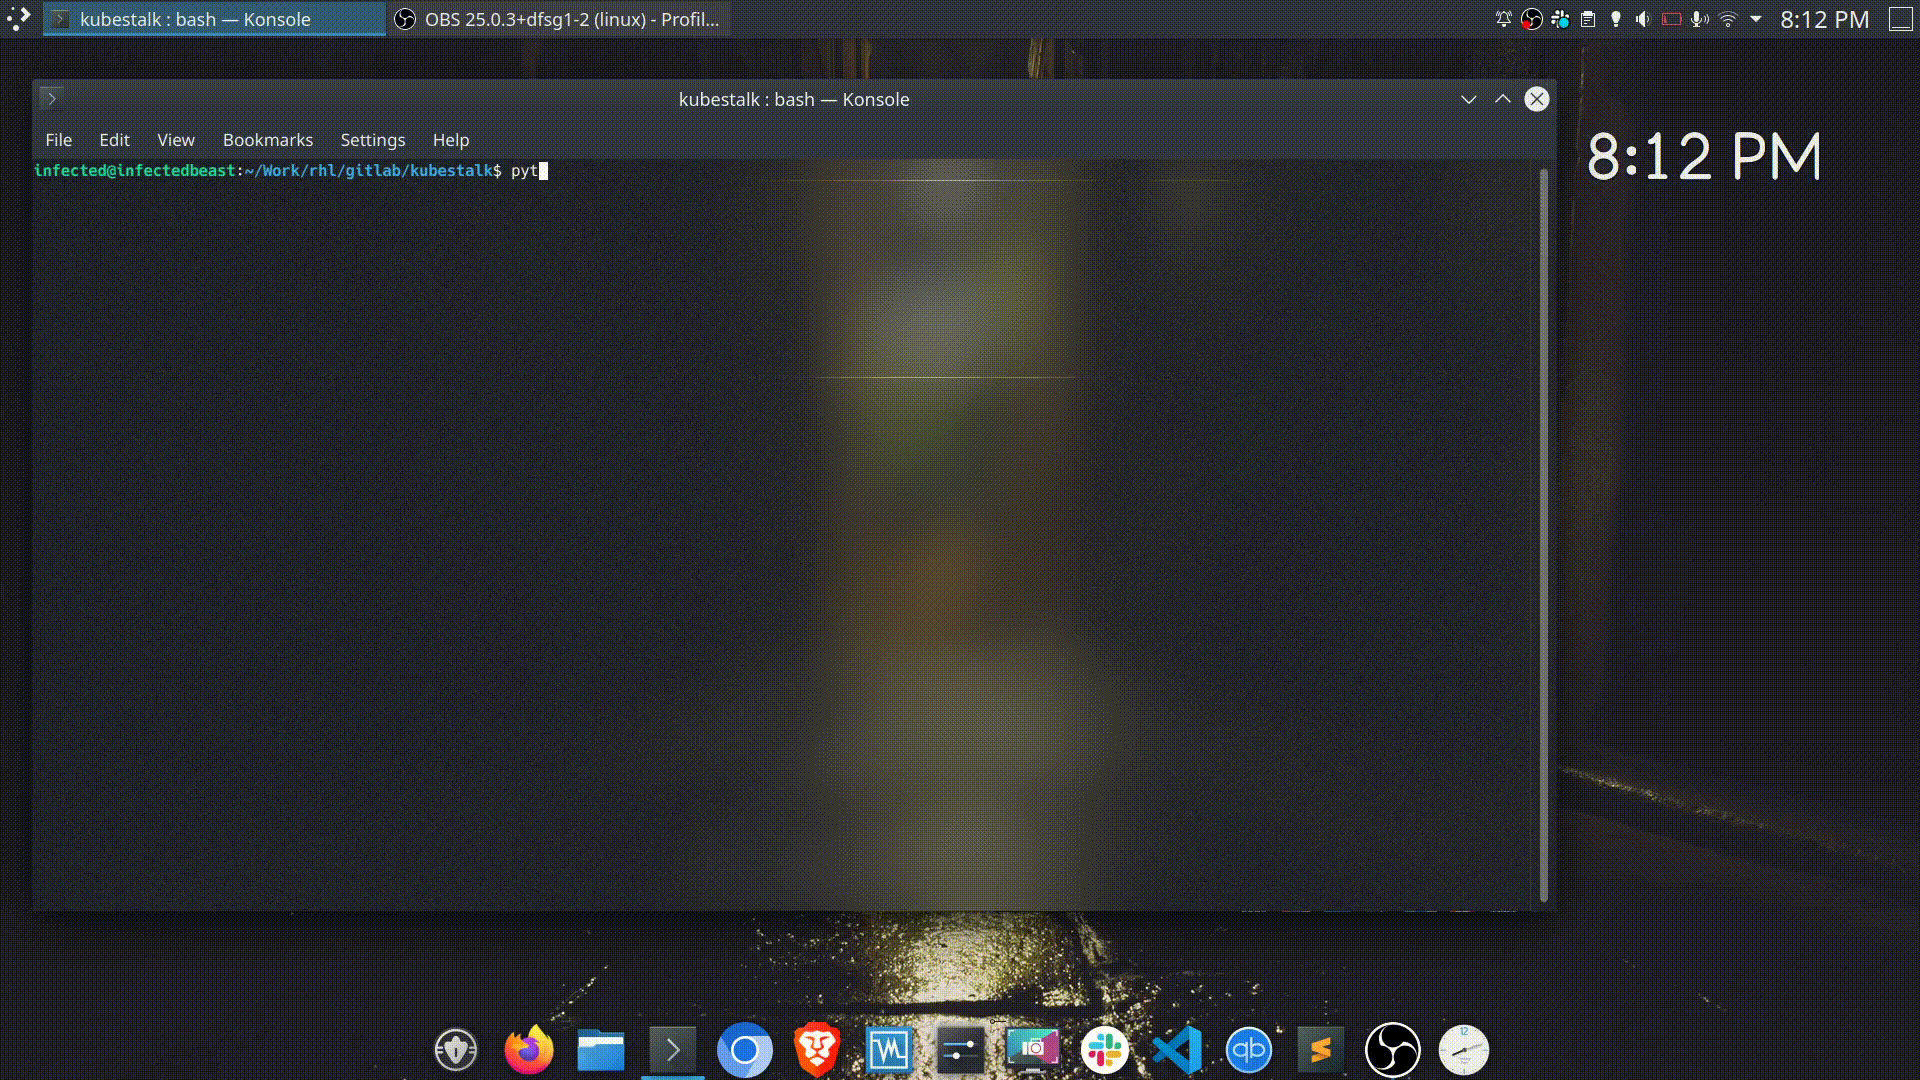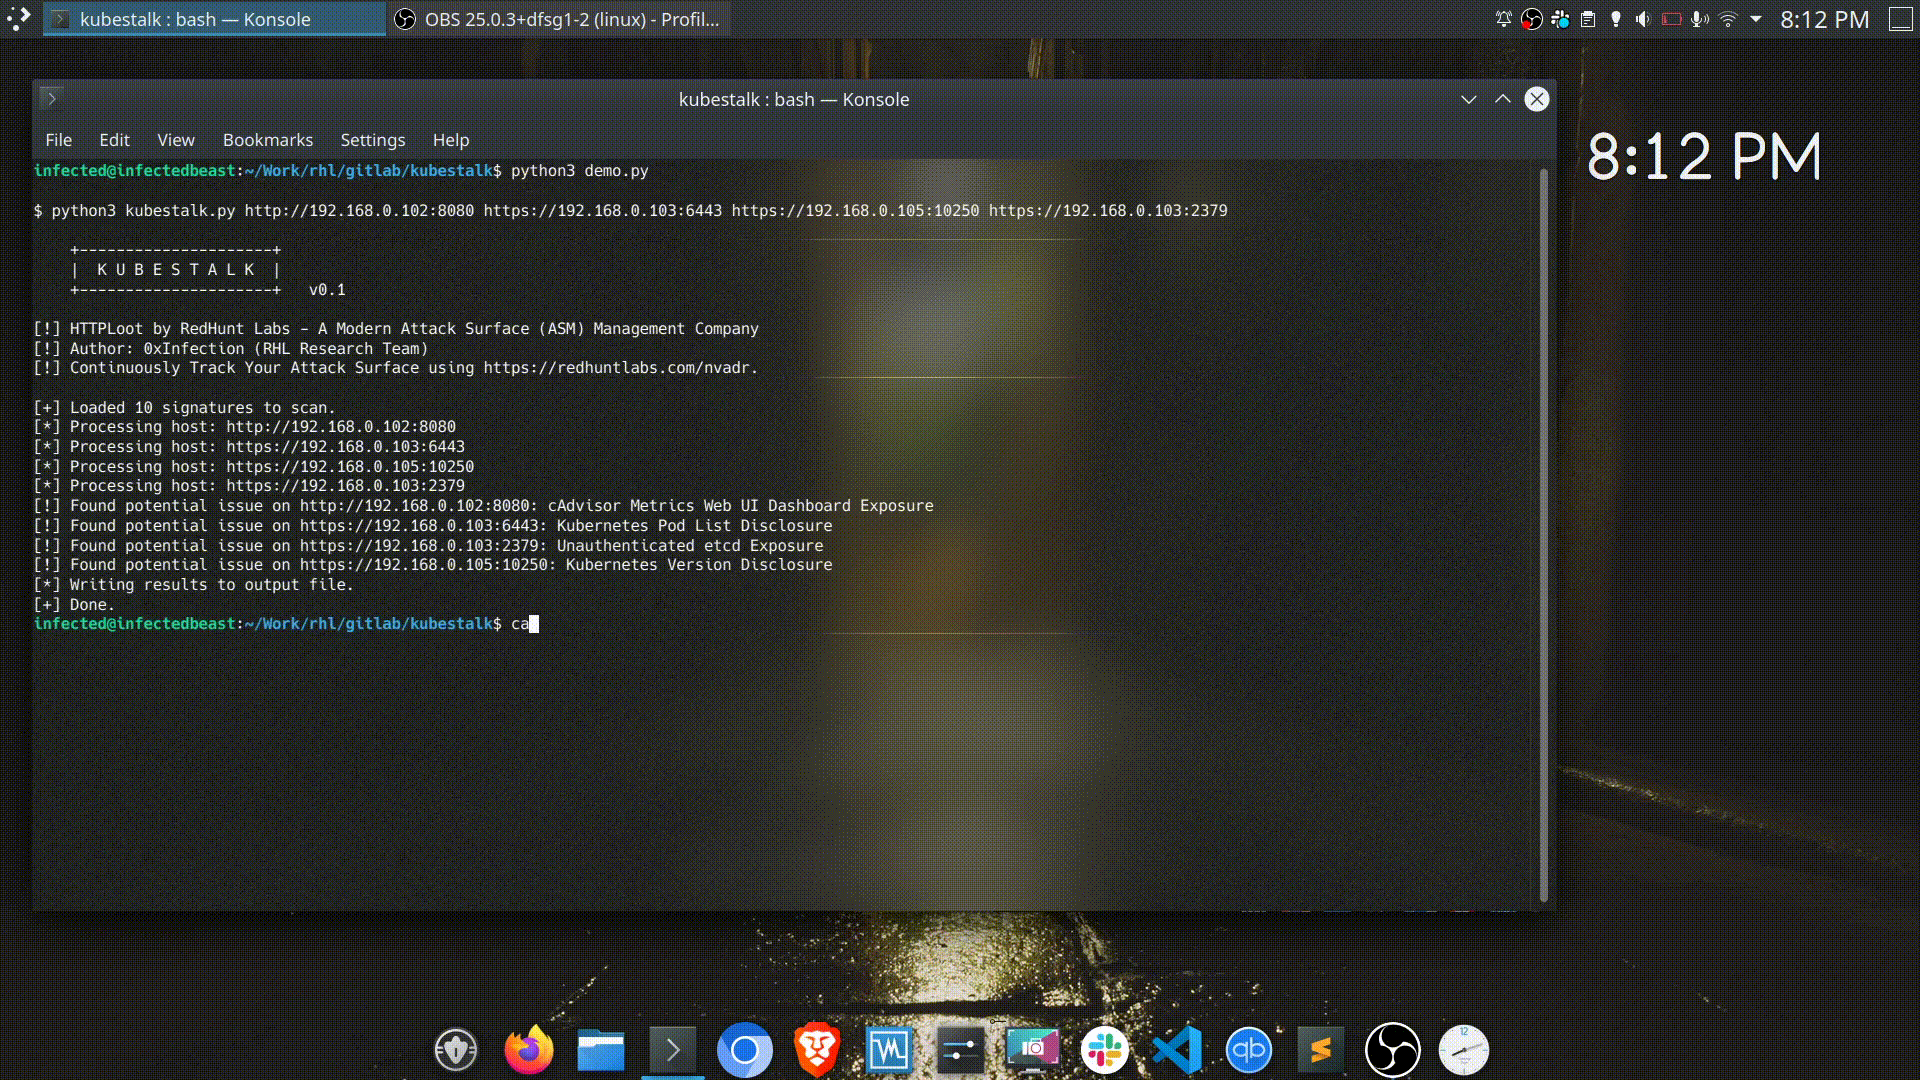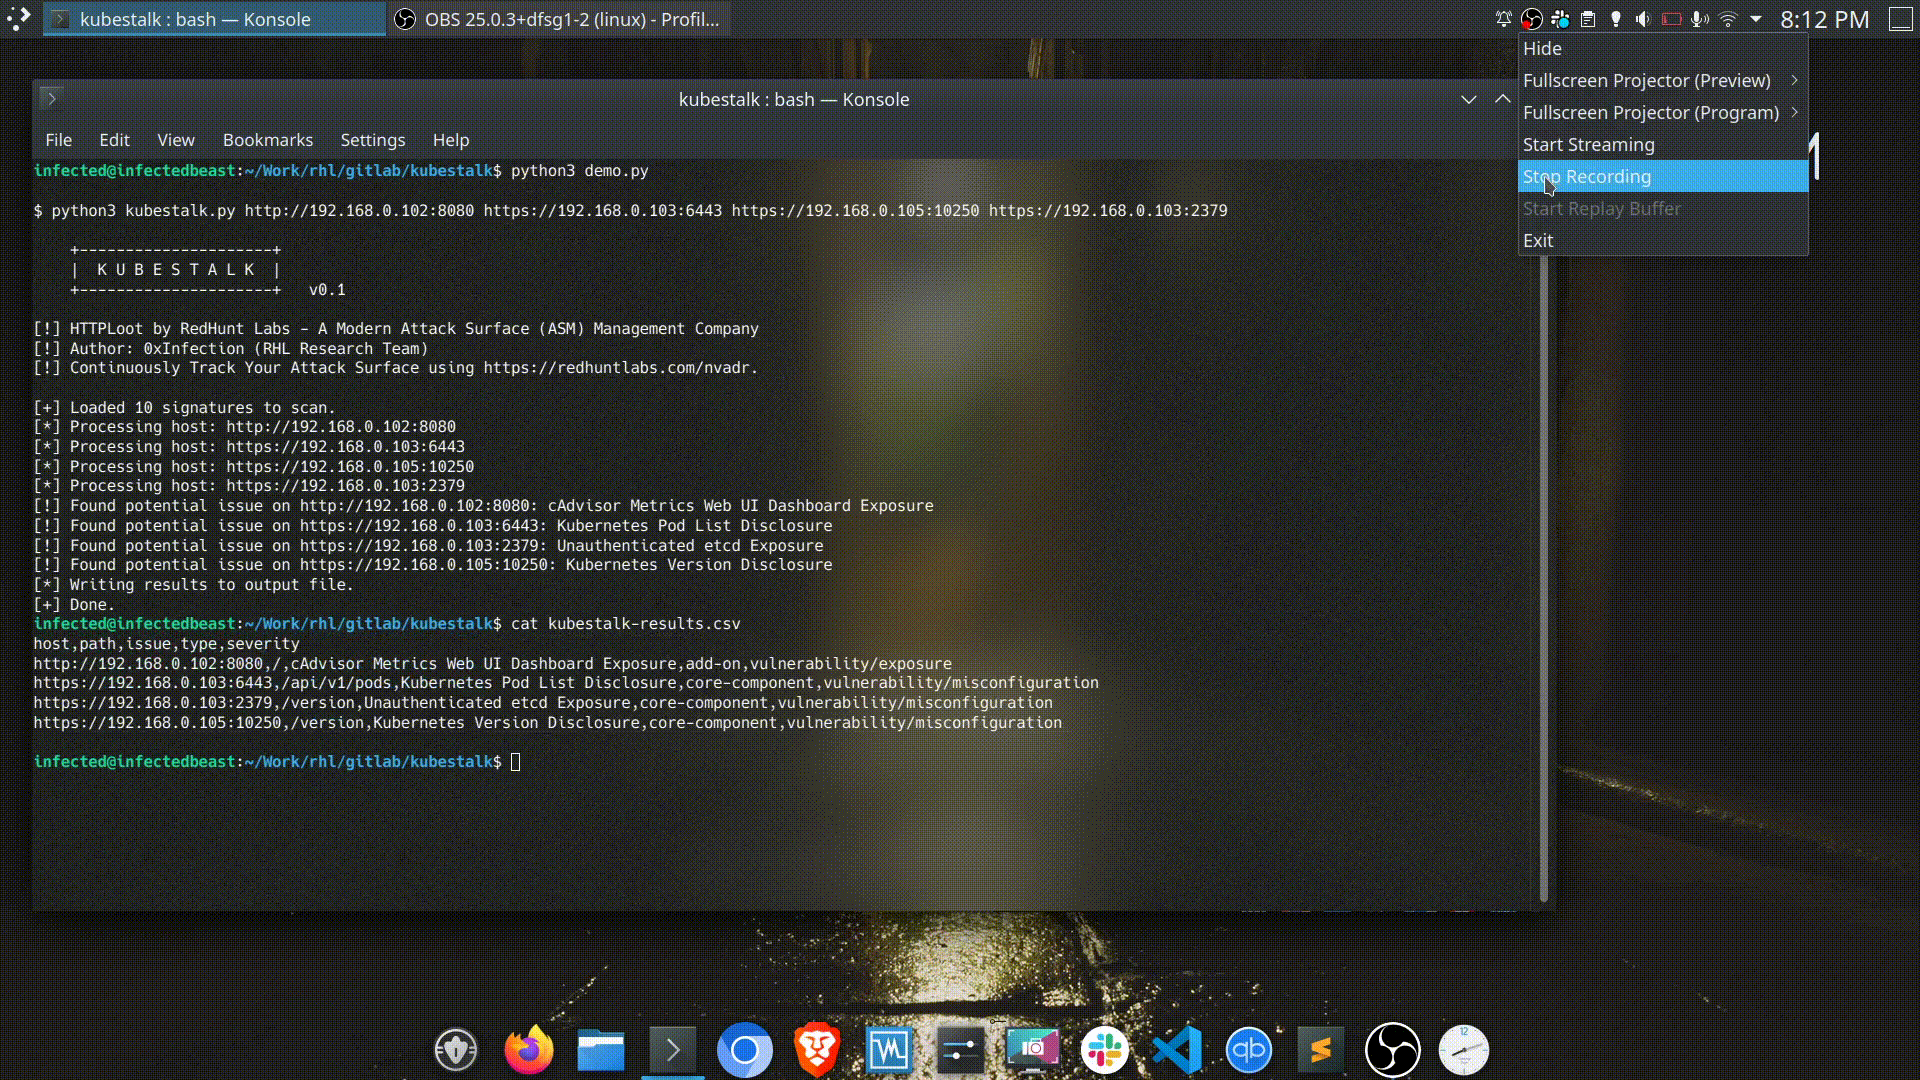 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 cved-sources/cve-2018-11776
Docker container providing a vulnerable Apache Struts2 environment for CVE-2018-11776 exploitation practice and security education.
 cved-sources/cve-2019-10678
Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…
 cved-sources/cve-2017-8046
Docker-based vulnerable environment for CVE-2017-8046 Spring framework remote code execution exploit, part of the Cved vulnerable container…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2017-12615
Docker container providing a vulnerable Apache Tomcat environment for CVE-2017-12615 exploitation, enabling hands-on practice of PUT method file…