

sast-scan
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
cloud-securitycode-analysisconfiguration-auditing+6
882
shiftleftsecurity/sast-scanScan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 freshdemo/apachestruts-cve-2018-11776
Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 chen-keinan/kube-beacon
Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 cilium/cilium
eBPF-based Networking, Security, and Observability
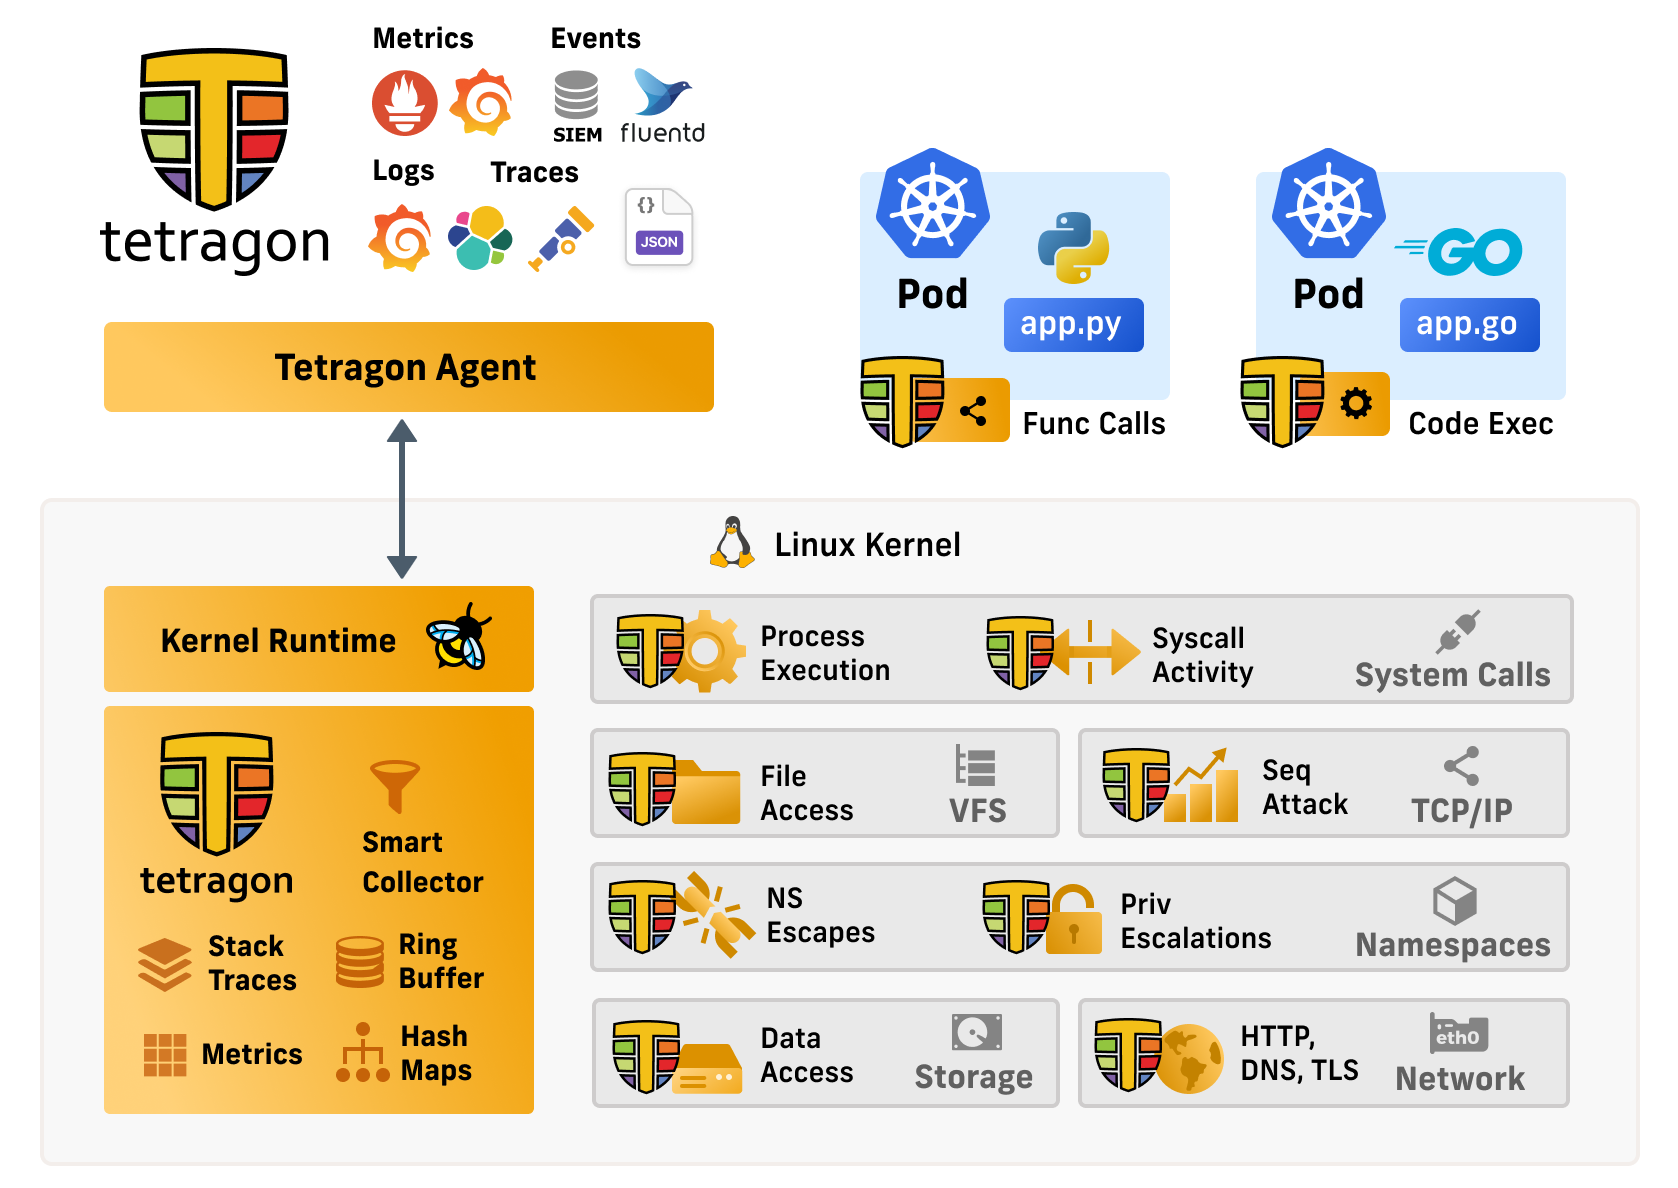 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…