

agentsh
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
ai-securityauthentication-authorizationcloud-security+7
40419h 23m ago
canyonroad/agentshExecution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 amlalabs/amla-sandbox
WASM sandbox with capability enforcement for AI agent code. Agents can only call explicitly provided tools with defined constraints. Sandboxed…
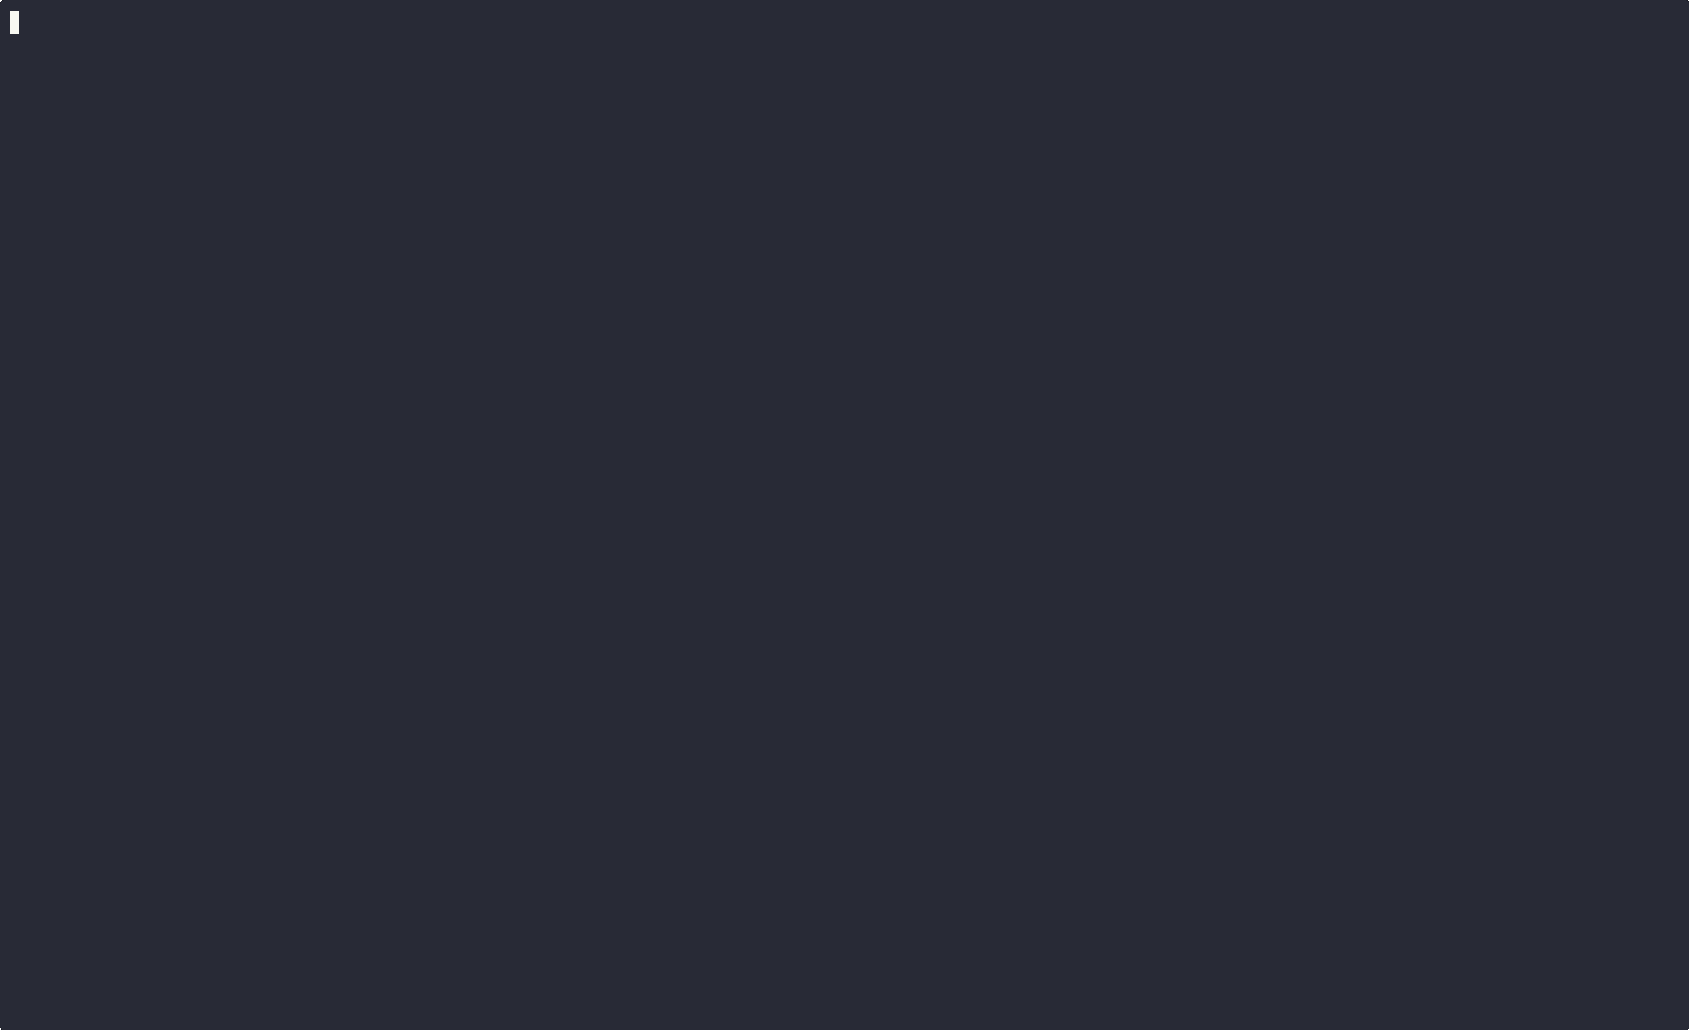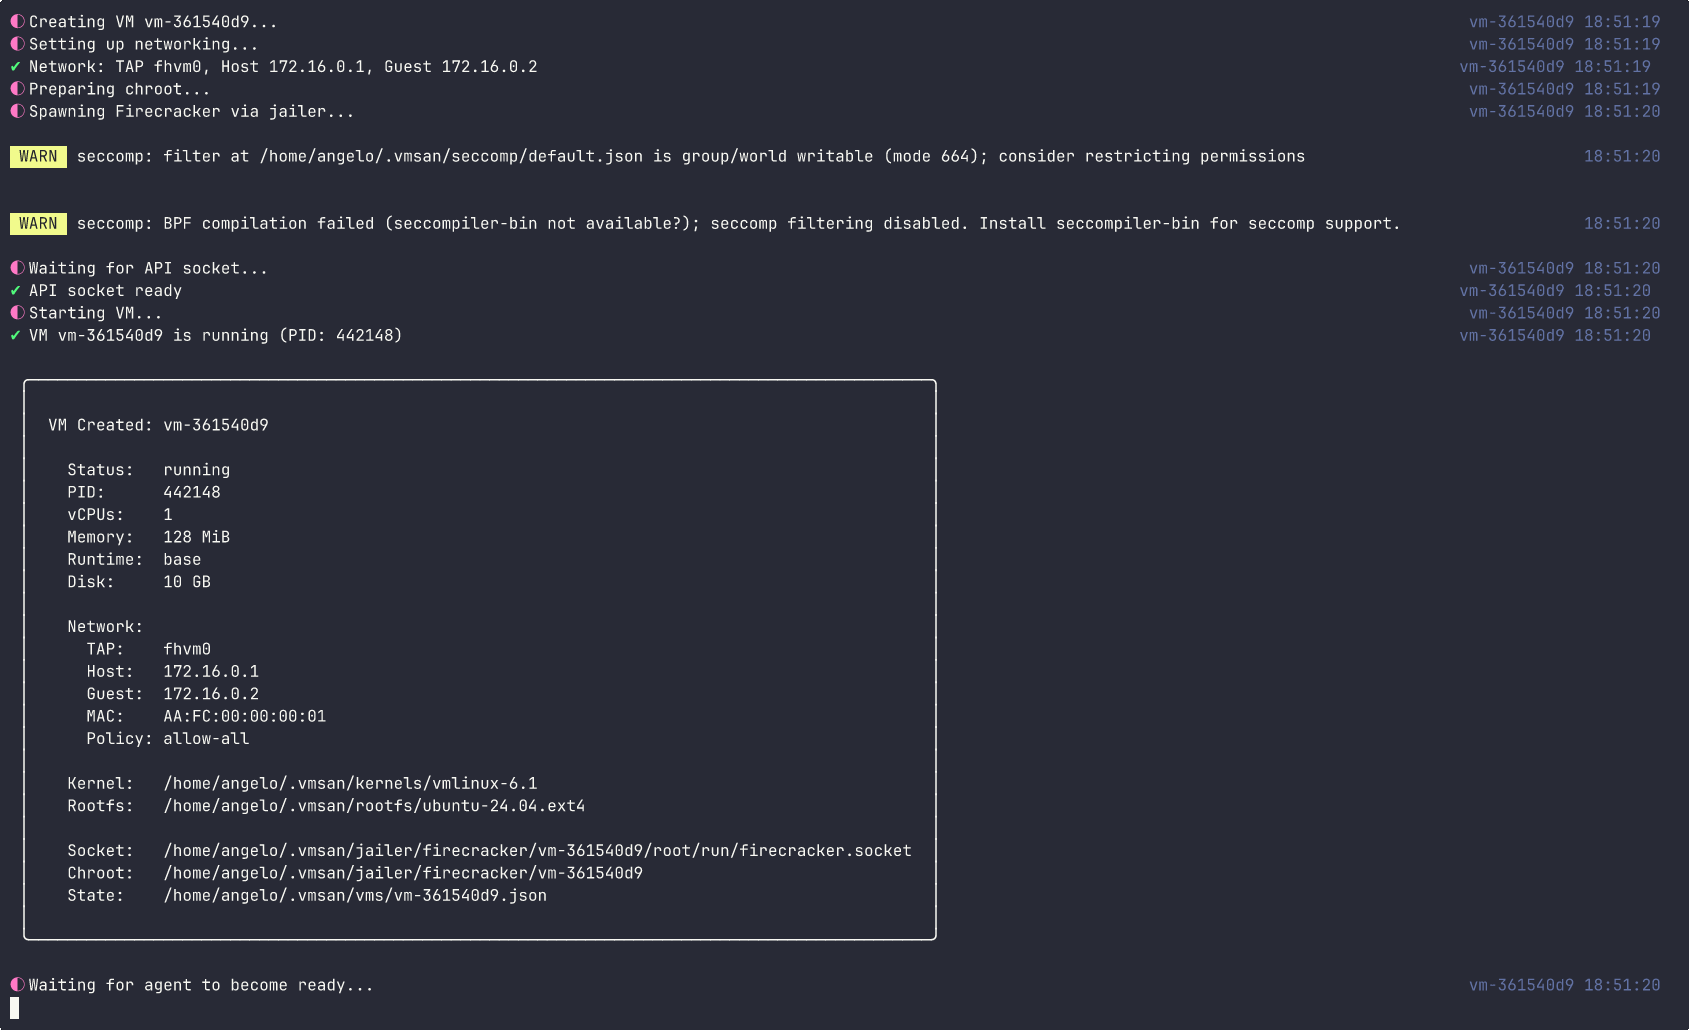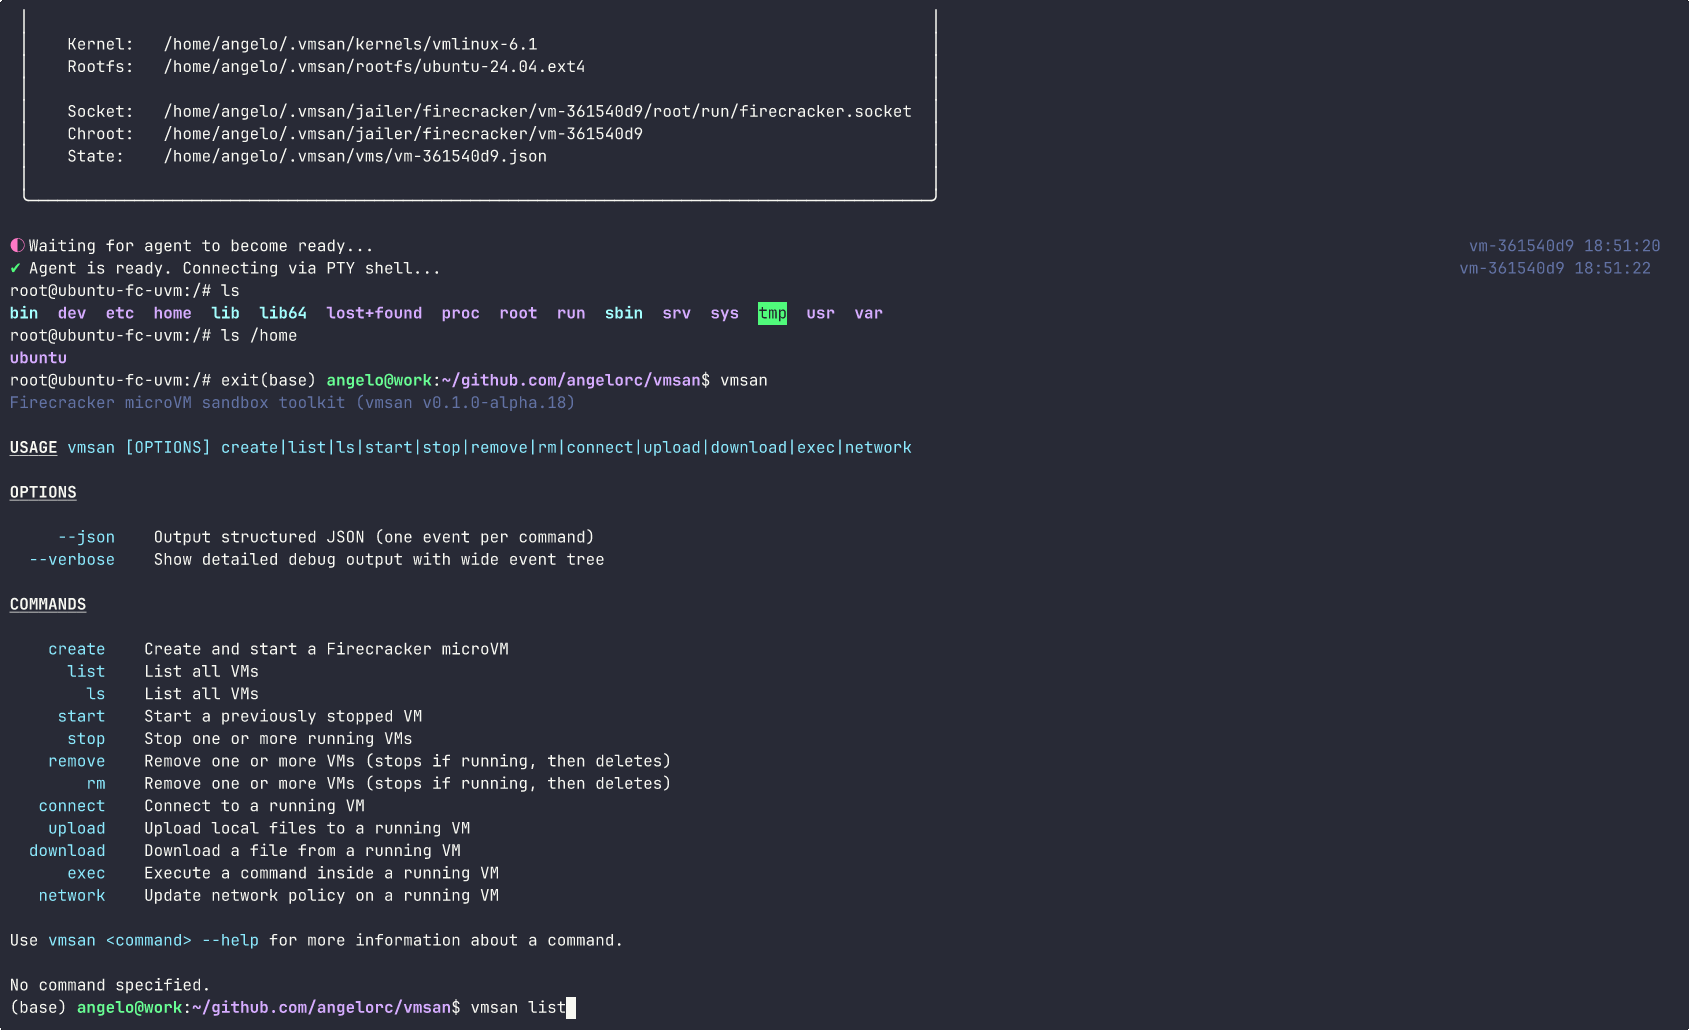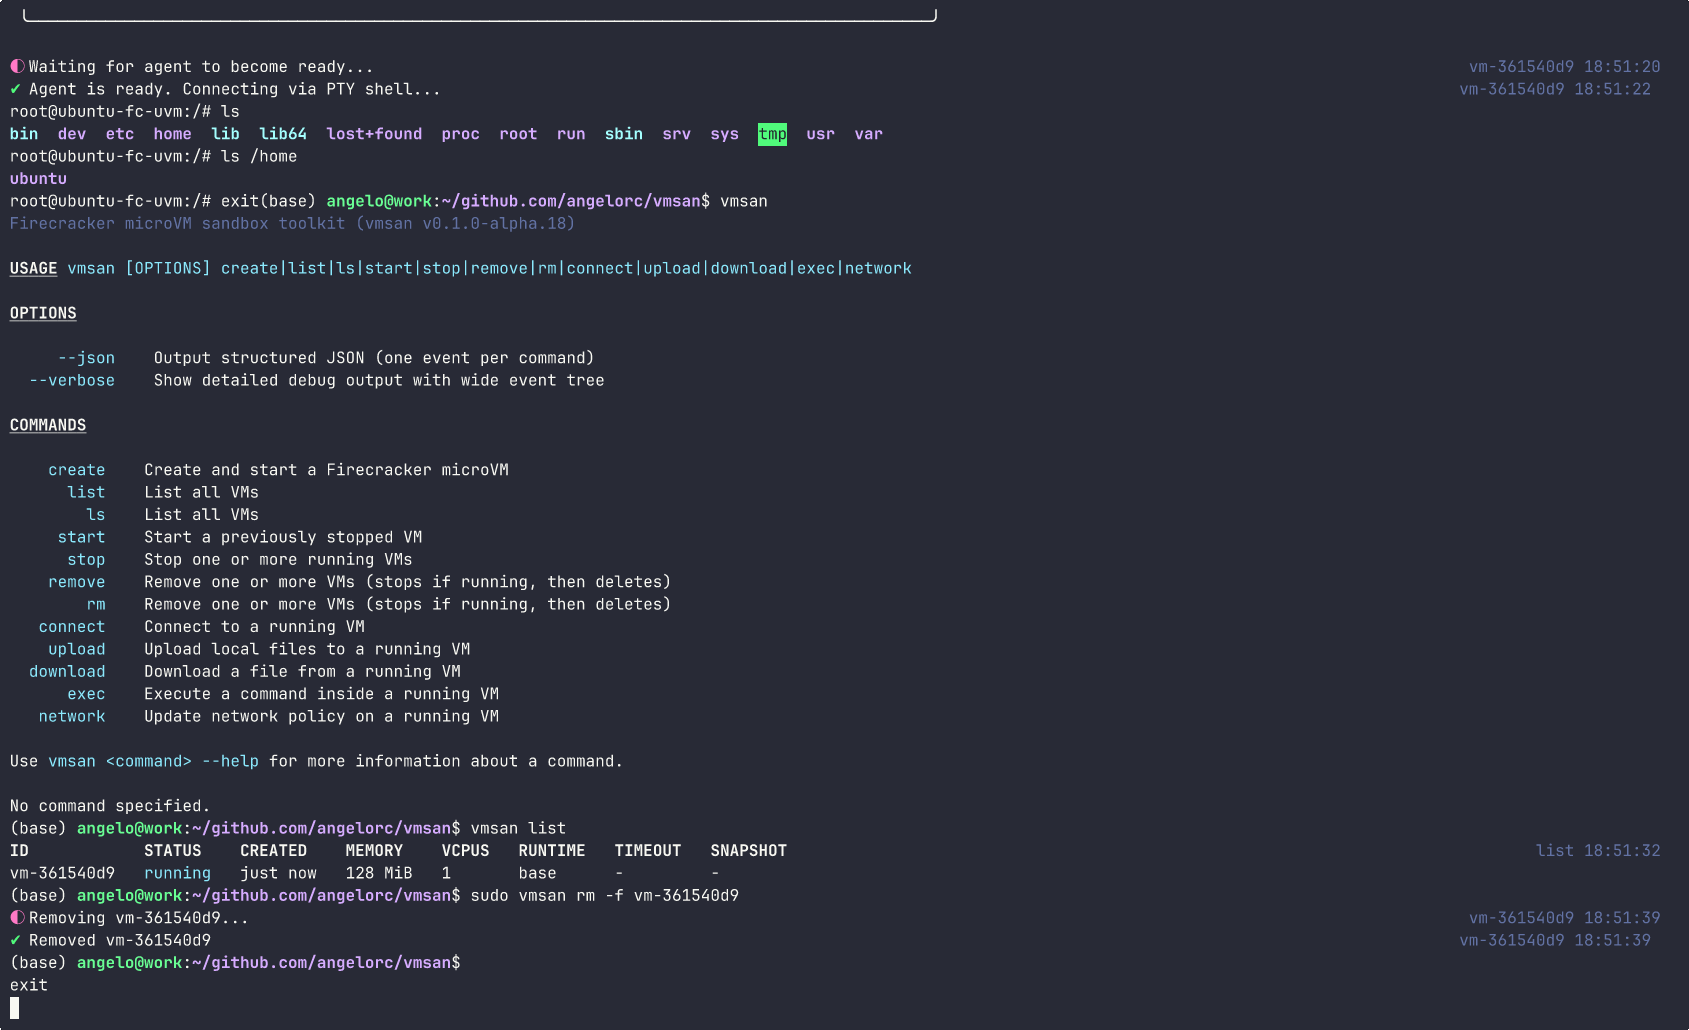 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
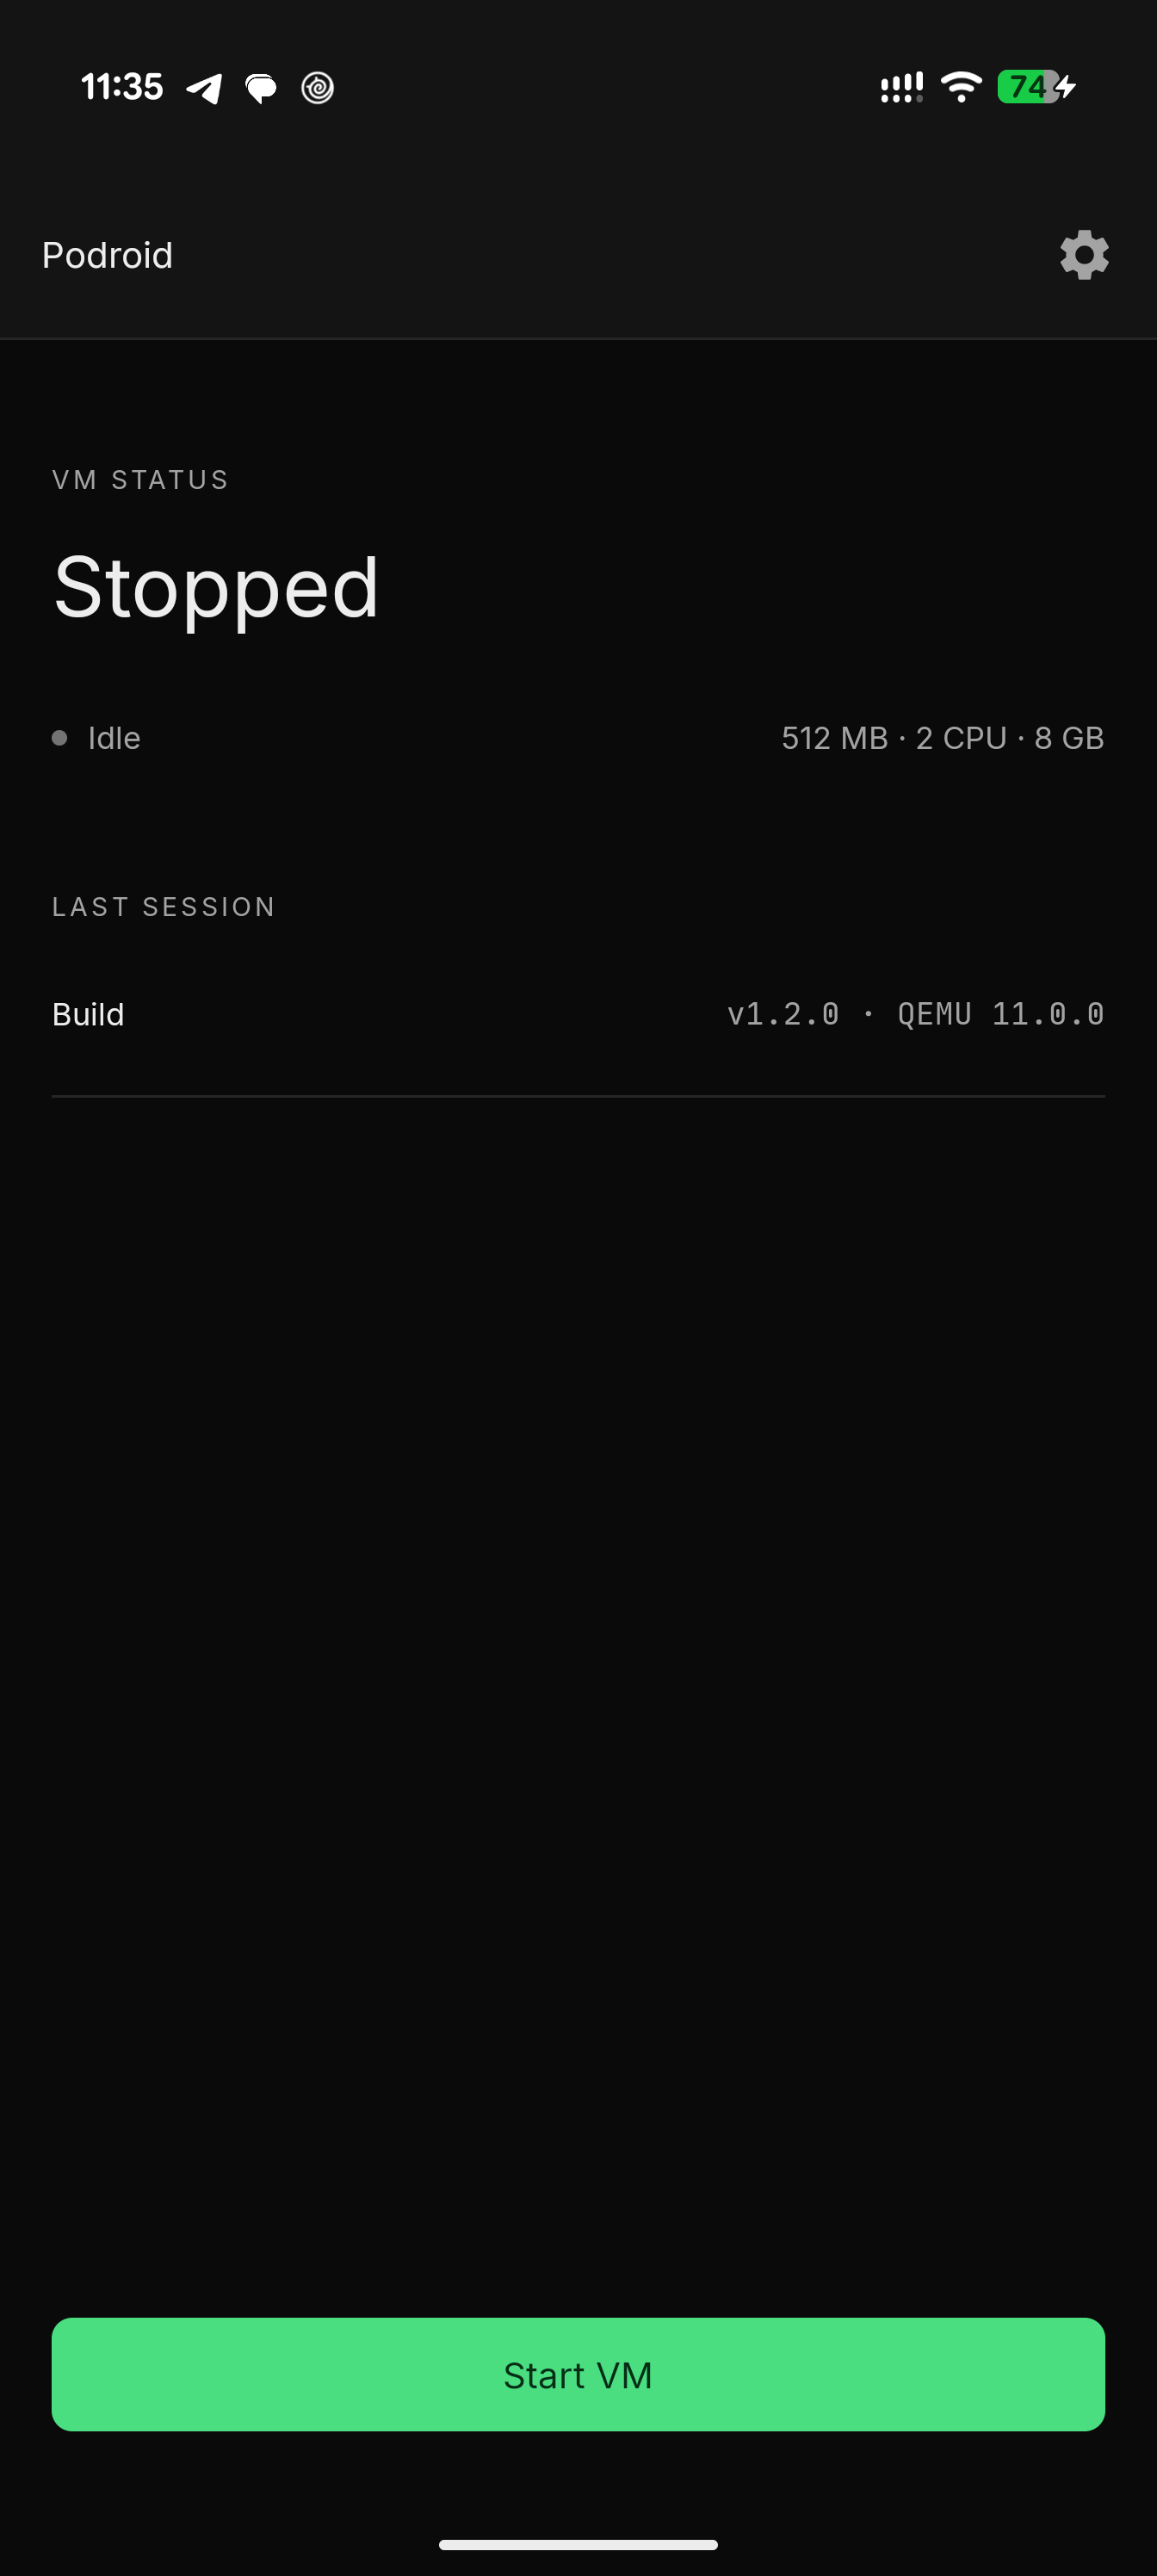 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 nccgroup/kubetcd
Post-exploit a compromised etcd, gain persistence and remote shell to nodes.
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…
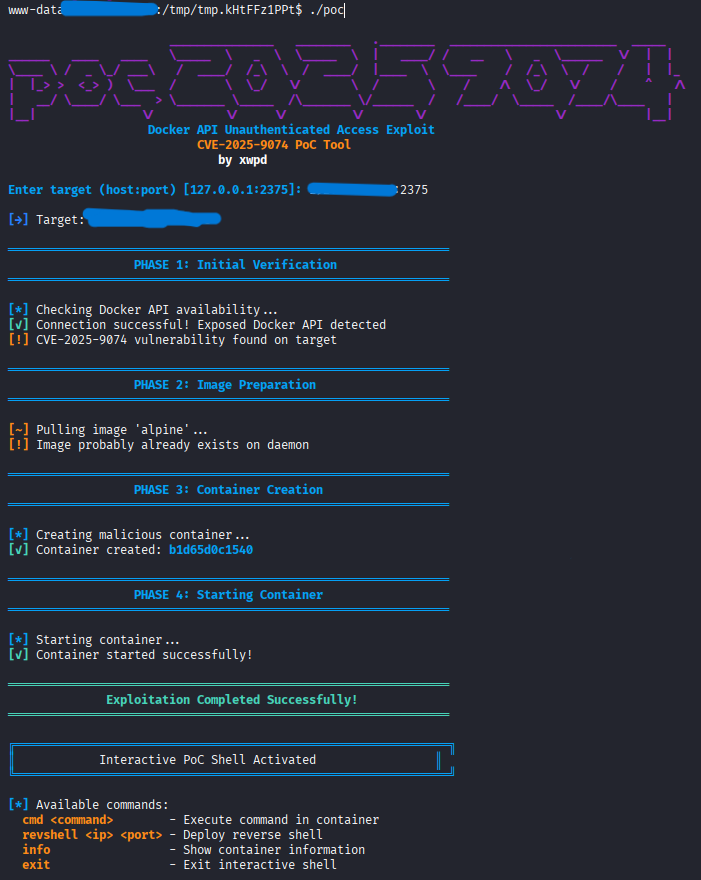 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 yifanzhg/cve-2020-15778
Reproduces CVE-2020-15778 SCP command injection exploit with Docker-based client-server setup for testing remote code execution and reverse shell…
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 zhaduchanhzz/cve-2025-32463_poc
Proof-of-concept exploit for CVE-2025-32463, a privilege-escalation vulnerability in sudo's chroot feature. Includes Docker environment and exploit…
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
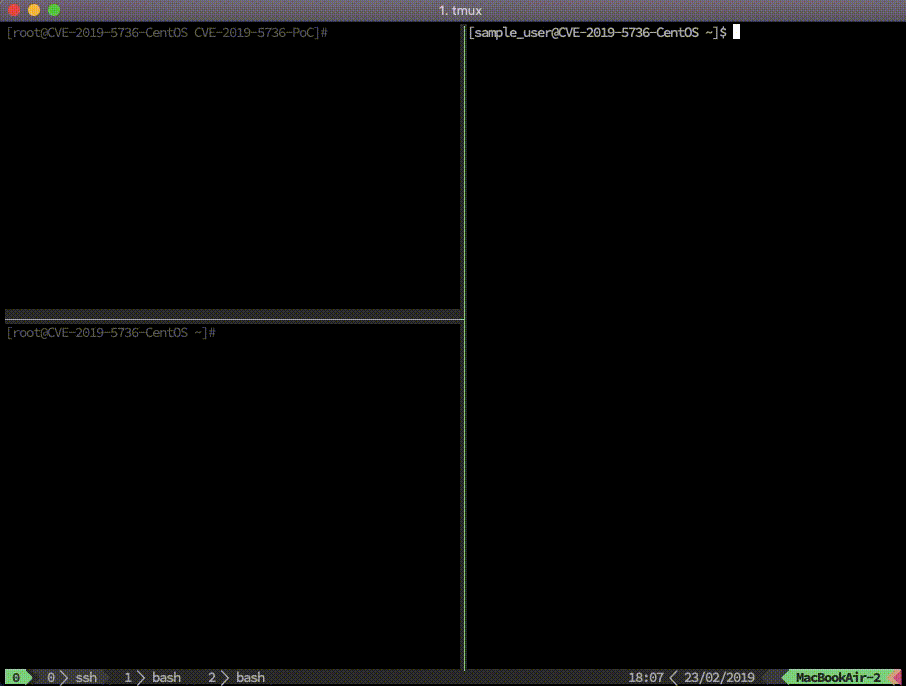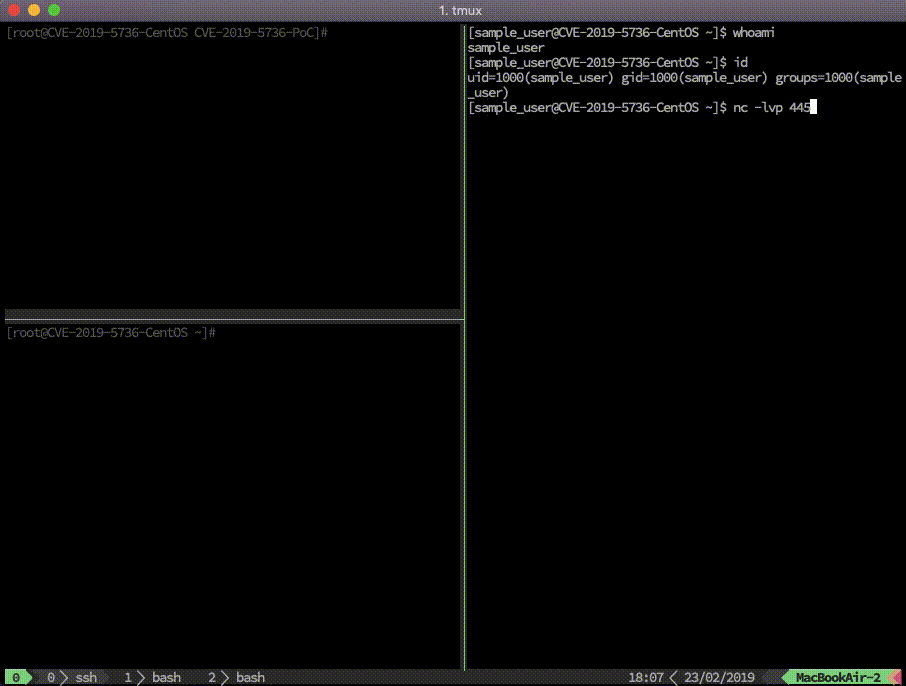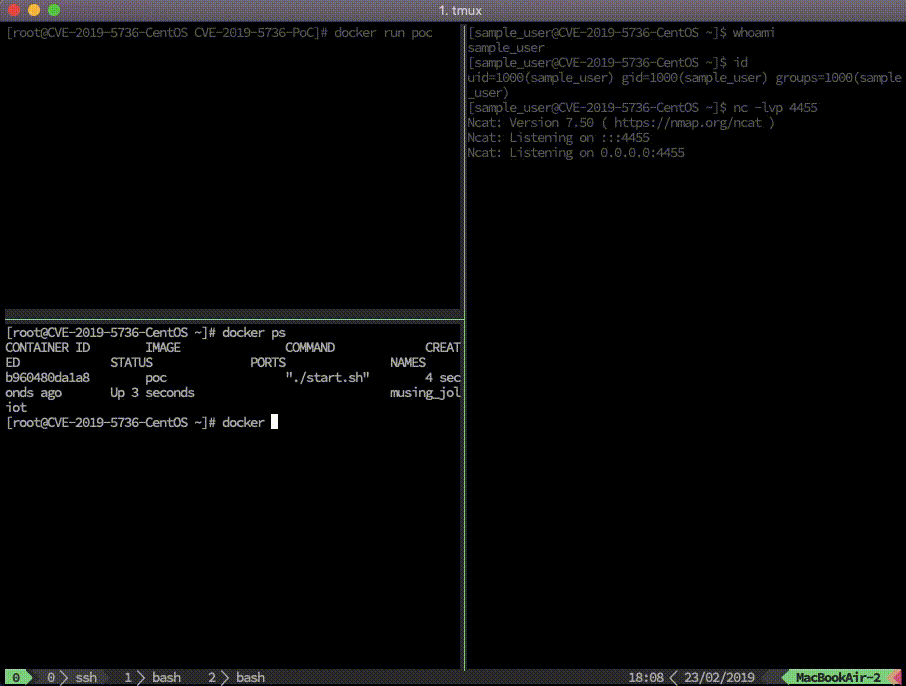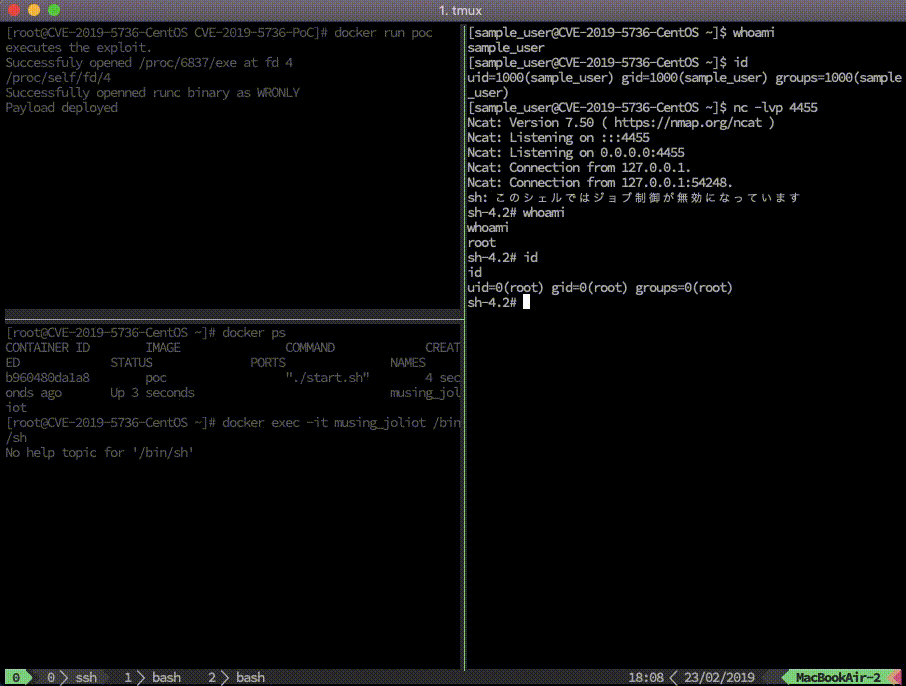 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…
 rtvkiz/minimal
Minimal CVE Hardened container image collection