kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…

Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…

VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security

Find binary files not installed through package manager

CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.

Dockerfile containing all the necessary setup files to demo the exploit

Proof-of-concept exploit for CVE-2026-5555, demonstrating container escape via /proc/self/fd symlink in rshared volumes to overwrite host files and…

This contains the necessary files and Docker to replicate A vulnerability in OURPHP that has a XSS Vulnerability (CVE-2023-30212)

This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…

Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.

A lightweight orchestrator and worker scanner setup for running large/continuous scans across split input files. This repository contains…

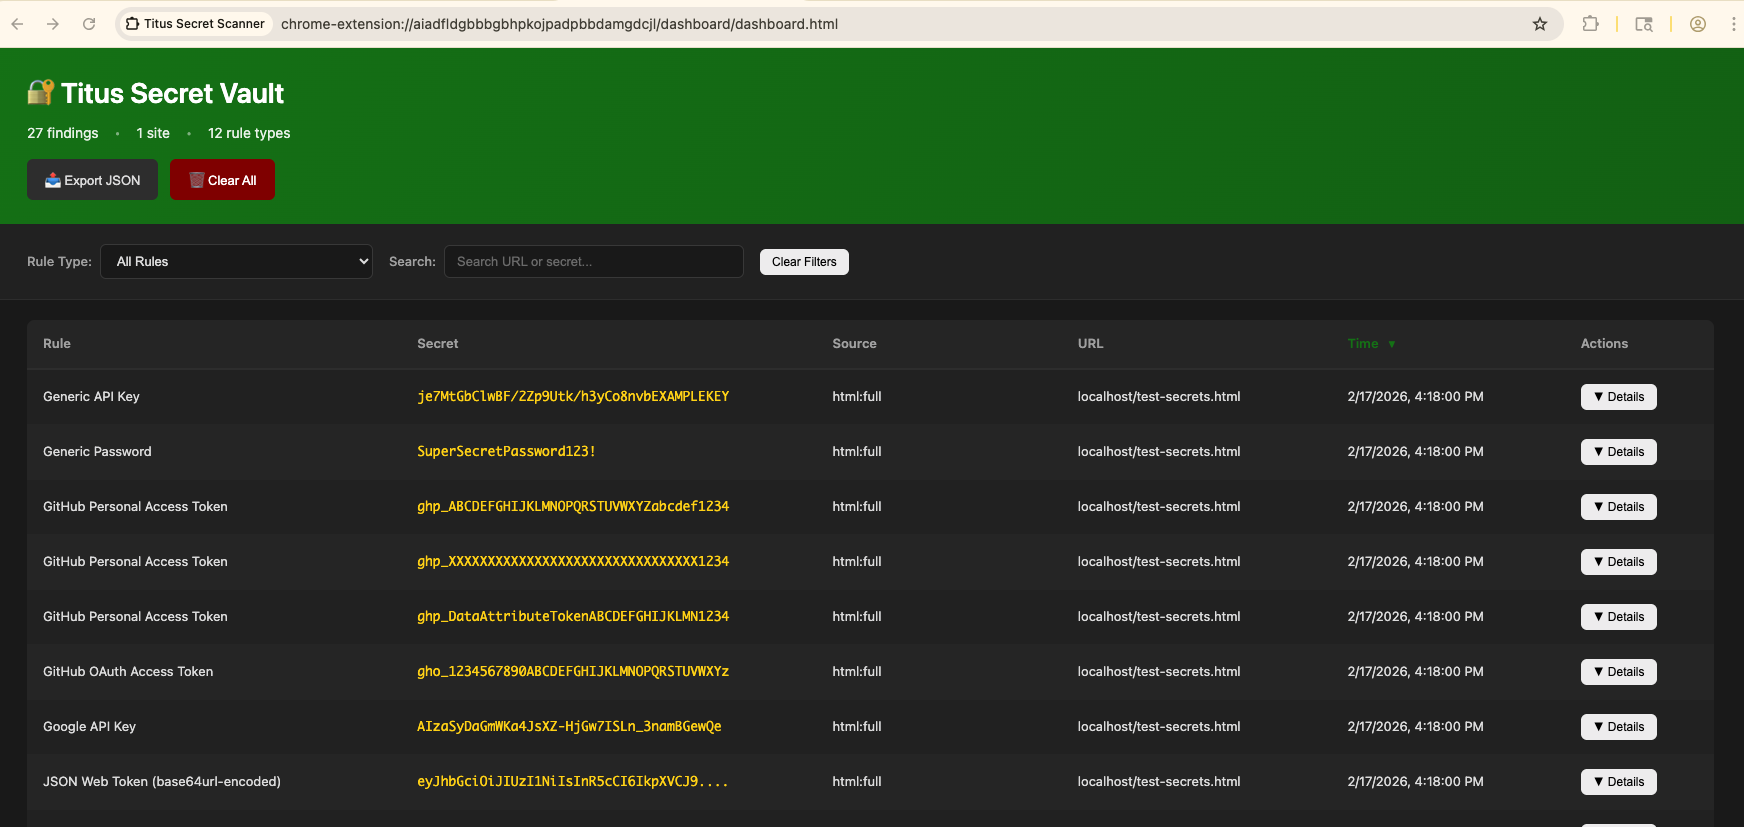
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸

Security for the modern age of AI: defend against bad AI agents and malicious npm packages

Docker CVE-2022-37708

OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…