
docker-onion-nmap
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
container-securitydns-analysisinformation-gathering+8
543
milesrichardson/docker-onion-nmapScan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
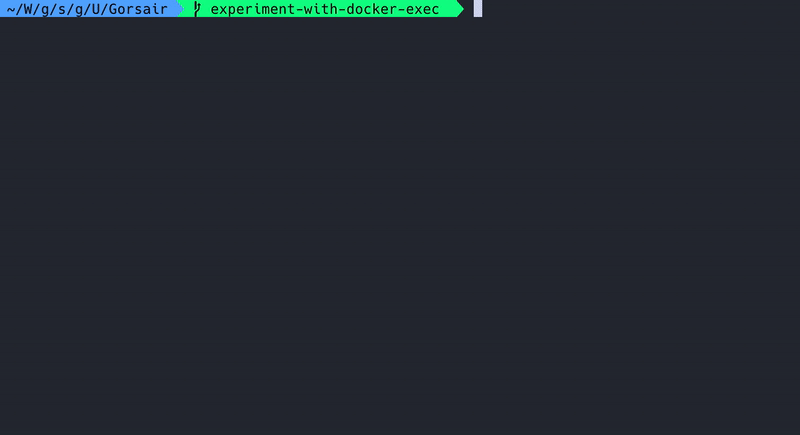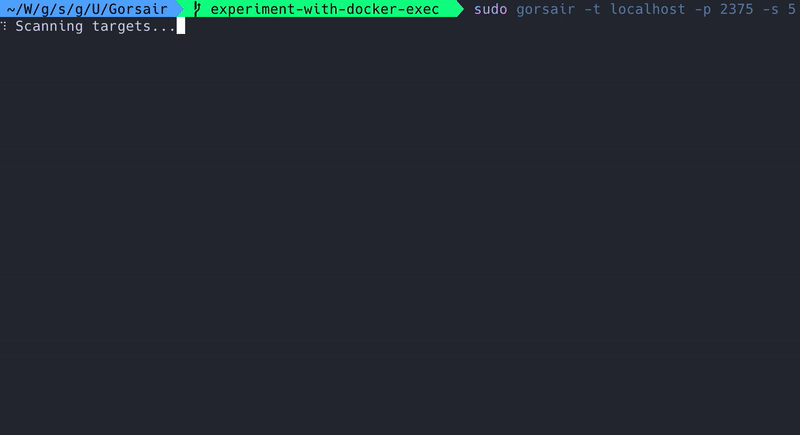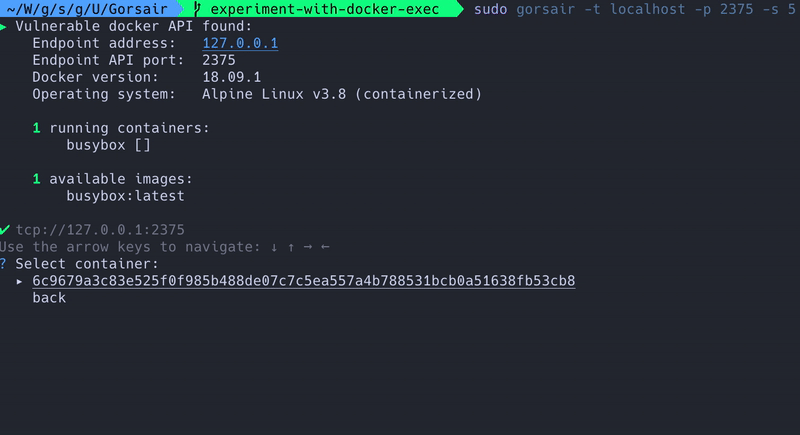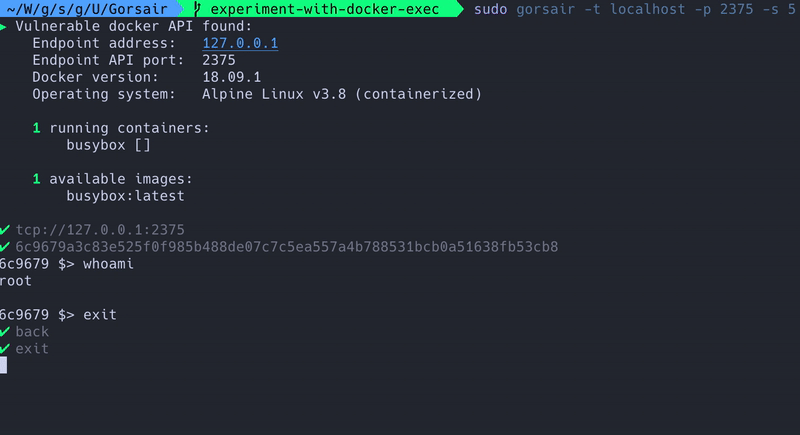 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
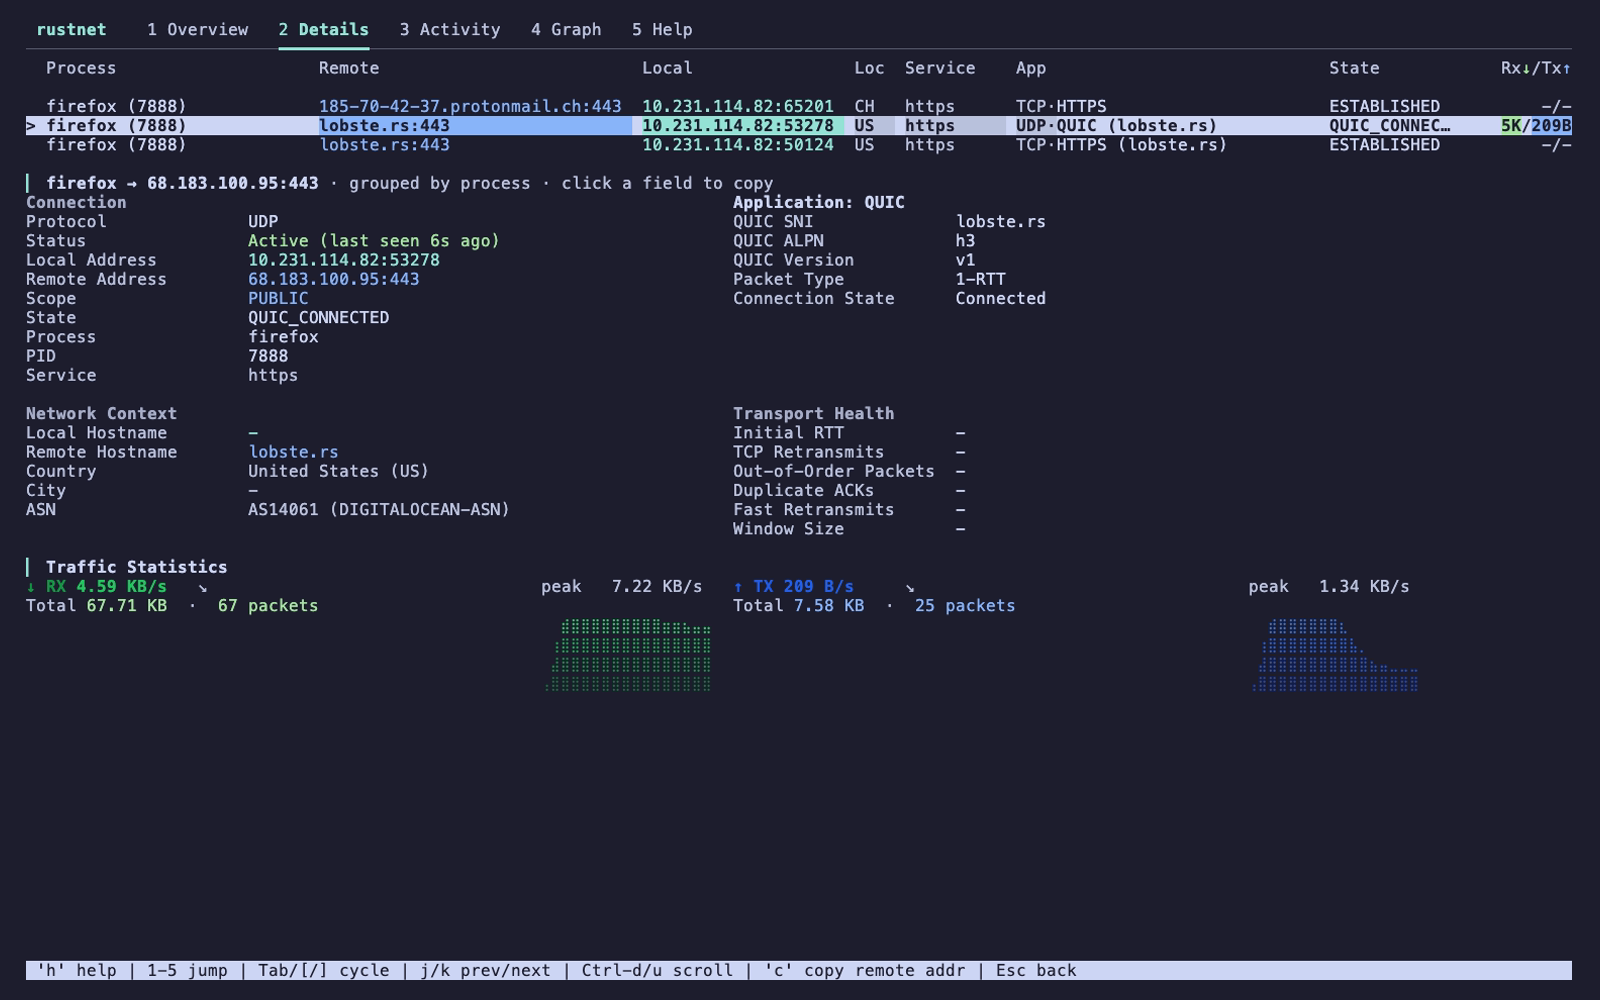 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 cloudflare/flan
A pretty sweet vulnerability scanner
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 skydive-project/skydive
An open source real-time network topology and protocols analyzer
 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 al0ne/linuxcheck
Linux应急处置/信息搜集/漏洞检测工具,支持基础配置/网络流量/任务计划/环境变量/用户信息/Services/bash/恶意文件/内核Rootkit/SSH/Webshell/挖矿文件/挖矿进程/供应链/服务器风险等13类70+项检查
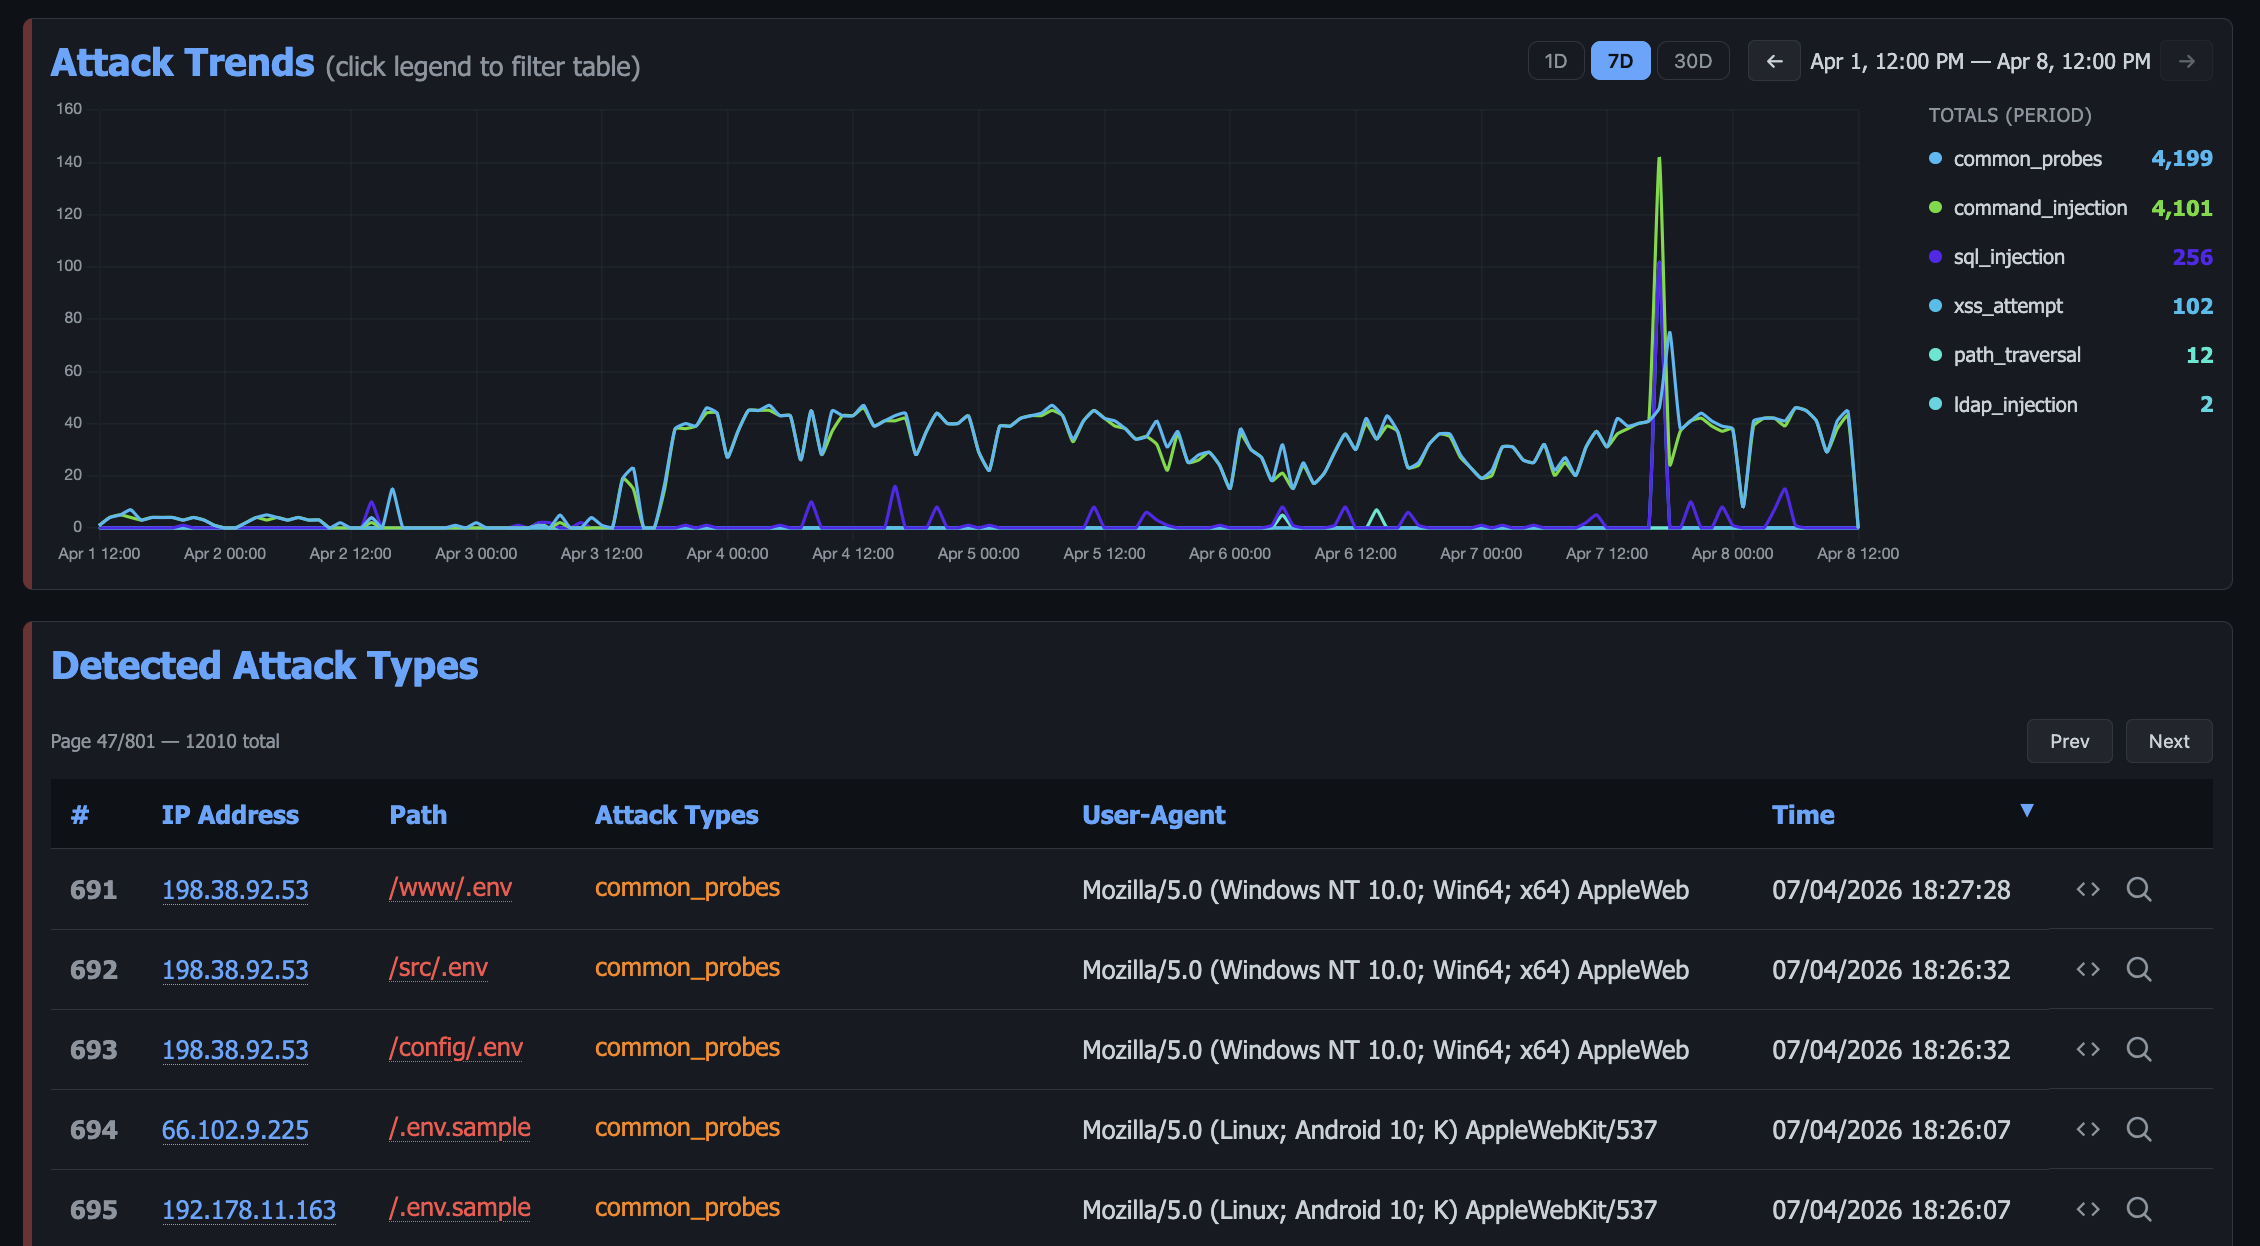 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…