
stratus-red-team
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
adversarial-attackcloud-infrastructure-securitycloud-security+5
2.4k
datadog/stratus-red-team:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 axelbankole/cve-2012-1495-webcalendar-
Sets up a Dockerized WebCalendar environment to demonstrate CVE-2012-1495 exploitation using Metasploit on Kali Linux.
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
 mauroeldritch/gevaudan
Exploit for Red Hat / GlusterFS CVE-2018-1088 & CVE-2018-1112, featured @ DEFCON 26, Las Vegas!
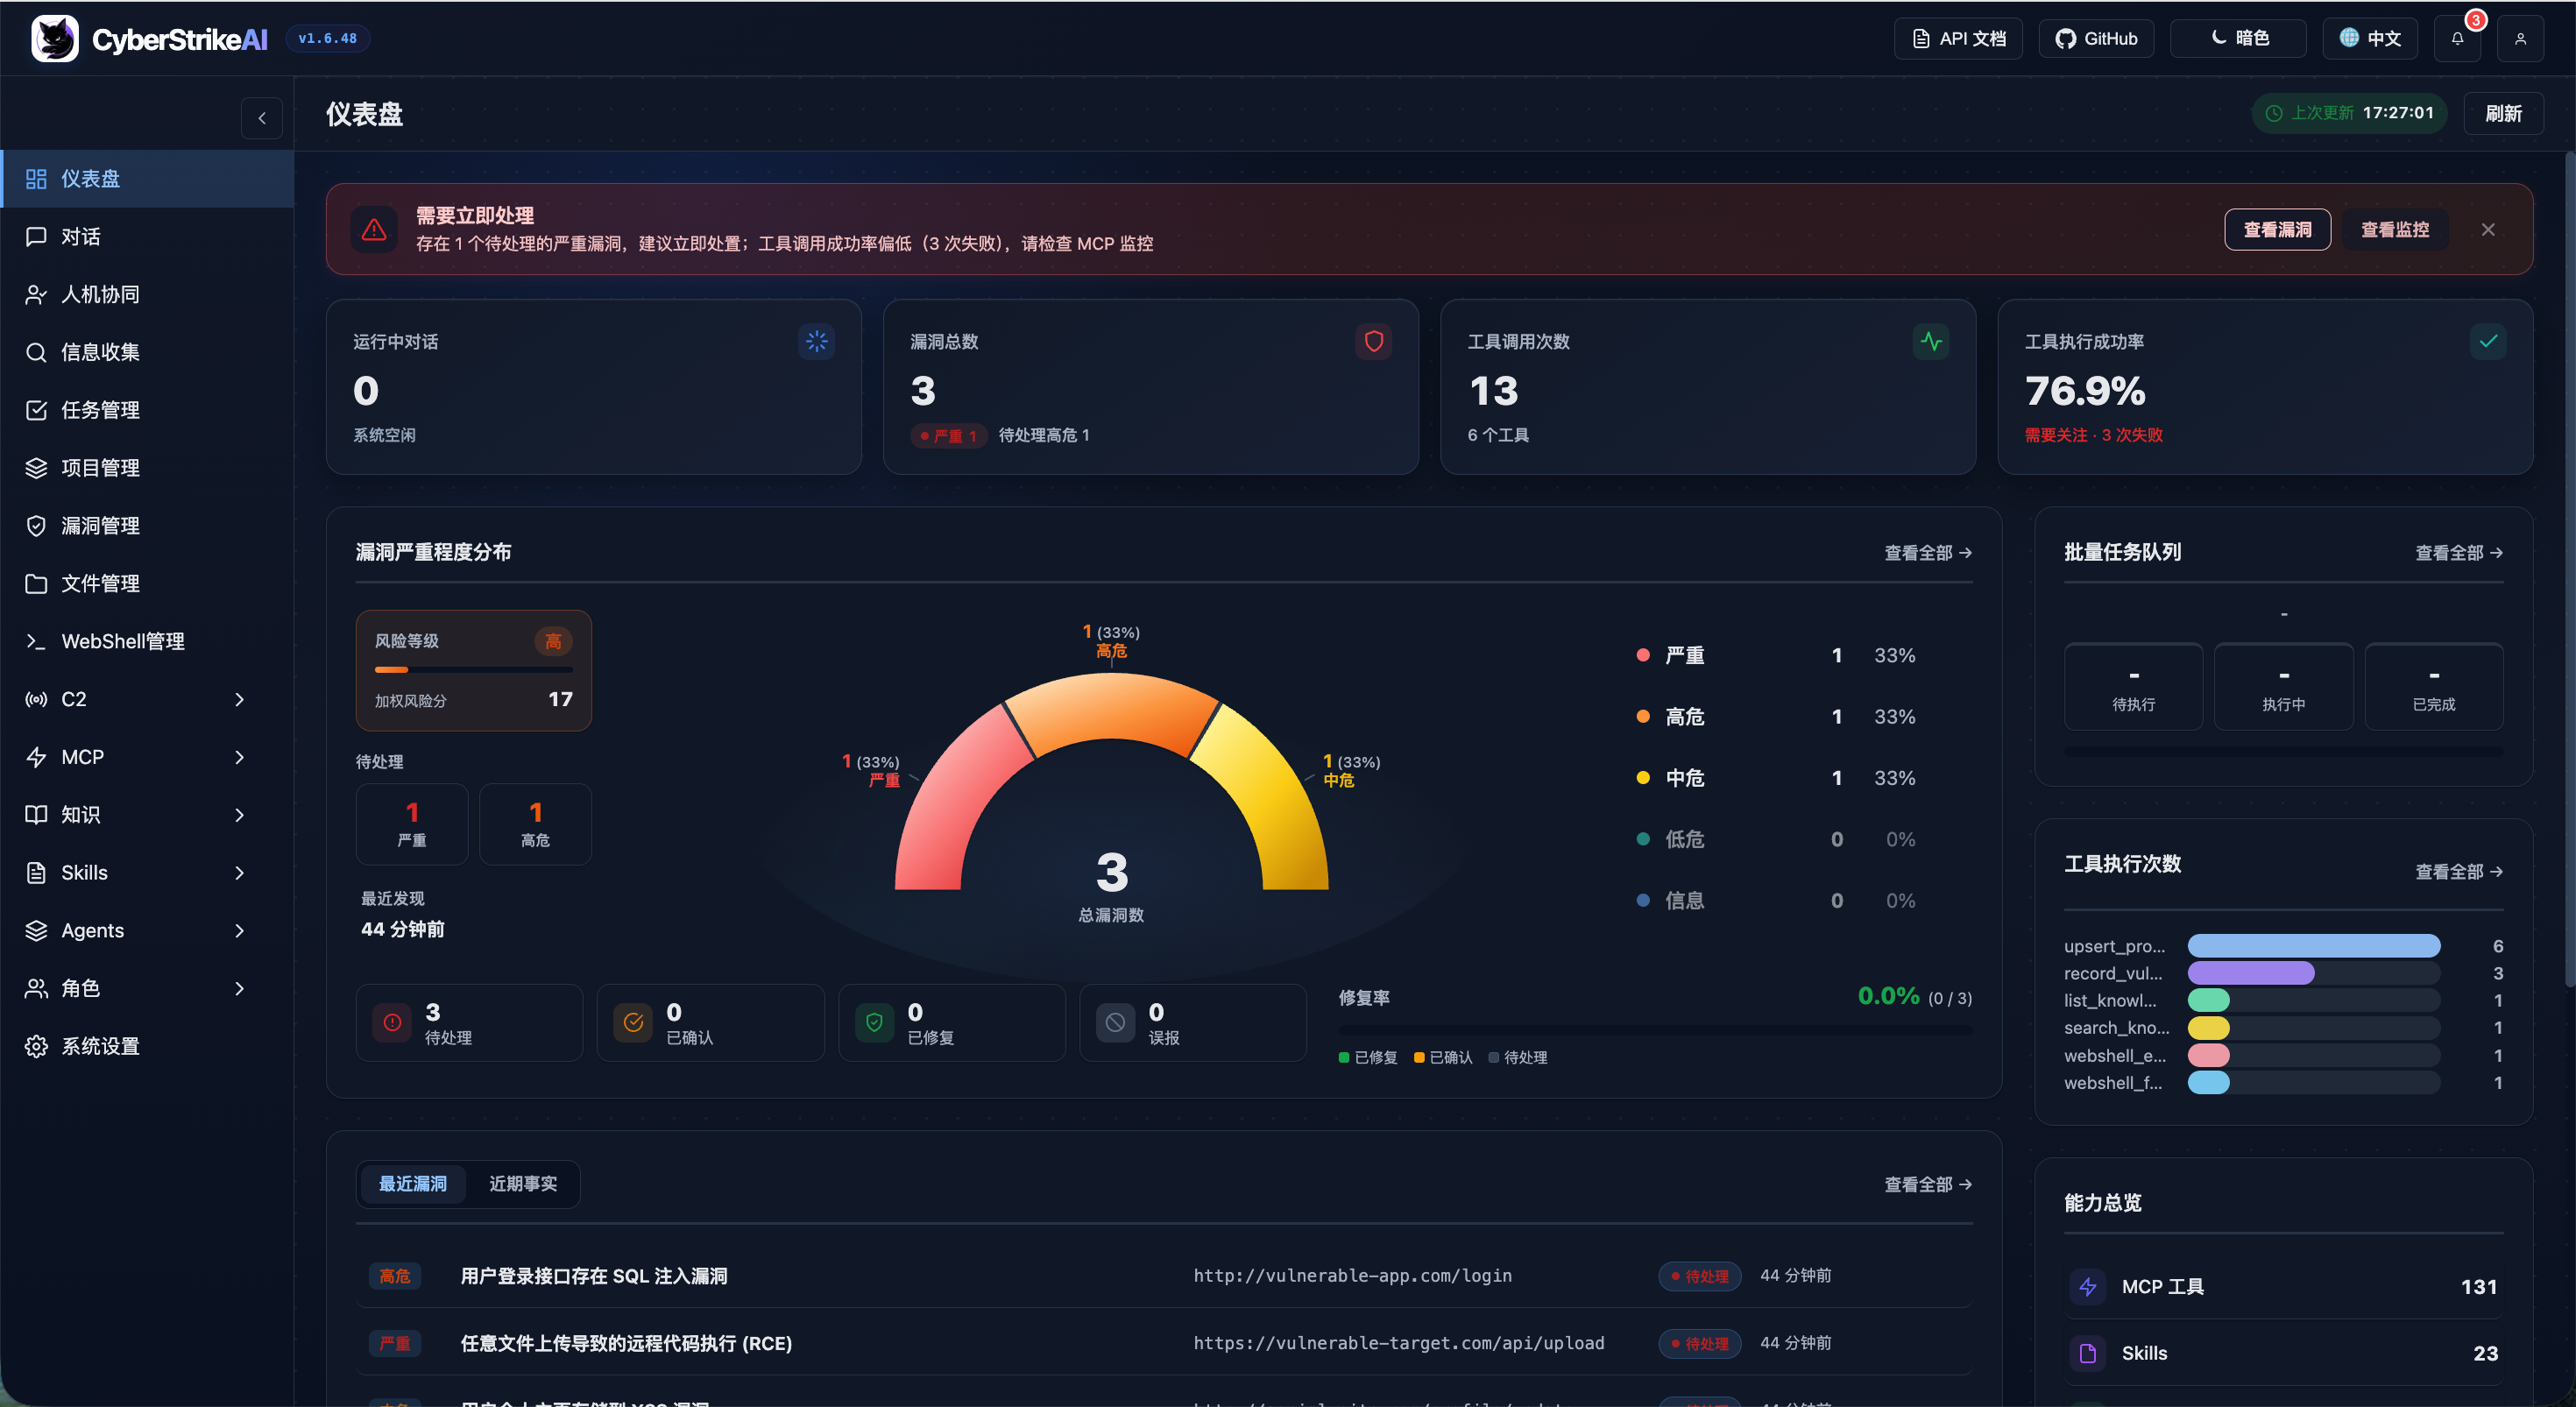 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
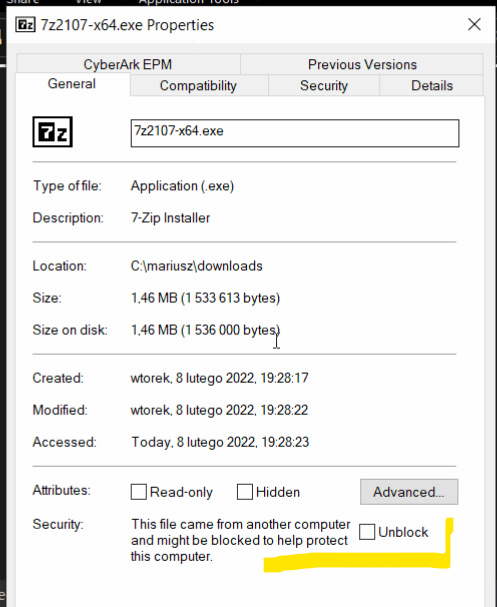 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
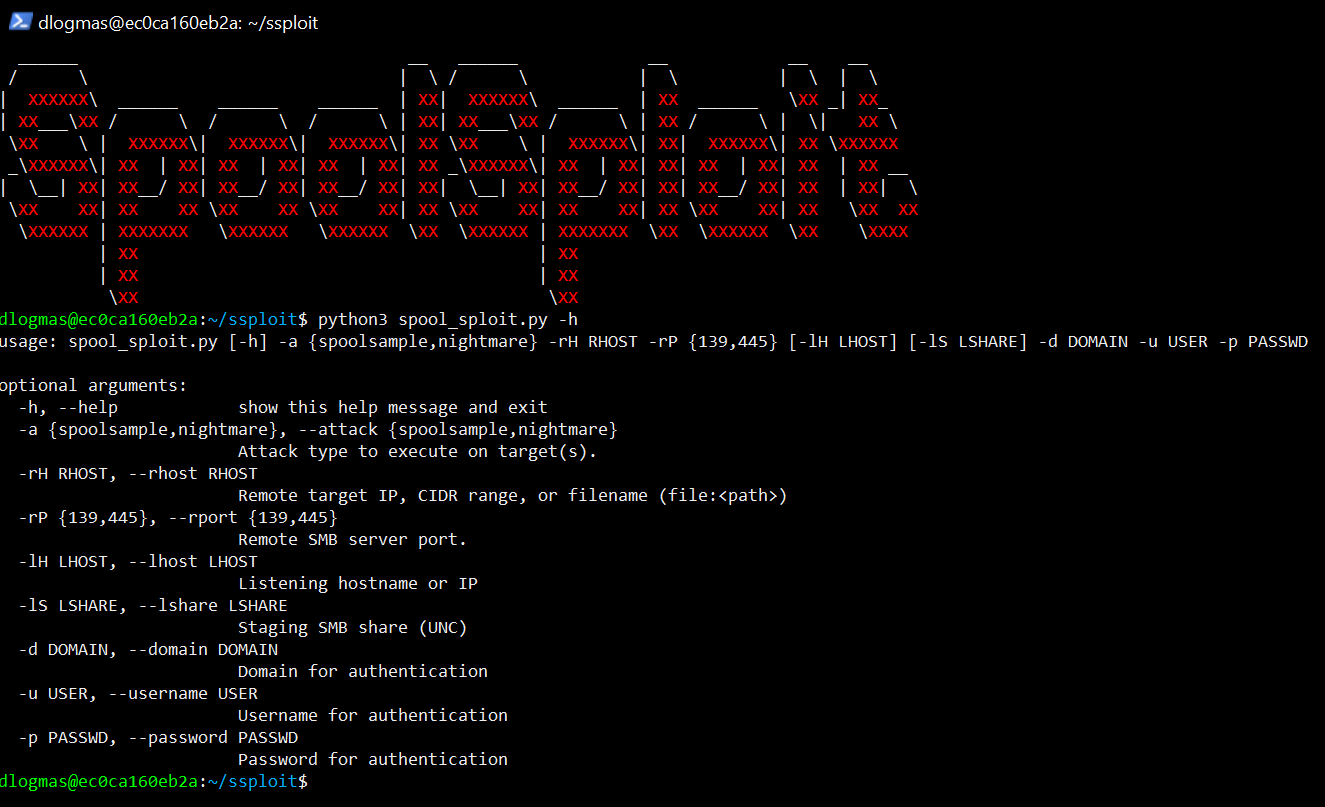 beetlechunks/spoolsploit
A collection of Windows print spooler exploits containerized with other utilities for practical exploitation.