
aqua-checksums
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
container-securitydefensive-toolsdevsecops+2
knqyf263/aqua-checksumsMonitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 jasalurah/creating-a-vulnerable-docker-environment-cve-2023-30212-
Docker-based vulnerable environment for practicing CVE-2023-30212 exploitation, featuring an OURPHP web app with a reflected XSS vulnerability for…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
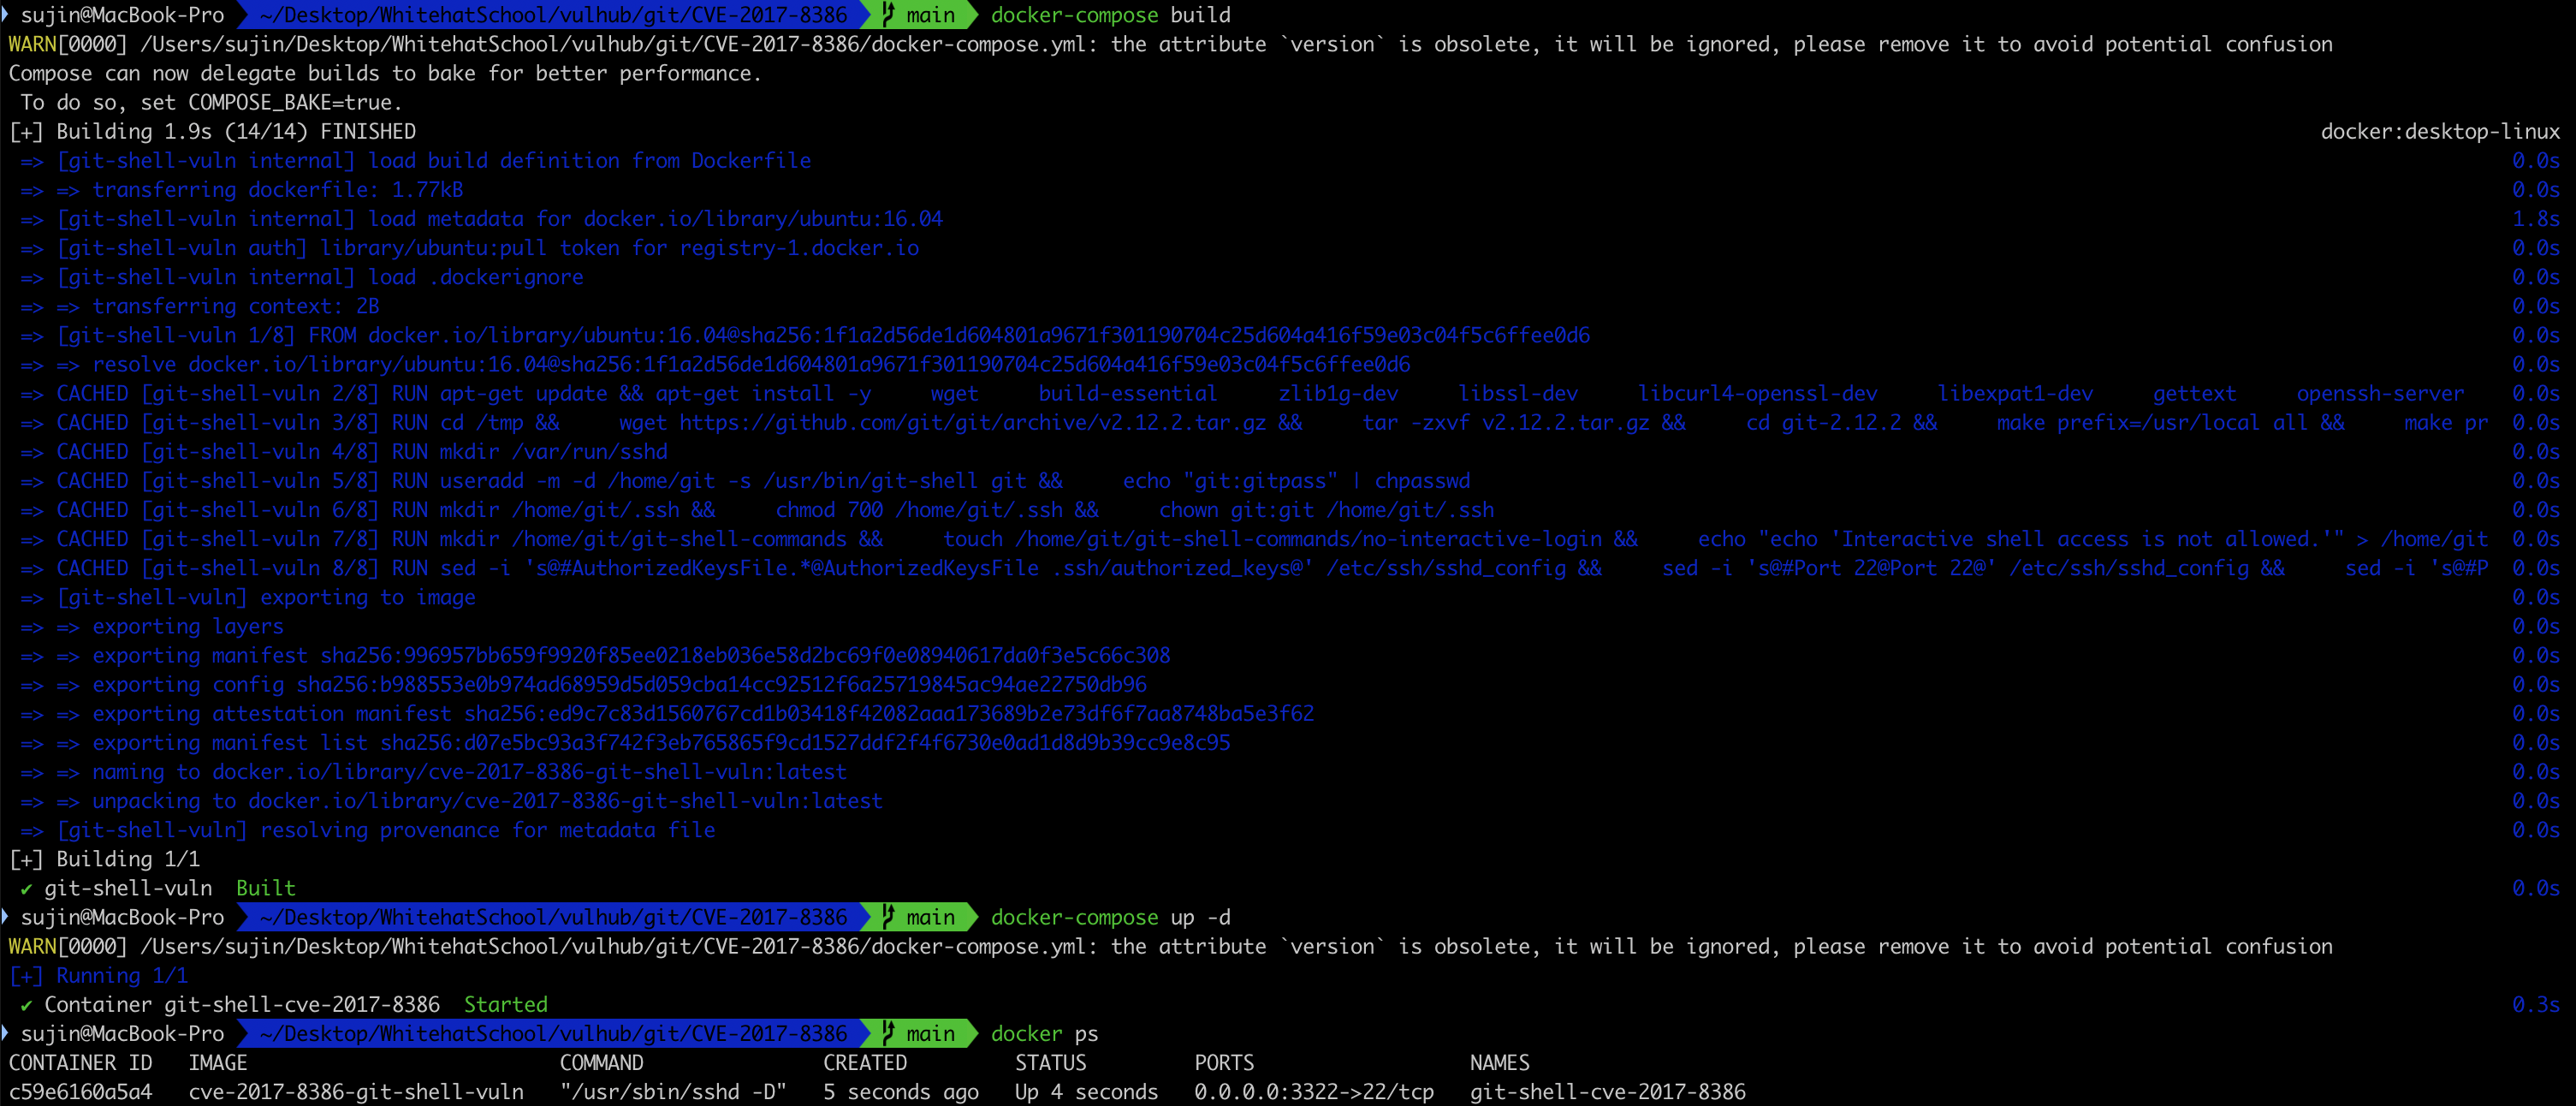 suz1n/whs3_vulhub
PoC for CVE-2017-8386 Git-Shell sandbox bypass vulnerability.
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 ssst0n3/docker-cve-2022-39253-poc
Proof-of-concept exploit for CVE-2022-39253 demonstrating Docker container escape via malicious Git repository build, enabling host file system read…

 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 mochizuki875/cve-2024-10220-githooks
CVE-2024-10220 Test repo
 twseptian/cve-2018-11235-git-submodule-ce-and-docker-ngrok-configuration
CVE-2018-11235-Git-Submodule-CE + Docker Ngrok Configuration