

horusec
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
cloud-securitycode-analysiscontainer-security+5
1.3k3 years ago
zupit/horusecHorusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
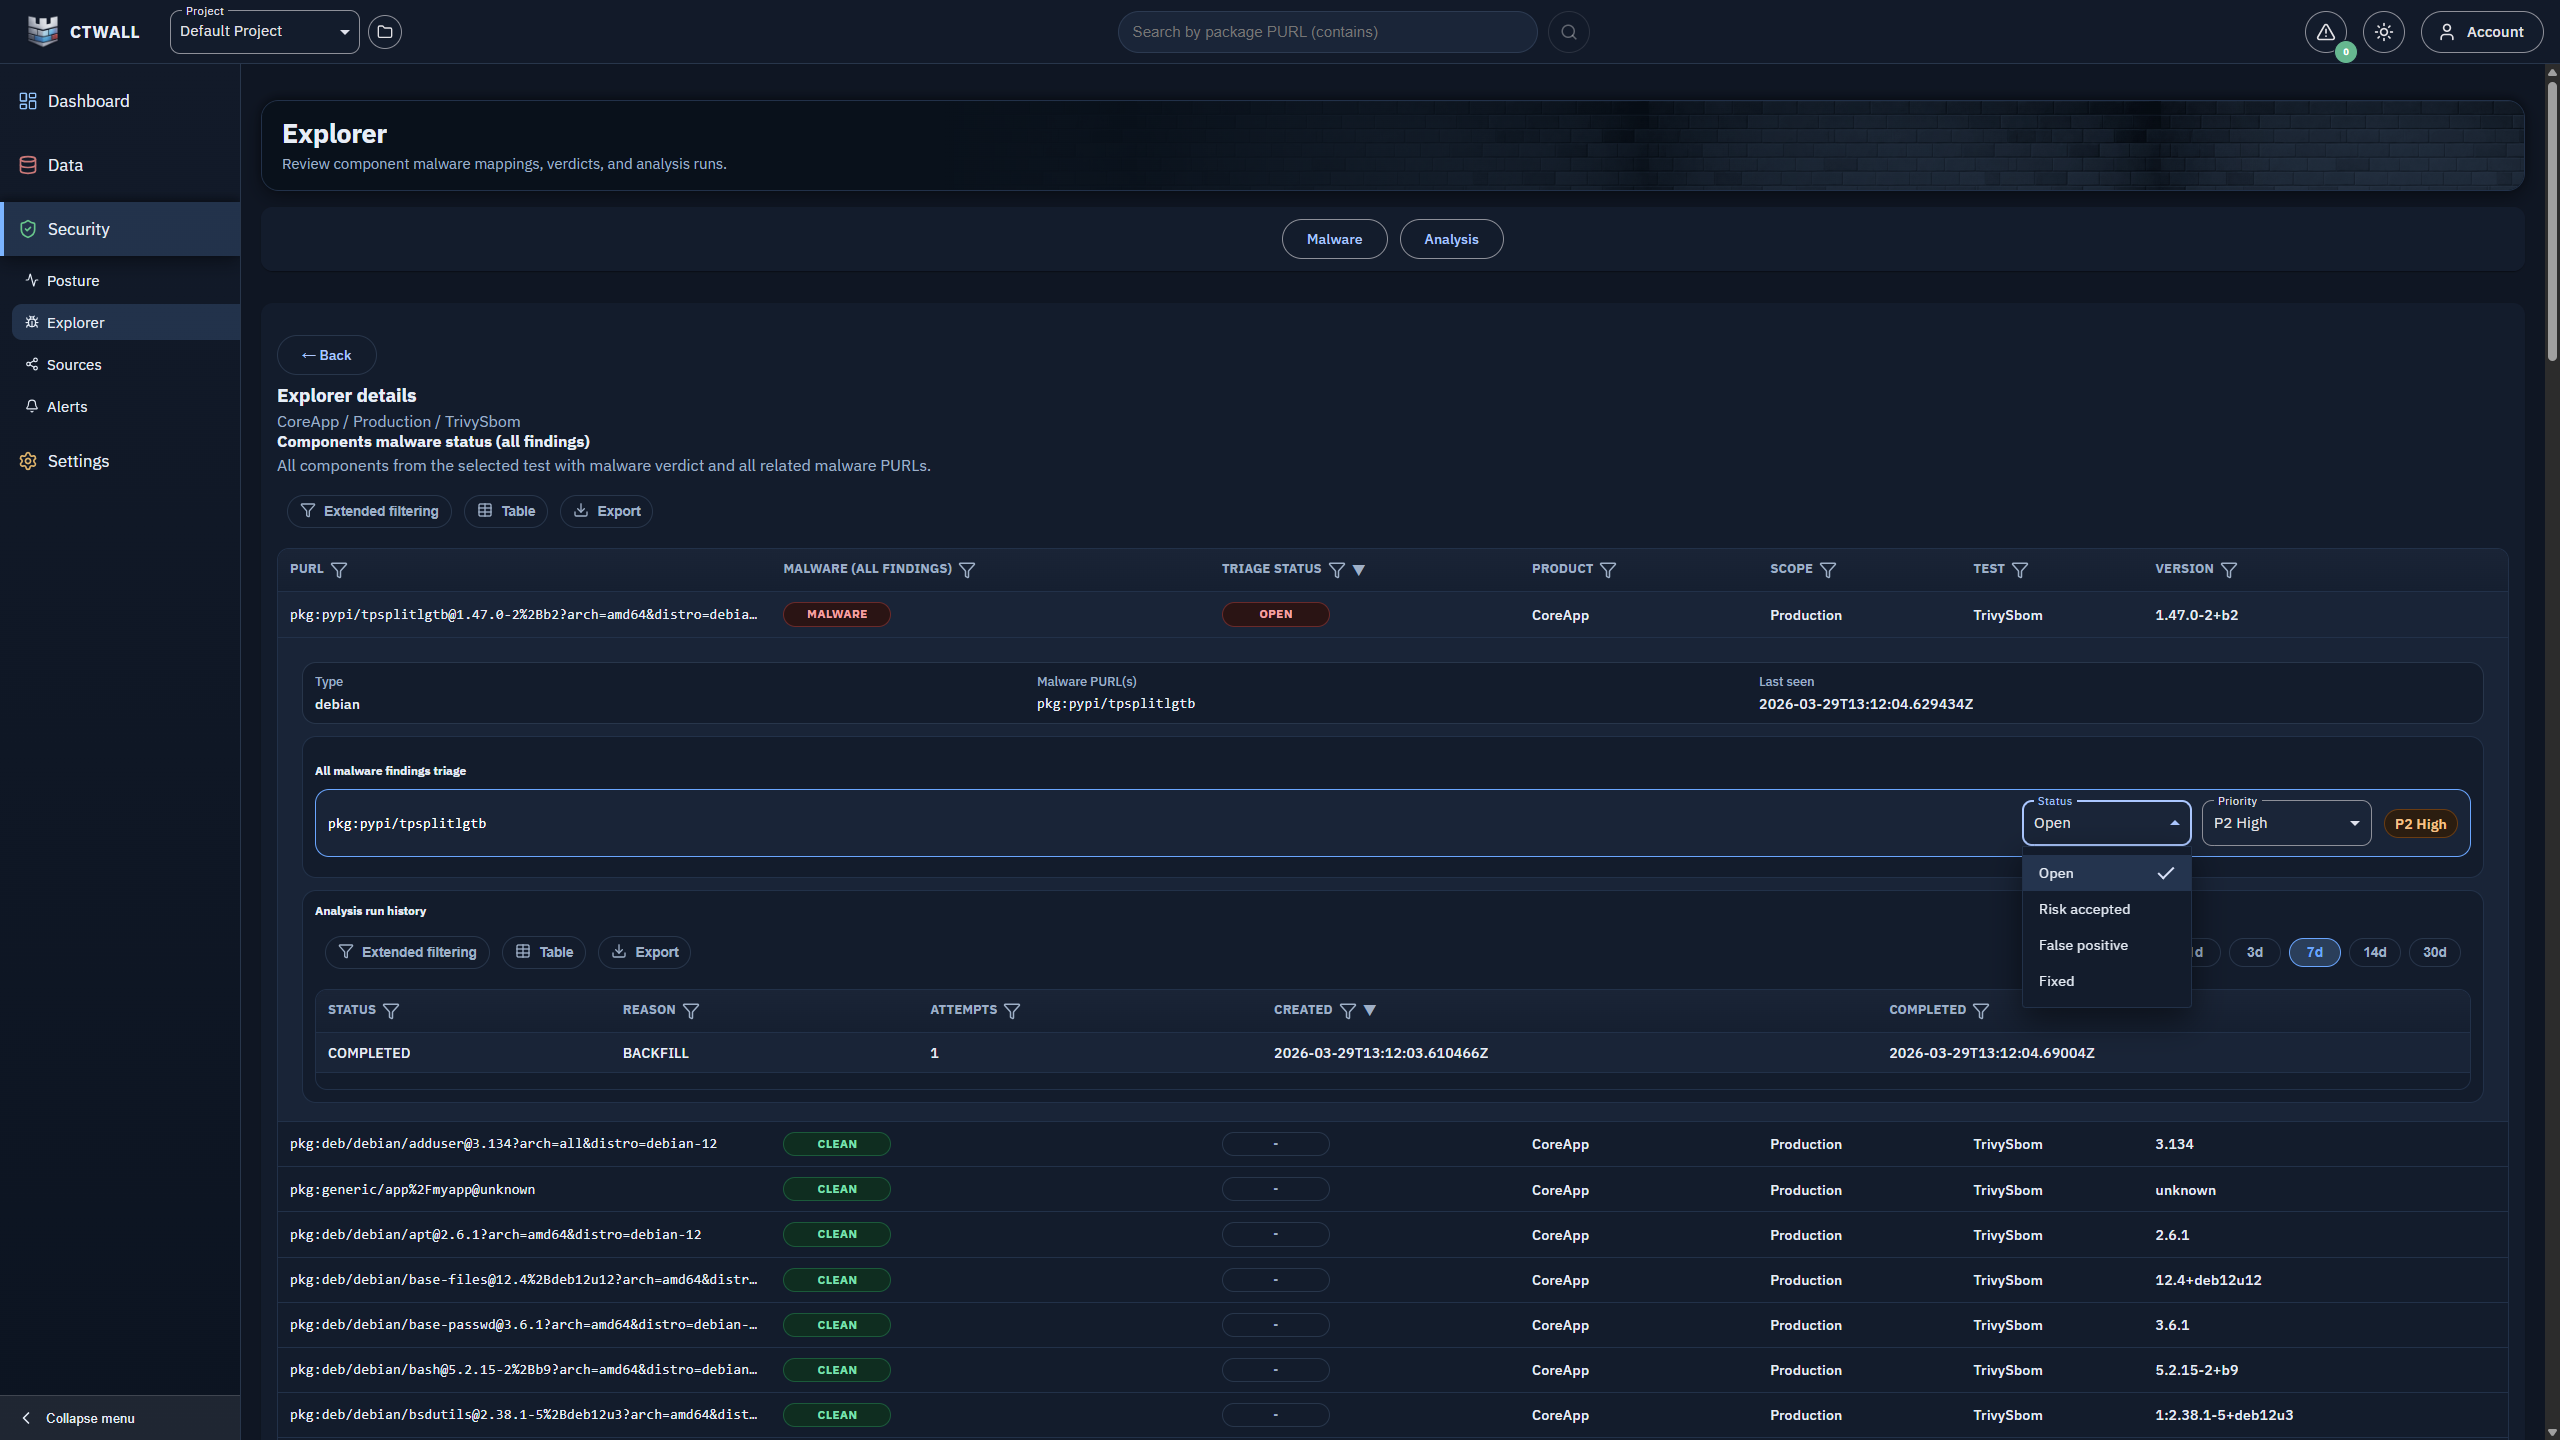 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
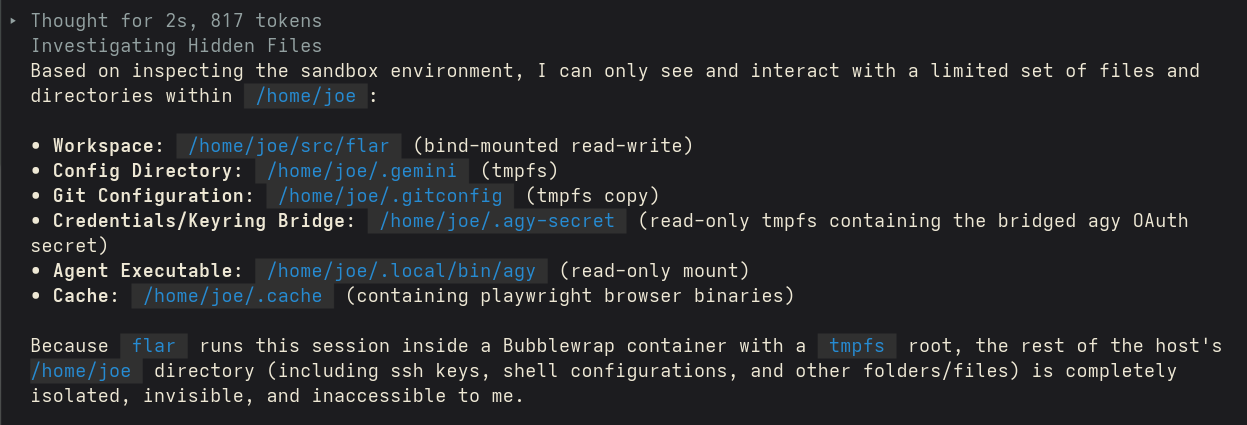 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 optiopay/klar
Integration of Clair and Docker Registry
 0xbingo/cve-2025-1974
A minimal test tool to help detect annotation injection vulnerabilities in Kubernetes NGINX Ingress controllers. This script sends a crafted…
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2018-15961
Docker container for CVE-2018-15961, part of the Cved framework for managing and testing vulnerable Docker environments in security labs.
 cved-sources/cve-2018-9208
Docker container exploit for CVE-2018-9208, part of the Cved framework for managing and testing vulnerable containers in security labs.
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 cved-sources/cve-2017-4971
Docker-based vulnerable environment for CVE-2017-4971 (Spring WebFlow RCE) to practice exploitation and security testing in a controlled lab setup.
 cved-sources/cve-2015-5602
Docker container with CVE-2015-5602 for practicing privilege escalation in a controlled environment. Part of the Cved framework for managing…
 cved-sources/cve-2015-1427
Docker container with a pre-configured vulnerable Elasticsearch instance for practicing CVE-2015-1427 exploitation in a safe lab environment.
 cved-sources/cve-2019-9194
Docker container with CVE-2019-9194 for practicing vulnerability exploitation in a controlled environment. Part of the Cved vulnerable container…
 cved-sources/cve-2010-0426
Docker container with a pre-configured CVE-2010-0426 environment for practicing privilege escalation exploitation in a controlled lab setting.