
neko
 m1k1o/neko
A self hosted virtual browser that runs in docker and uses WebRTC.
container-securityprivacyremote-access-tool+1
m1k1o/nekoA self hosted virtual browser that runs in docker and uses WebRTC.
 skydive-project/skydive
An open source real-time network topology and protocols analyzer
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 mhaggis/package-inferno
A Public Package Scanner for The Community
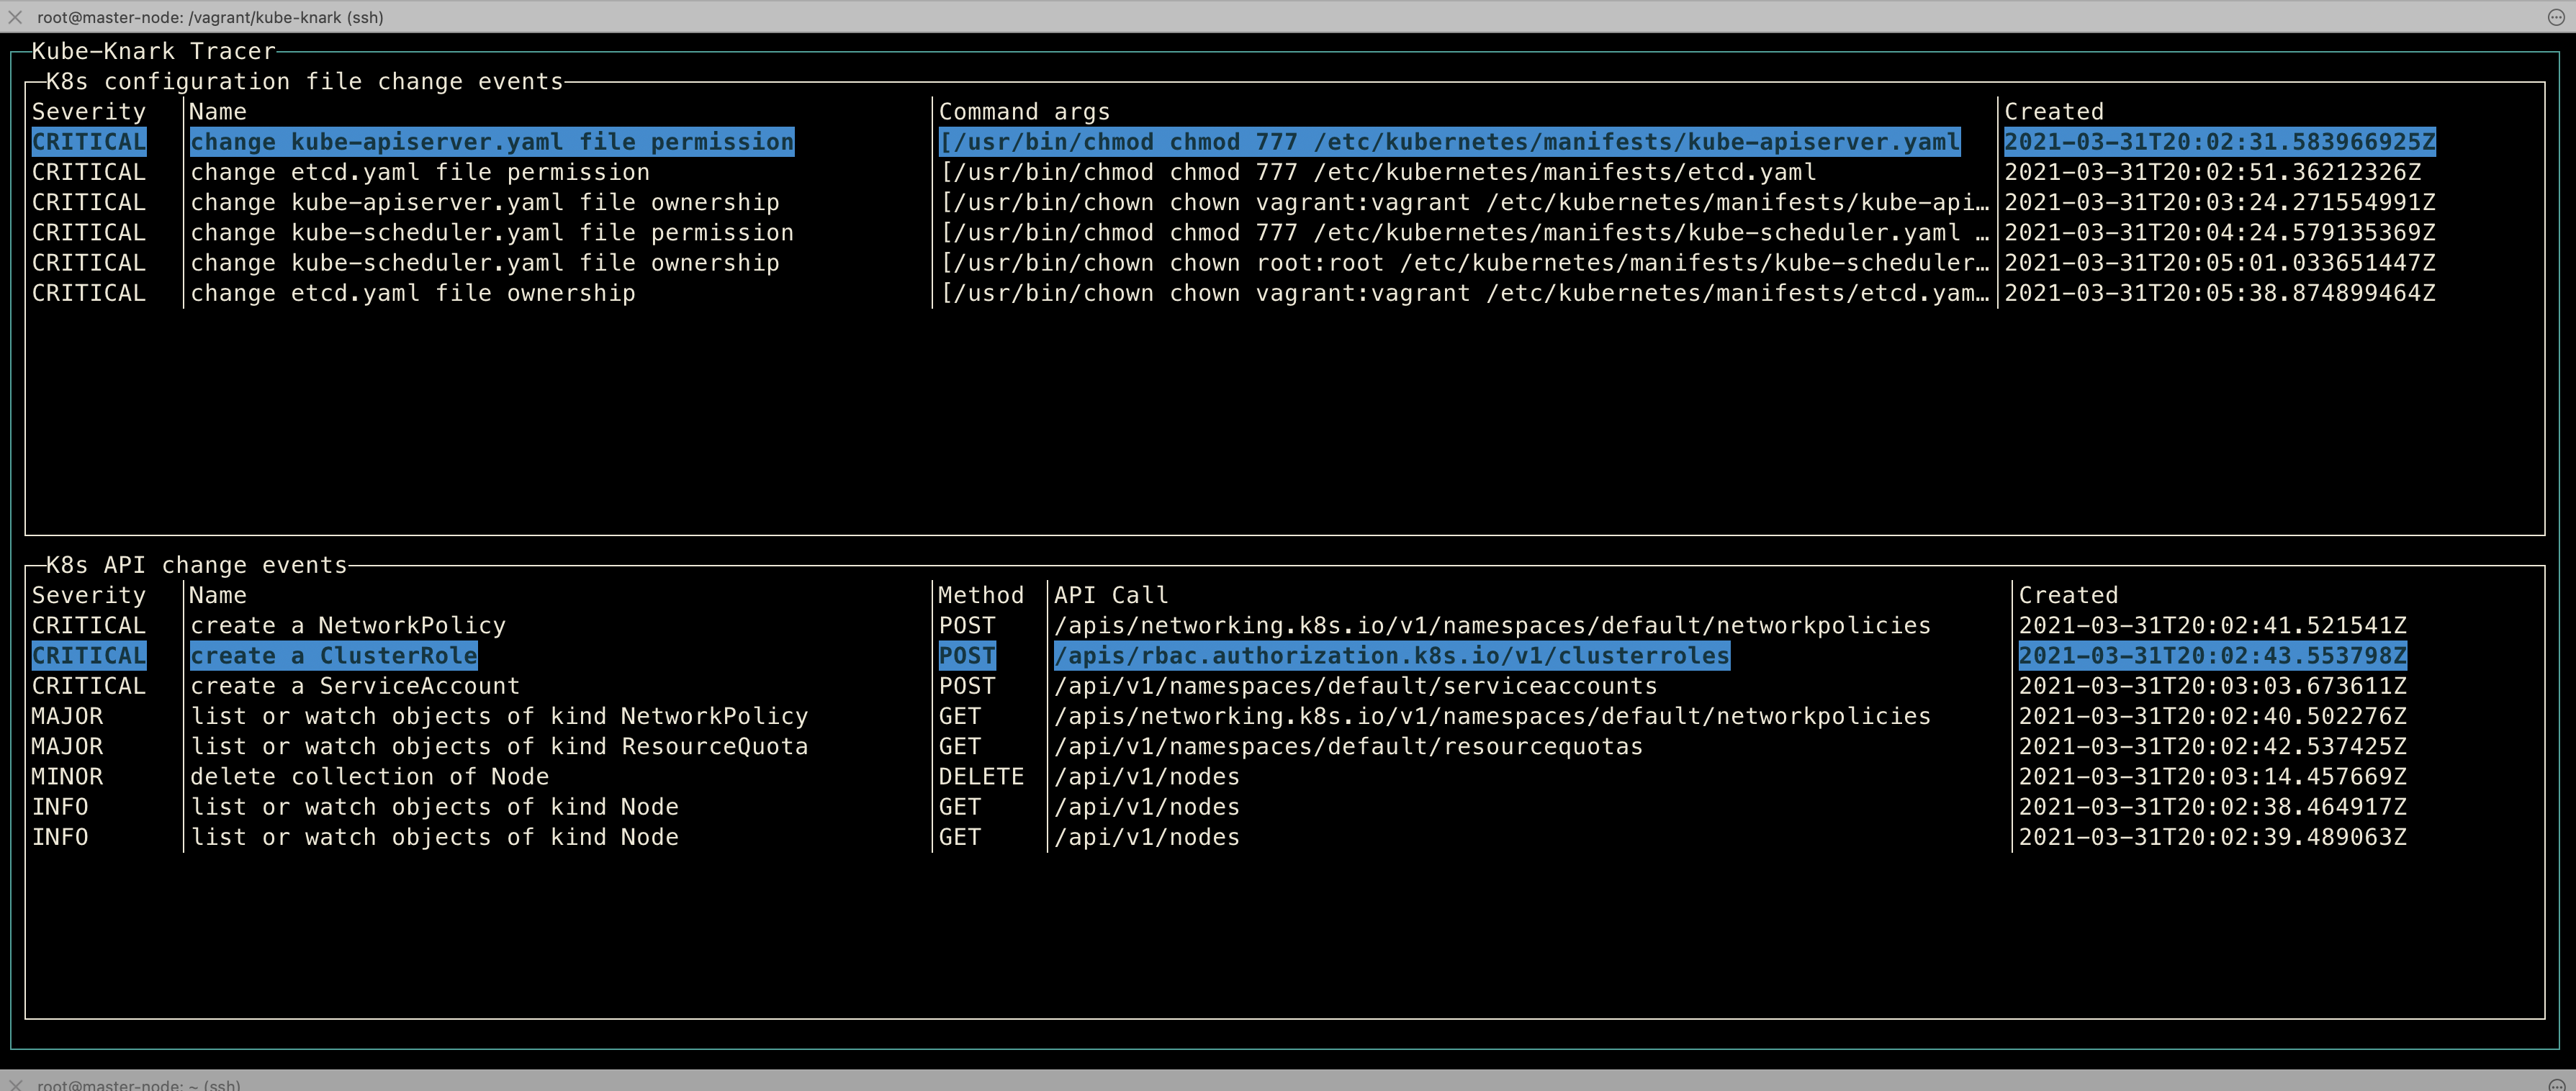 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
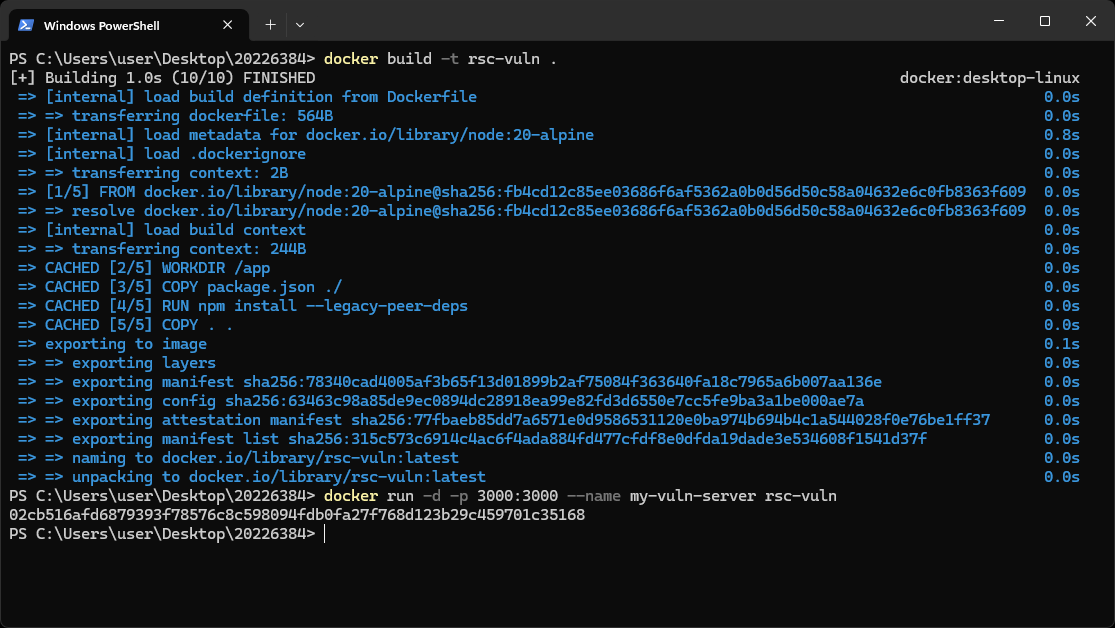
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 rootdirective-sec/cve-2026-23744-lab
Docker lab to compare vulnerable and patched builds of MCPJam Inspector for CVE-2026-23744, demonstrating network binding differences and API…
 chaostoolkit/chaostoolkit-kubernetes
Kubernetes driver extension of the Chaos Toolkit probes and actions API
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
 gravitational/cve-2018-1002105
Kubernetes cluster vulnerability scanner that detects CVE-2018-1002105 by testing for unauthenticated API access and privilege escalation via…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
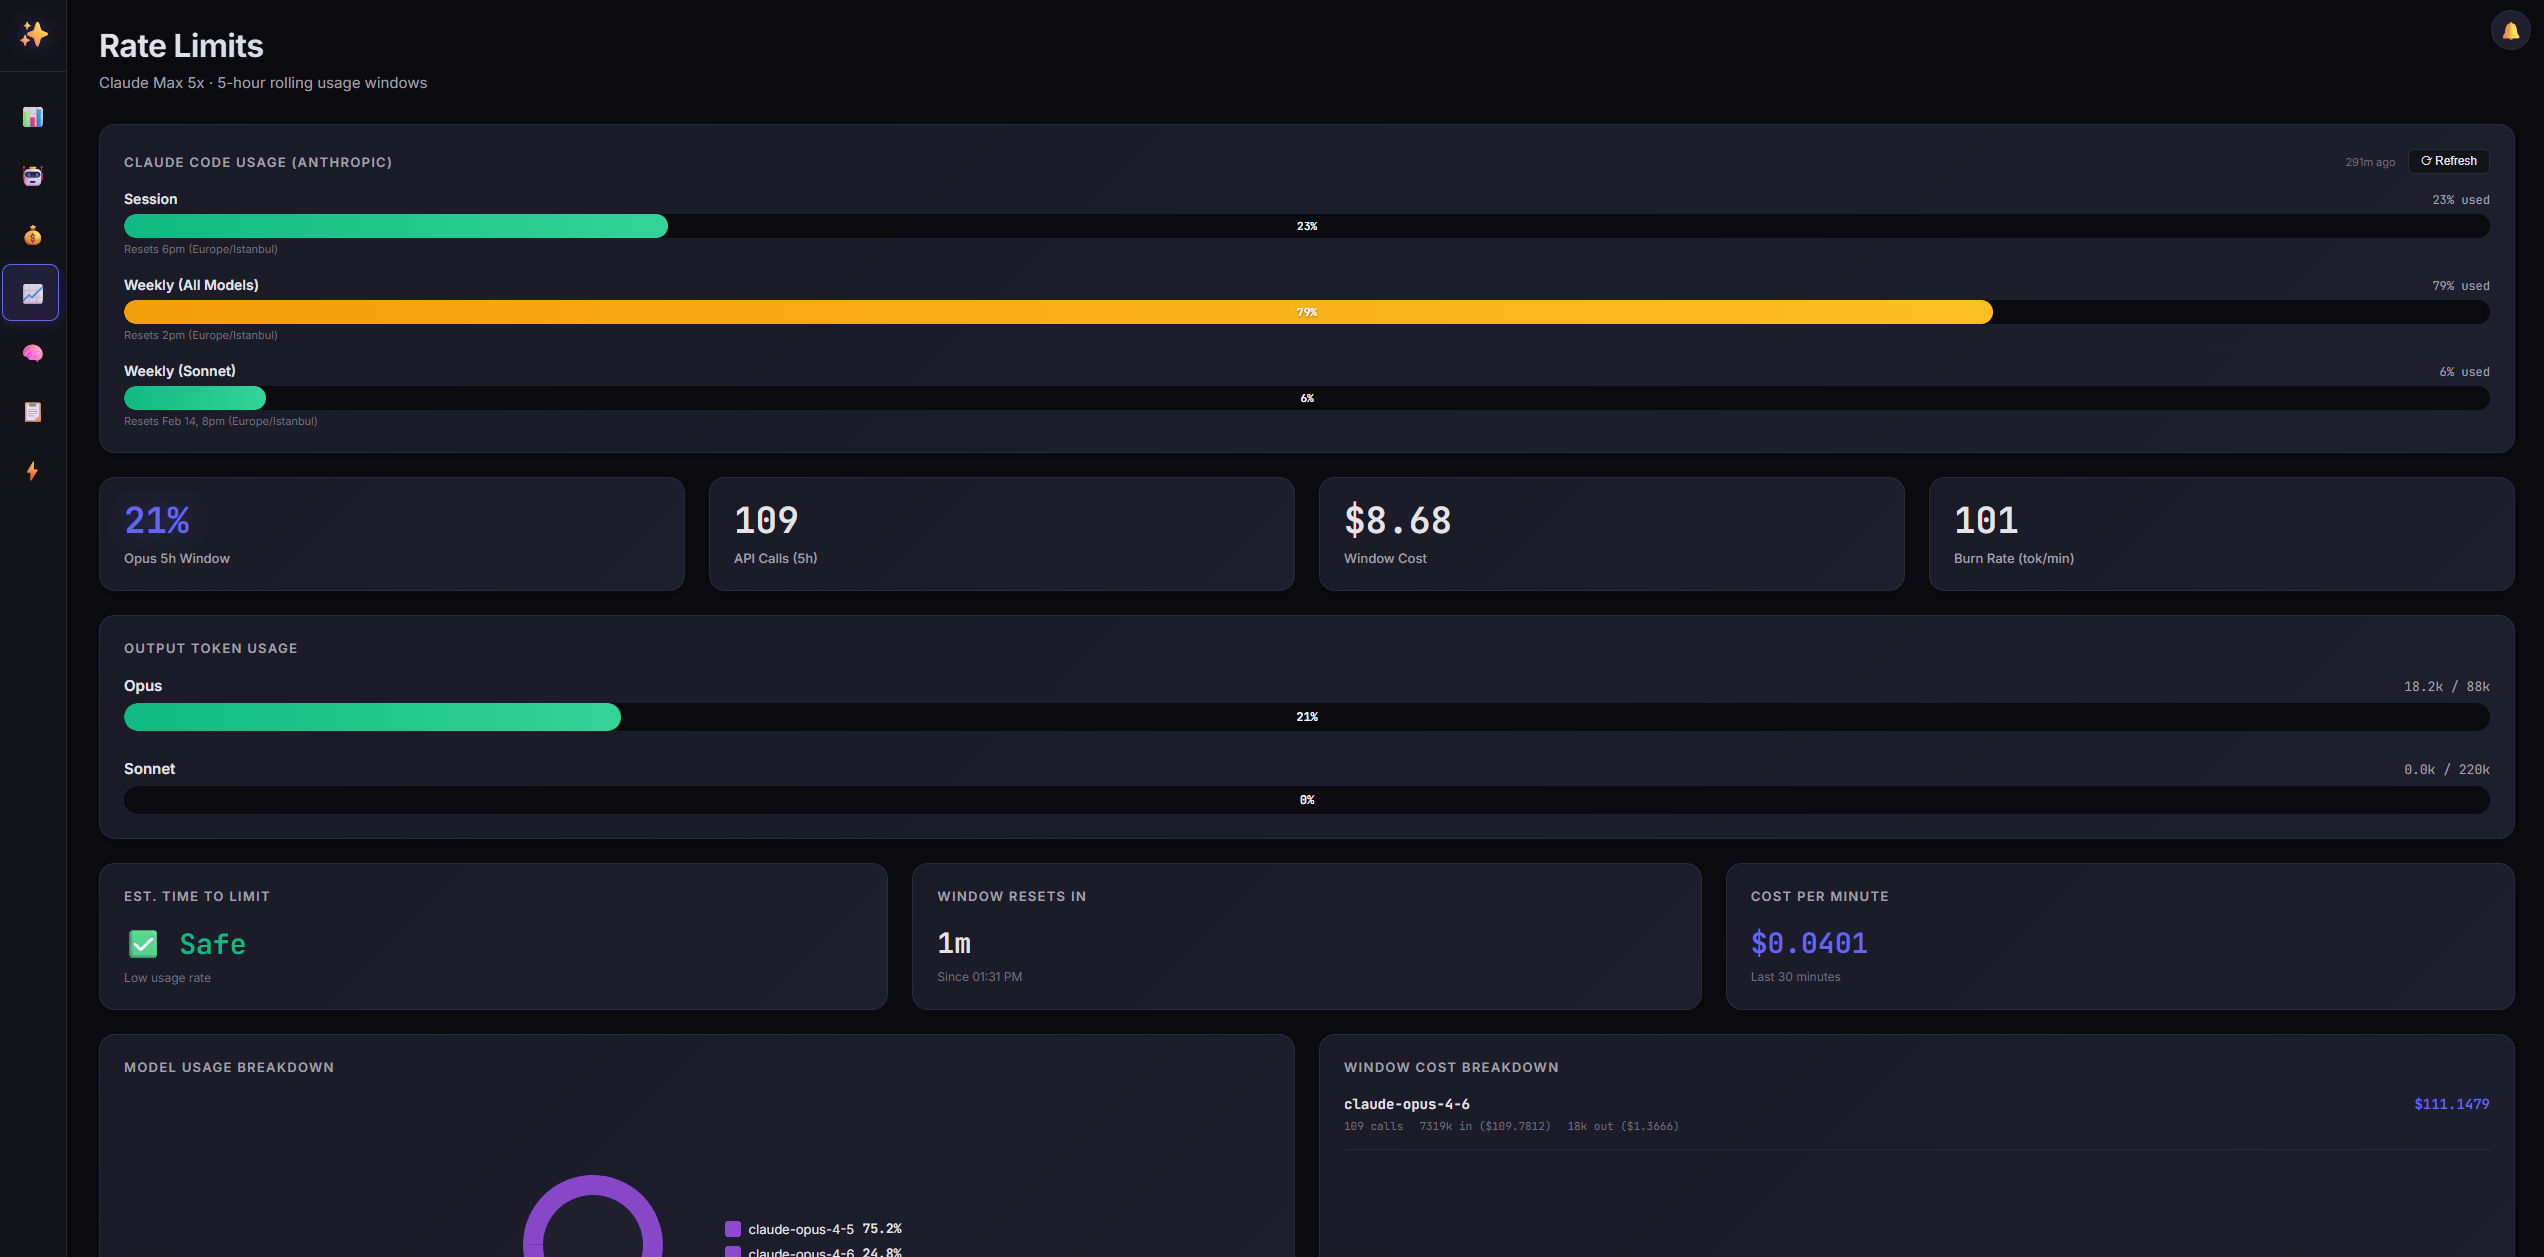 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.