
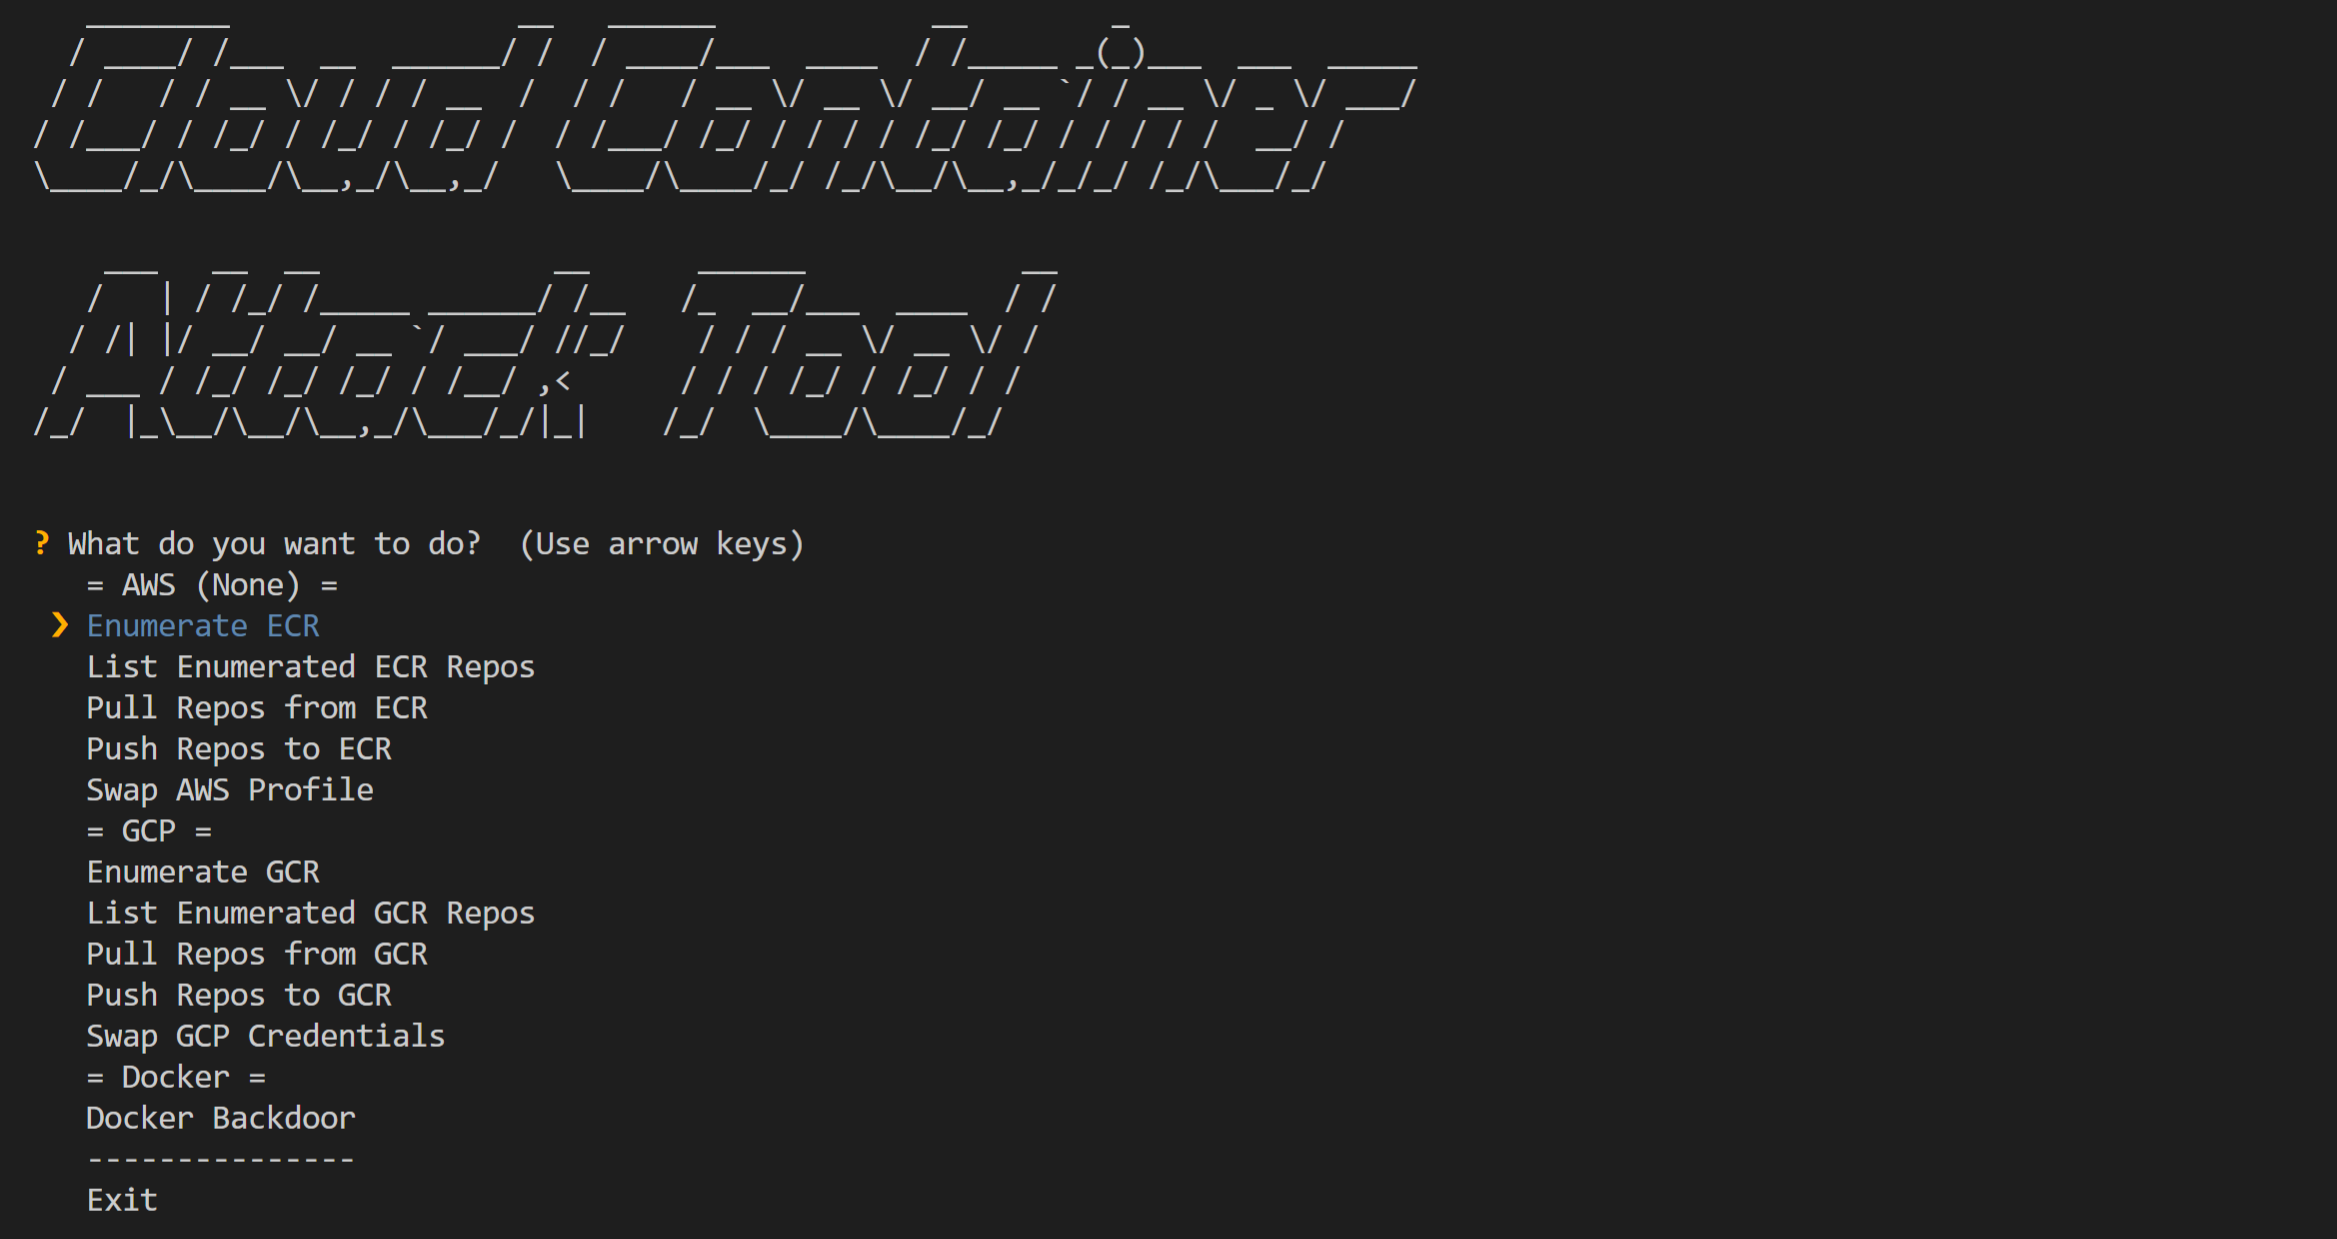
ccat
 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
cloud-securitycontainer-securityexploitation+1
6536 years ago
rhinosecuritylabs/ccatCloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
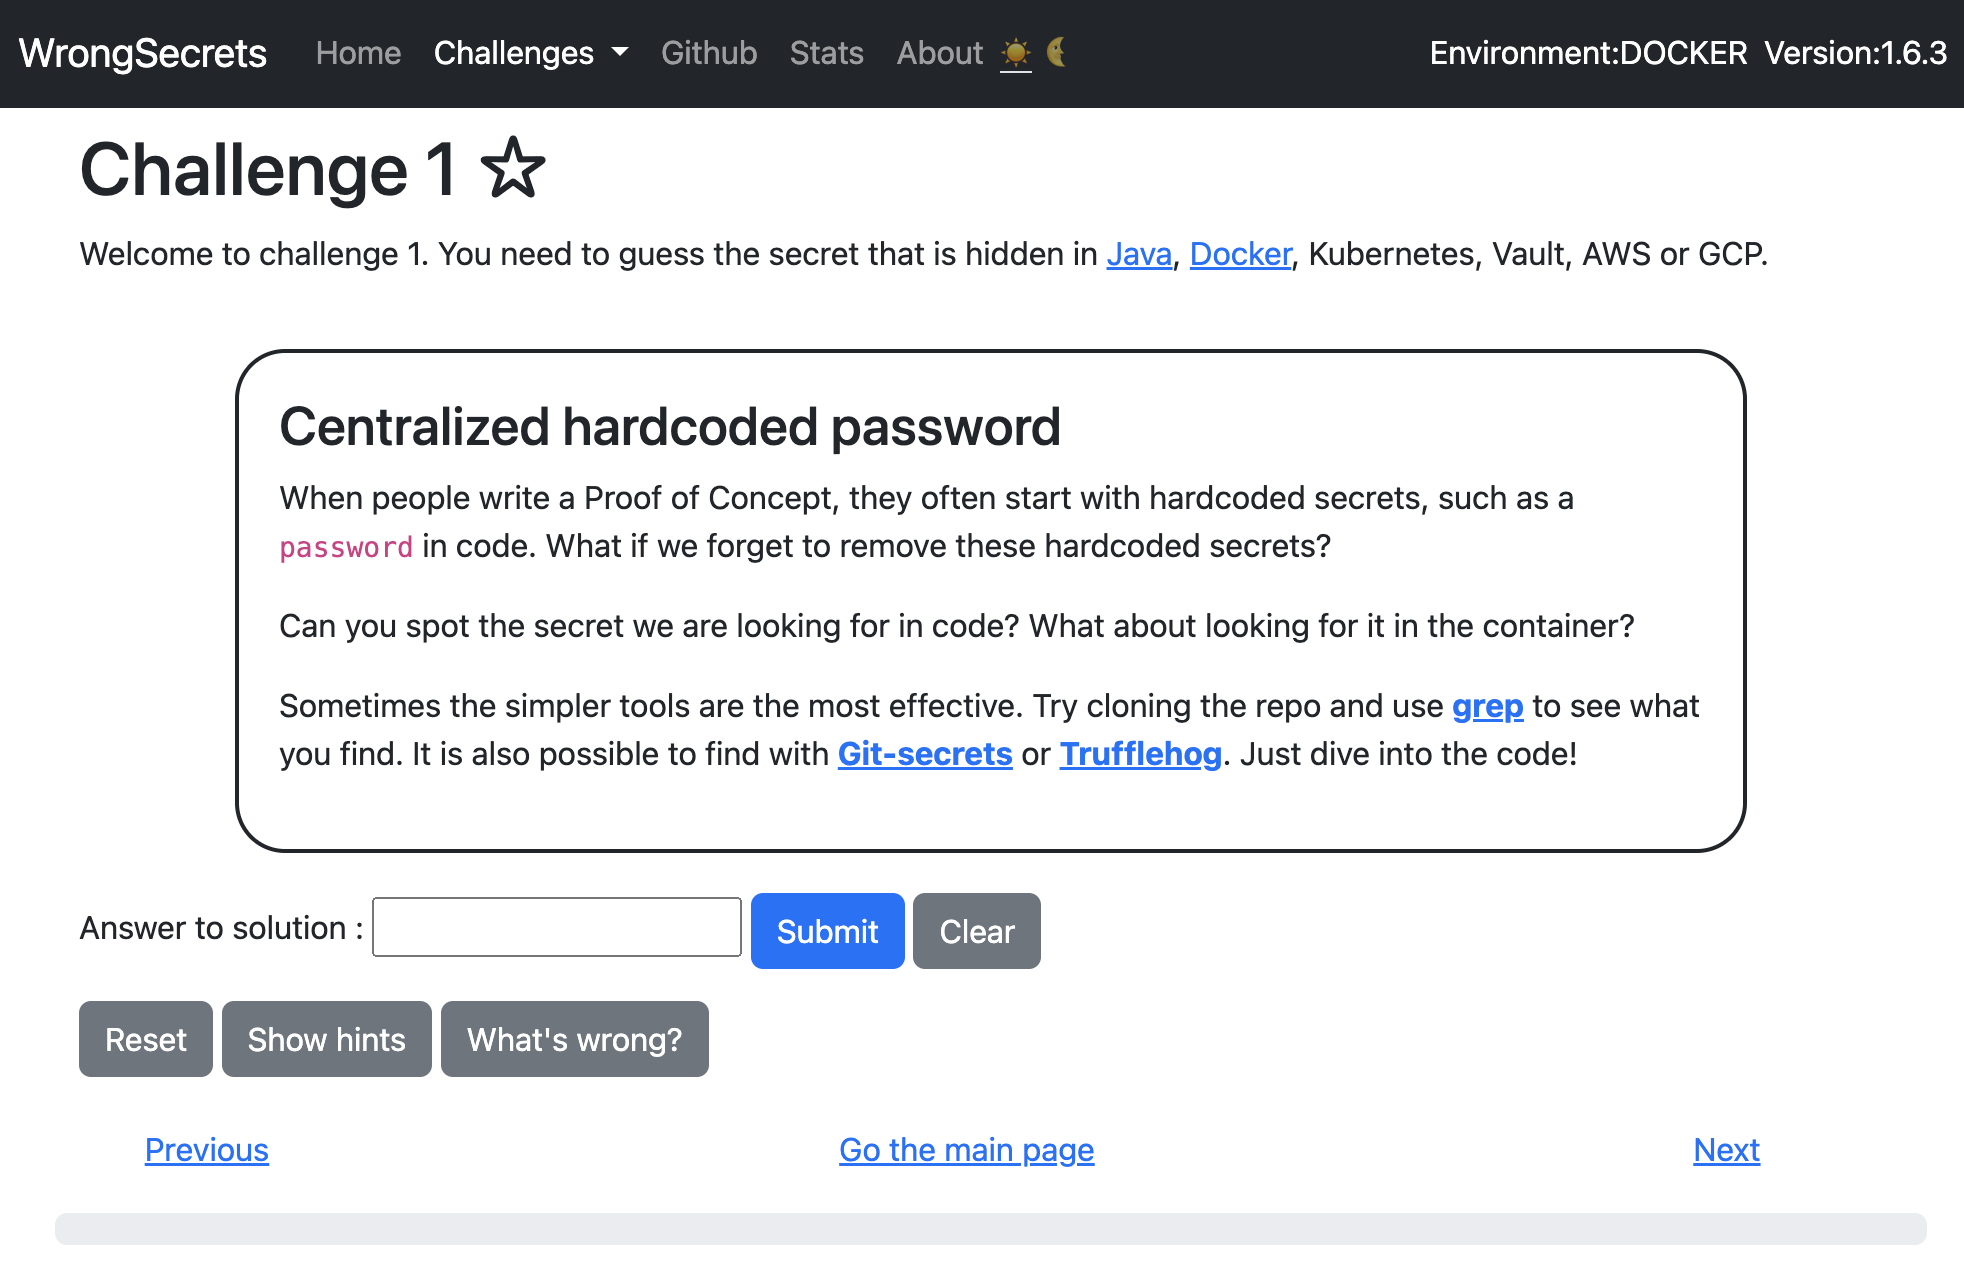 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 wshinkle/cve-2023-2982
Python exploit script for CVE-2023-2982, packaged in a Docker container for automated deployment and testing against vulnerable targets.
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
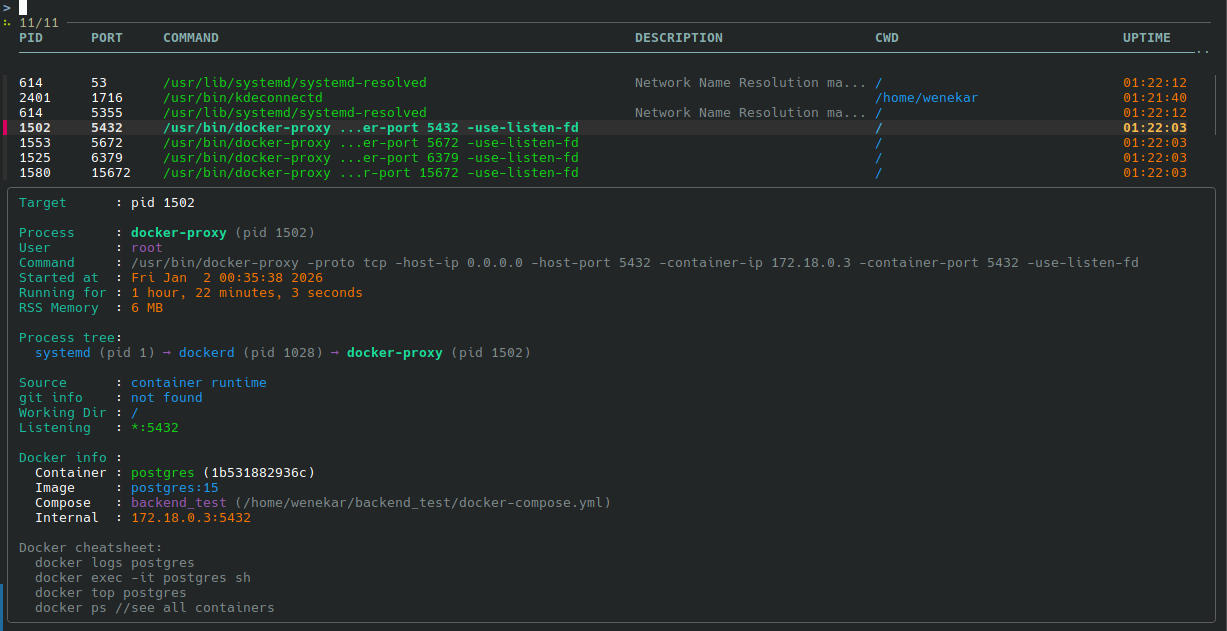 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…