
CVE-2023-2982
 wshinkle/cve-2023-2982
Python exploit script for CVE-2023-2982, packaged in a Docker container for automated deployment and testing against vulnerable targets.
container-securityexploitationscripting-automation+2
wshinkle/cve-2023-2982Python exploit script for CVE-2023-2982, packaged in a Docker container for automated deployment and testing against vulnerable targets.
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
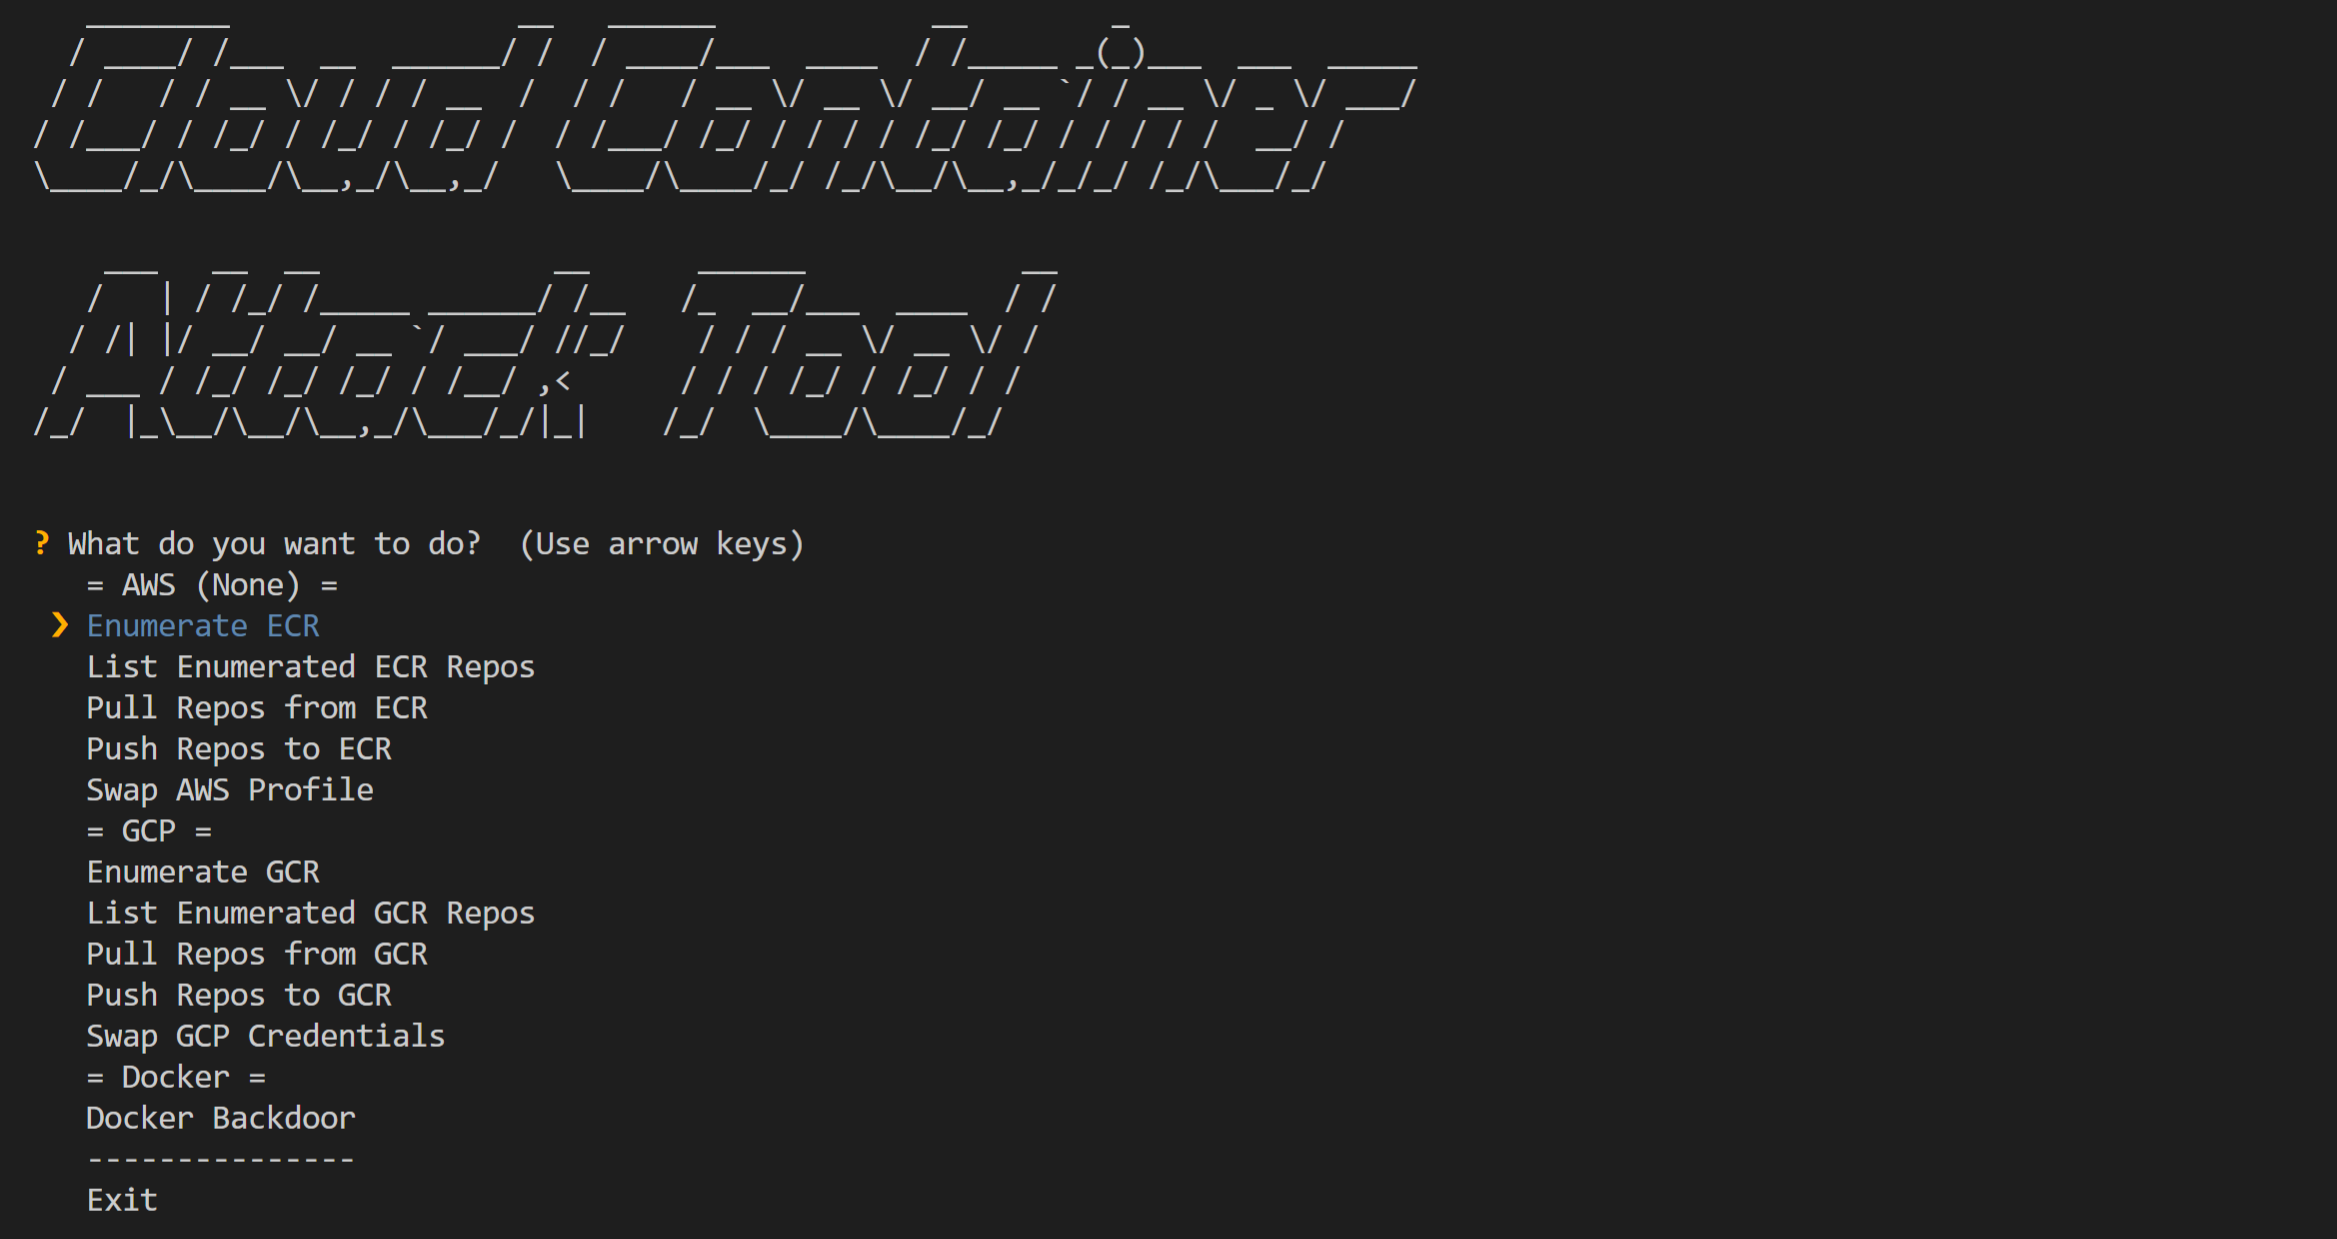 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
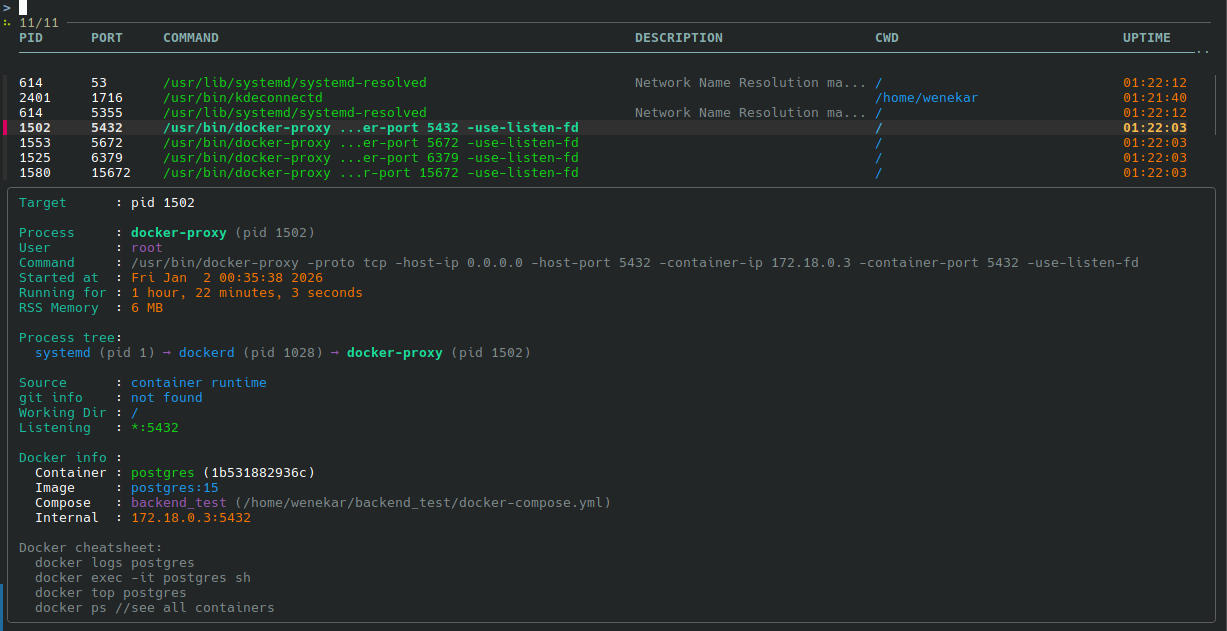 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431