
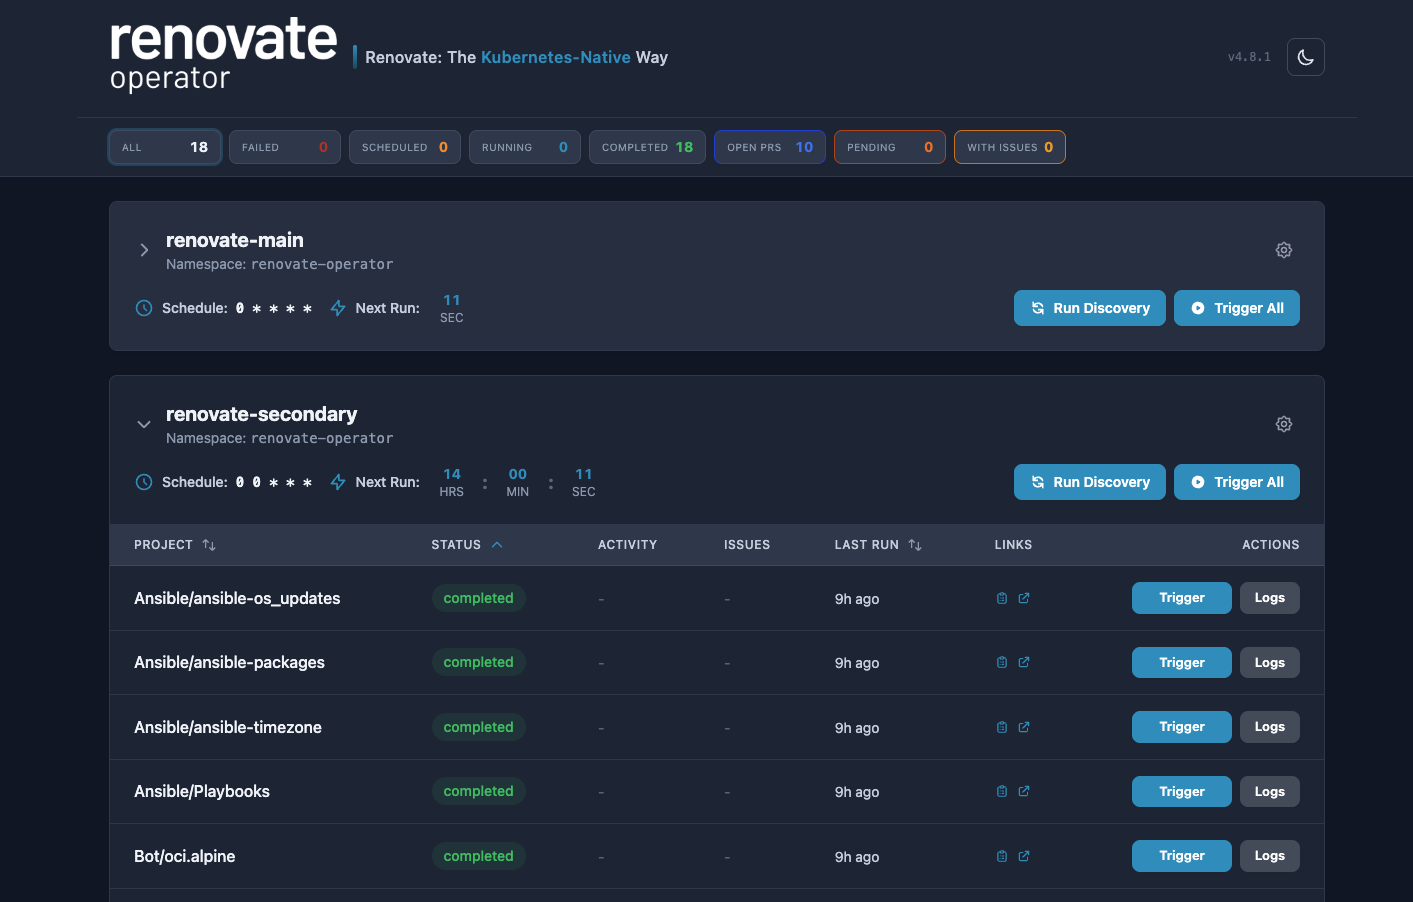
renovate-operator
 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
cloud-securityconfiguration-auditingcontainer-security+4
539
mogenius/renovate-operatorOperator to streamline renovate executions in Kubernetes
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
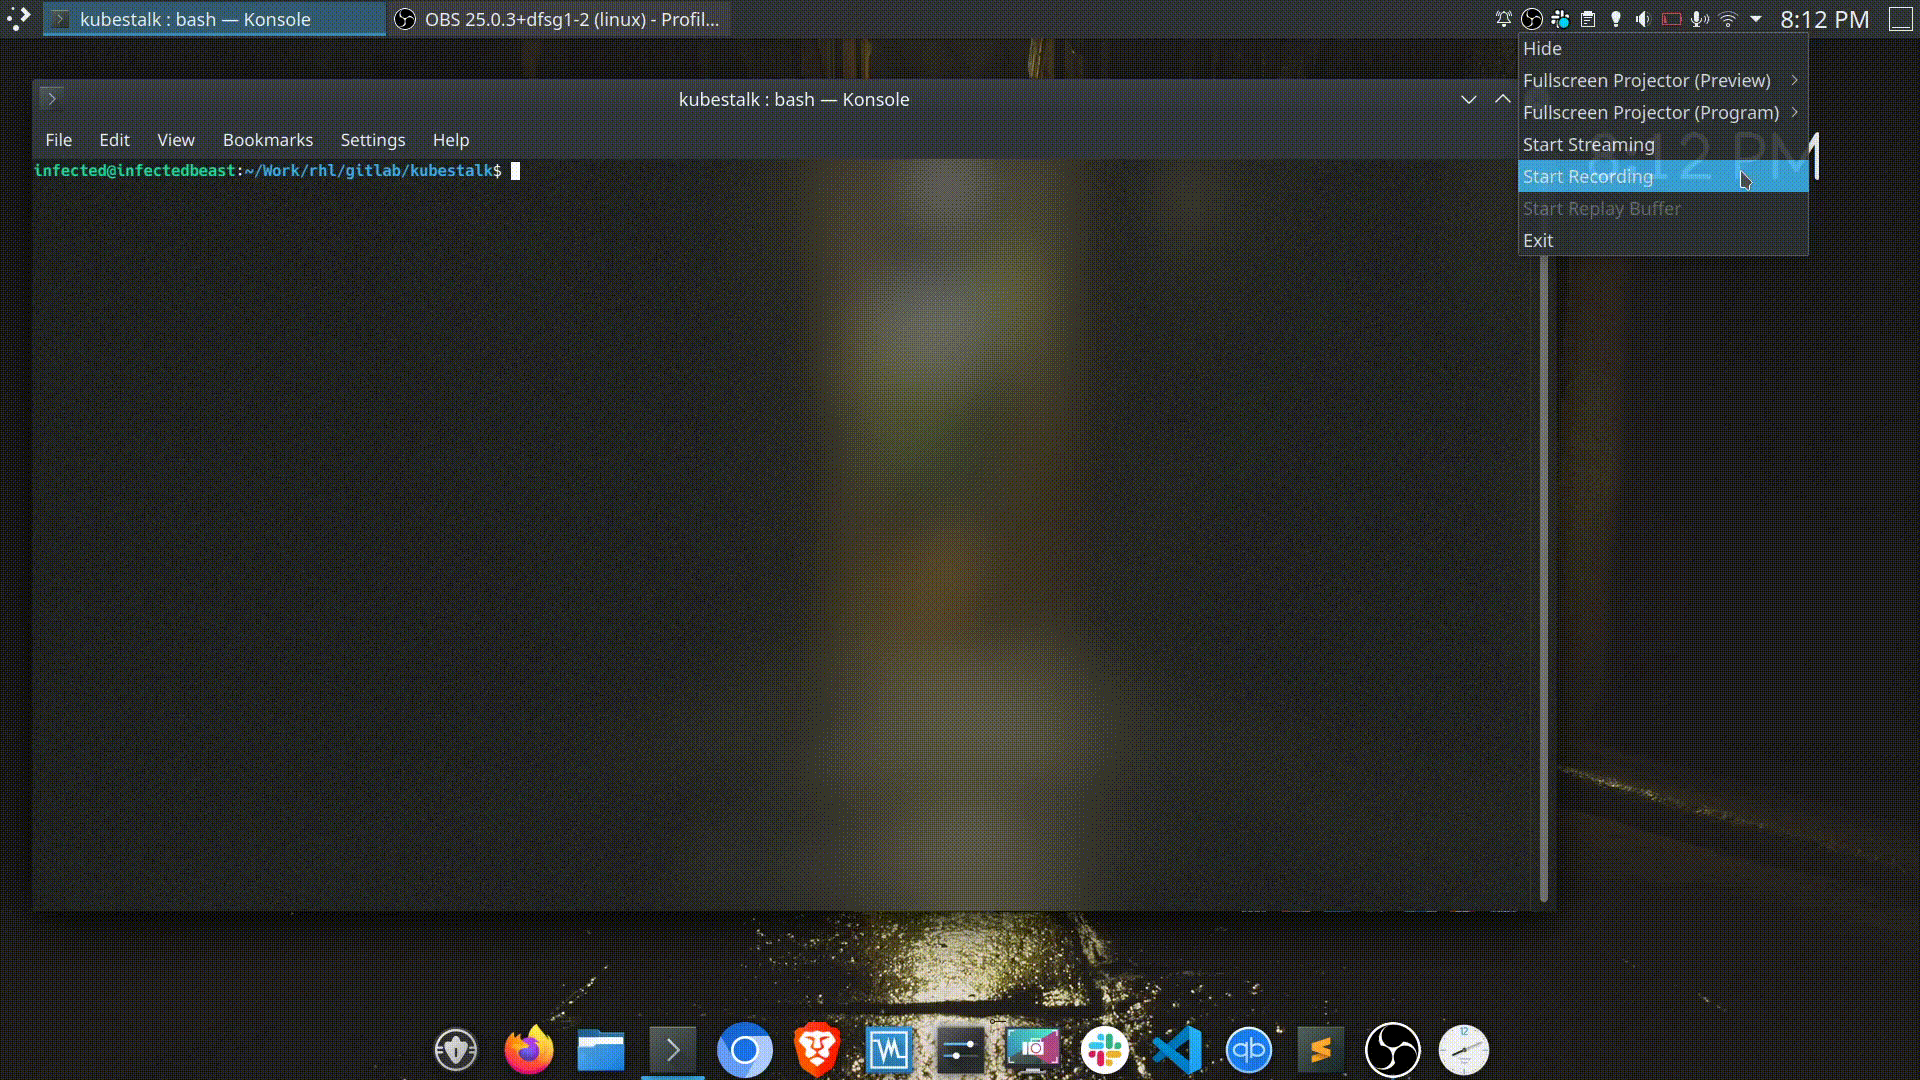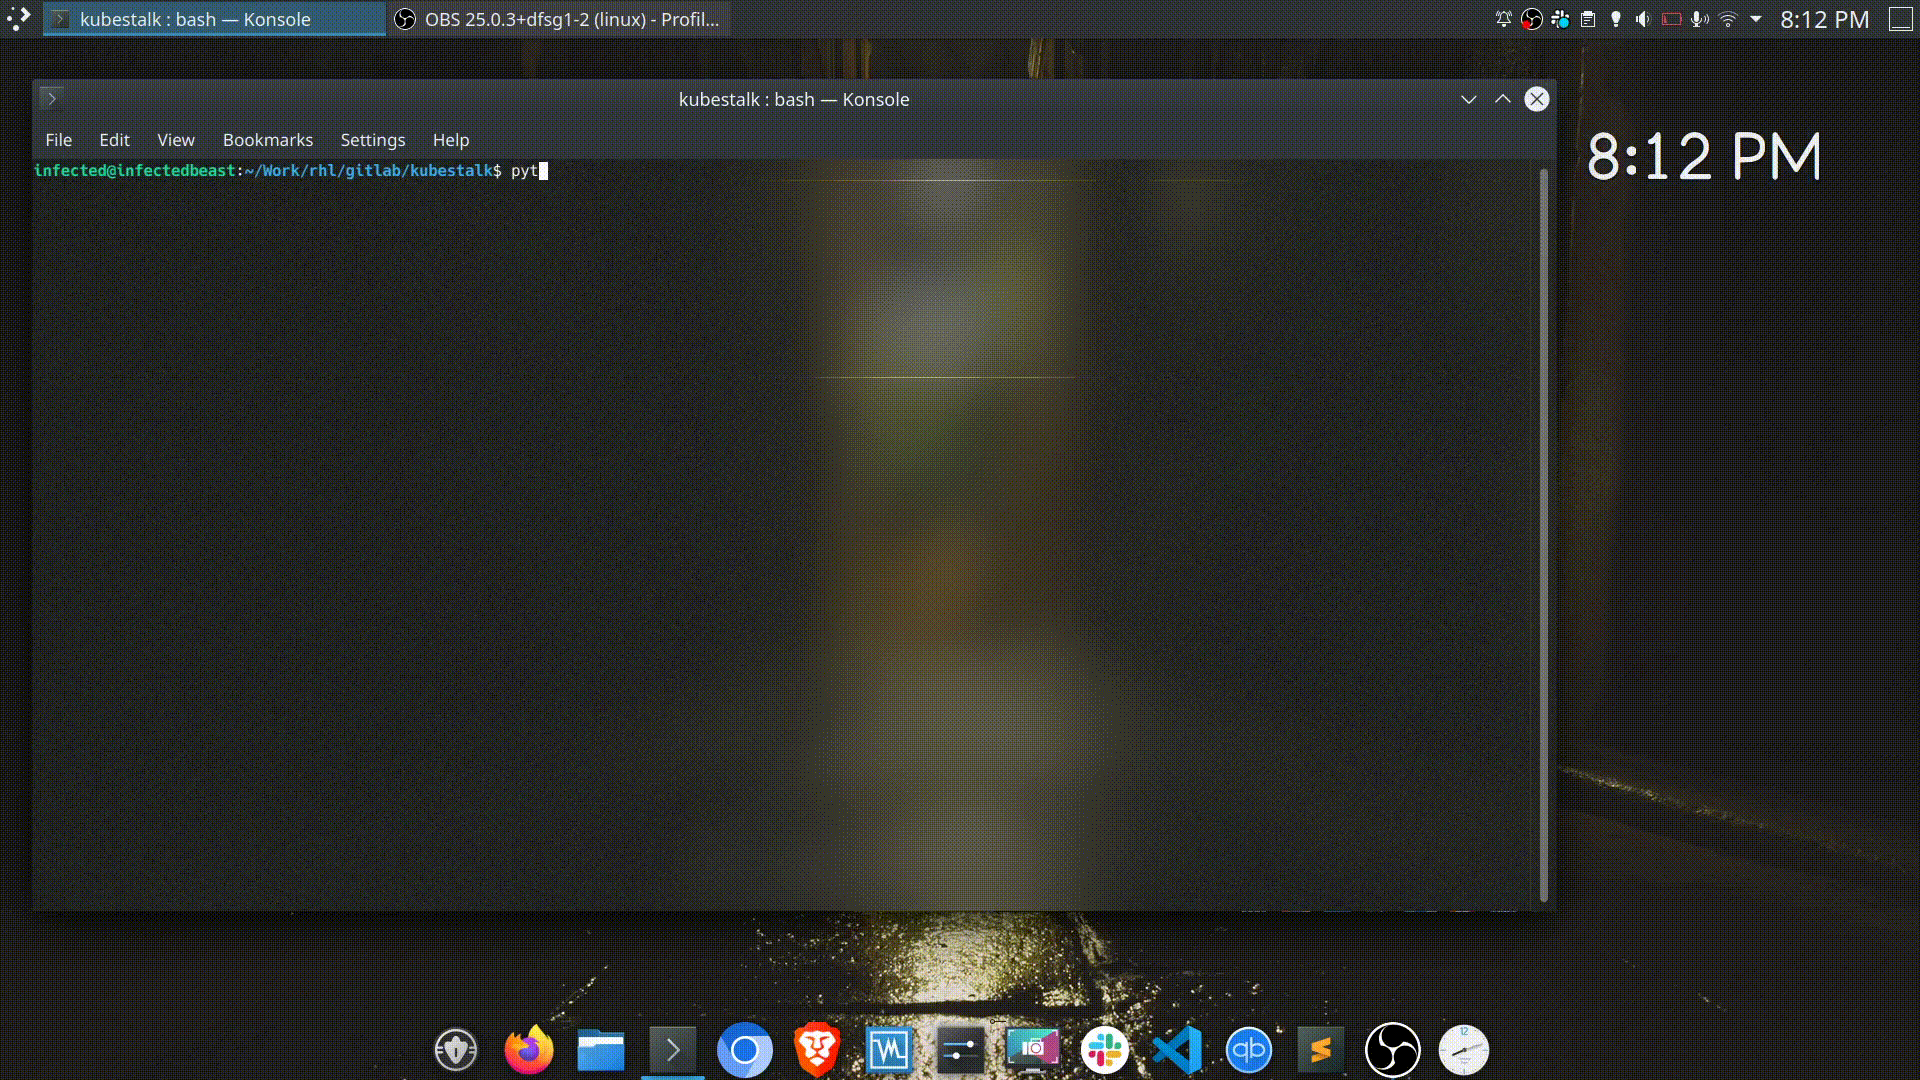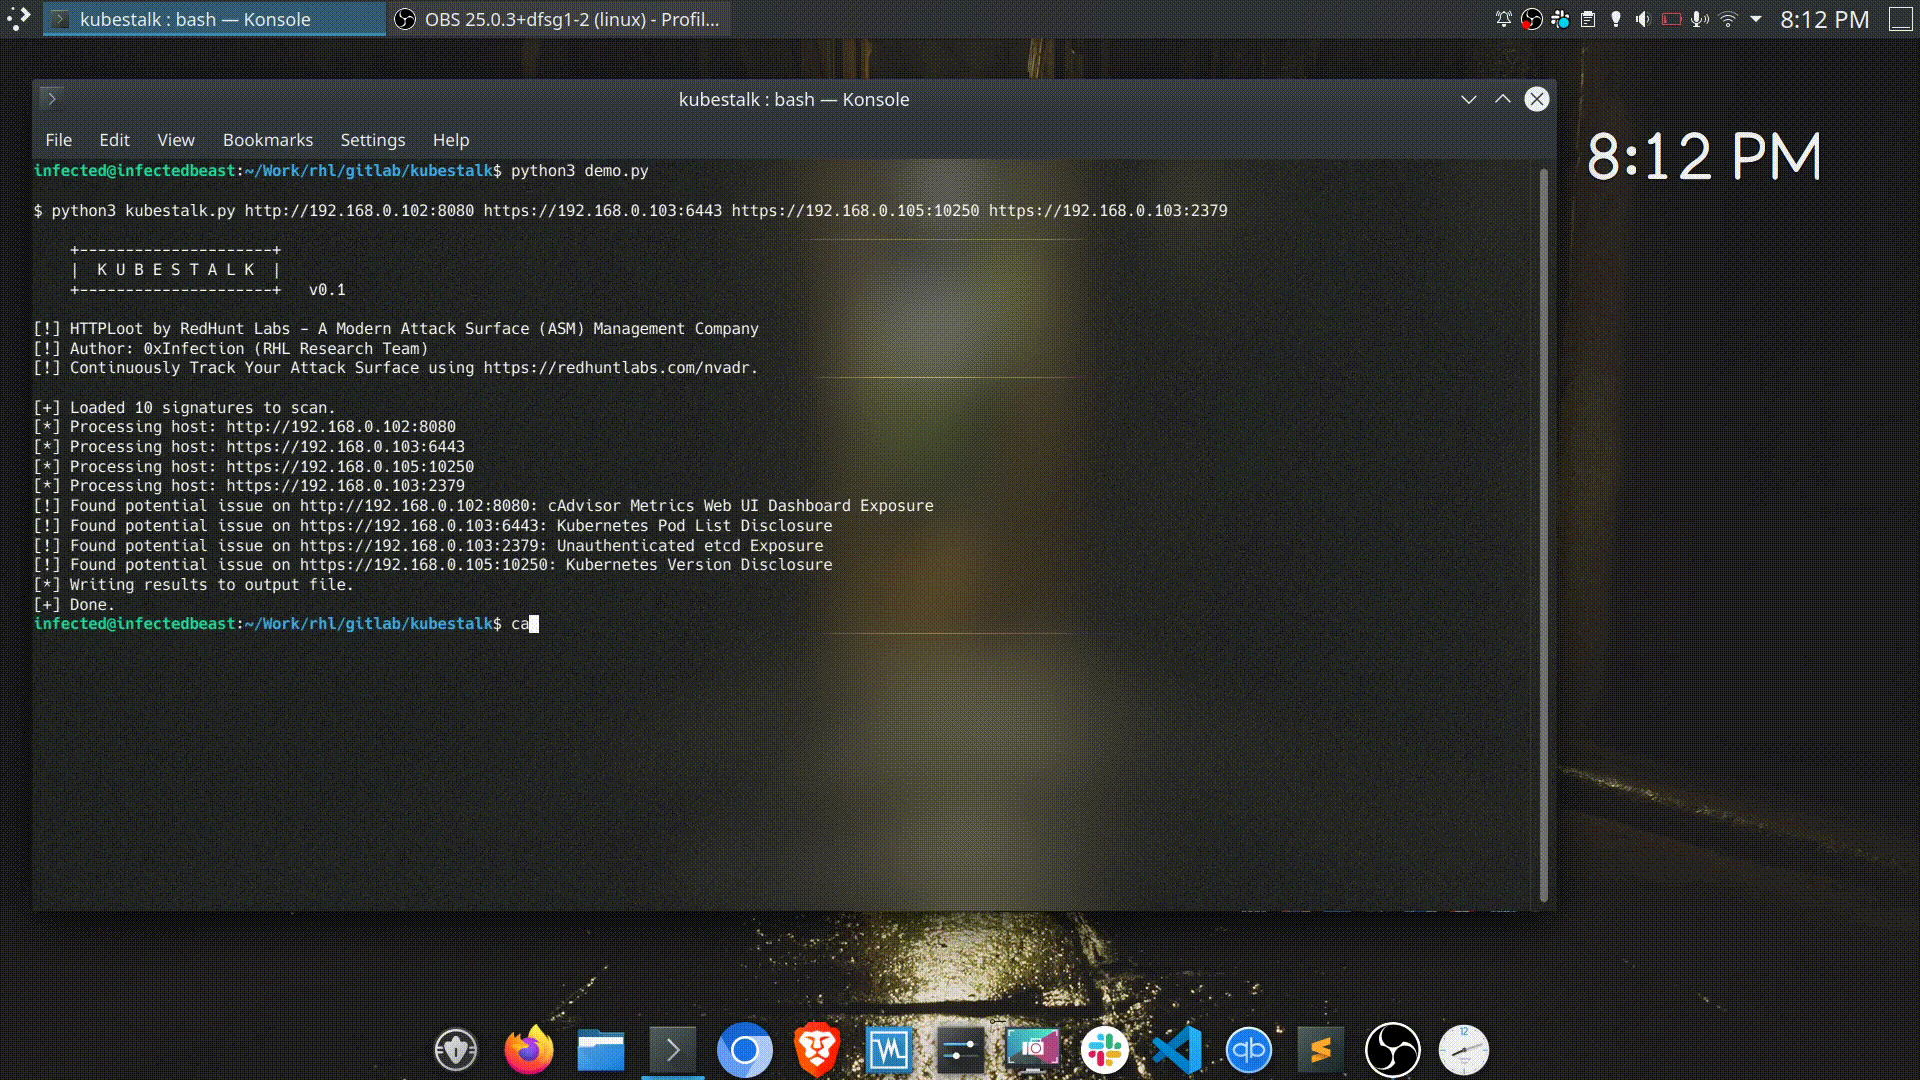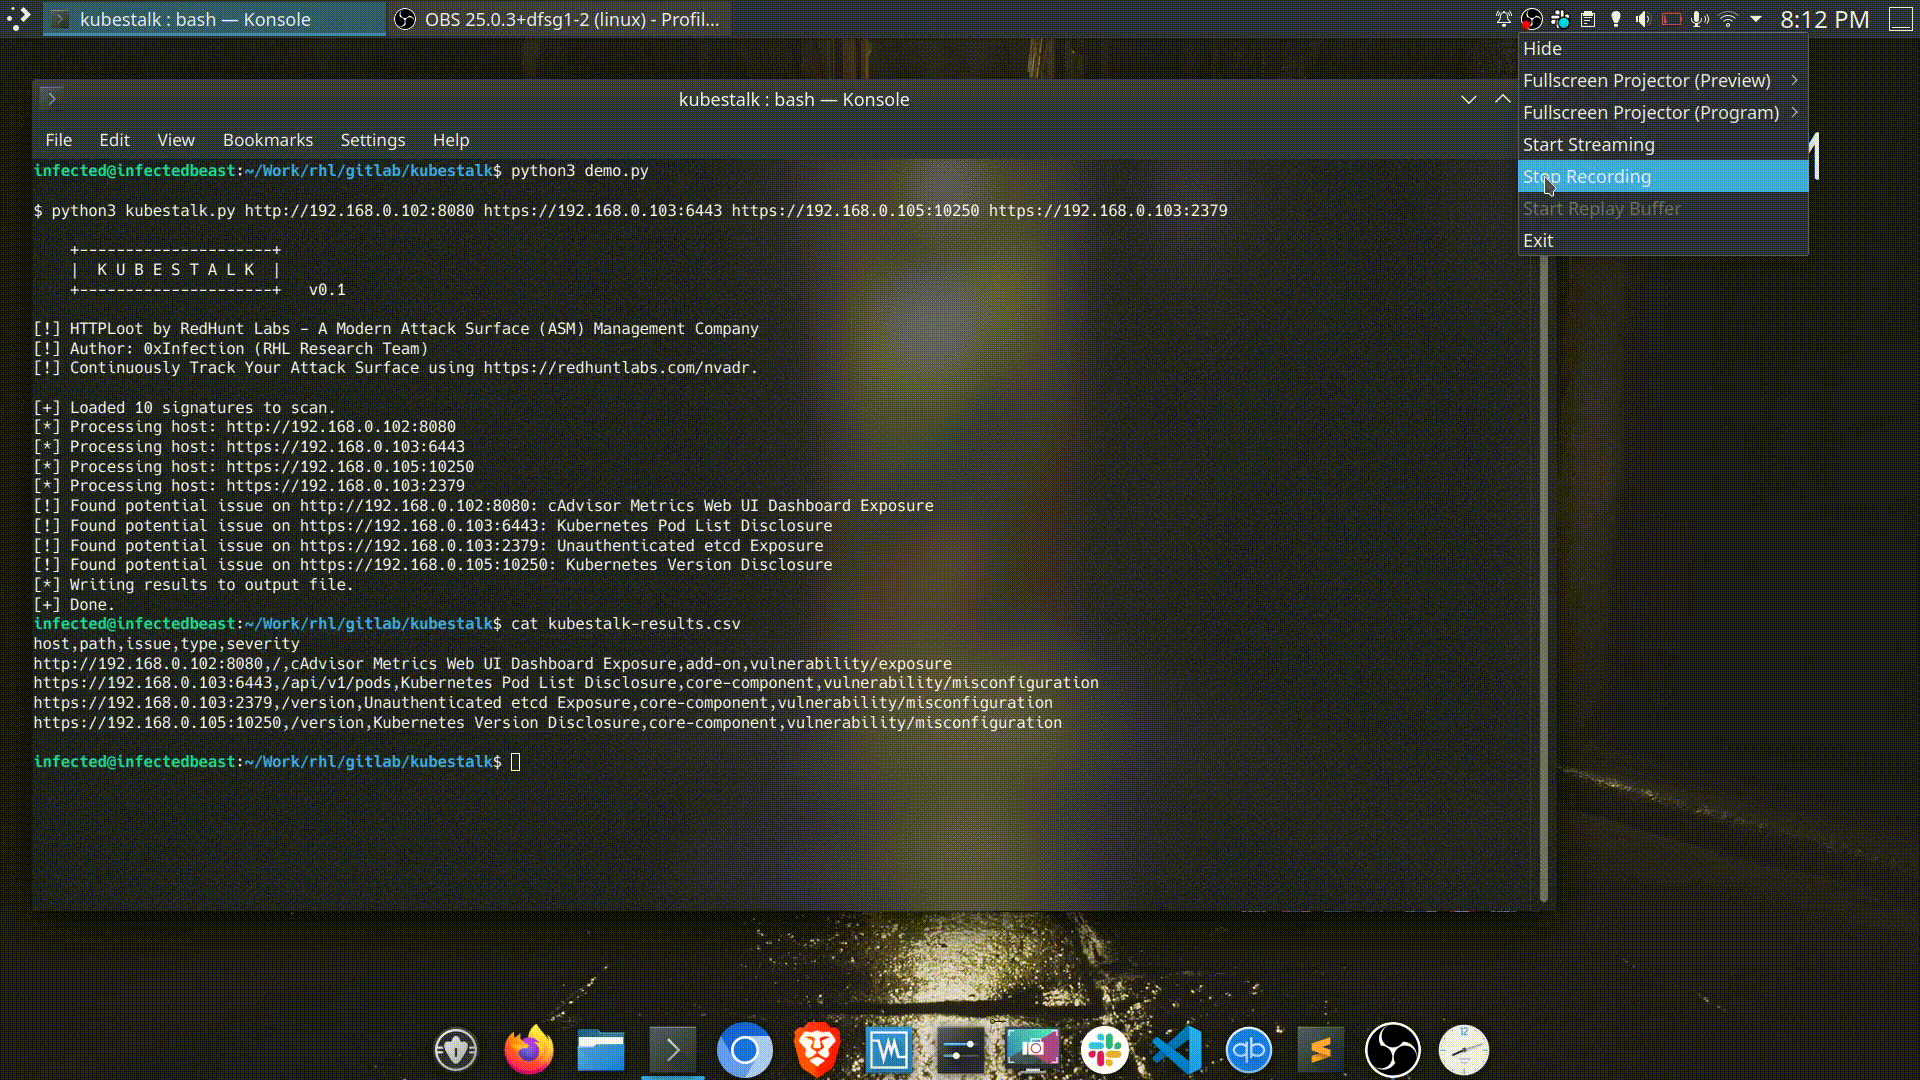 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 eeriedusk/nysm
eBPF-based stealth container that hides processes, sockets, eBPF objects, and audit logs from system monitoring tools, enabling covert…
 yonathanpy/cve-2025-32462-cve-2025-32463-poc-lab
Container-based lab with proof-of-concept exploits for two critical sudo vulnerabilities: host validation bypass (CVE-2025-32462) and NSS library…
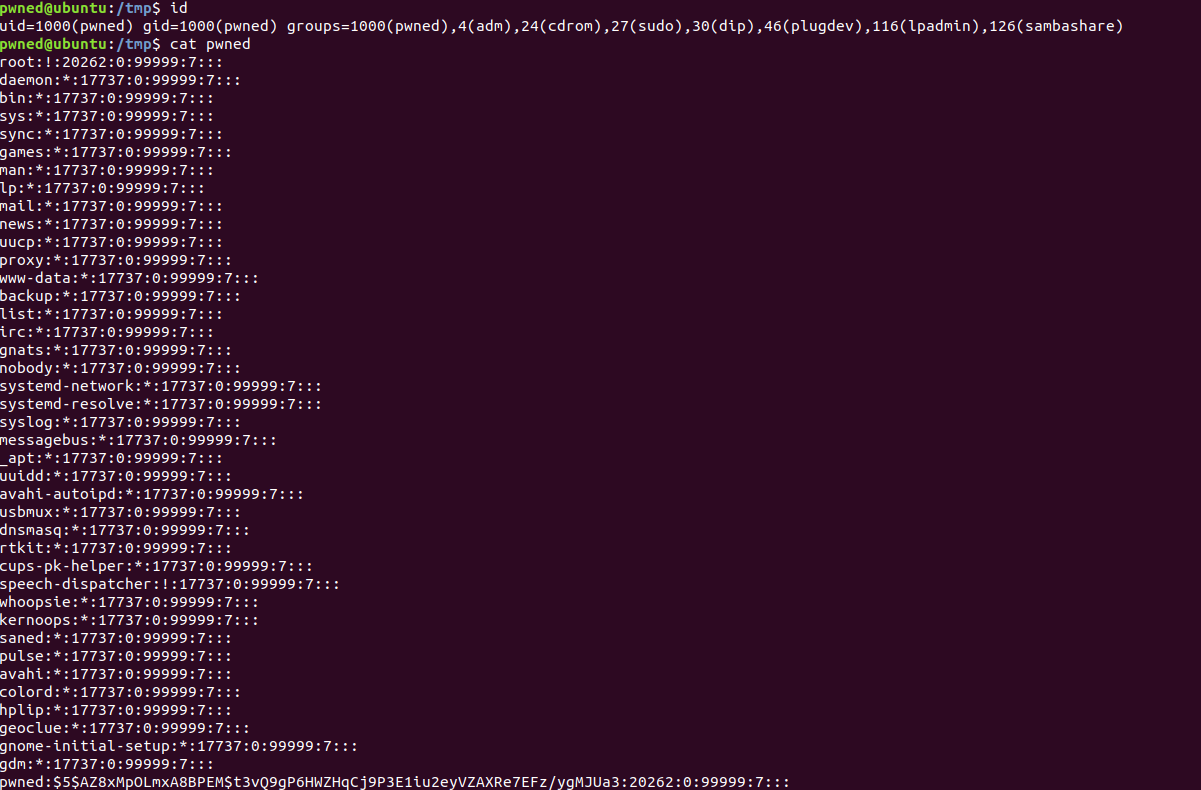 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 target/strelka
Real-time, container-based file scanning at enterprise scale
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 blasty/cve-2021-41773
CVE-2021-41773 playground
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 chen-keinan/kube-beacon
Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
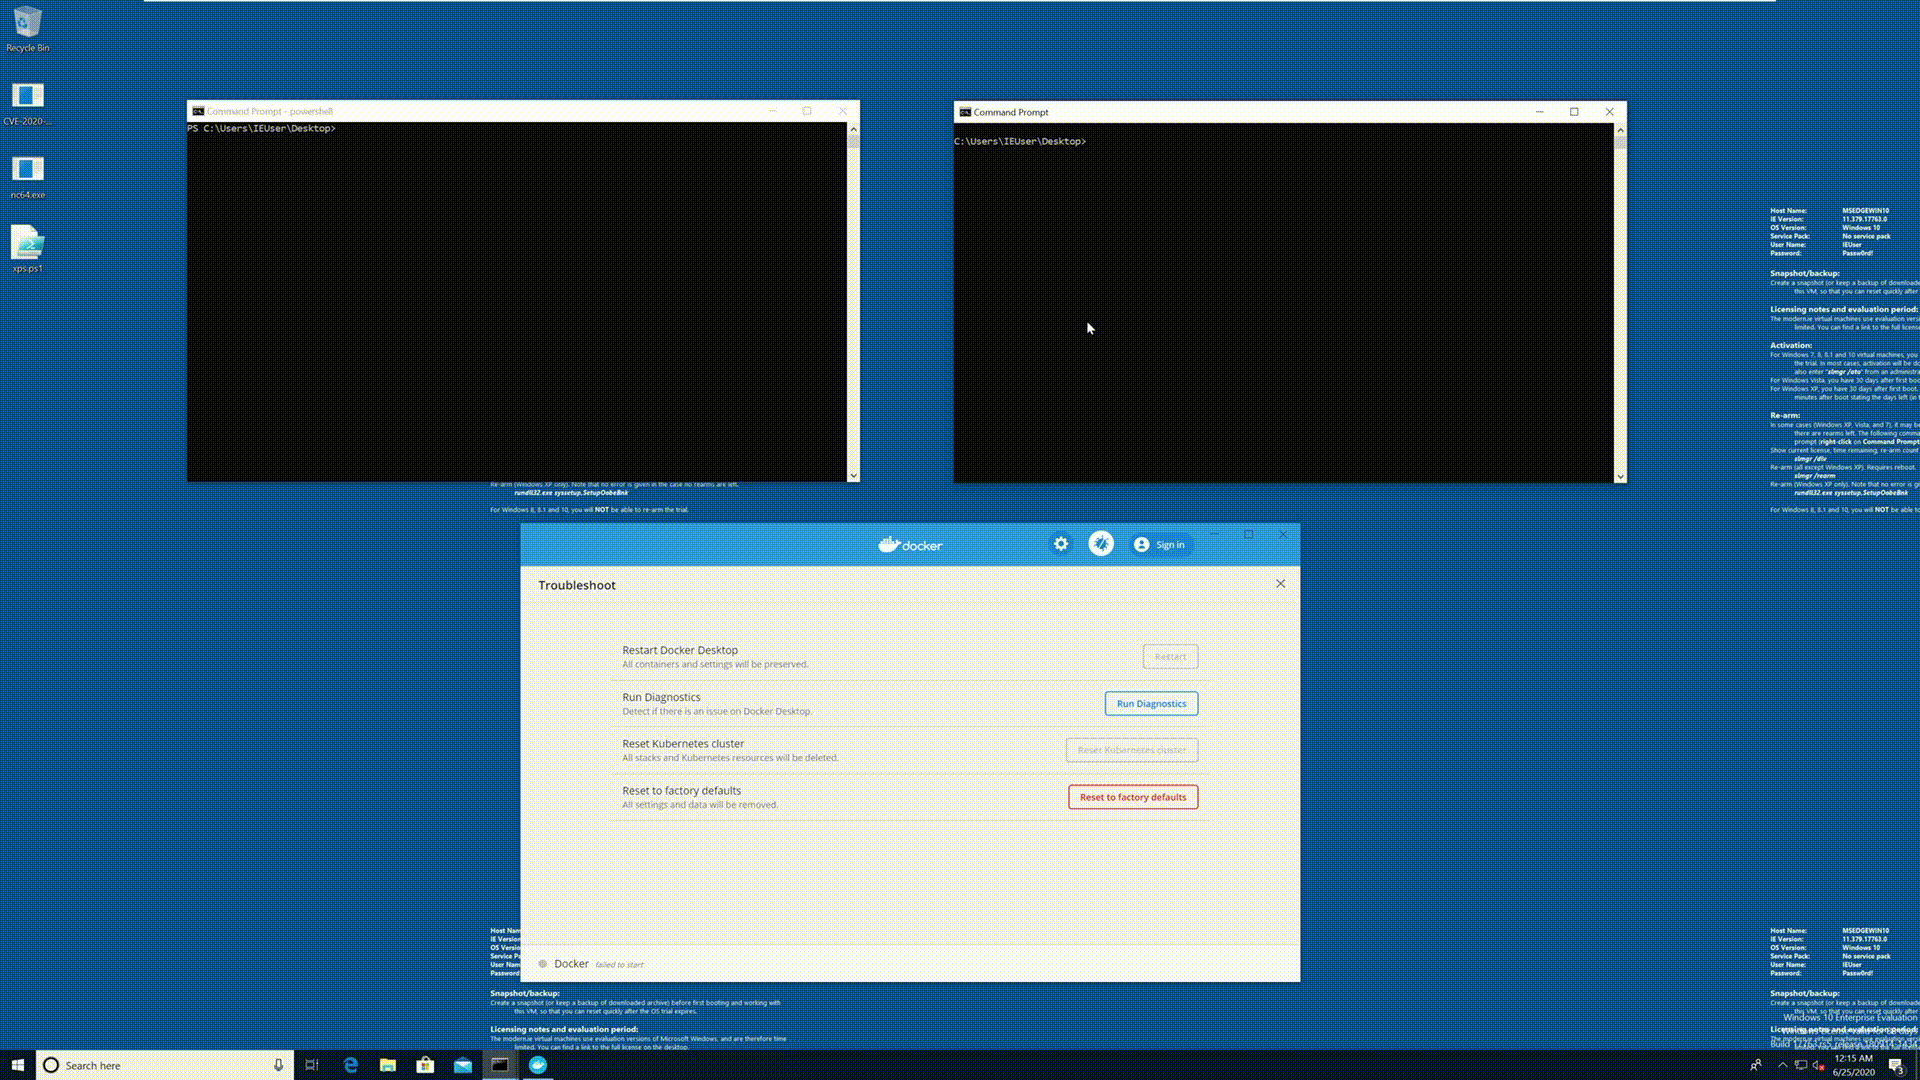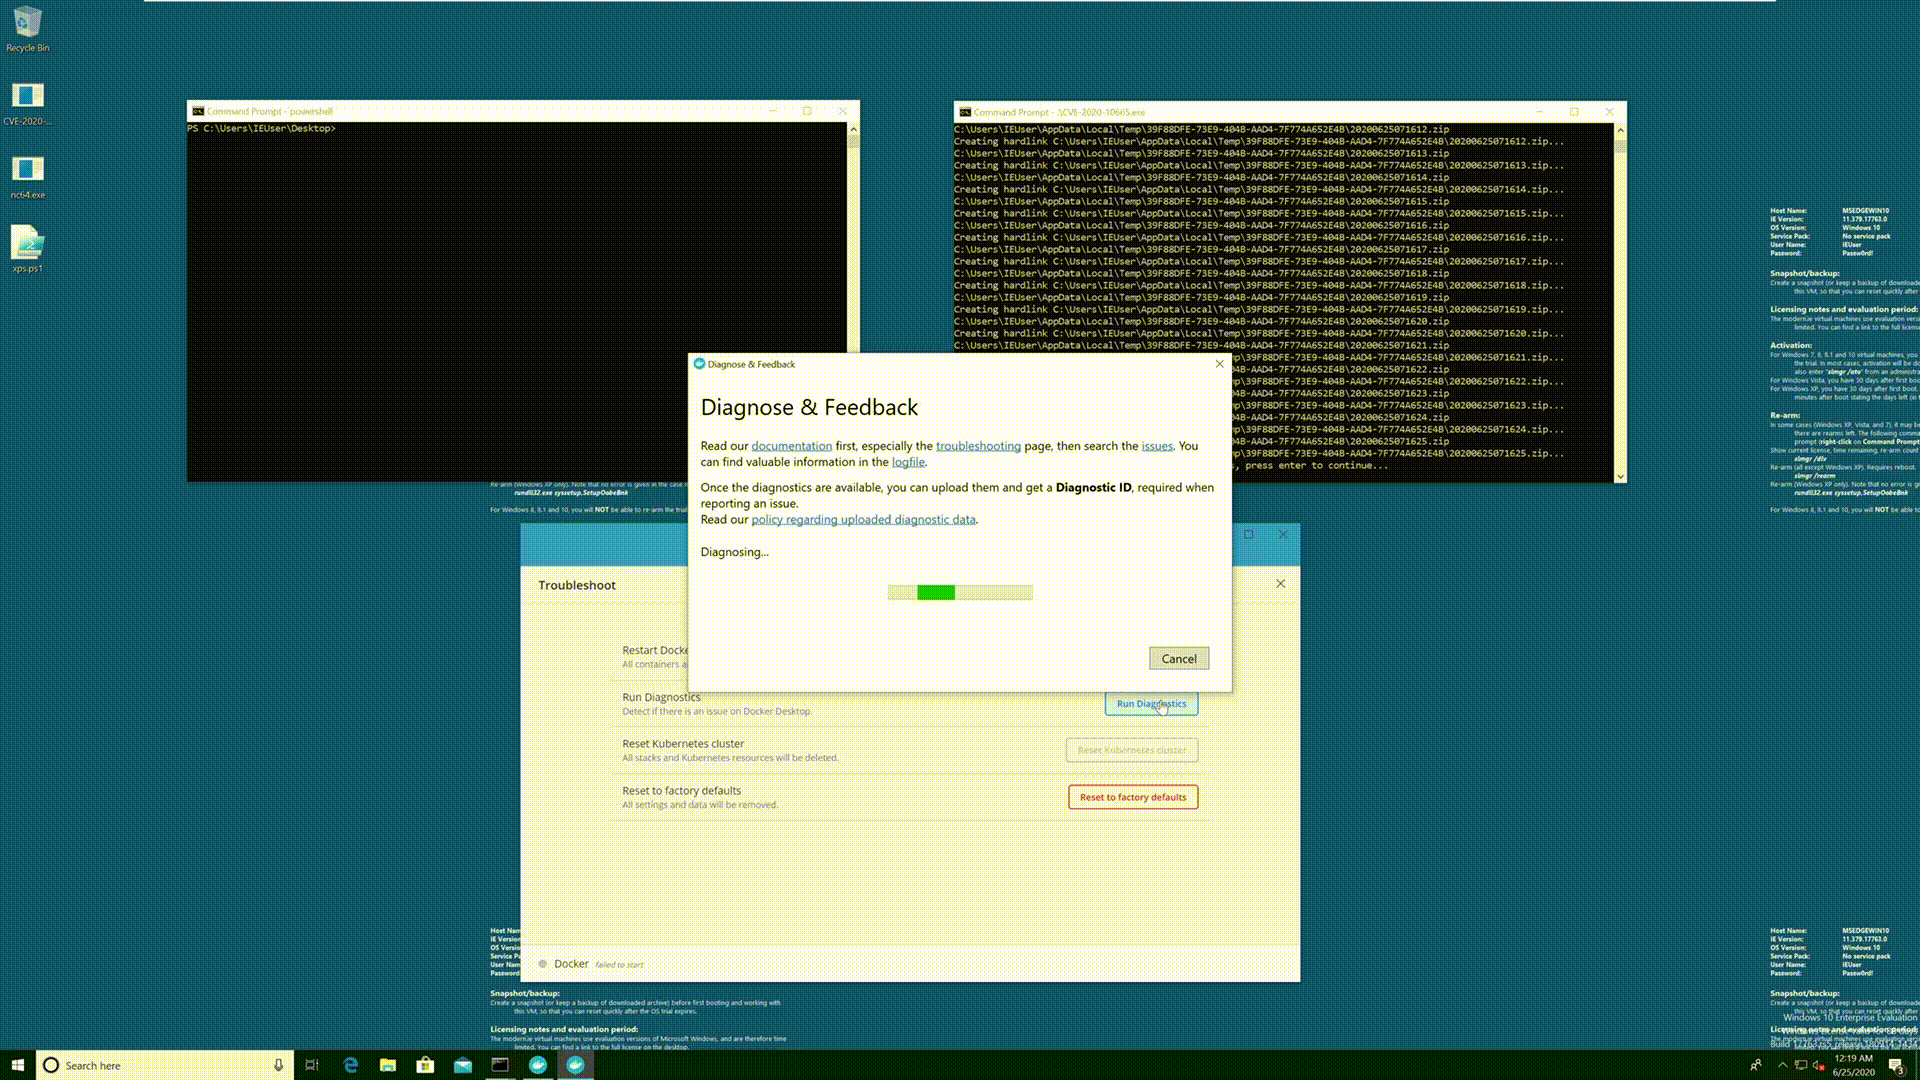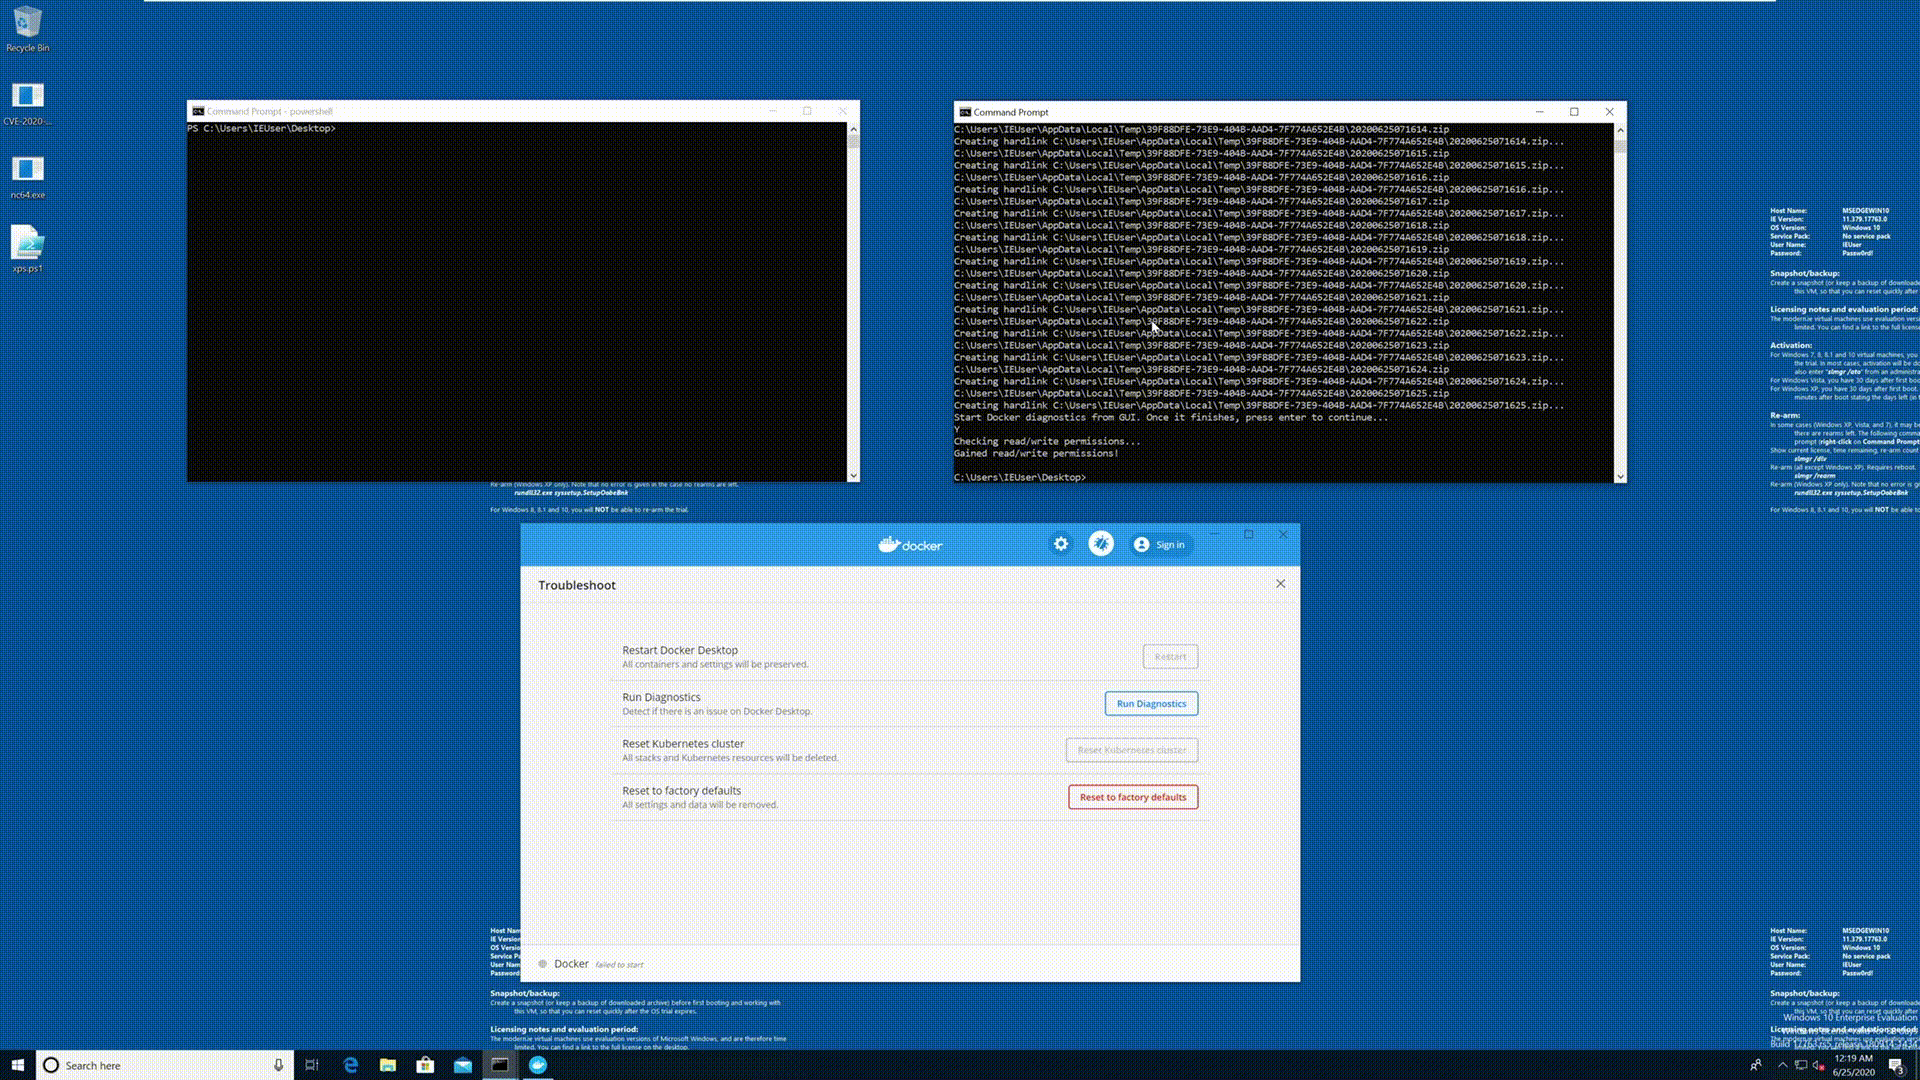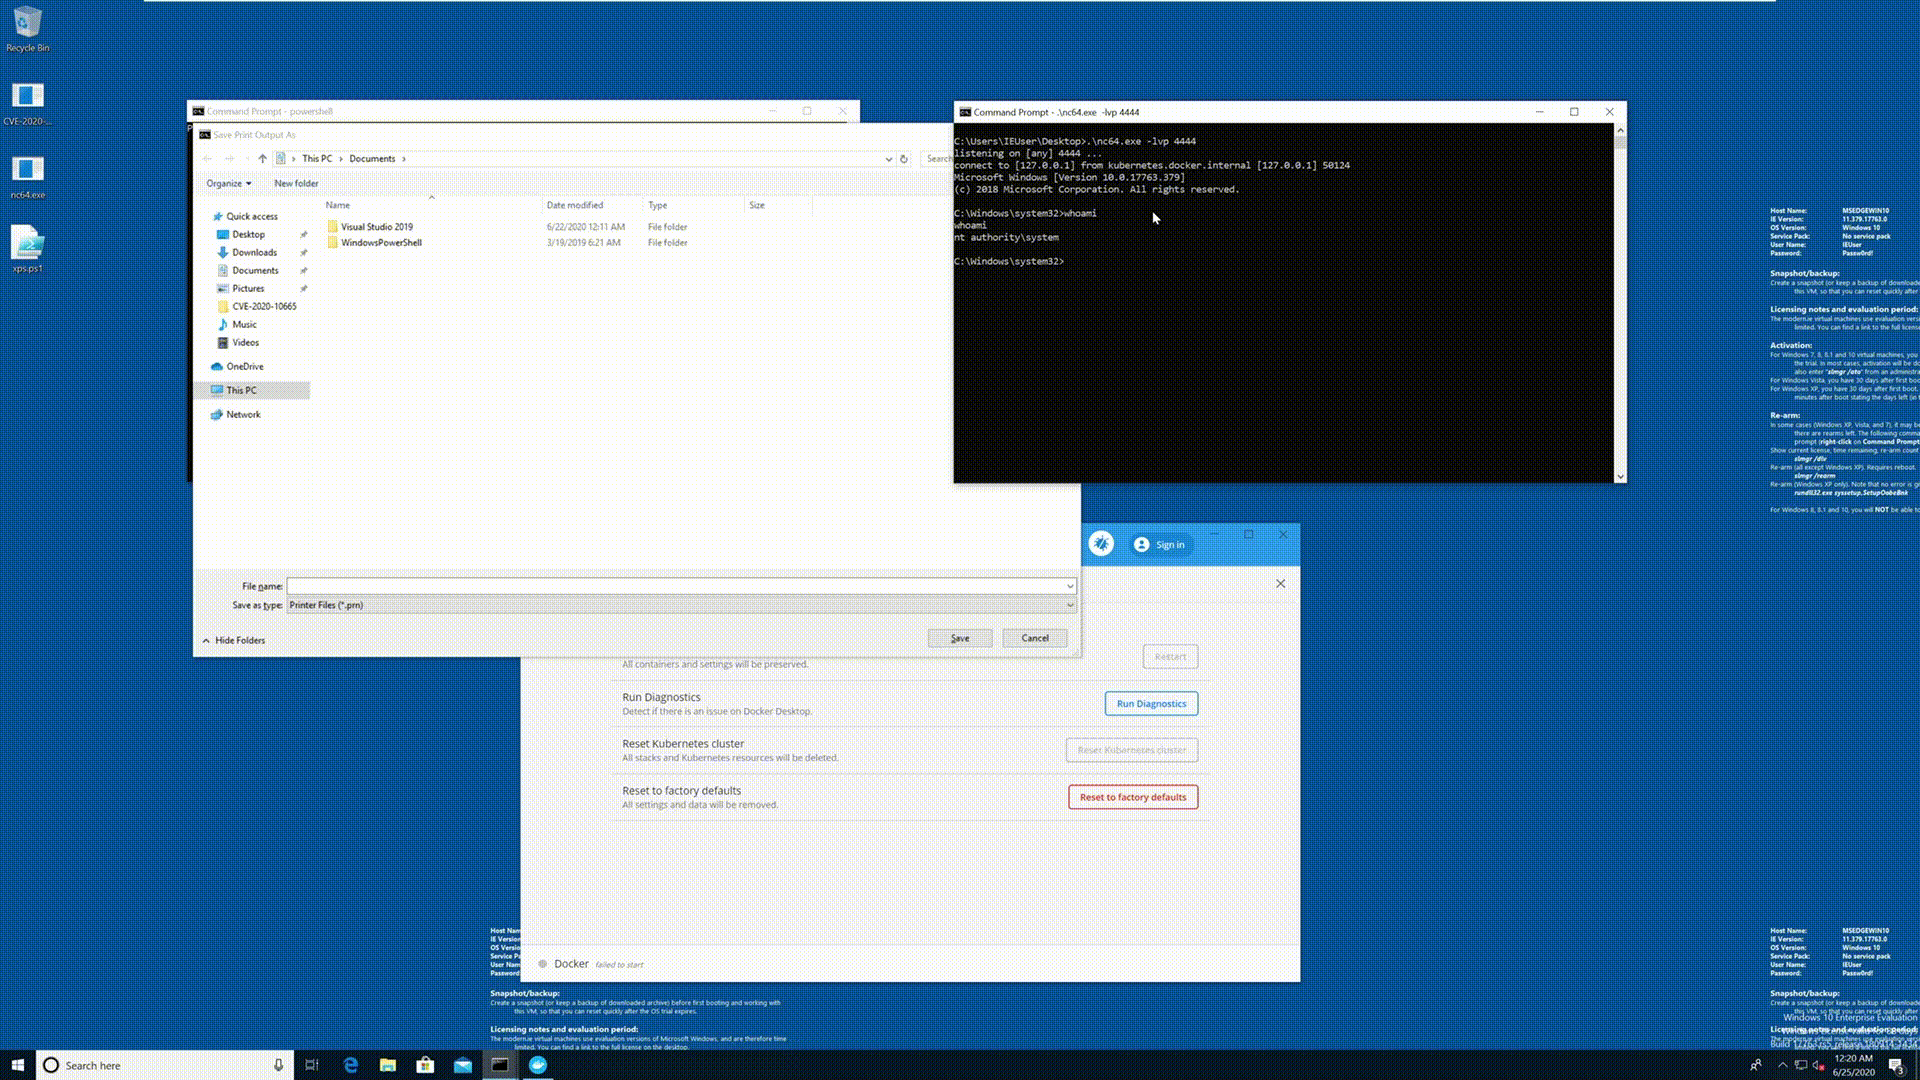 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation