
titus
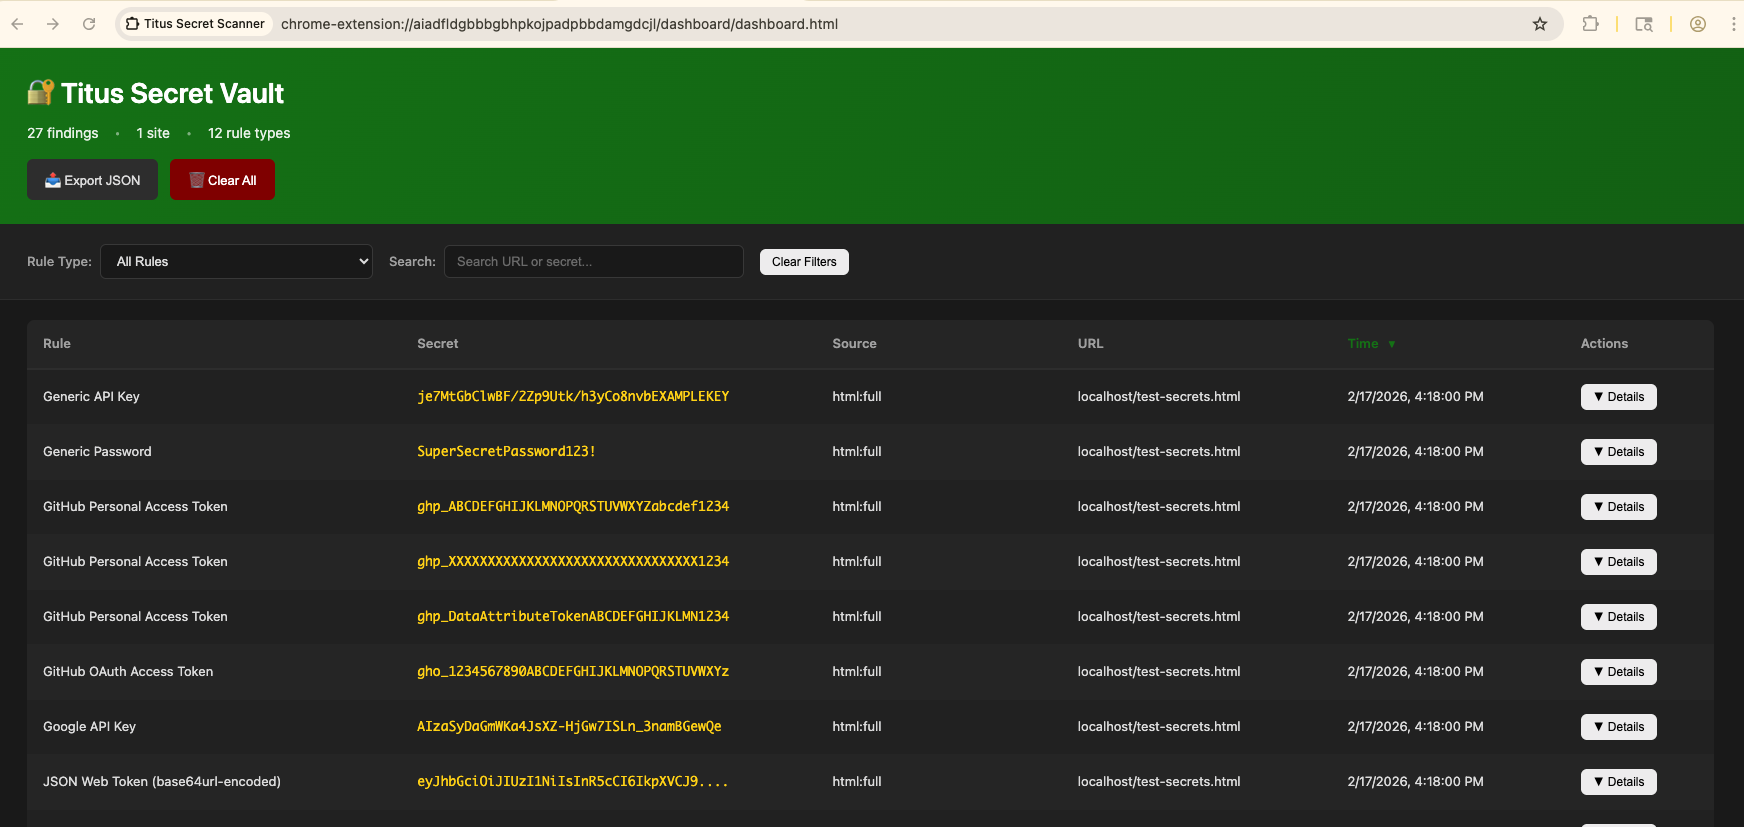
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
code-analysiscontainer-securitydevsecops+6
705
praetorian-inc/titusHigh-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 greenhandatsjtu/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 george0papasotiriou/cve-2026-5555-container-escape-via-proc-self-fd-symlink-in-shared-volume
Proof-of-concept exploit for CVE-2026-5555, demonstrating container escape via /proc/self/fd symlink in rshared volumes to overwrite host files and…
 visdev23/vulnerable-docker--cve-2023-30212-
This contains the necessary files and Docker to replicate A vulnerability in OURPHP that has a XSS Vulnerability (CVE-2023-30212)
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.