
Archived
purpleteam-s2-containers
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
cloud-securitycontainer-securitydevsecops+5
purpleteam-labs/purpleteam-s2-containersStage two containers
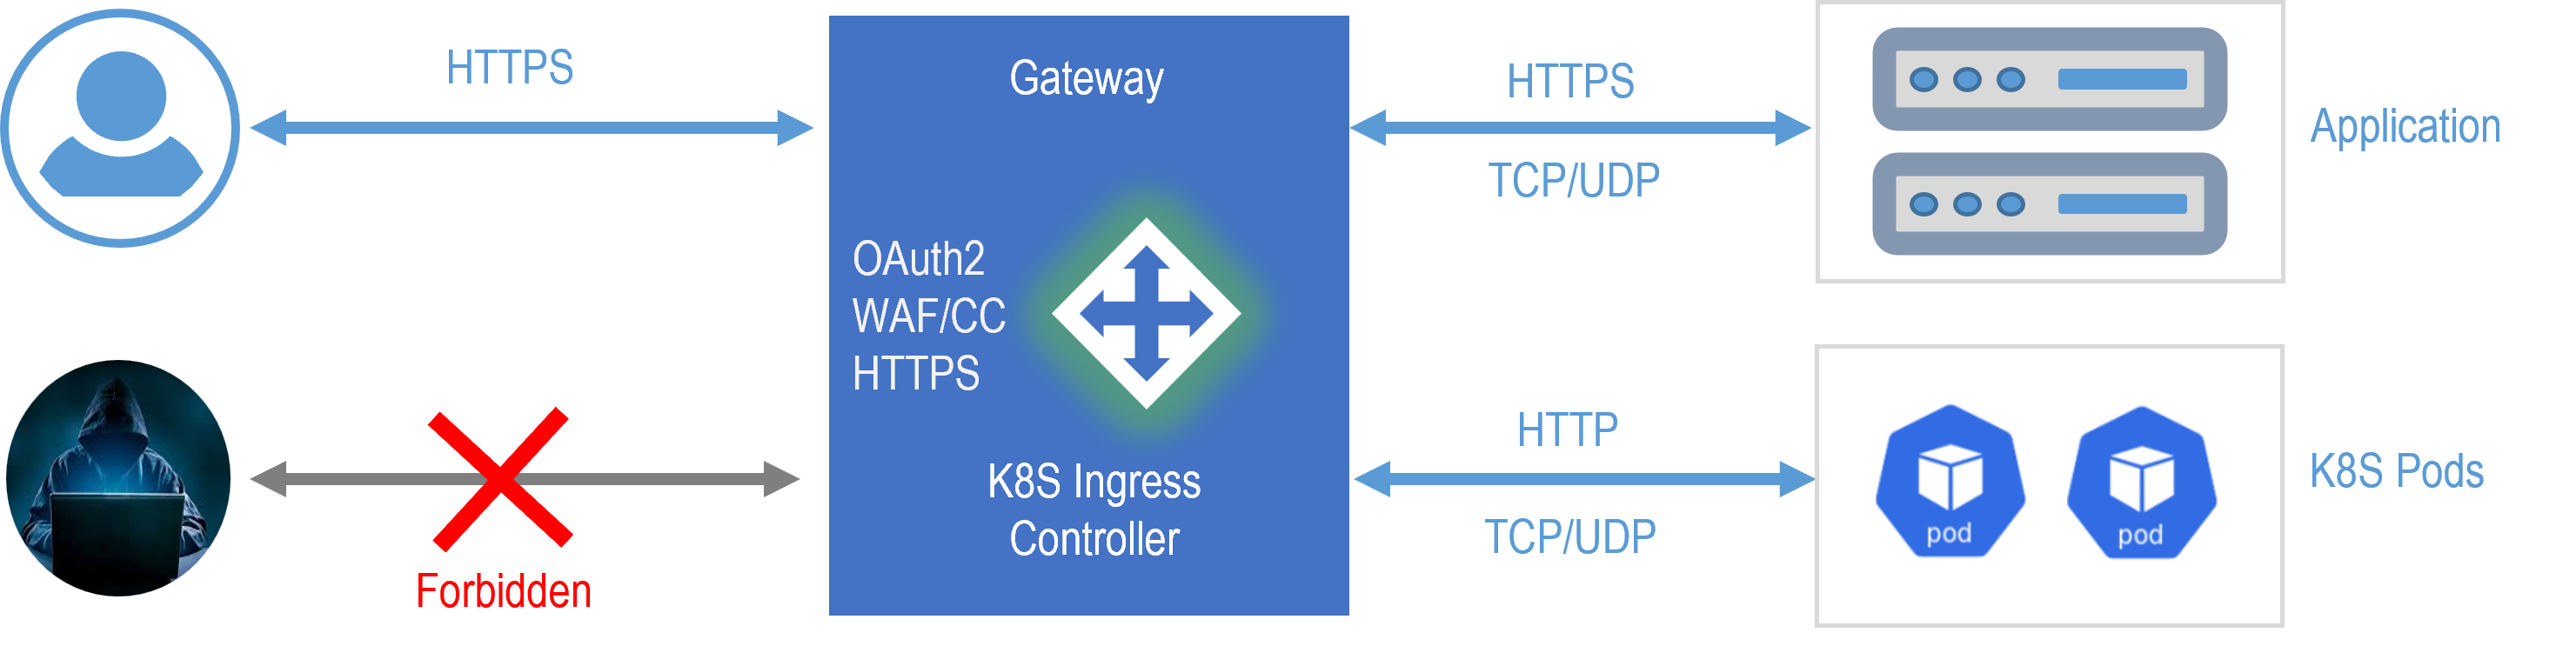
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 limxuan/ehir-vuln-enterprise-login
Deliberately vulnerable web application portal with a containerized backend, designed for practicing exploitation of CVE-2021-44228 and container…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 nu11secur1ty/cve-2021-44228-vuln-app
Dockerized vulnerable web application demonstrating the Log4j CVE-2021-44228 remote code execution vulnerability for educational exploitation and…
 rhbb/cve-2019-13956
Dockerized proof-of-concept exploit for CVE-2019-13956, targeting a web application vulnerability accessible via HTTP on port 8090.
 rosehgal/dockerent
The only open-source tool to analyze vulnerabilities and configuration issues with running docker container(s) and docker networks.
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 optiopay/klar
Integration of Clair and Docker Registry
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 aquasecurity/starboard
Superseded by https://github.com/aquasecurity/trivy-operator
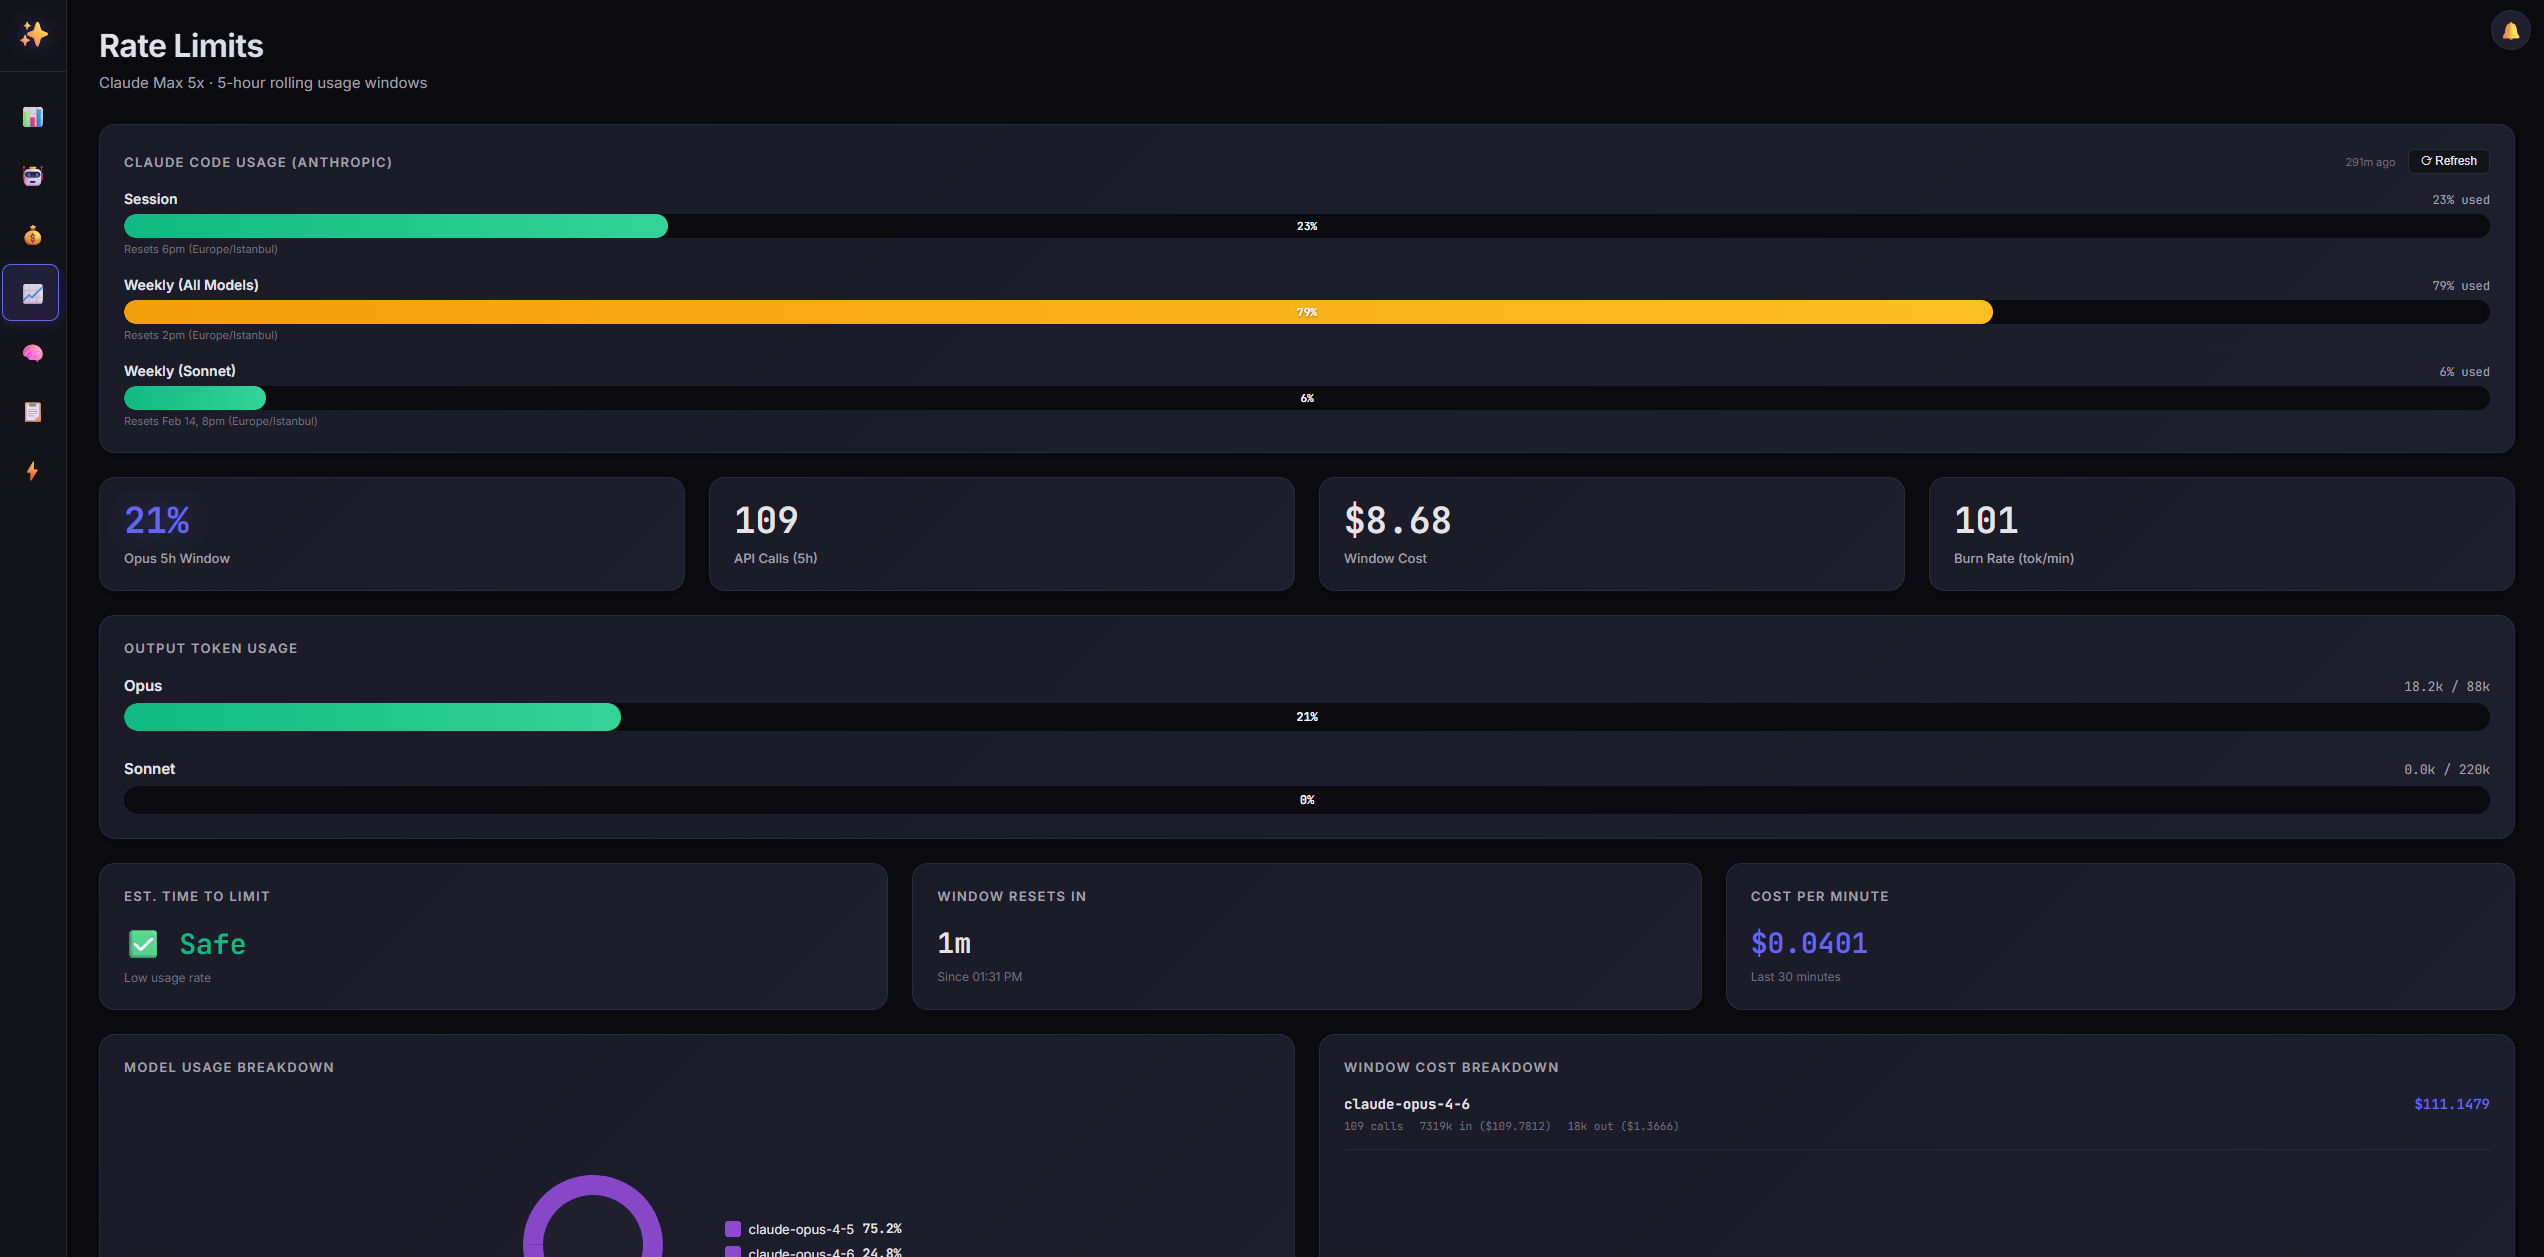 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.