
POC-2020-8558
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
cloud-securitycontainer-securityexploitation+5
43
tabbysable/poc-2020-8558Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
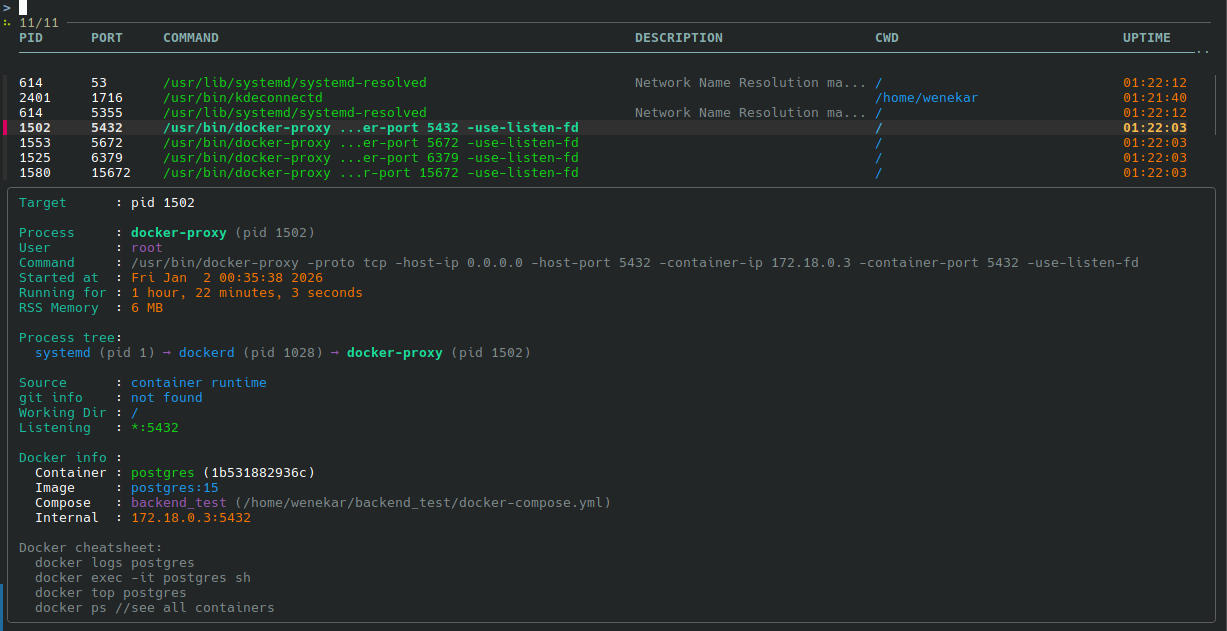 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 maherazzouzi/cve-2022-47952
LXC Information Disclosure vulnerability.
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 astefanutti/kubebox
⎈❏ Terminal and Web console for Kubernetes
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 purpleteam-labs/purpleteam-s2-containers
Stage two containers