
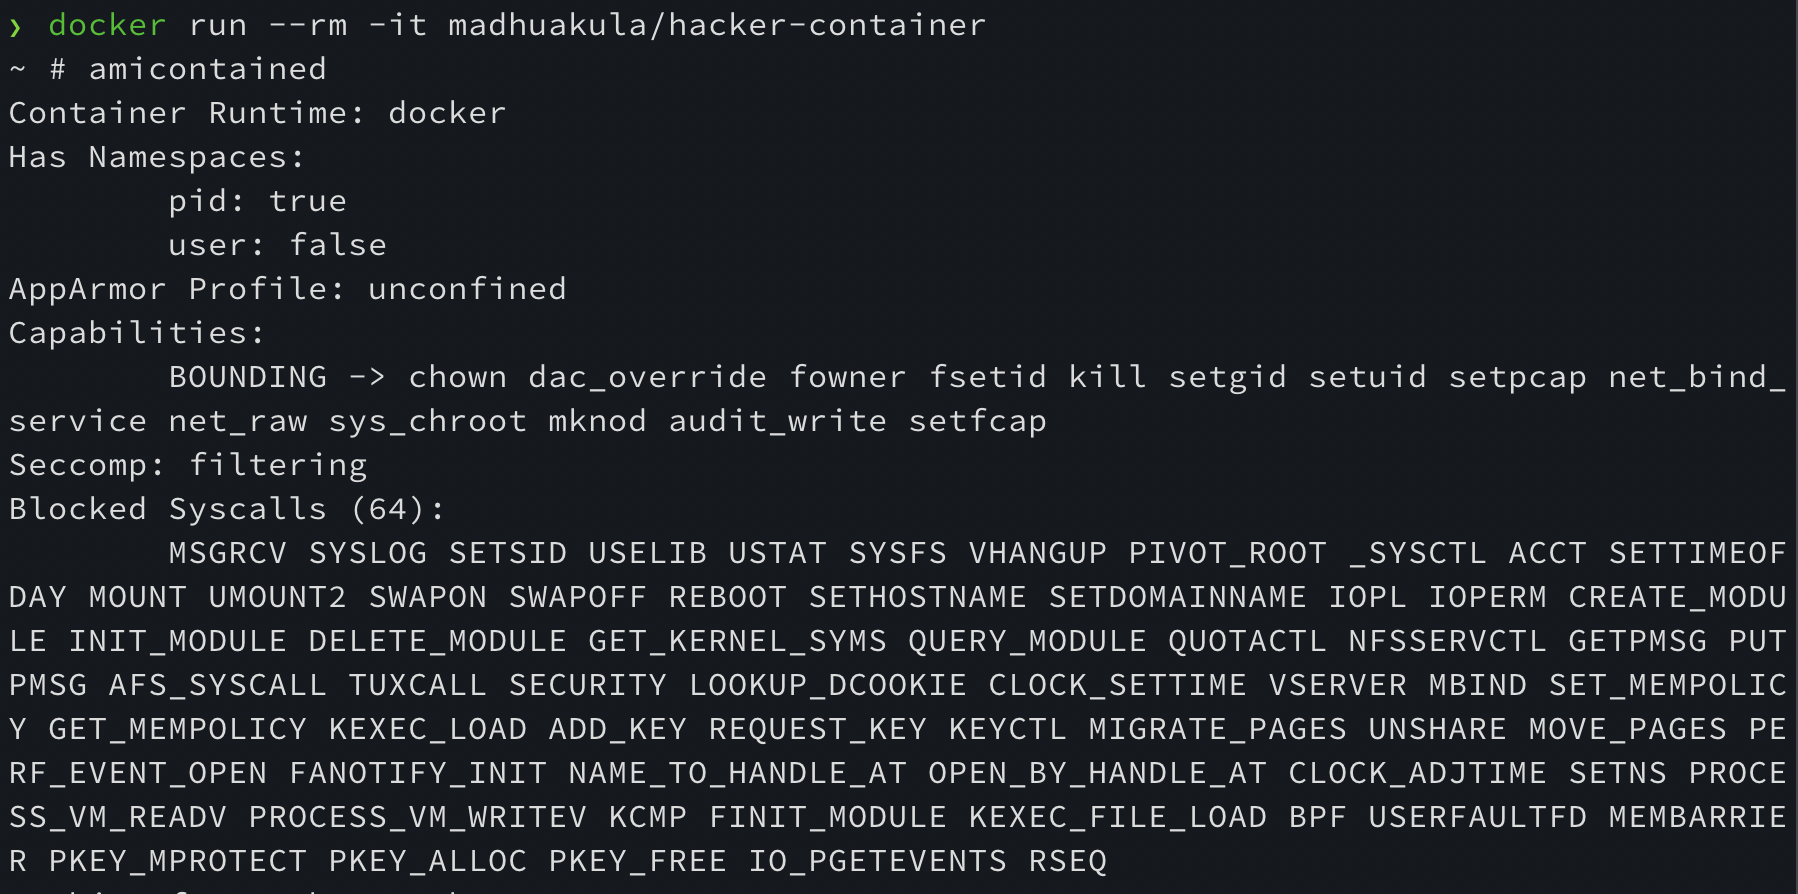
hacker-container
 madhuakula/hacker-container
The Swiss Army Container for Cloud Native Security. Container with all the list of useful tools/commands while hacking and securing Containers,…
cloud-securitycontainer-securitypenetration-testing+1
295
madhuakula/hacker-containerThe Swiss Army Container for Cloud Native Security. Container with all the list of useful tools/commands while hacking and securing Containers,…
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.
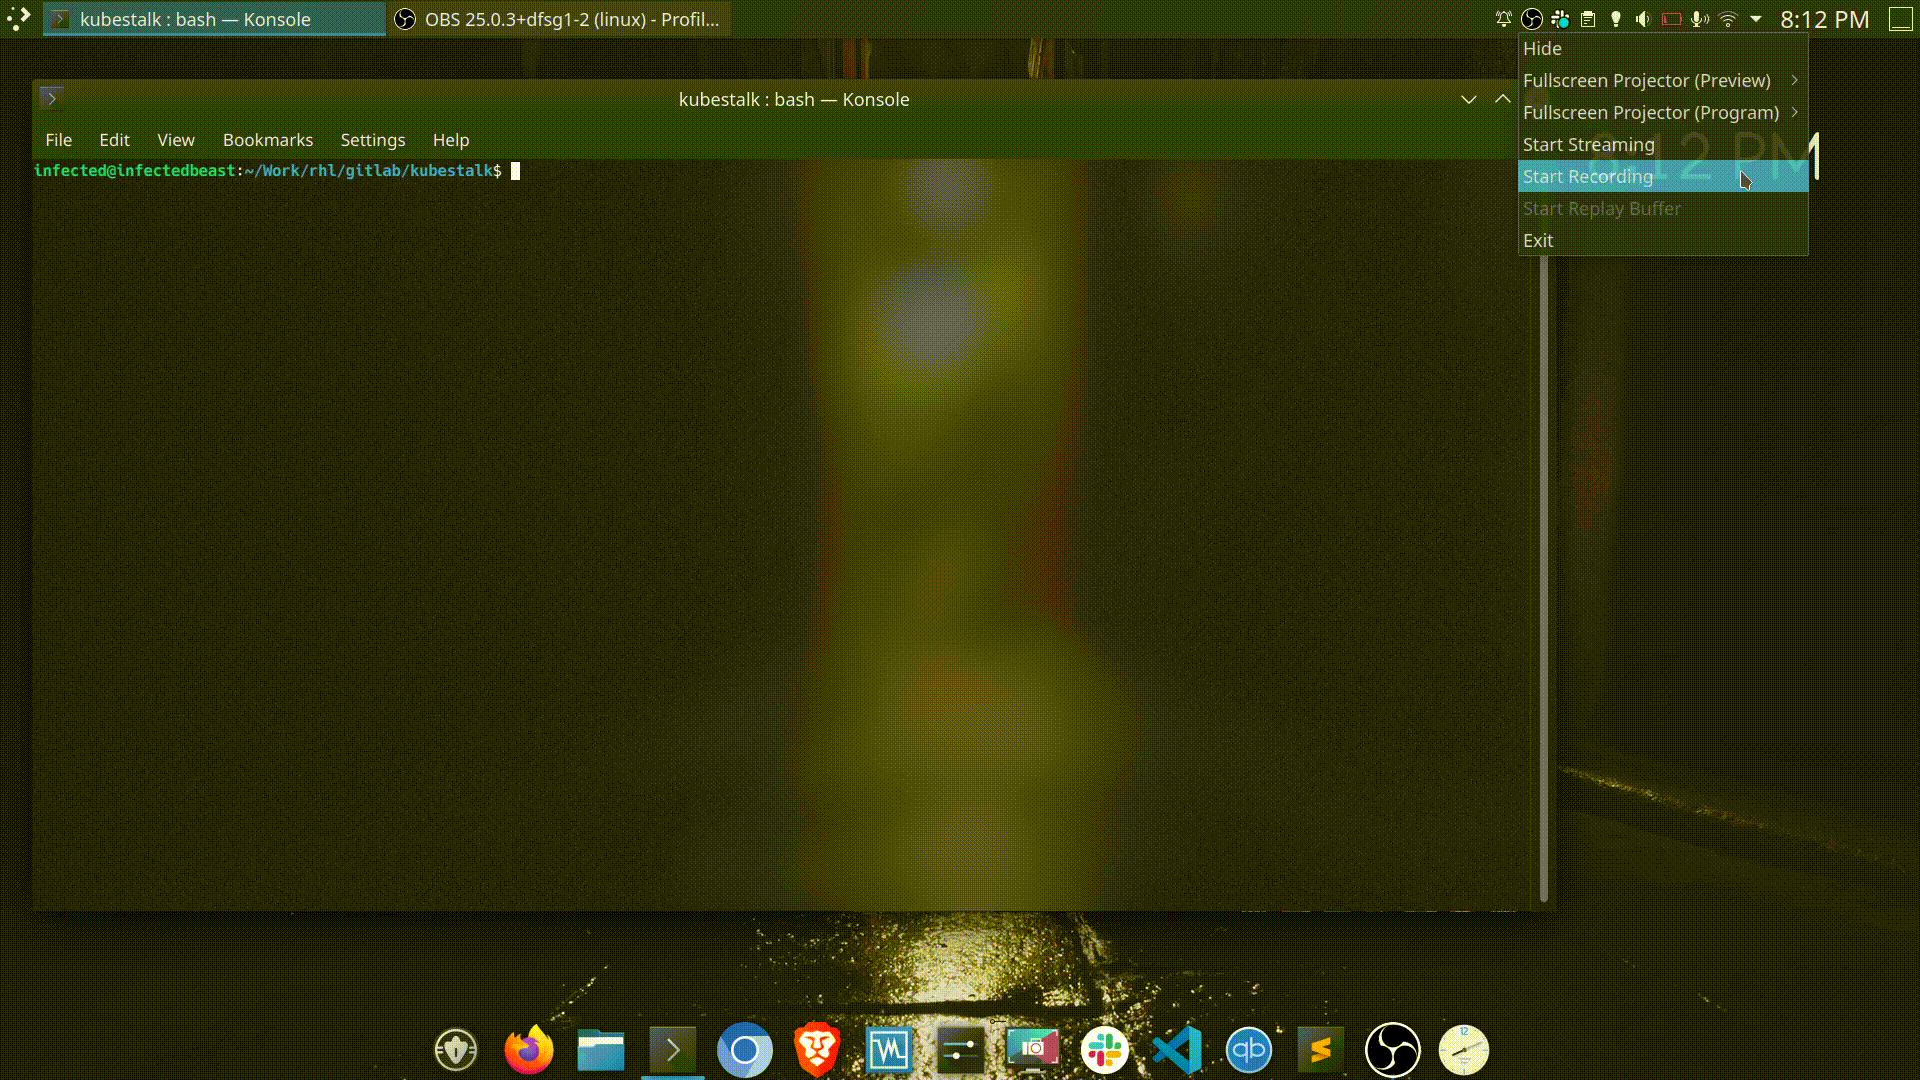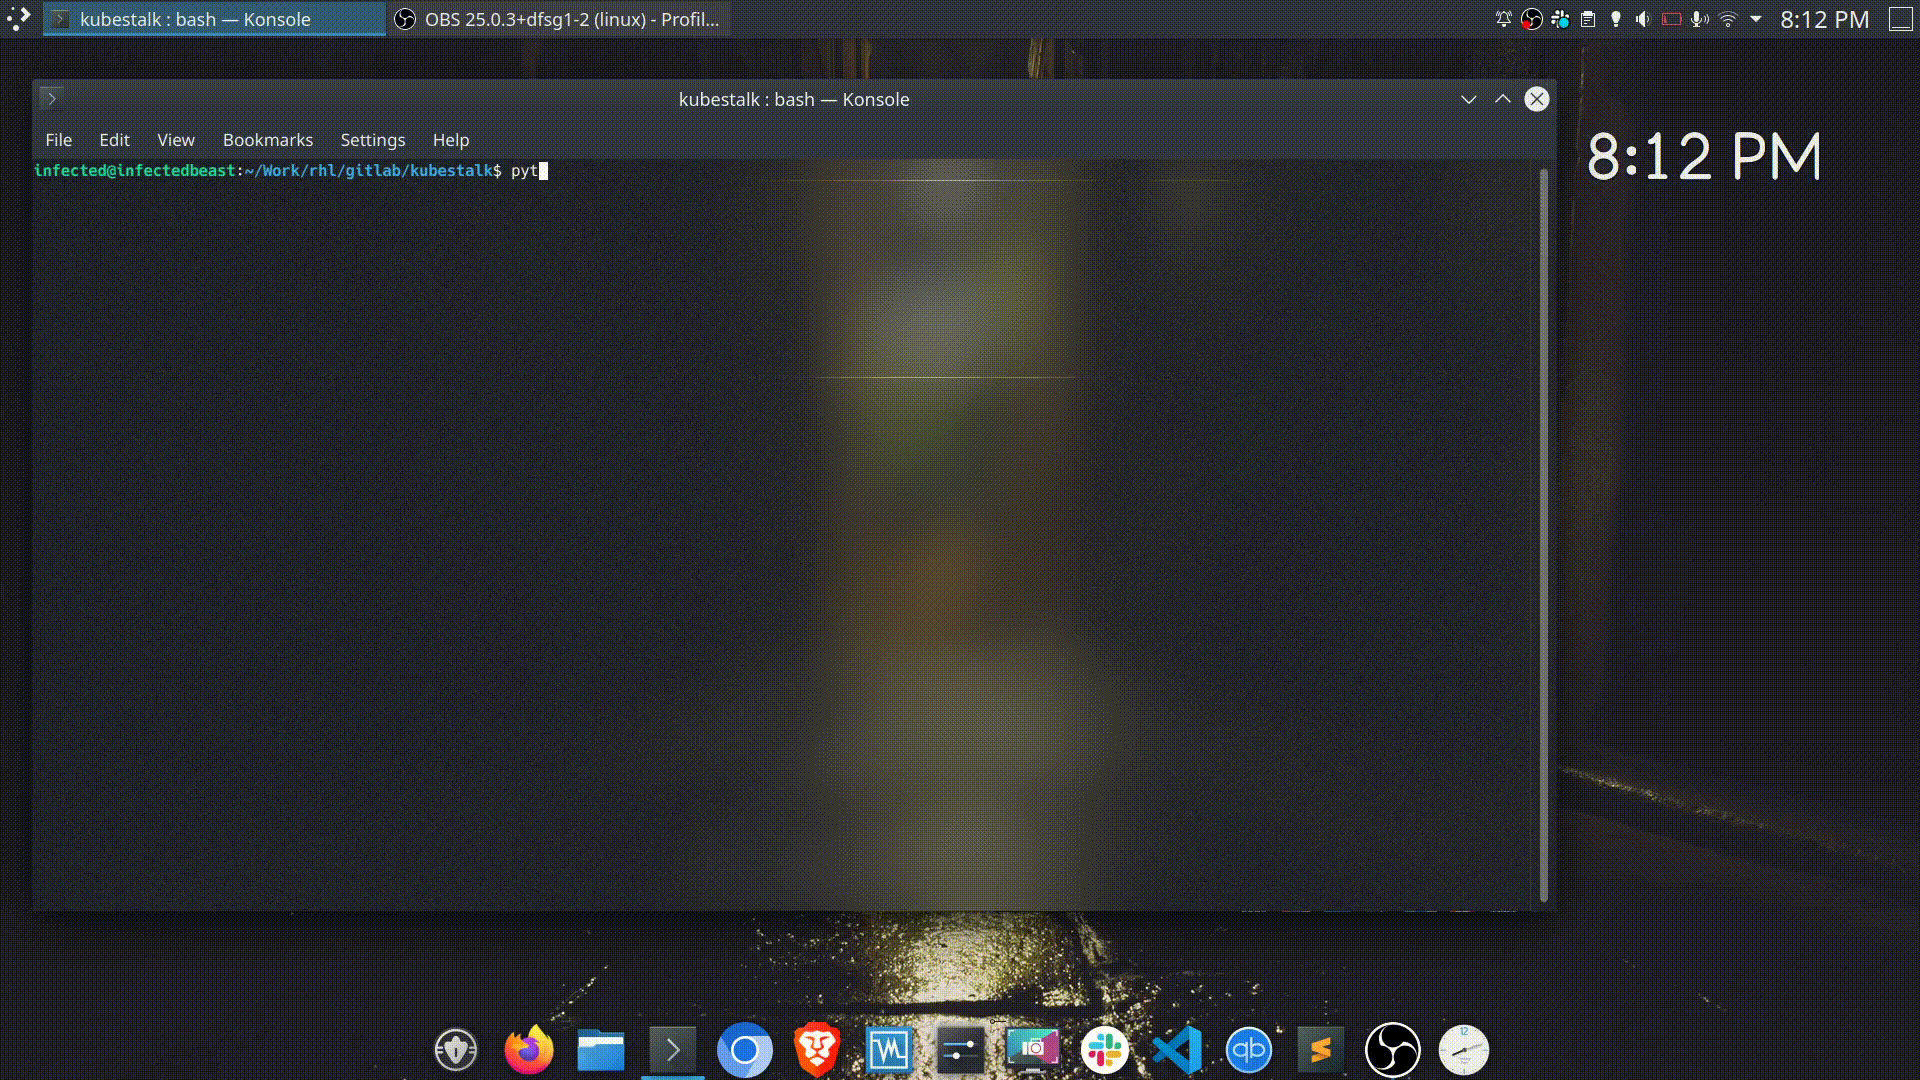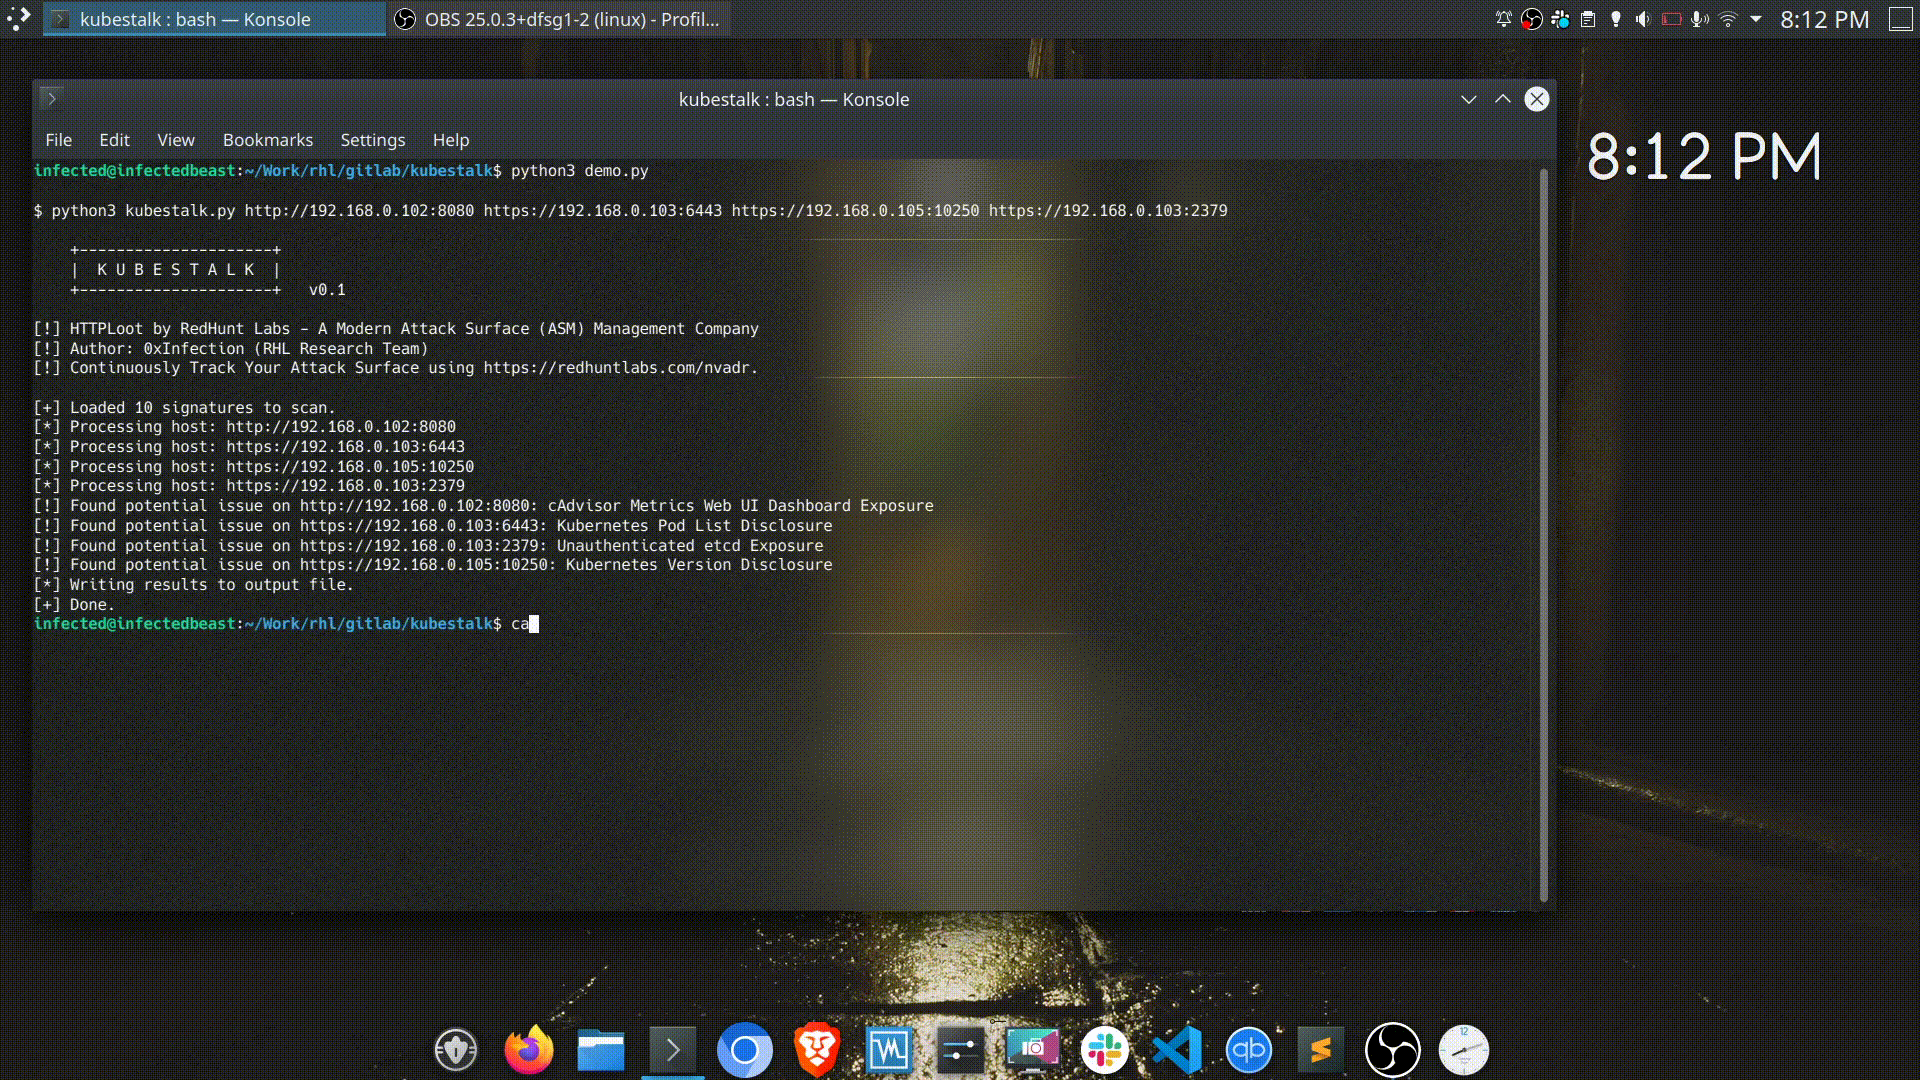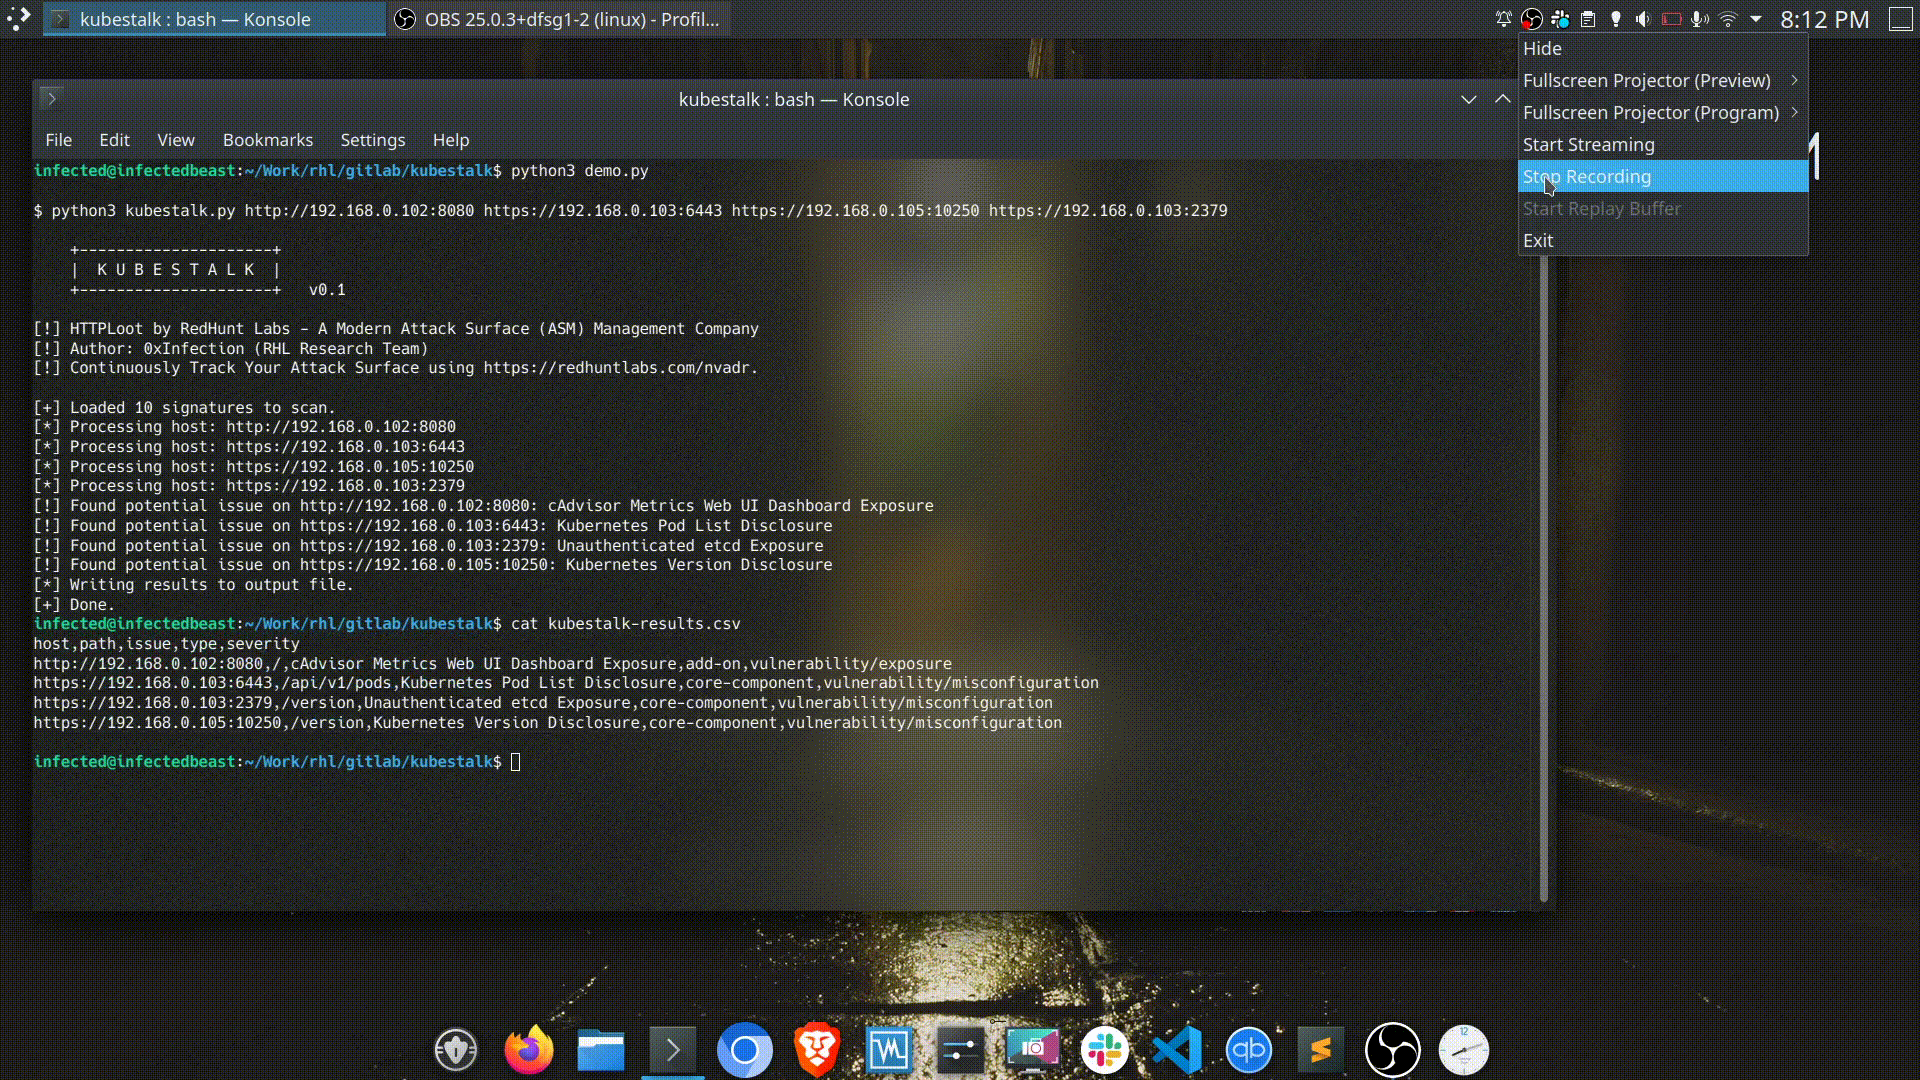 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 hakaioffsec/ingressnightmare-poc
This is a PoC code to exploit the IngressNightmare vulnerabilities (CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, and CVE-2025-1974).
 node9-ai/node9-proxy
The Execution Security Layer for the Agentic Era. Providing deterministic "Sudo" governance and audit logs for autonomous AI agents.
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
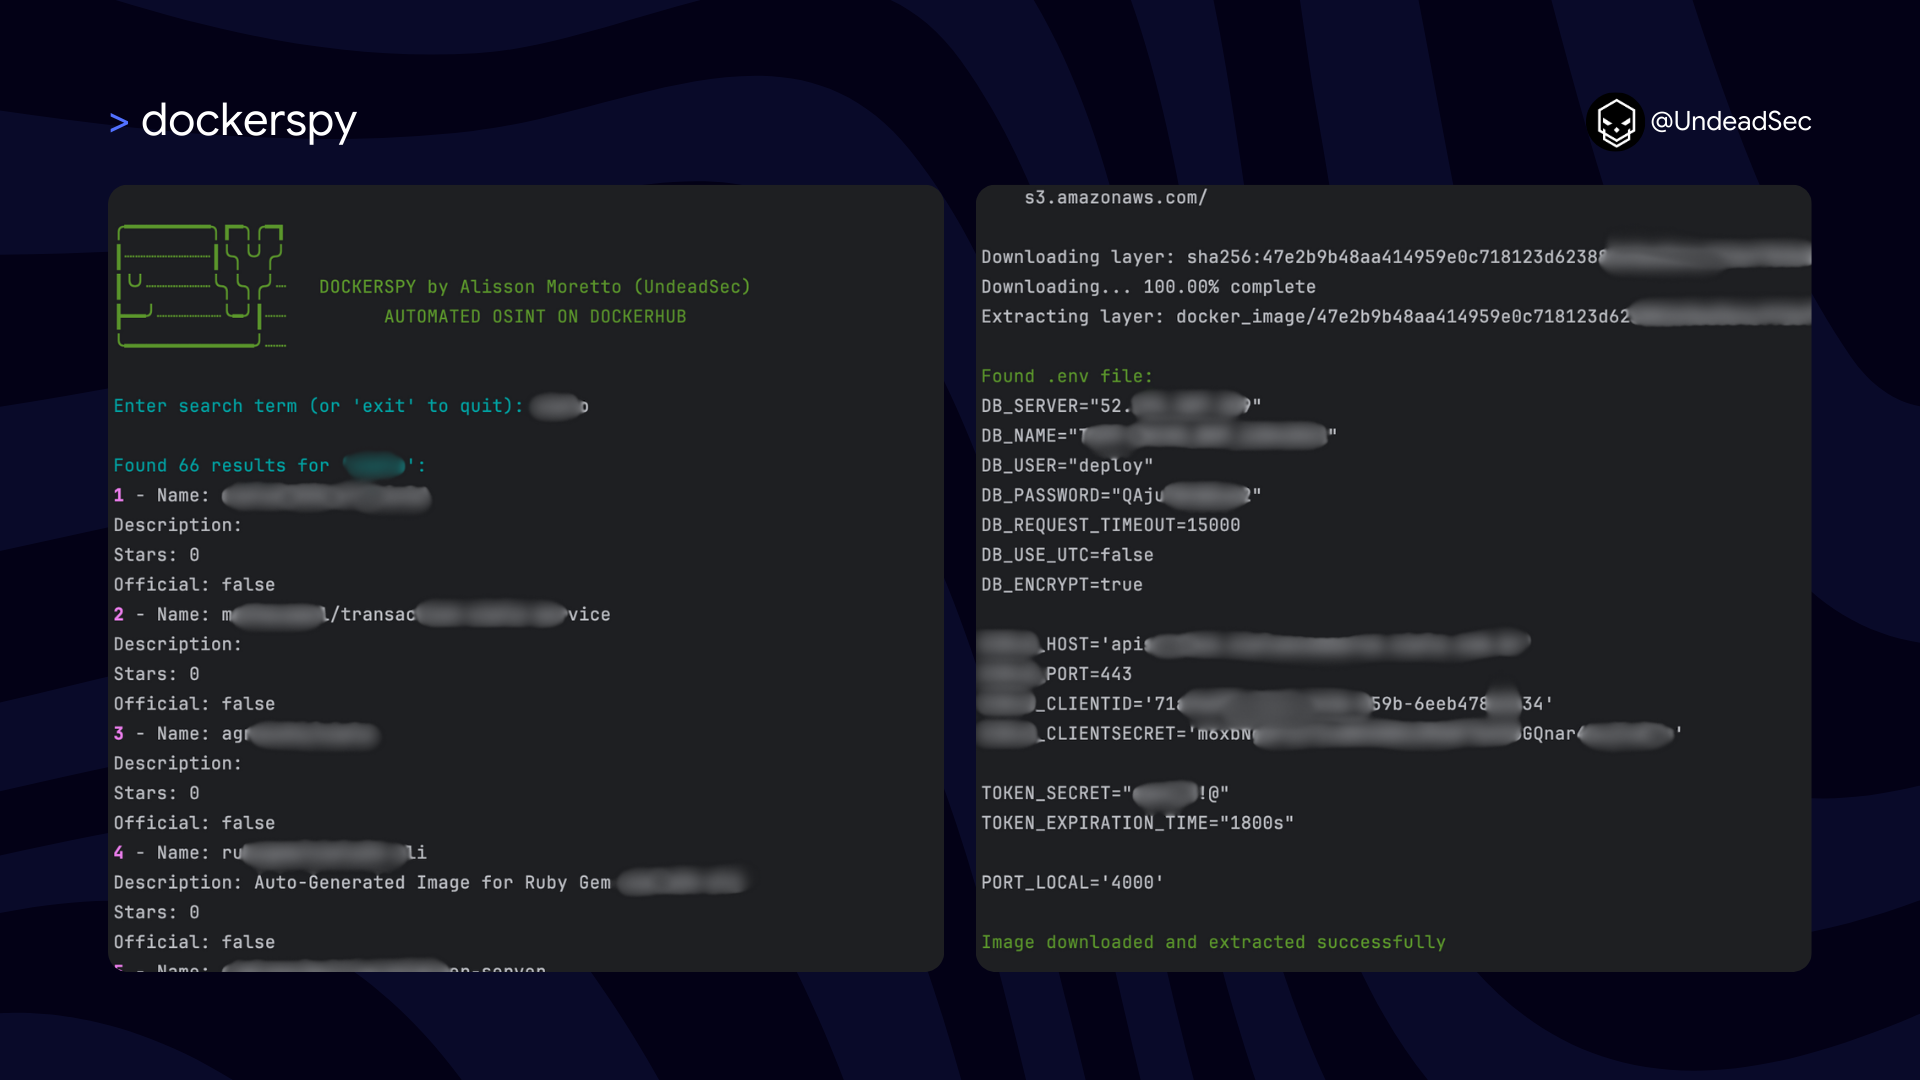 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 linux-lock/bpflock
eBPF-driven security tool for locking and auditing Linux machines. Restricts kernel features, blocks fileless execution, protects memory, and hardens…
 iaga-team/iaga-sentinel
Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 loresuso/psc
the ps utility, with an eBPF twist and container context
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
 eeriedusk/nysm
eBPF-based stealth container that hides processes, sockets, eBPF objects, and audit logs from system monitoring tools, enabling covert…