cve-2024-41110-checker

Parallel SSH-based scanner that detects CVE-2024-41110 in Docker installations, identifies vulnerable versions and AuthZ plugins, and generates a…

Parallel SSH-based scanner that detects CVE-2024-41110 in Docker installations, identifies vulnerable versions and AuthZ plugins, and generates a…

GhostLock - CVE-2026-43499 backport patch for openVZ 7

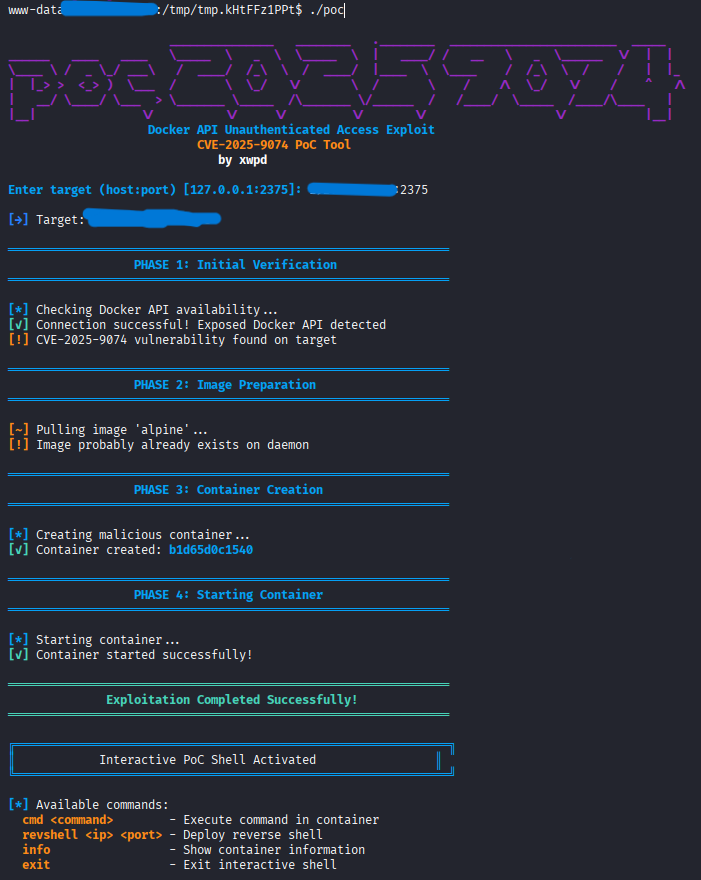
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…

Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…

Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…

Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.

Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…

CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…

eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/

A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…

Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist

Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.

Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…

Poc for CVE 2023 5044

CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…

Companion source for YouTube video "Stop Mounting docker.sock — Run Trivy Without Giving Away Root Access — (inspired by CVE-2026-33634)"

Proof-of-concept exploit for CVE-2020-8554, demonstrating Kubernetes service externalIP manipulation to achieve man-in-the-middle attacks on cluster…

An embeddable, portable, branchable virtual machine to safely run Agents locally.