
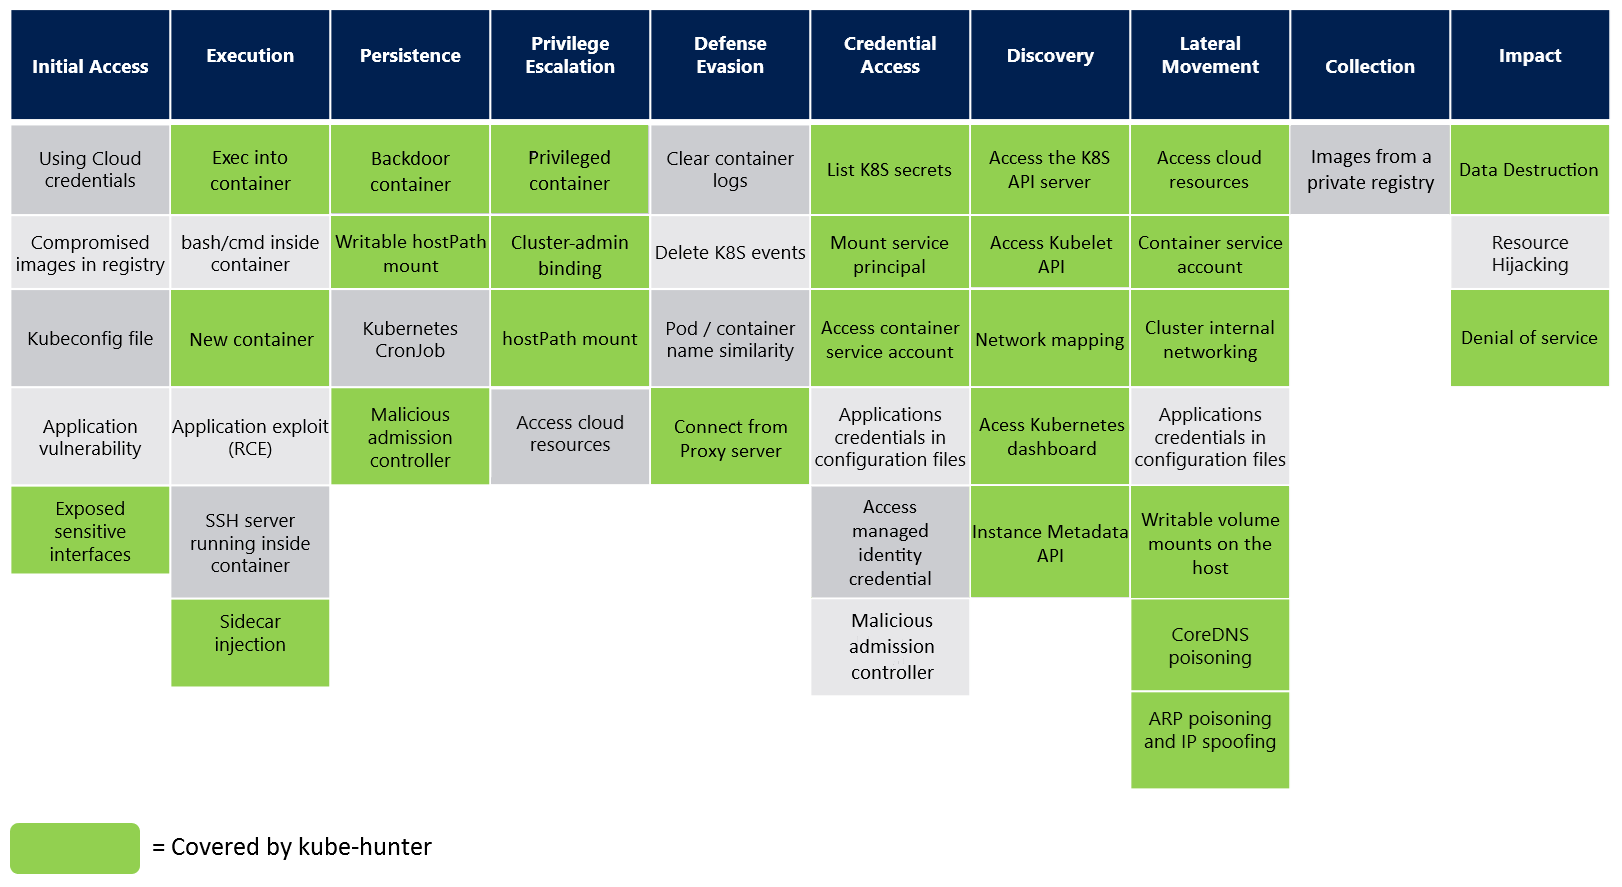
kube-hunter
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
cloud-infrastructure-securitycloud-securitycontainer-escape+5
5.1k
aquasecurity/kube-hunterHunt for security weaknesses in Kubernetes clusters
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 skydive-project/skydive
An open source real-time network topology and protocols analyzer
 microsoft/mxc
Policy-driven, layered isolation and containment
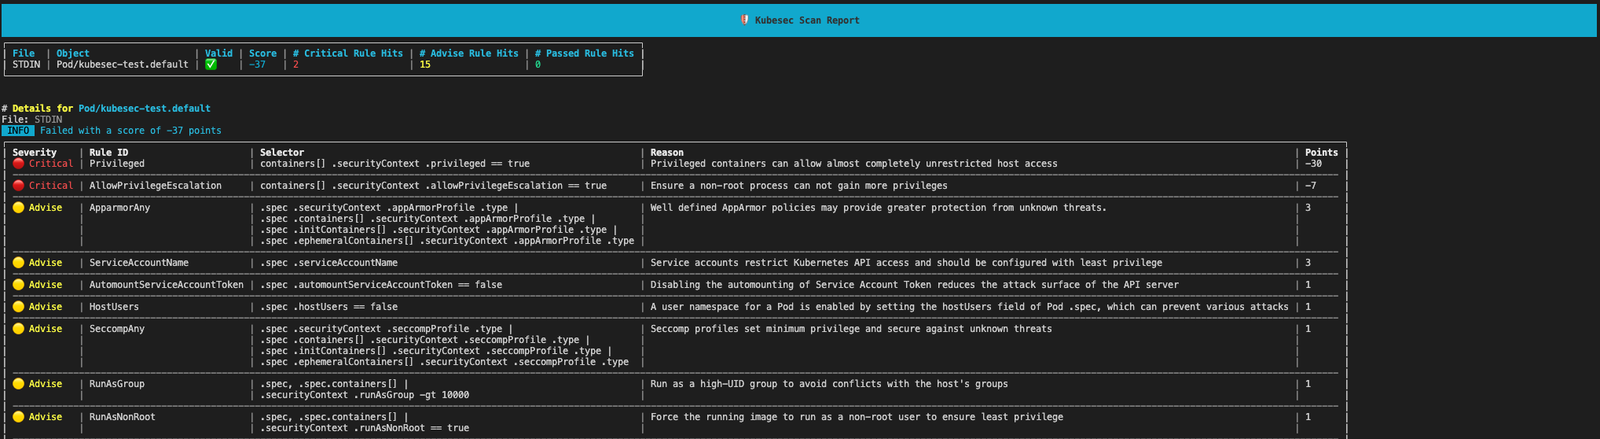 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
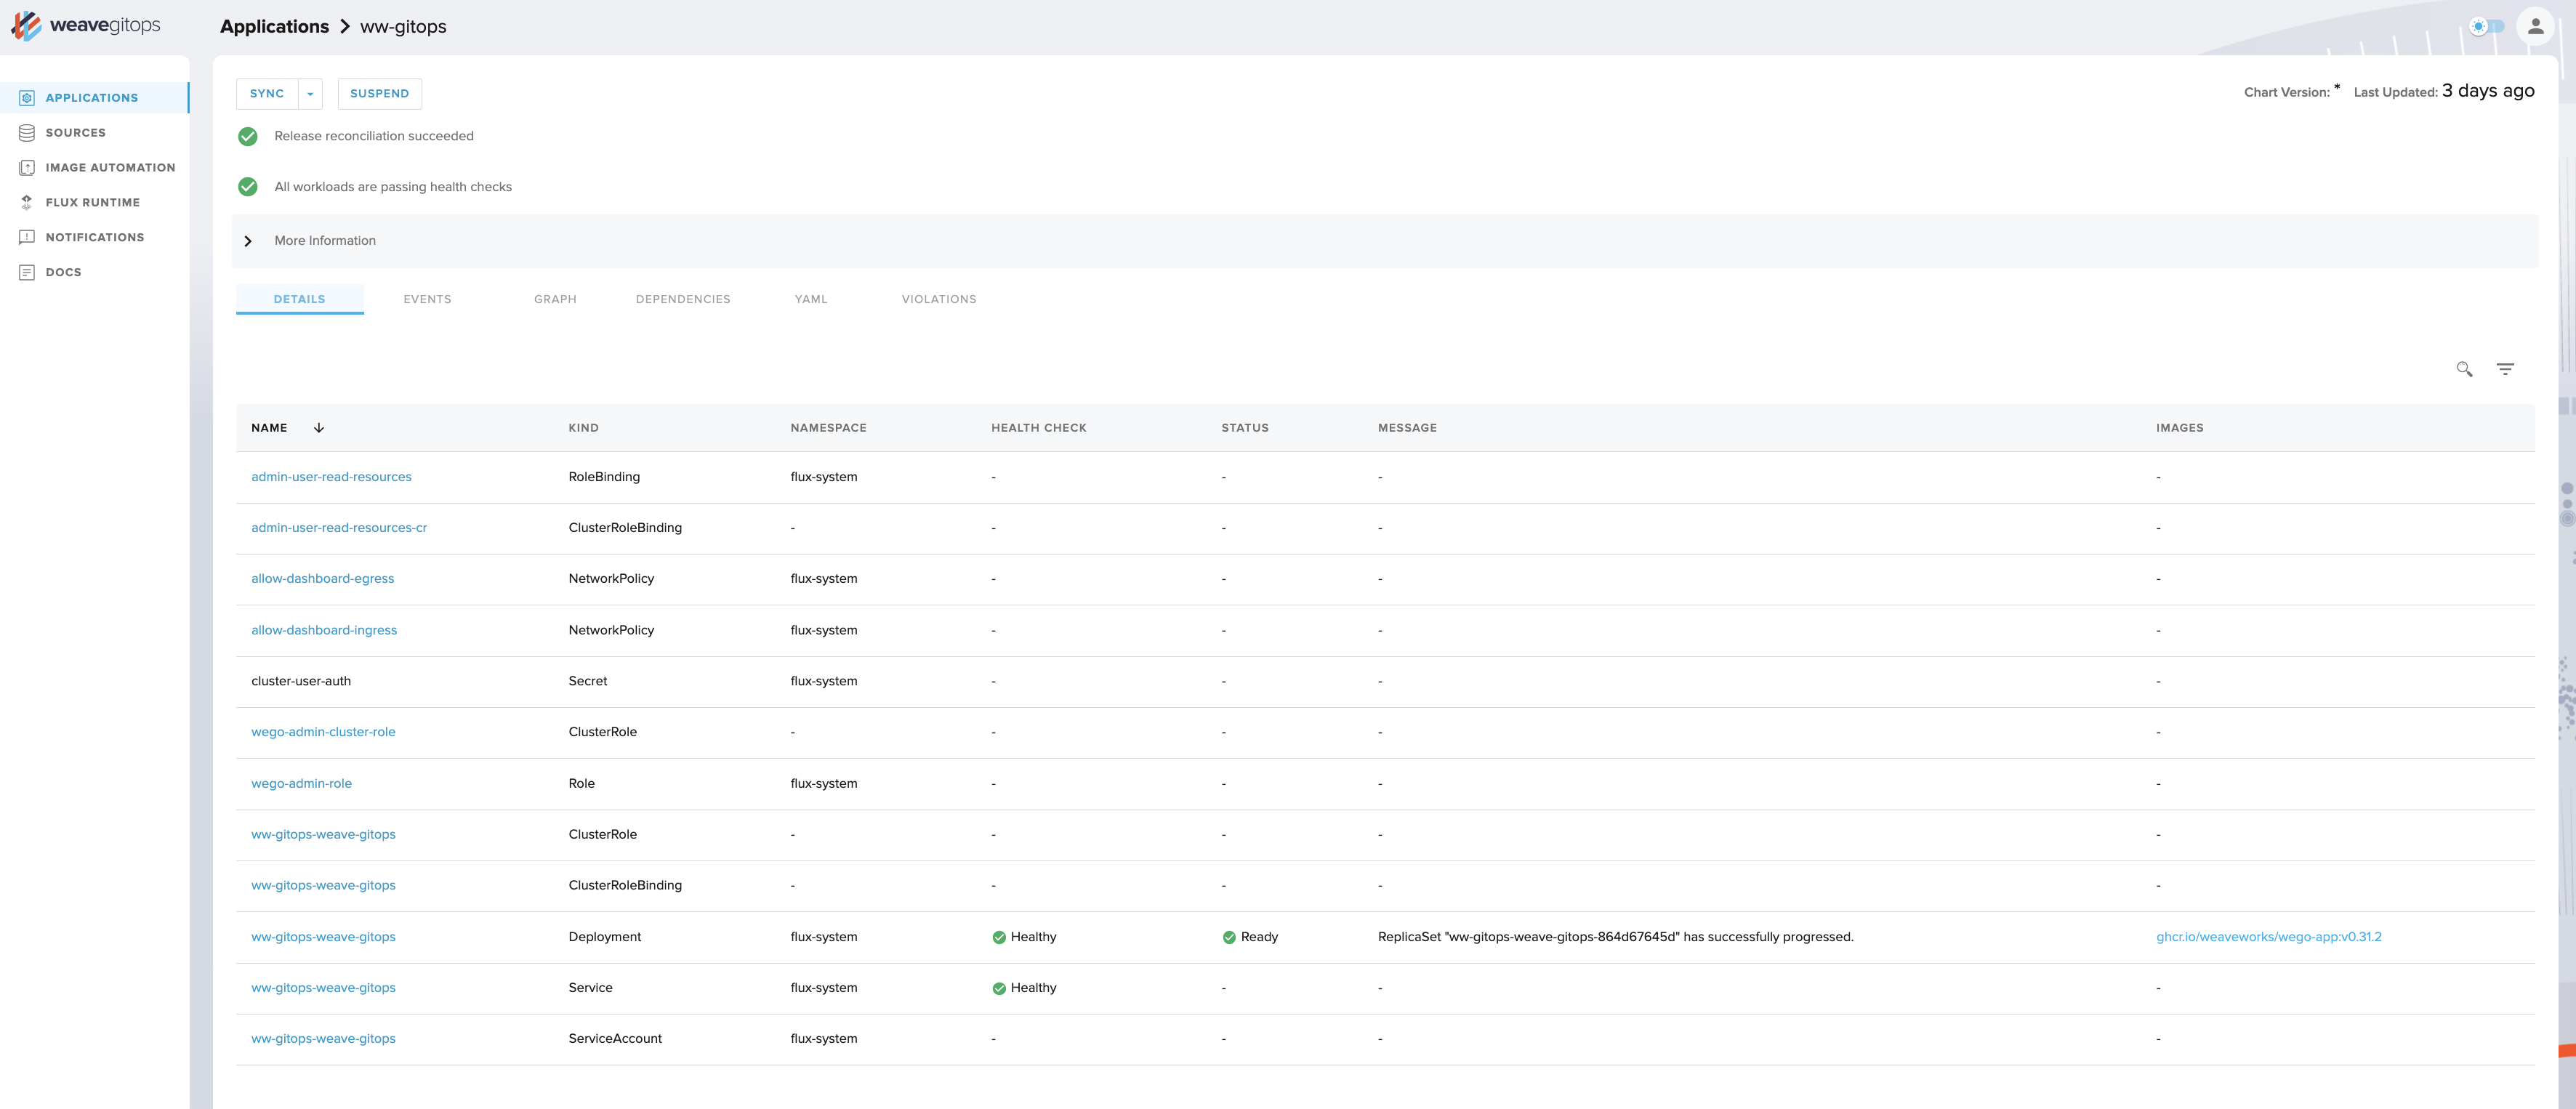 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 kubesphere/kubeeye
Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…
 chaostoolkit/chaostoolkit-kubernetes
Kubernetes driver extension of the Chaos Toolkit probes and actions API
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
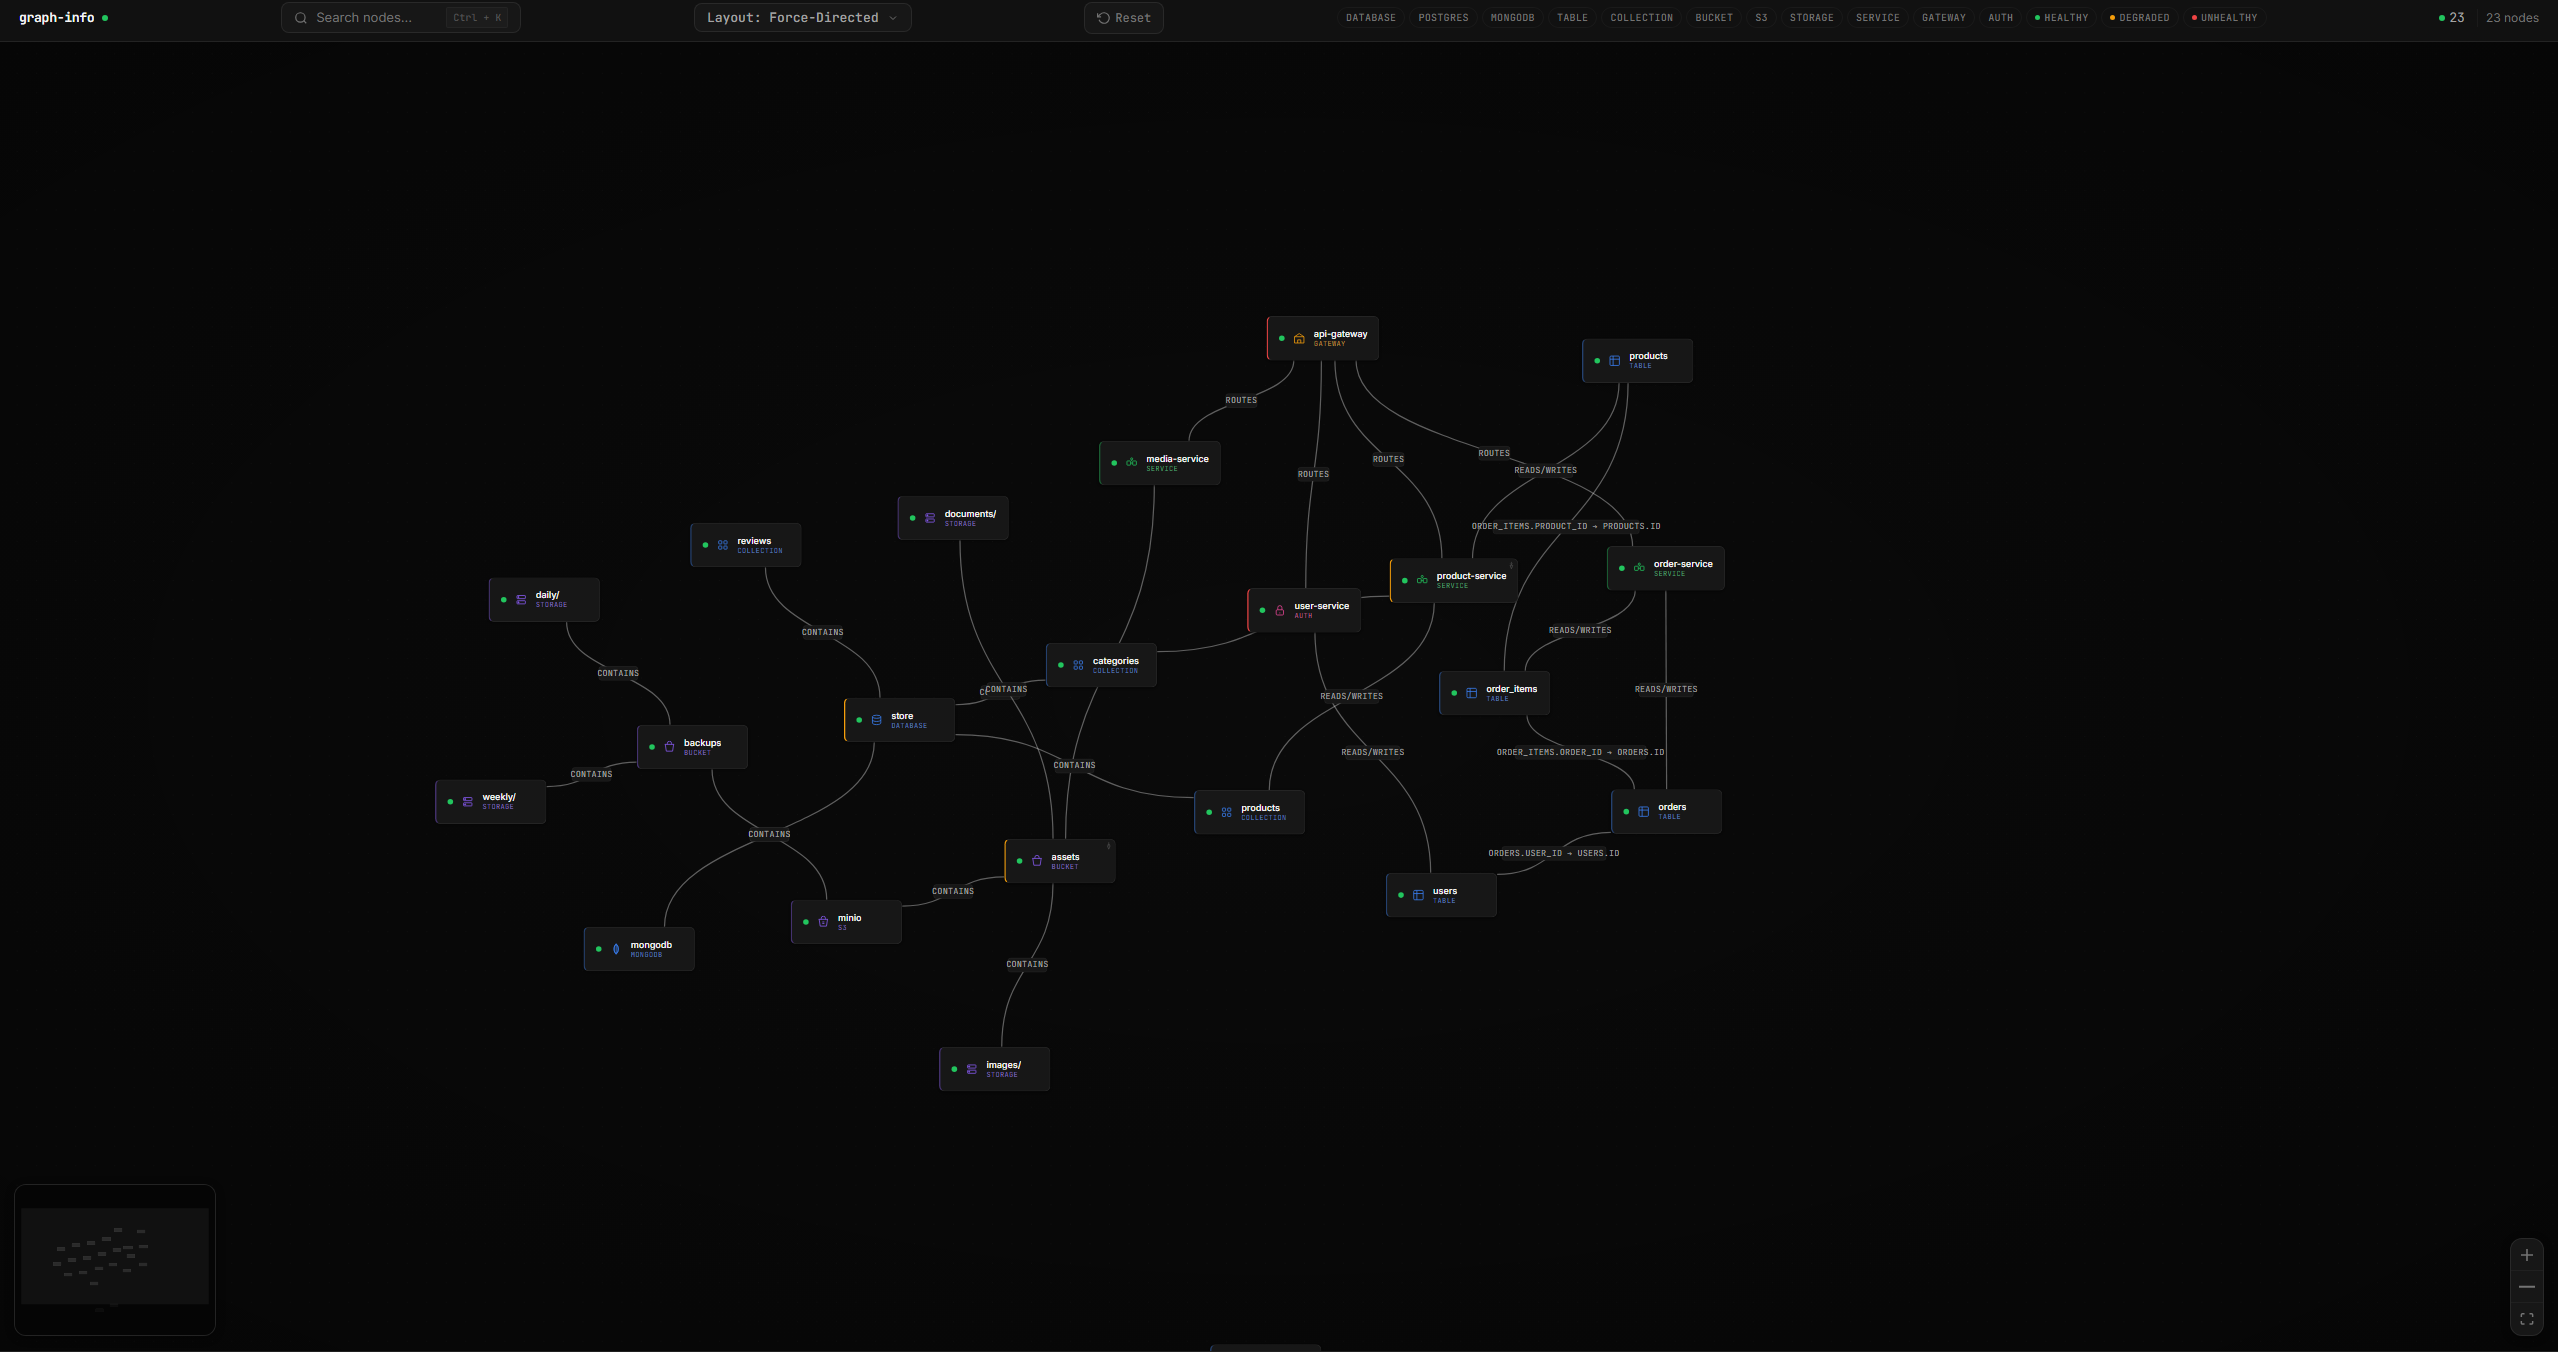 guilherme-grimm/graph-go
simply nodes and graphs
 owasp/kubelight
OWASP Kubernetes security and compliance tool [WIP]
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration