
practice-22-23
 lacinquette/practice-22-23
CVE-2017-9608 analysis
binary-analysiscontainer-securityeducation+3
lacinquette/practice-22-23CVE-2017-9608 analysis
 killerbees19/cve-2024-24760
mailcow: Docker Container Exposure to Local Network
 aws-samples/kubernetes-log4j-cve-2021-44228-node-agent
Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
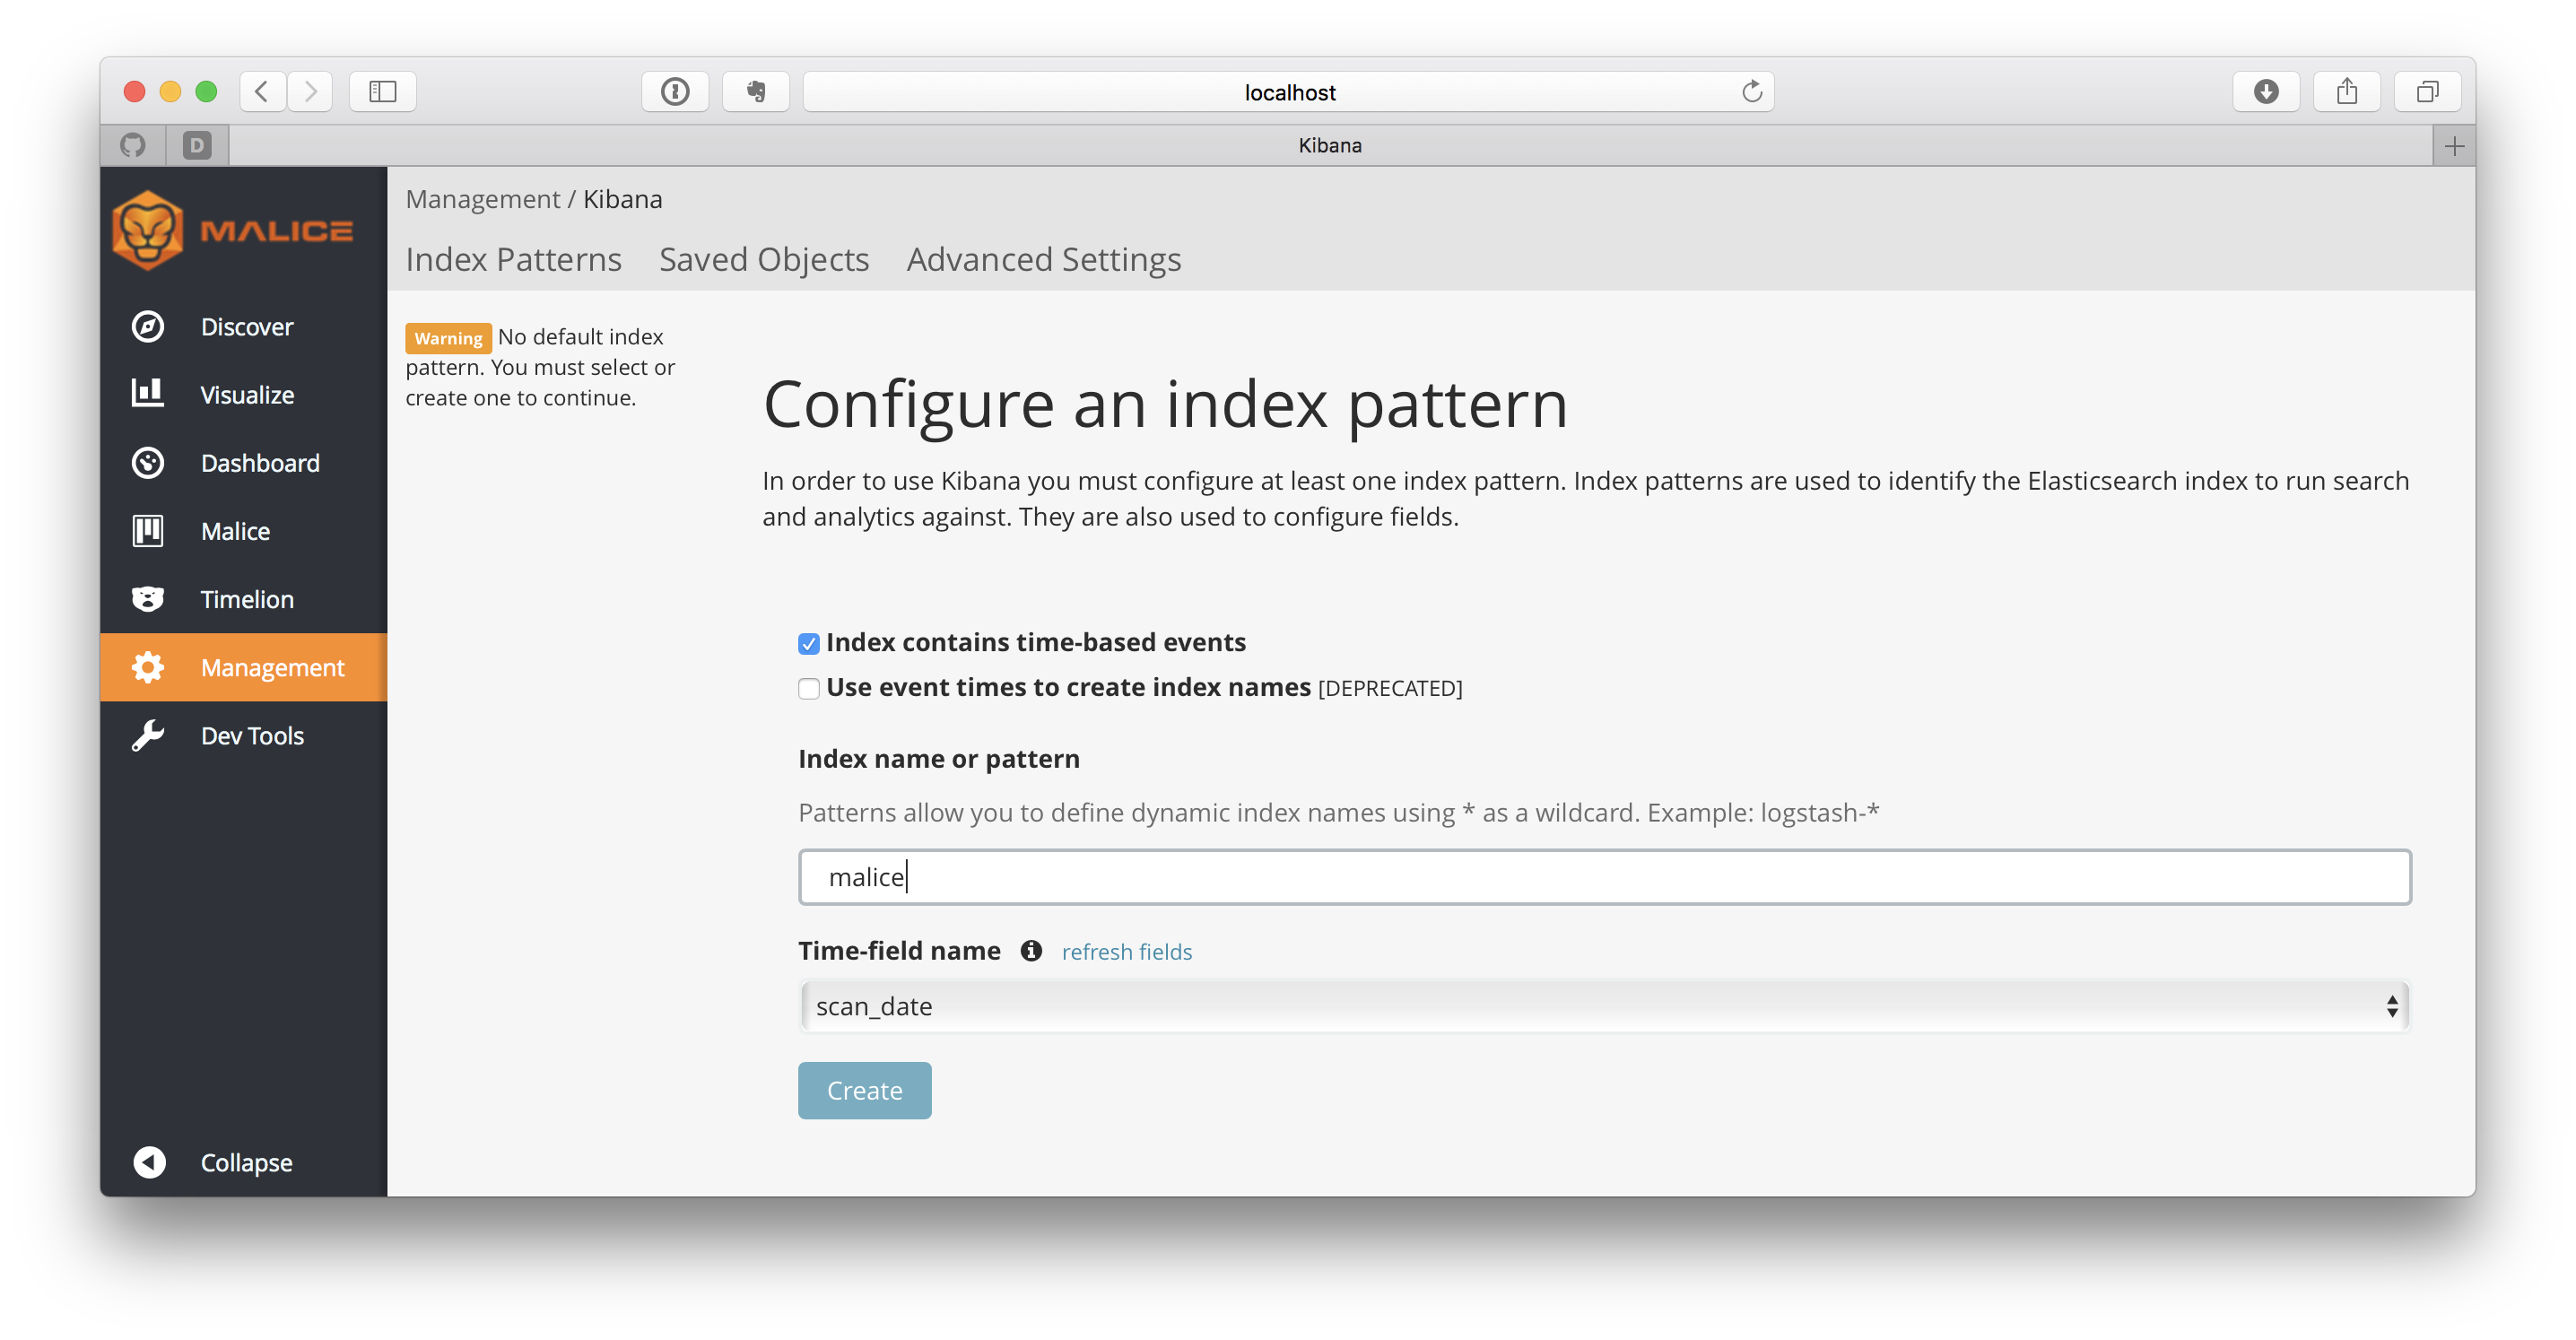 maliceio/malice
VirusTotal Wanna Be - Now with 100% more Hipster
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
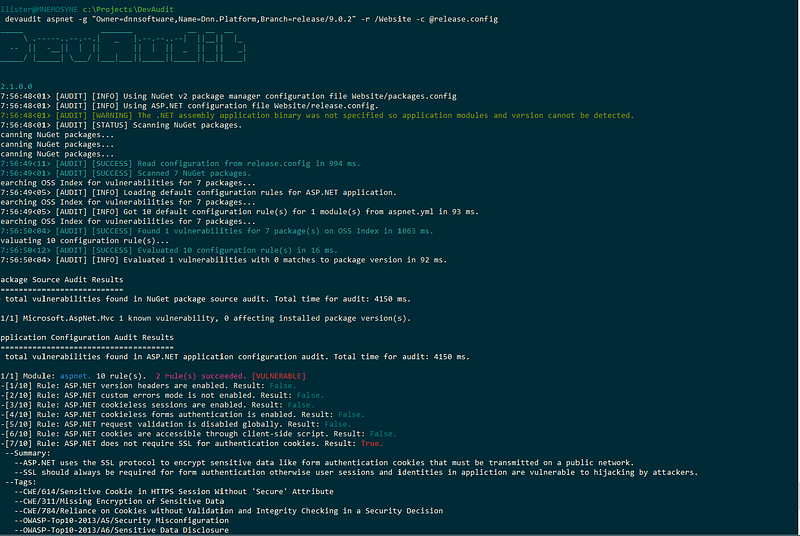 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 sandialabs/dr_robot
This tool can be used to enumerate the subdomains associated with a company by aggregating the results of multiple OSINT (Open Source Intelligence)…
 spiarh/webhook-cve-2022-0811
Simple webhook to block exploitation of CVE-2022-0811
 medicean/vulapps
快速搭建各种漏洞环境(Various vulnerability environment)
 grantbirki/redash-vulnerable
A Dockerized Redash instance that is vulnerable to CVE-2021-21239
 12345qwert123456/cve-2021-42013
Vulnerable configuration Apache HTTP Server version 2.4.49/2.4.50
 12345qwert123456/cve-2021-41773
Vulnerable configuration Apache HTTP Server version 2.4.49
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…