

openvas-scanner
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
configuration-auditingcontainer-securitydatabase-security+5
4.8k
greenbone/openvas-scannerThis repository contains the scanner component for Greenbone Community Edition.
 docker/docker-bench-security
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
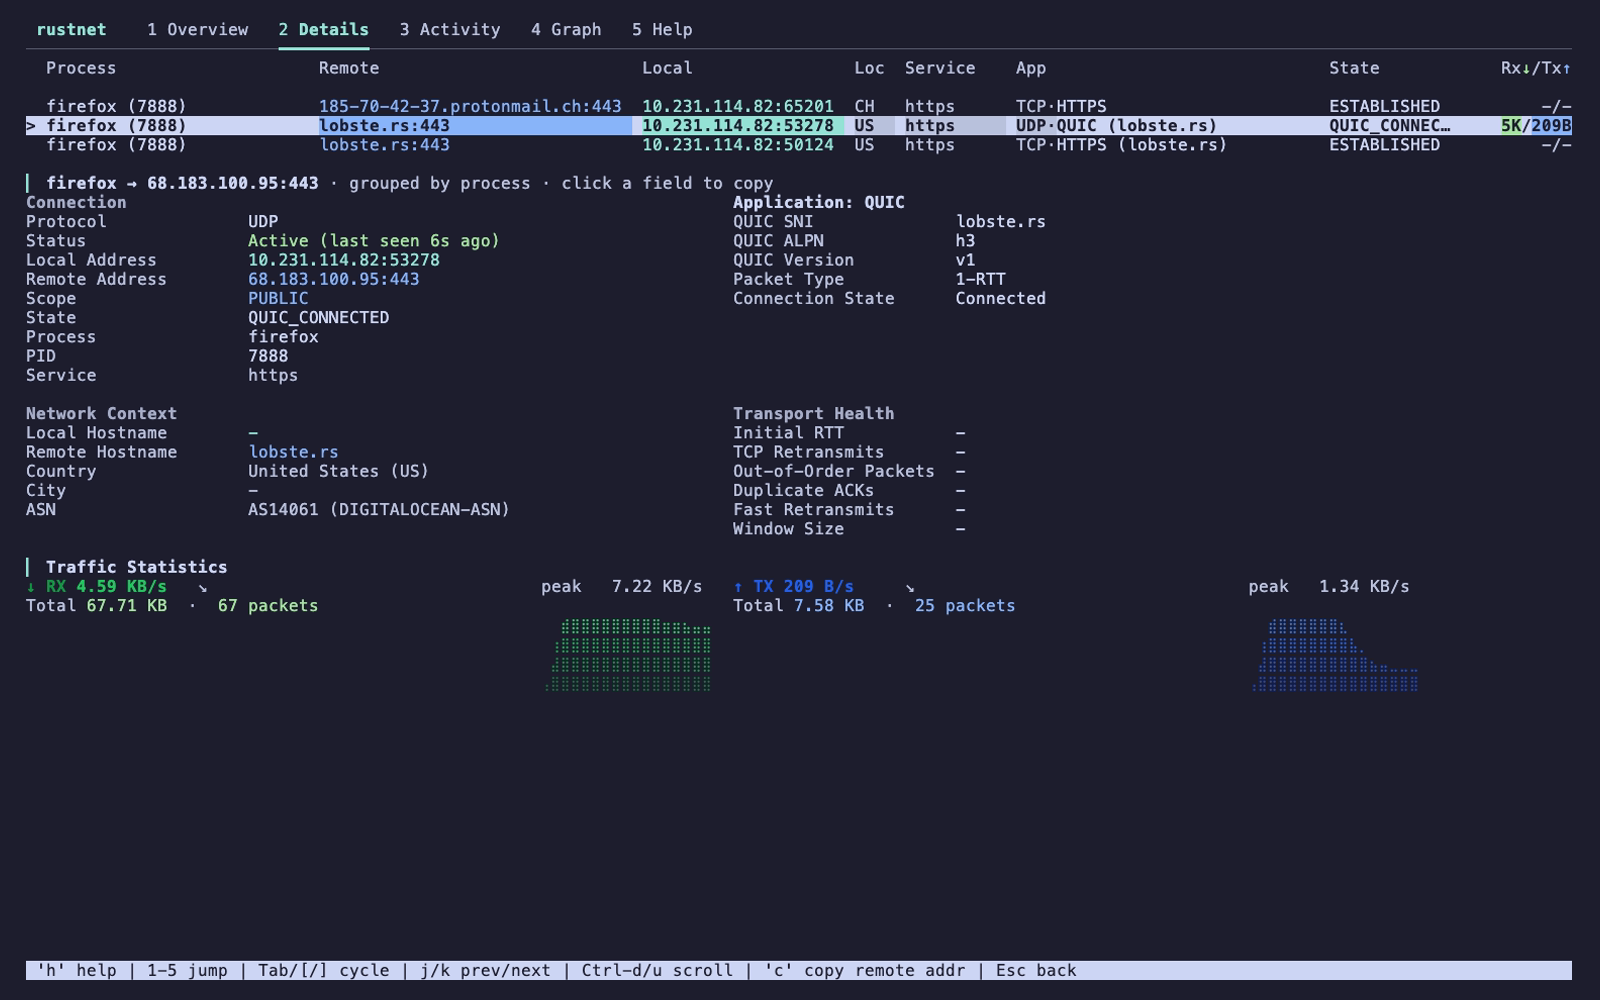 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 usmannasir/cyberpanel
Cyber Panel - The hosting control panel for OpenLiteSpeed
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 alexei-led/pumba
Chaos testing, network emulation, and stress testing tool for containers
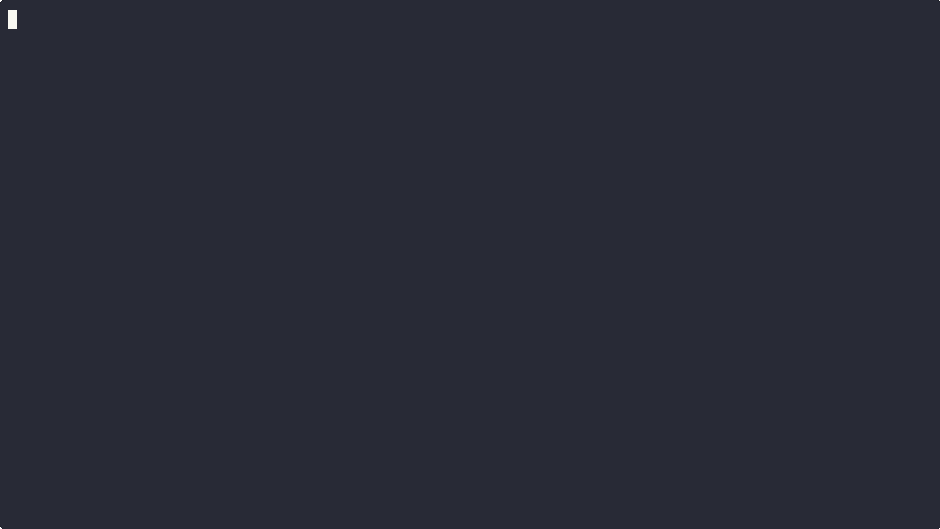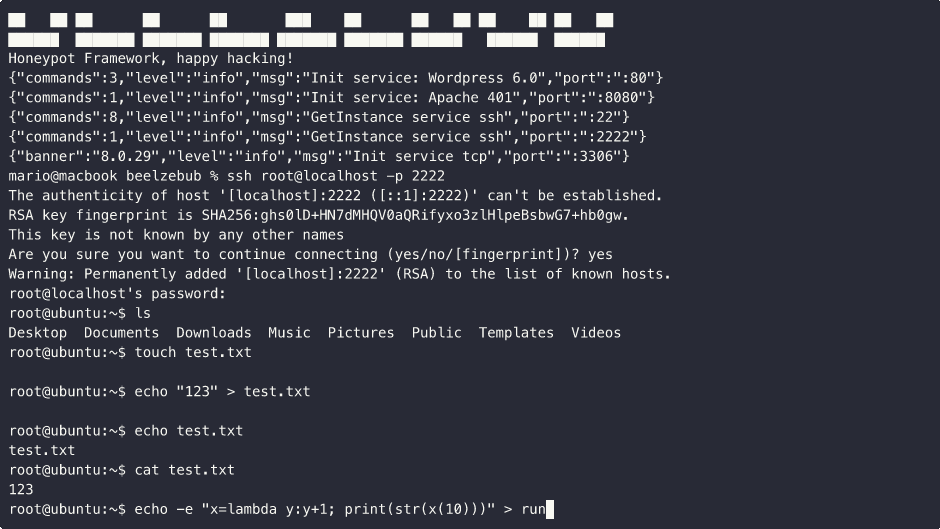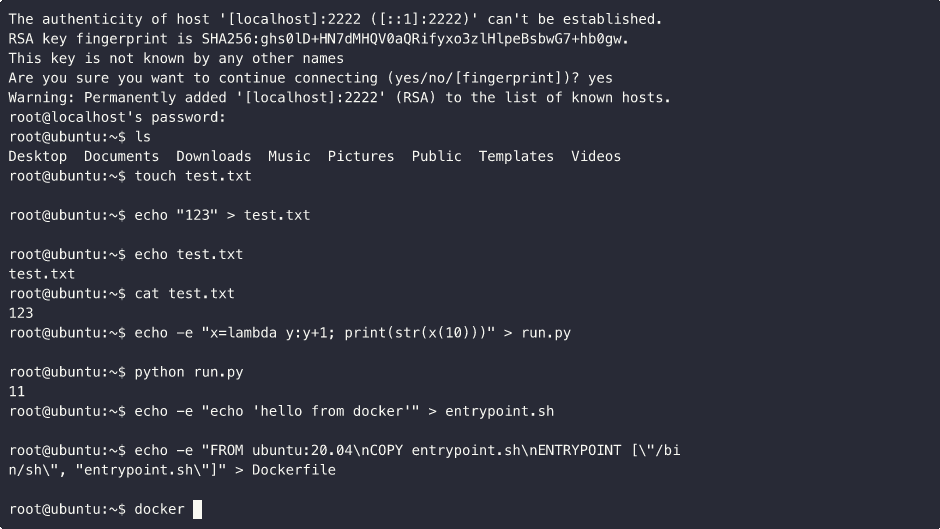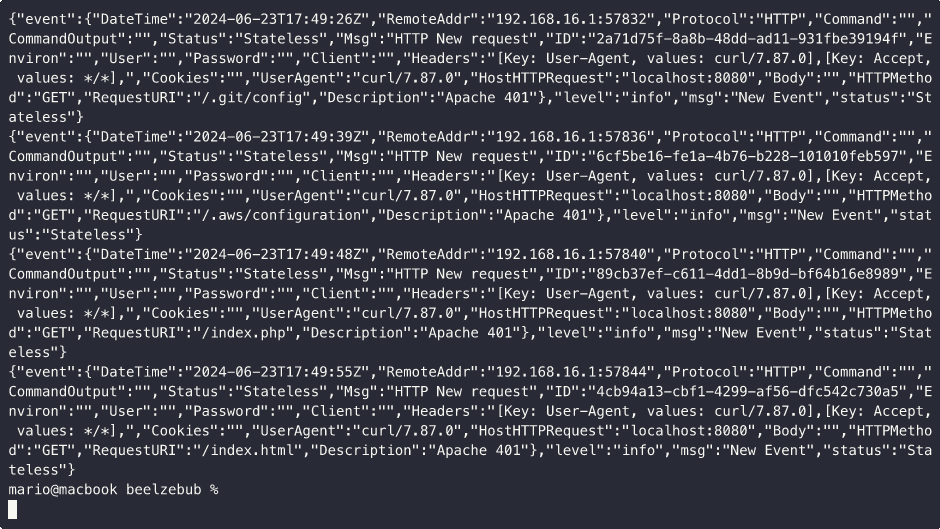 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
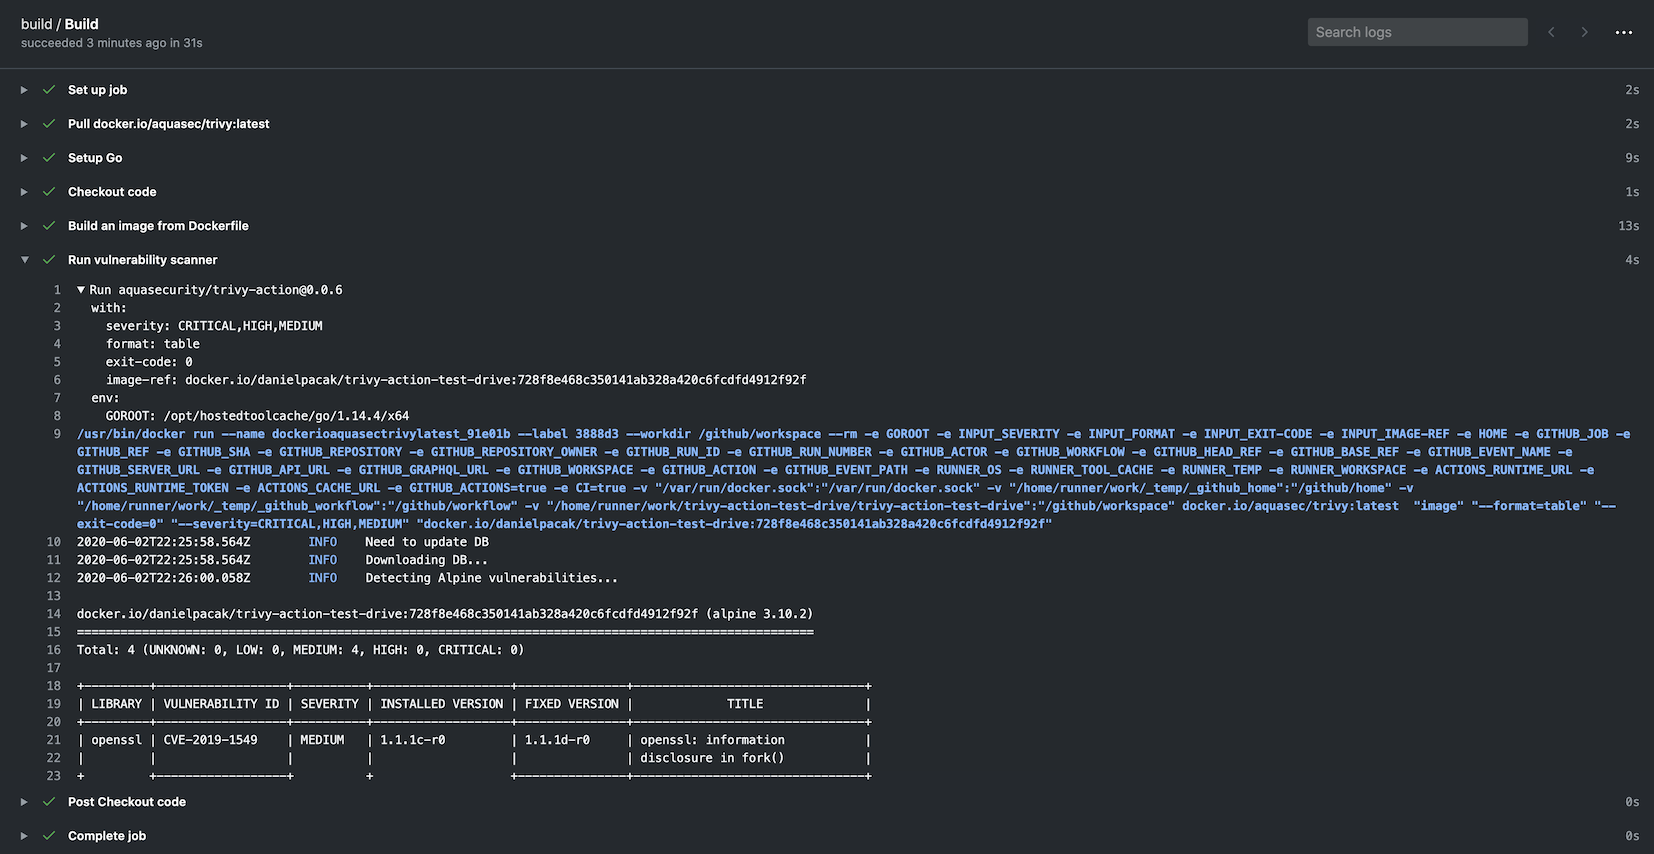 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
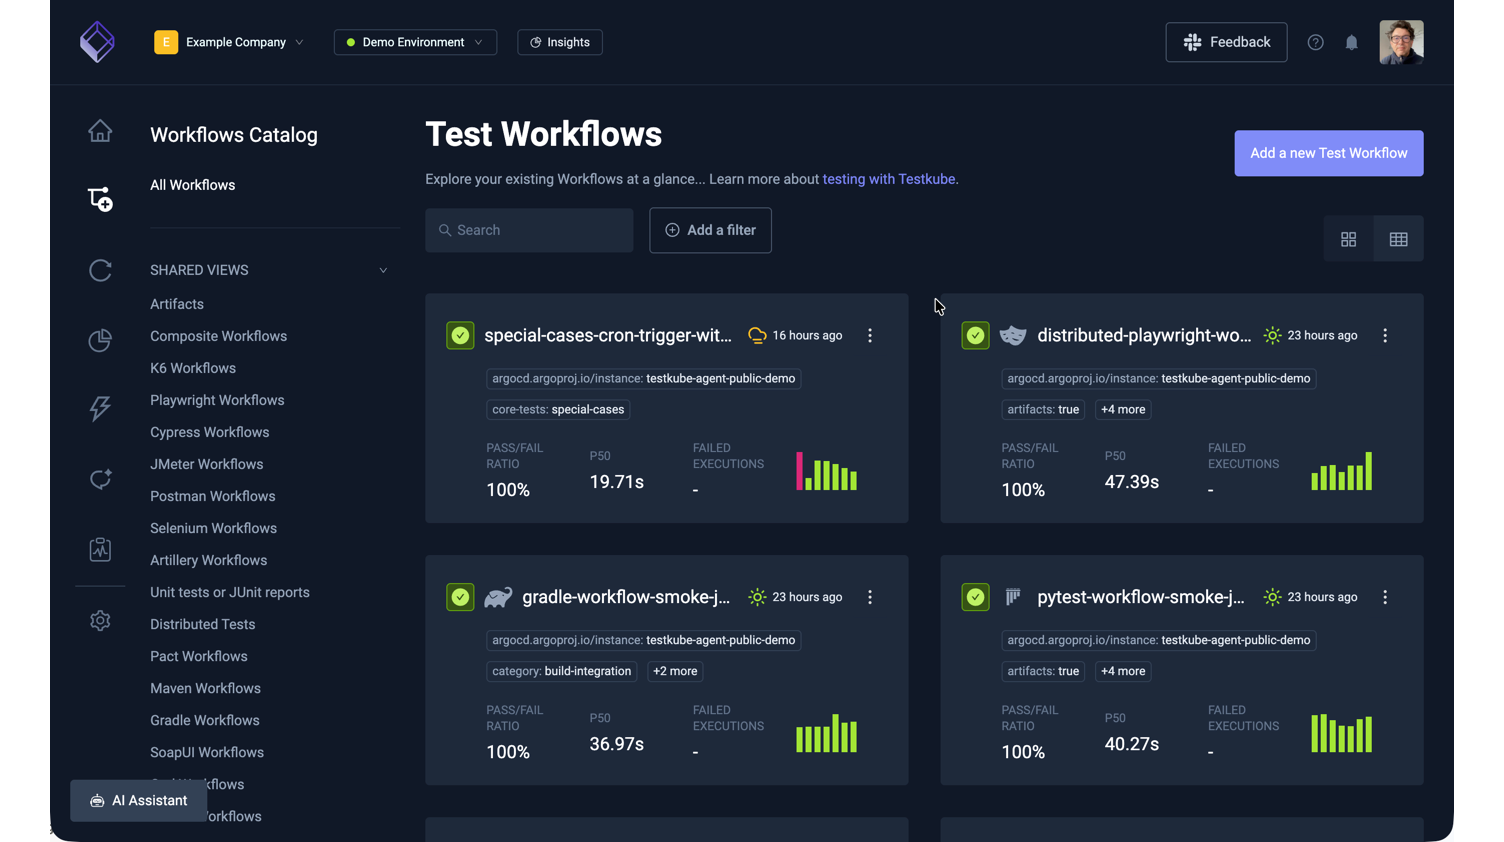 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
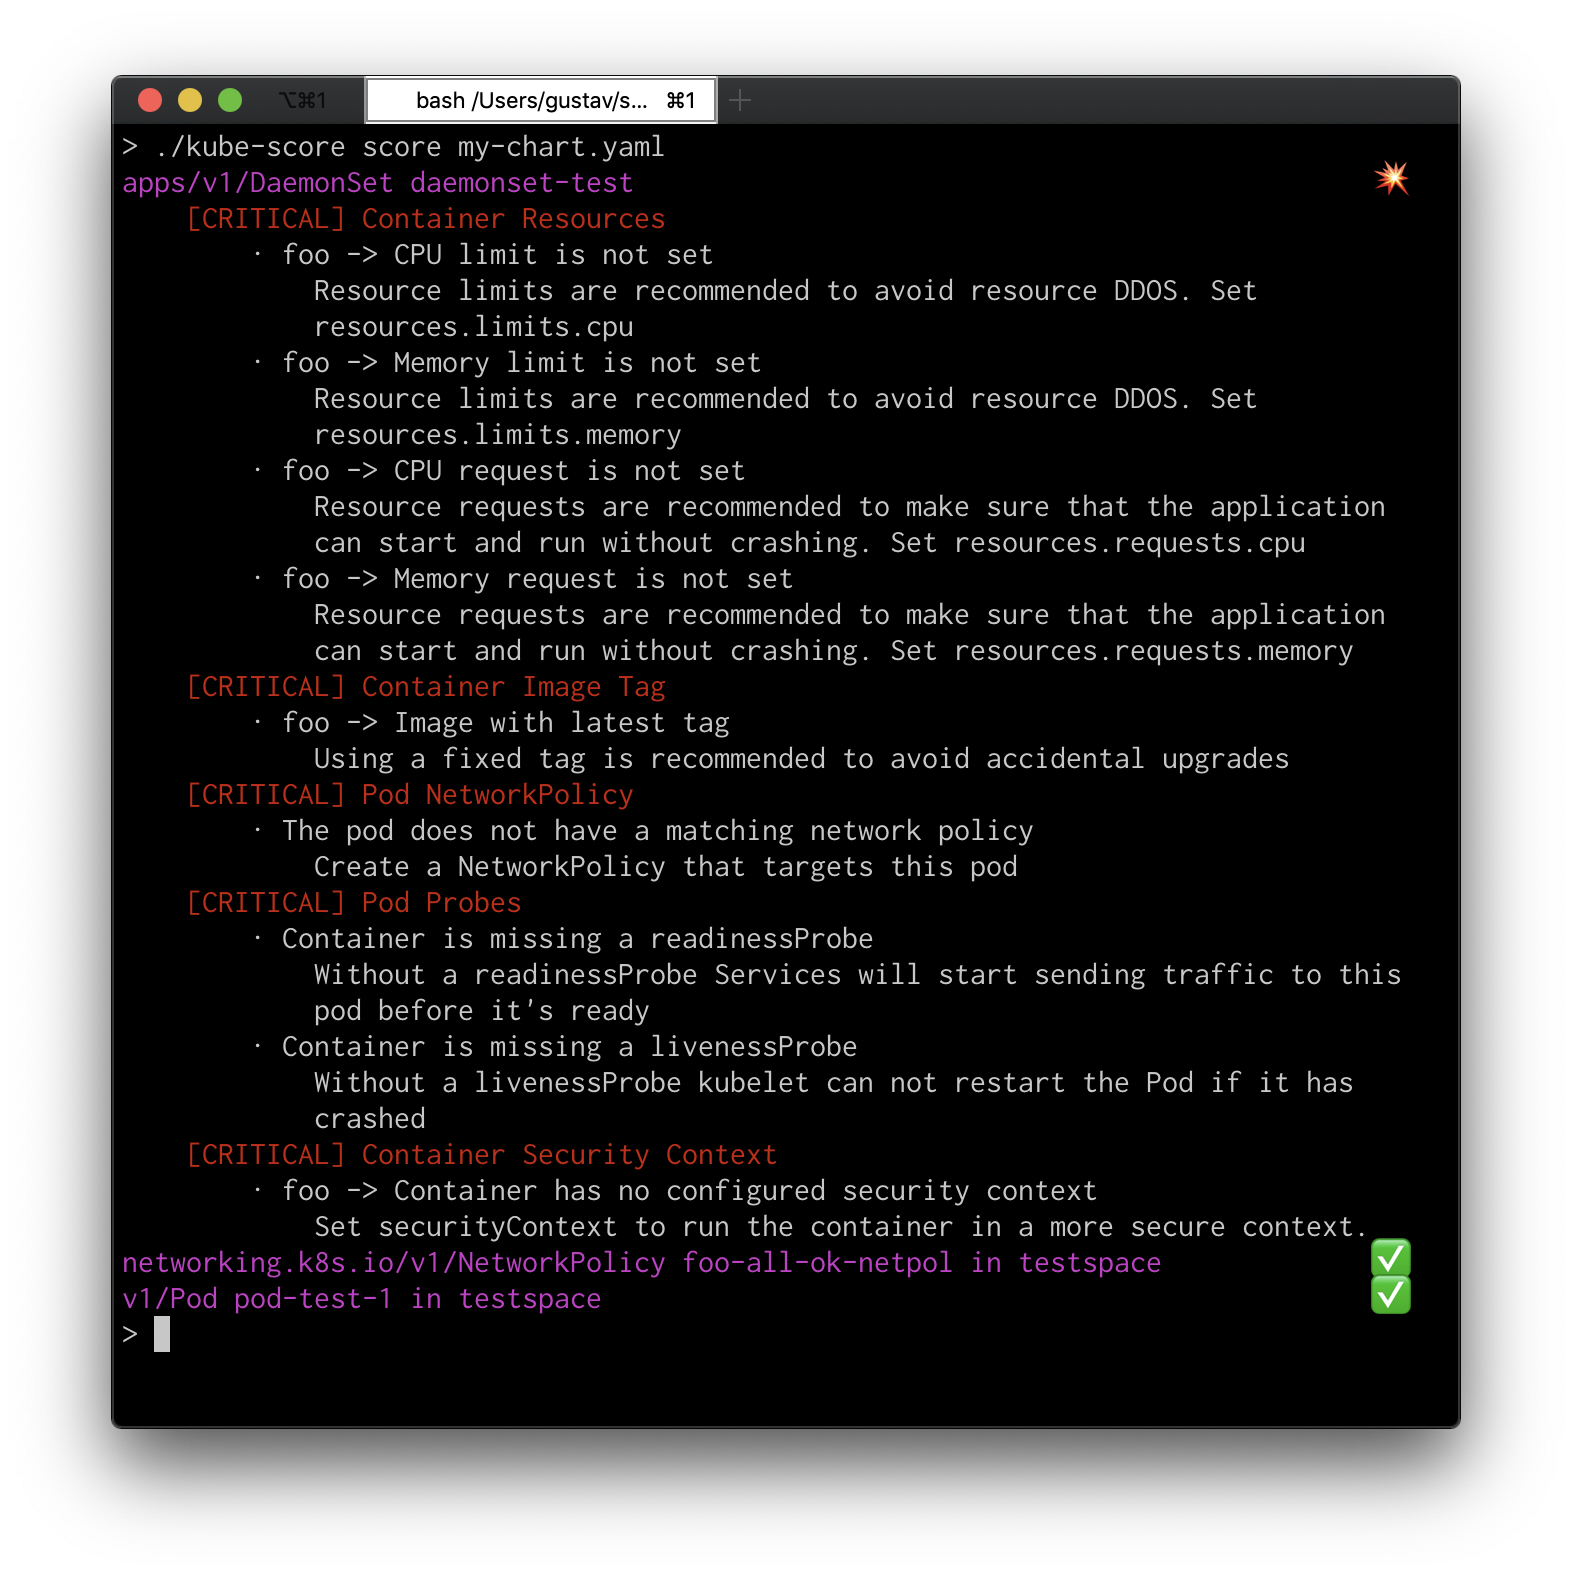 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…