

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
10.8k
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
 kubeshop/testkube
☸️ The Testing Platform for the agentic SDLC
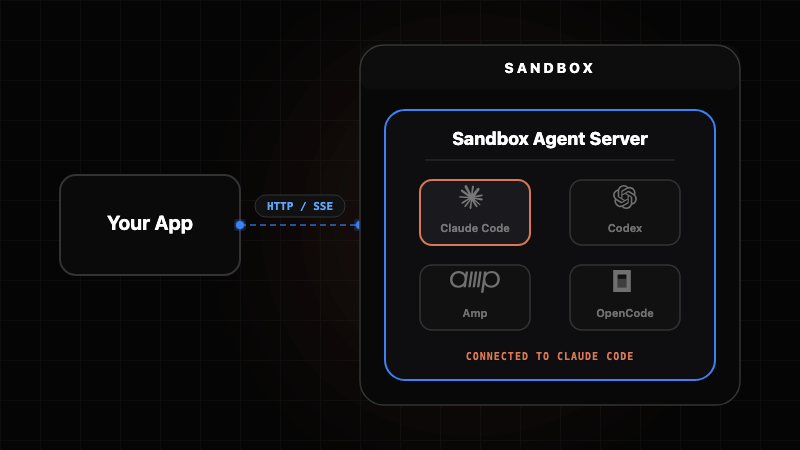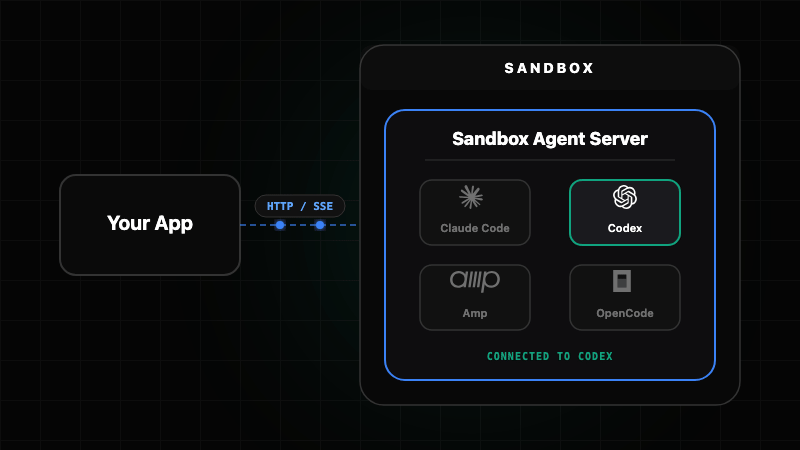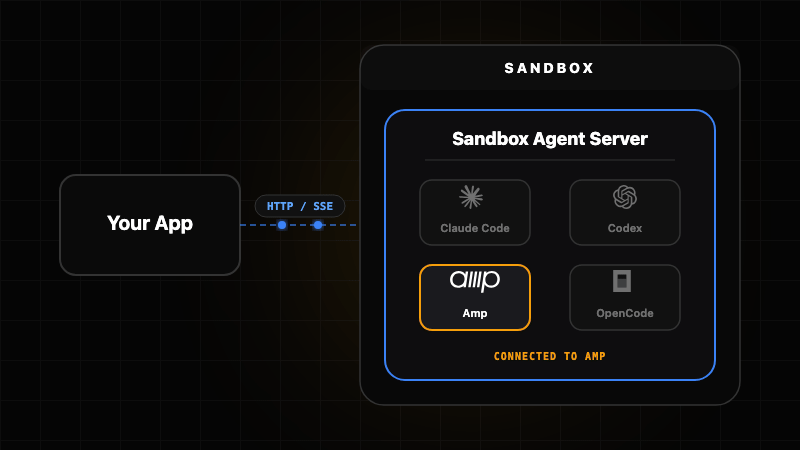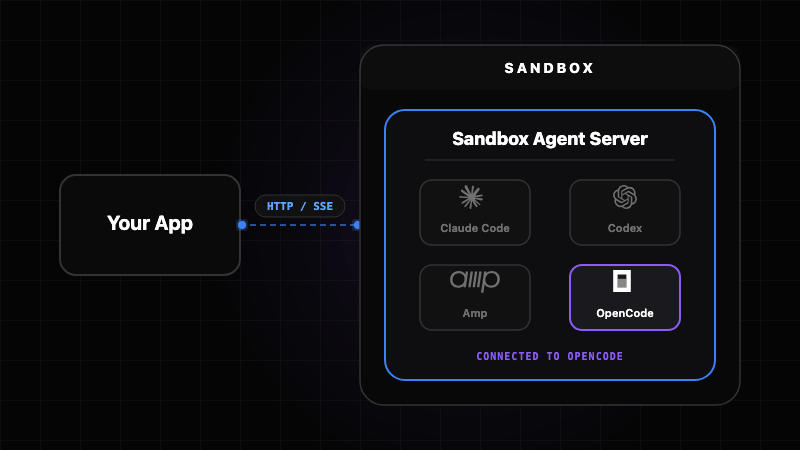 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
 instavm/coderunner
A local sandbox for your AI agents
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 afshinm/zerobox
Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.