

lxd_root
 initstring/lxd_root
Linux privilege escalation via LXD
container-securityexploitationpenetration-testing+3
142
initstring/lxd_rootLinux privilege escalation via LXD
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 sensepost/dwn
d(ockerp)wn - a docker pwn tool manager
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 rezilion/mi-x
Determine whether your compute is truly vulnerable to a specific vulnerability by accounting for all factors which affect *actual* exploitability…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 nccgroup/wubes
Qubes containerization on Windows
 sandumjacob/ingressnightmare-pocs
CVE-2025-1974
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 wh04m1001/cve-2023-36723
Proof-of-concept exploit for CVE-2023-36723, an arbitrary directory creation vulnerability in Windows Container Manager, enabling privilege…
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 esonhugh/ingressnightmare-cve-2025-1974-exps
IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…
 paloaltonetworks/can-ctr-escape-cve-2022-0492
Test whether a container environment is vulnerable to container escapes via CVE-2022-0492
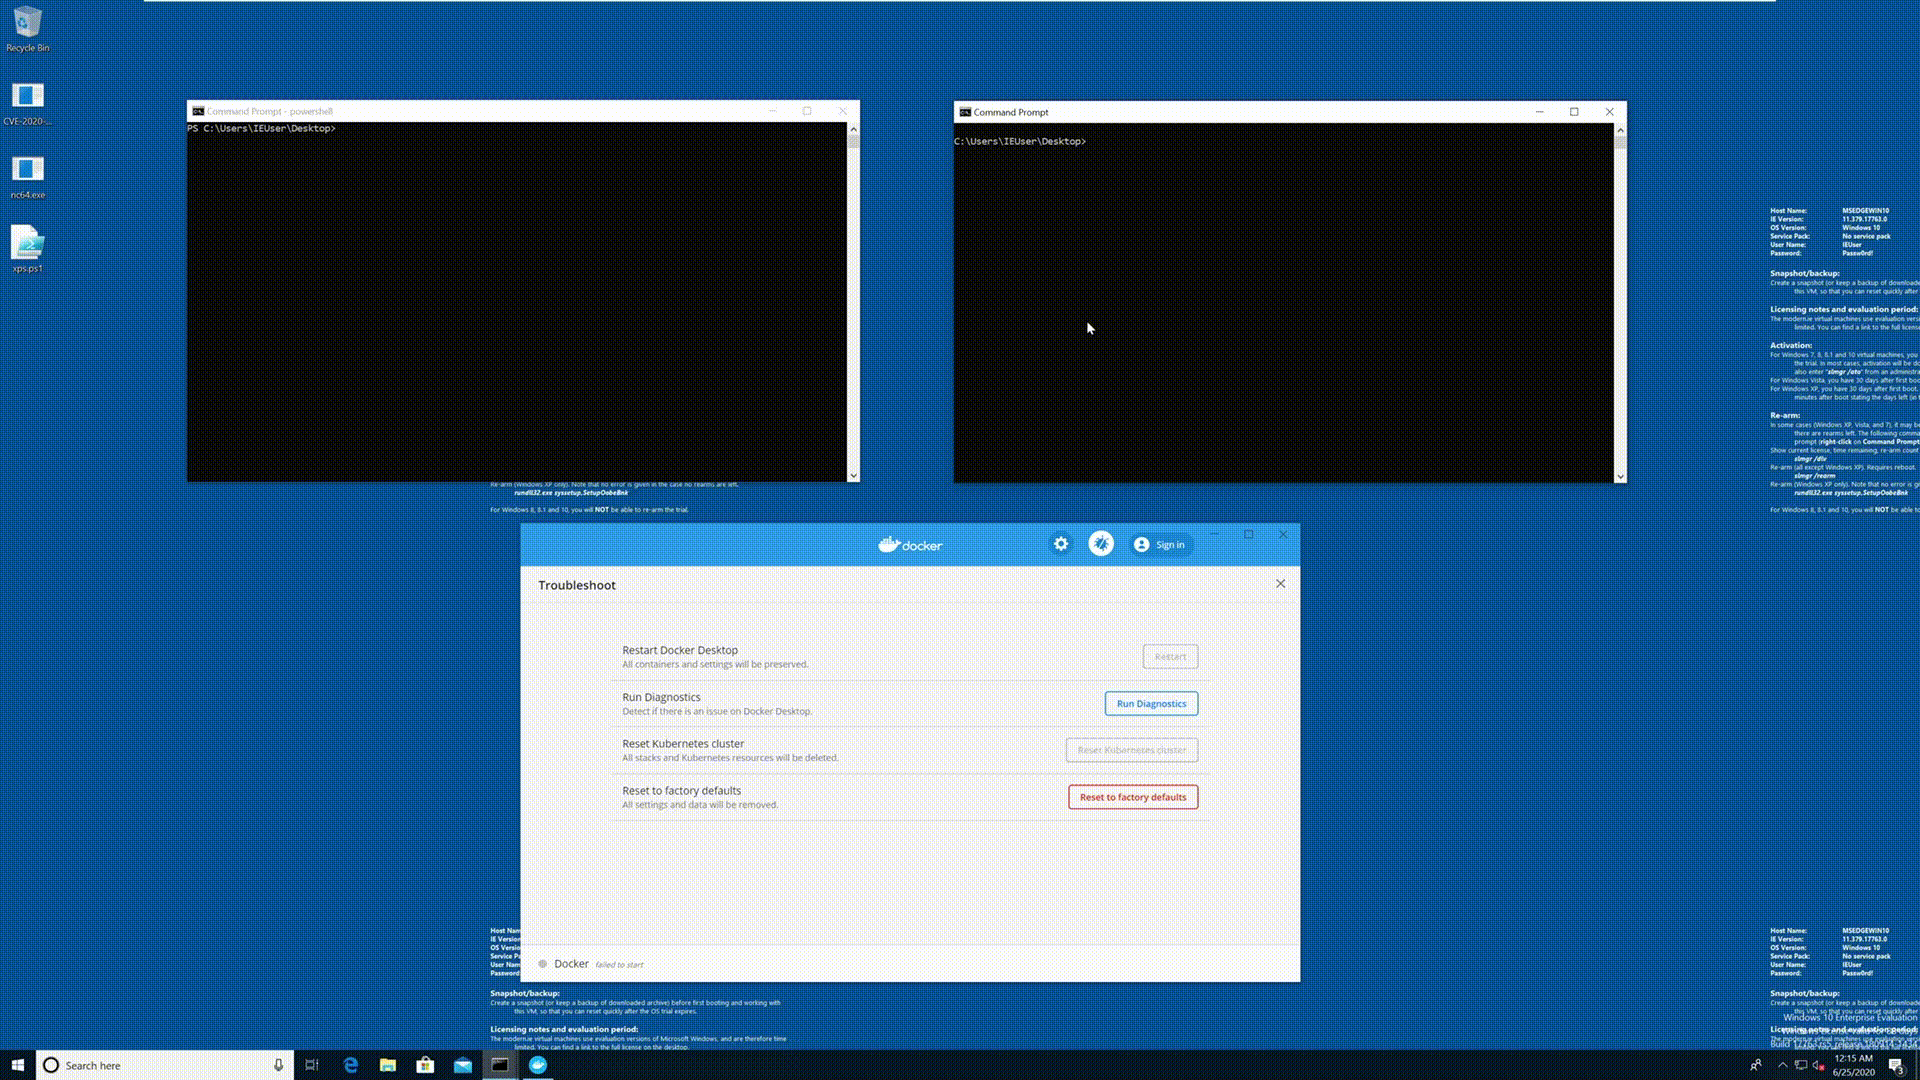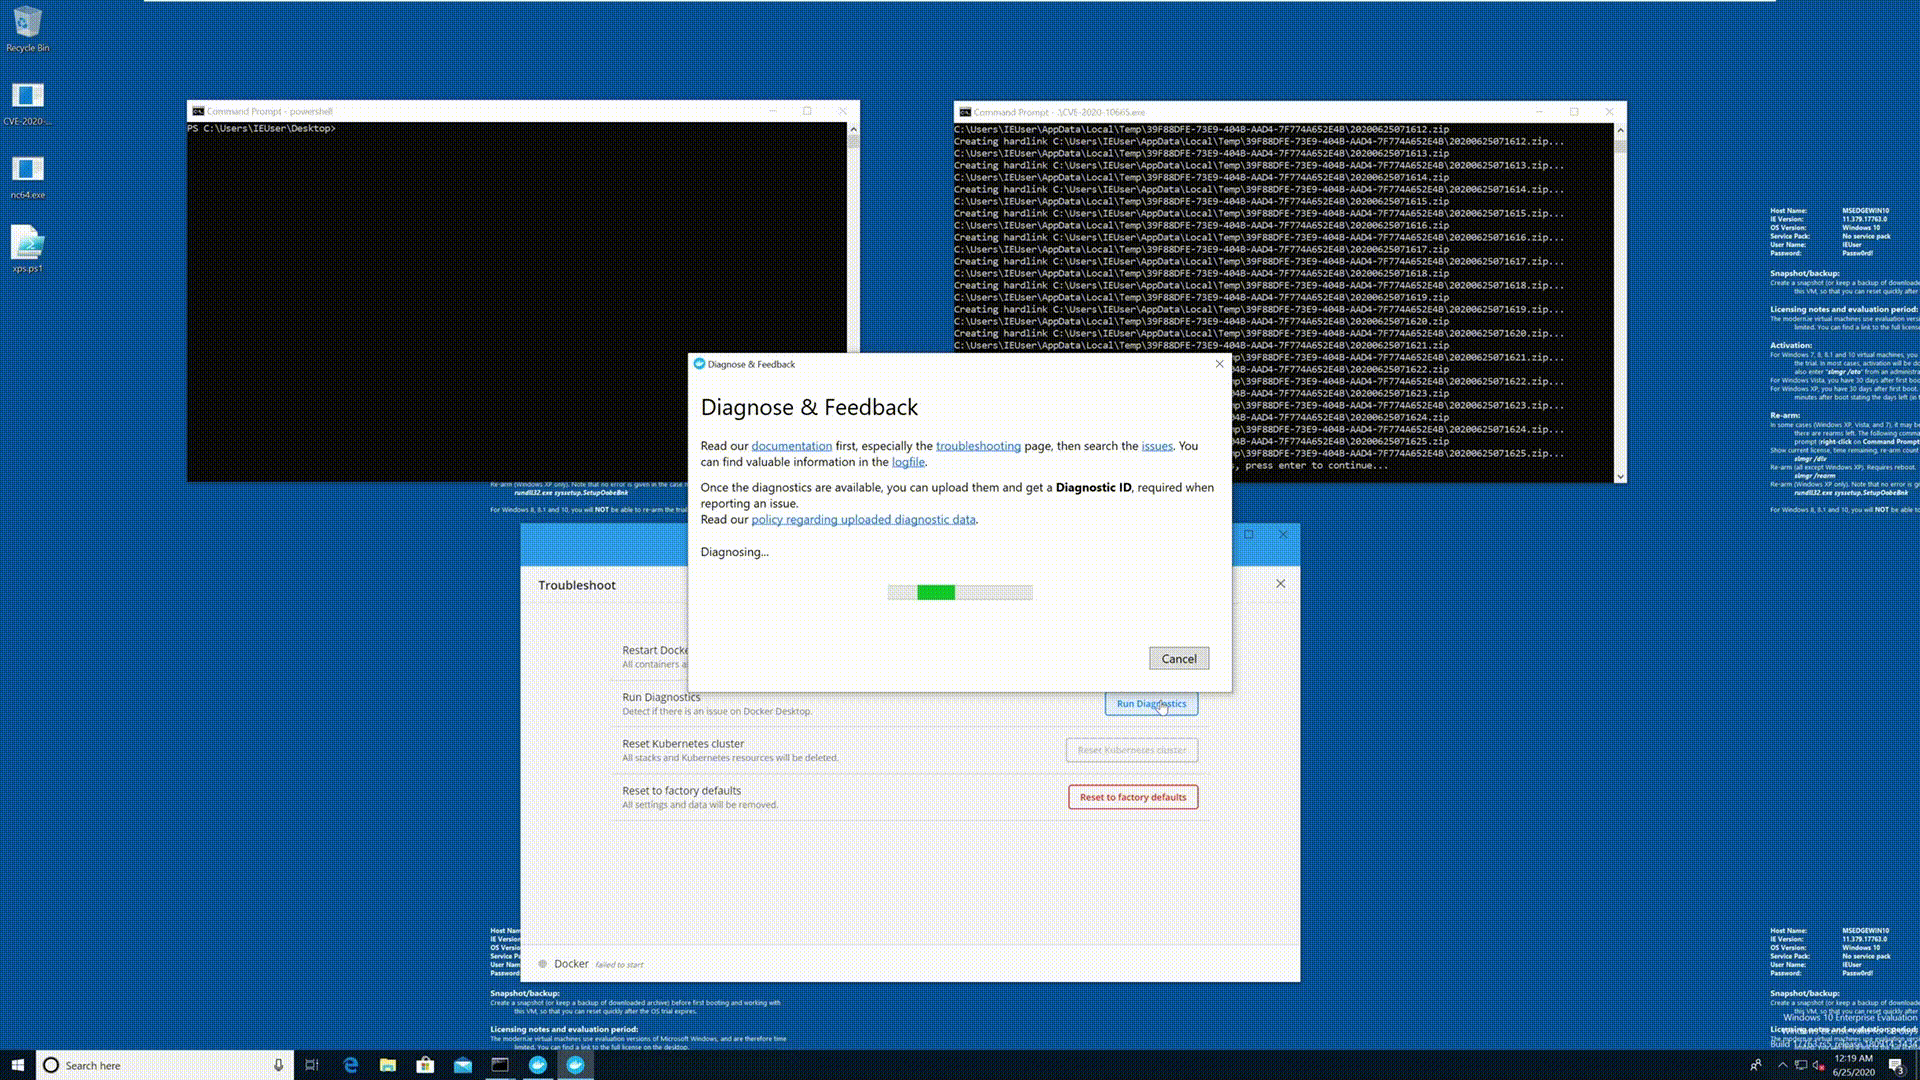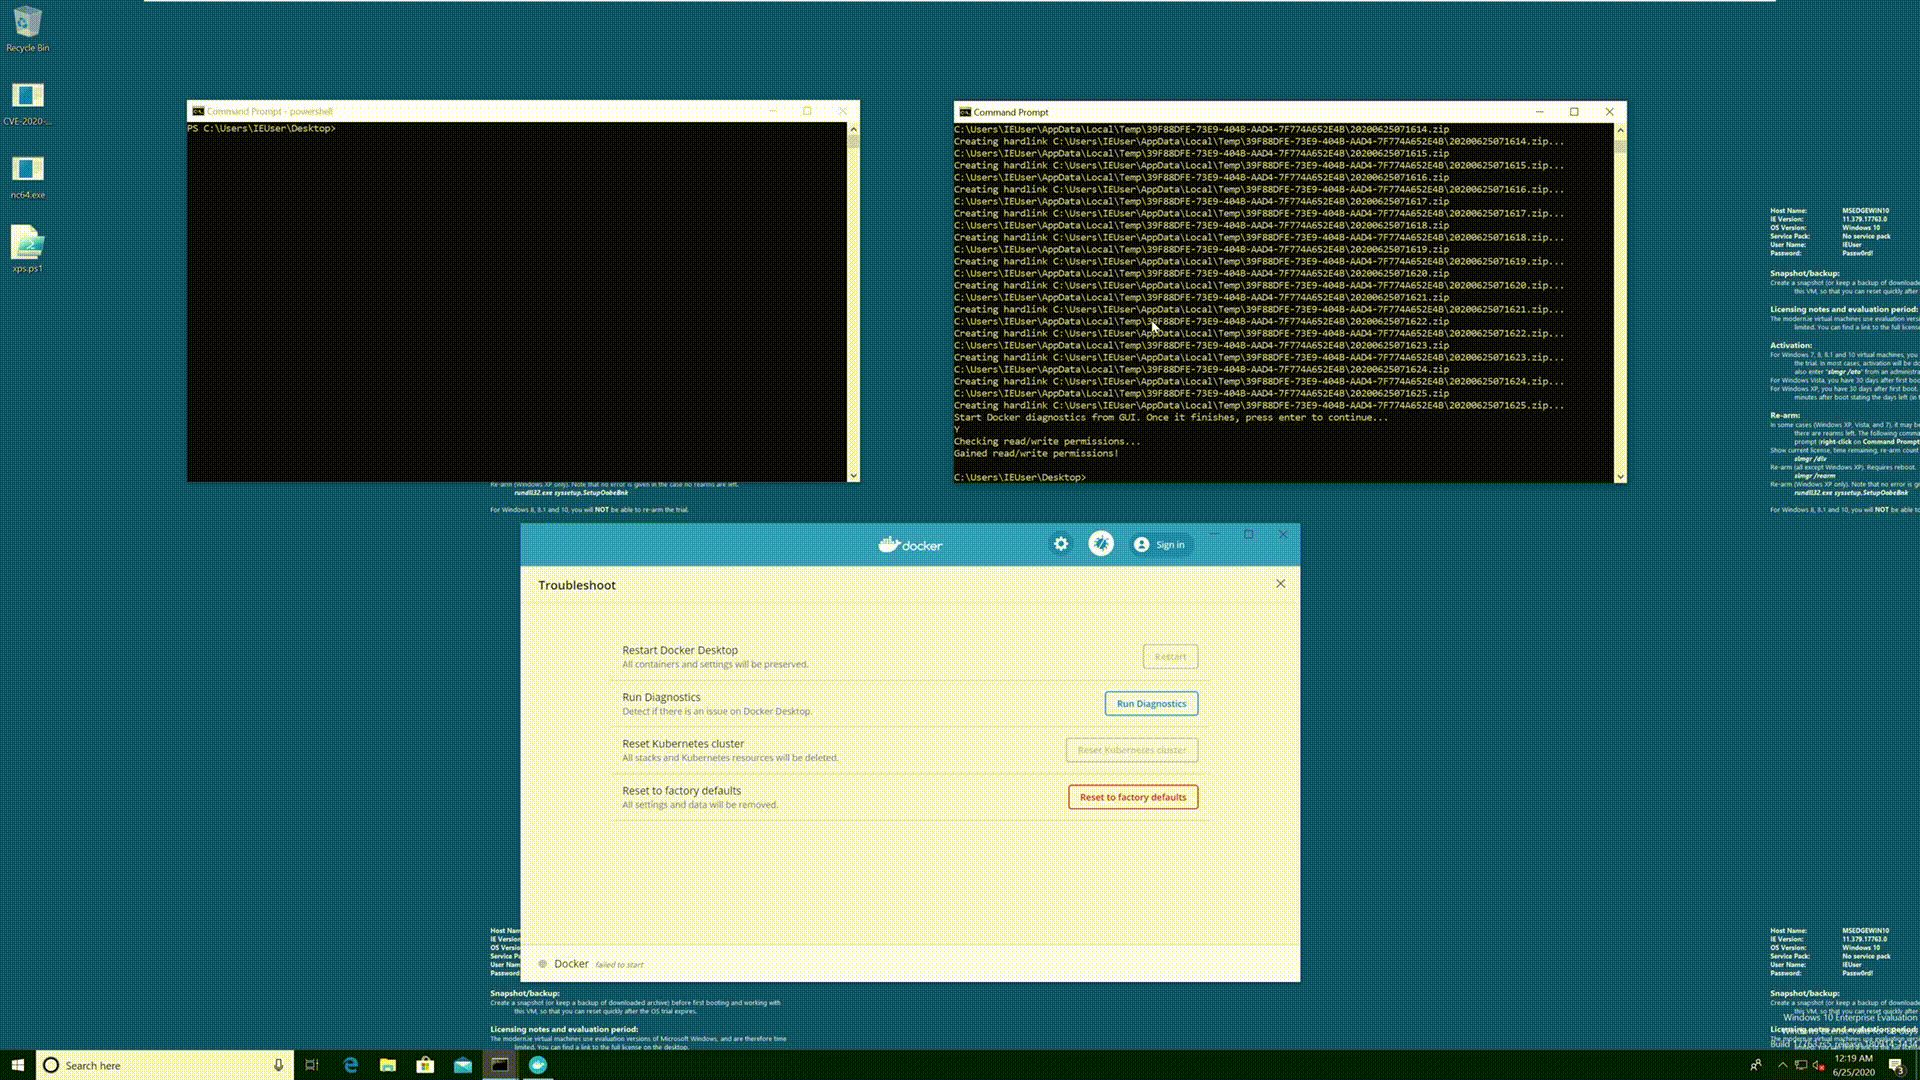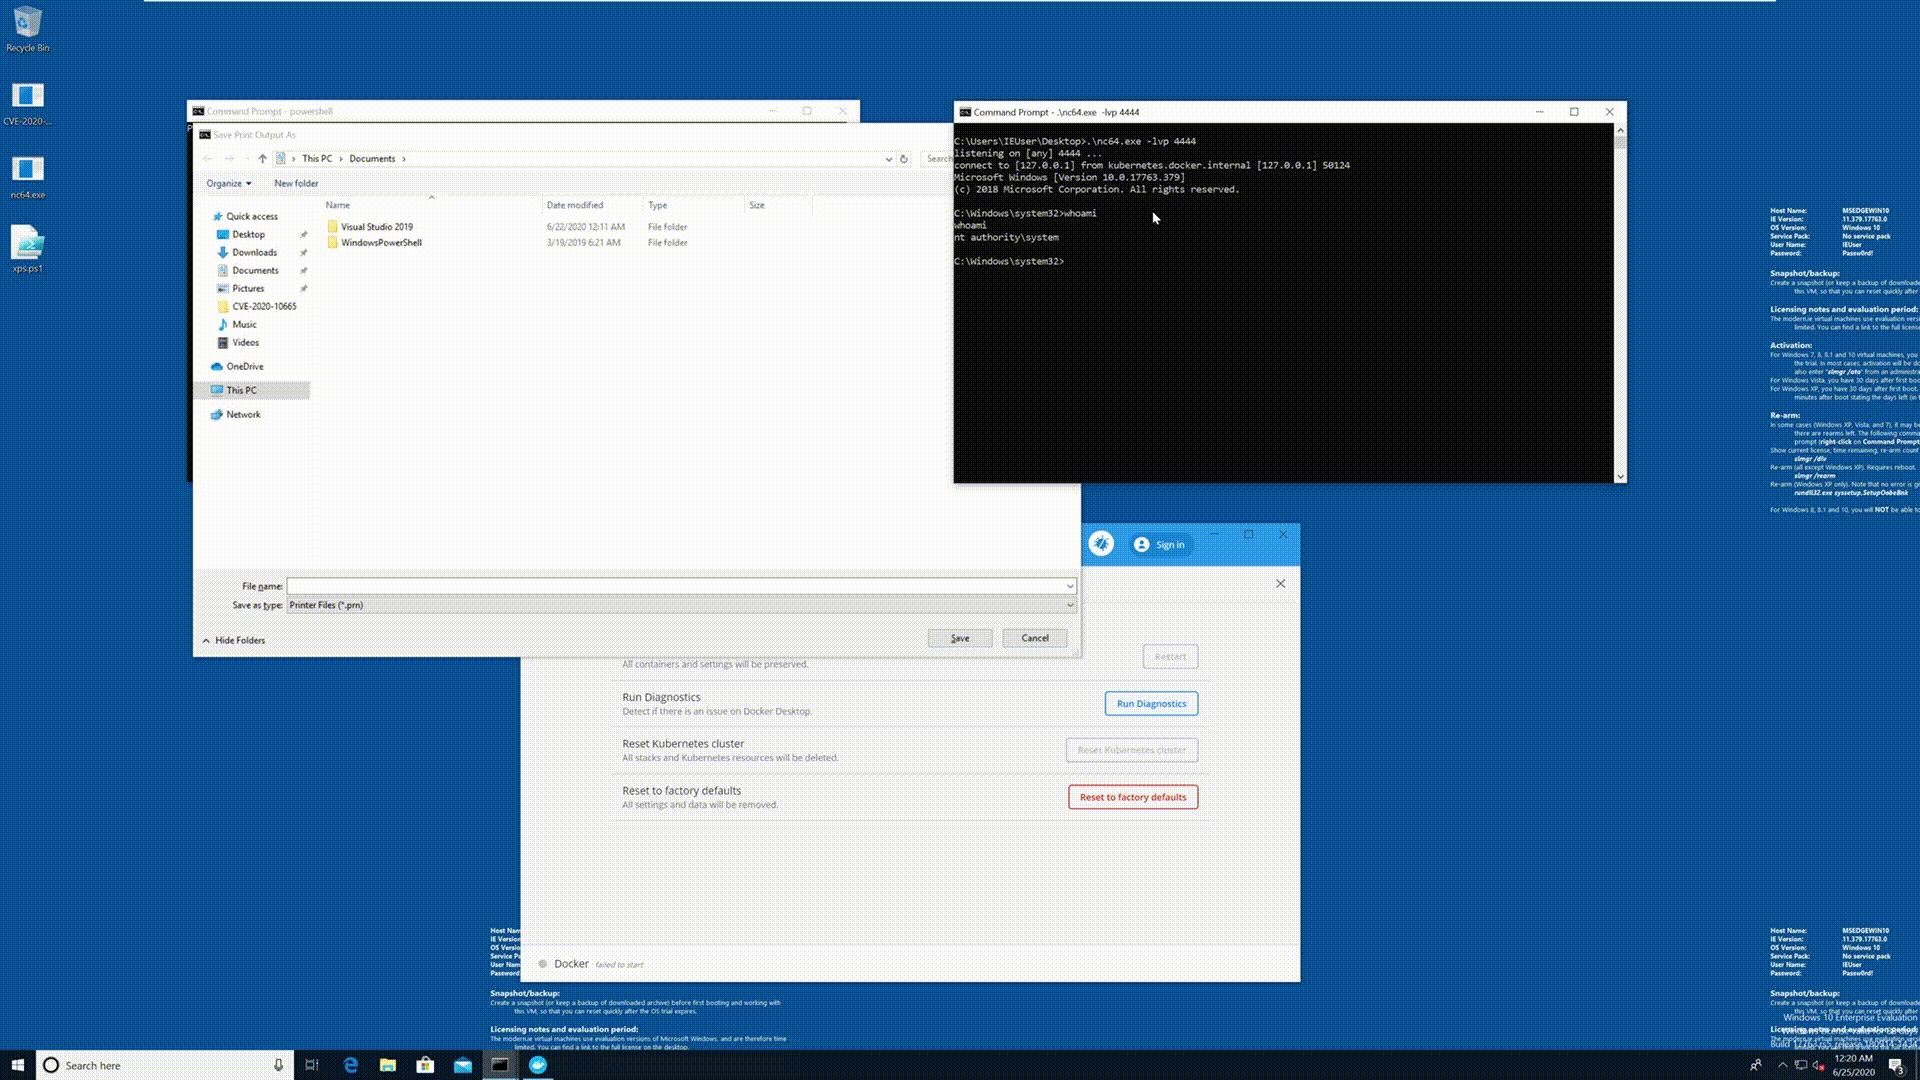 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 brumbelow/layerleak
layerleak the Docker Hub Secret Scanner