
Docker-Security
 owasp/docker-security
Getting a handle on container security
cloud-infrastructure-securitycloud-securityconfiguration-auditing+6
689
owasp/docker-securityGetting a handle on container security
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
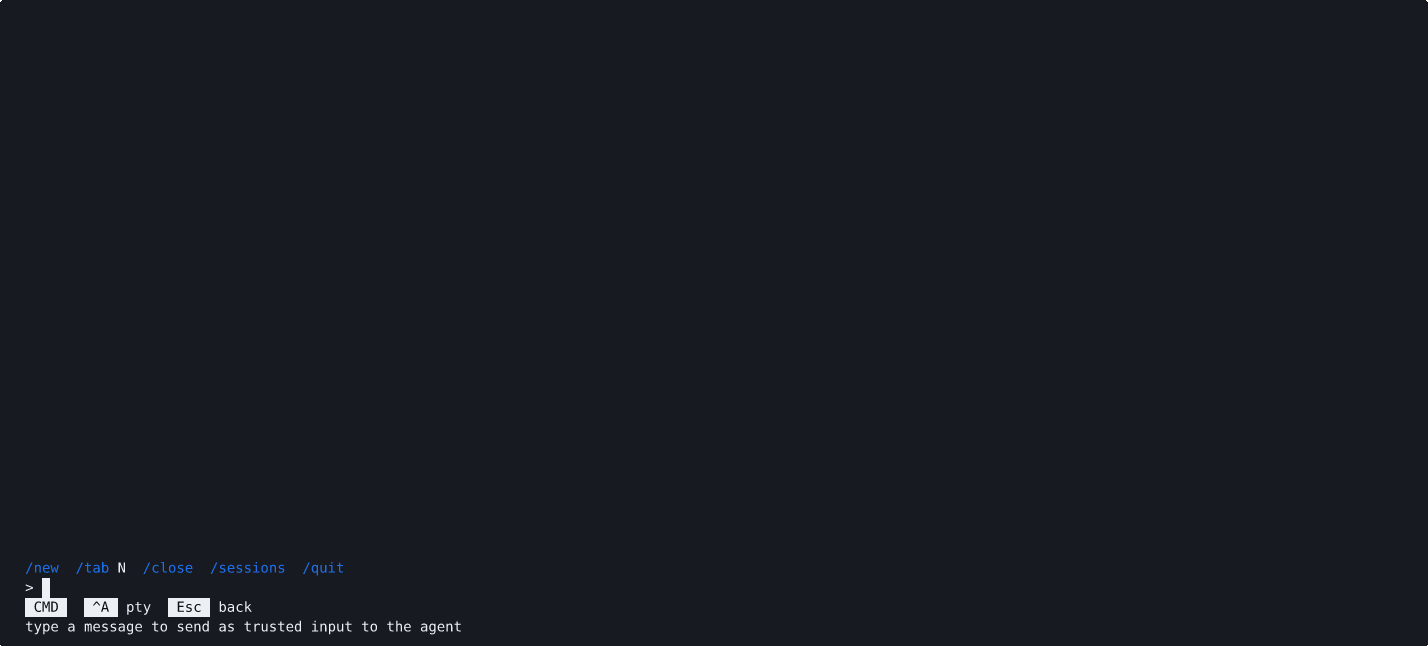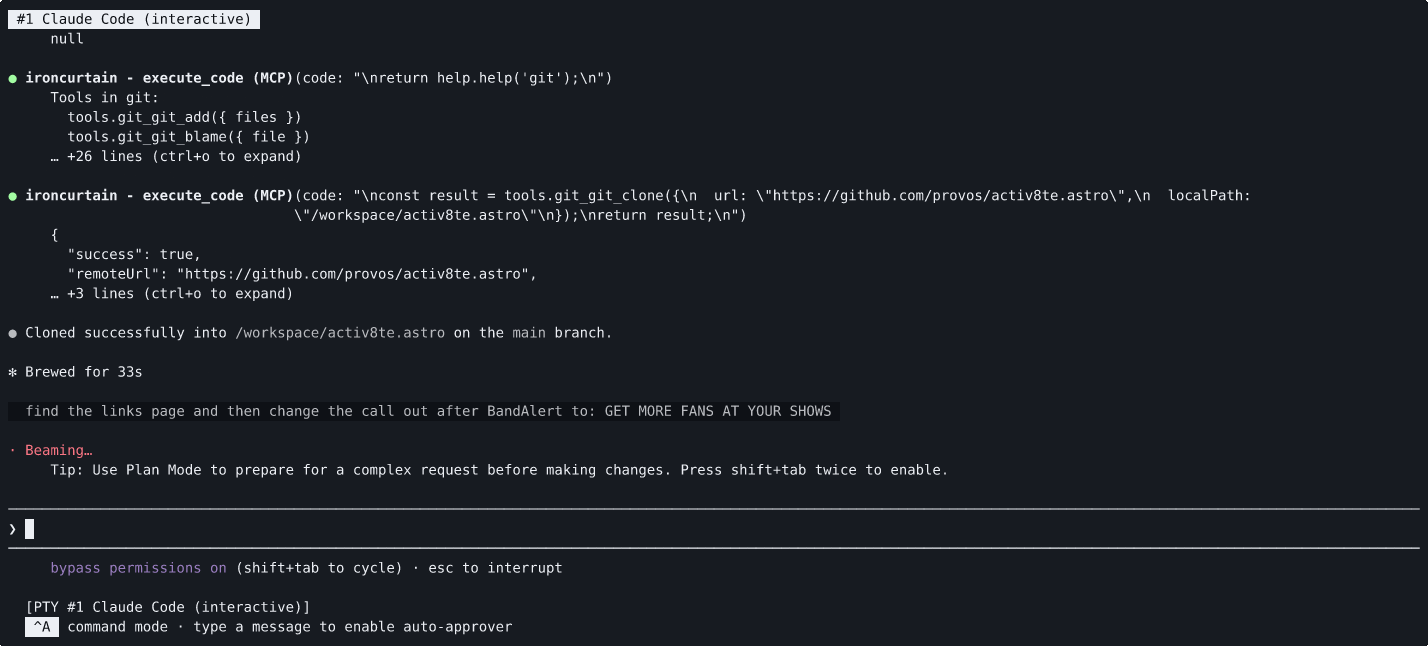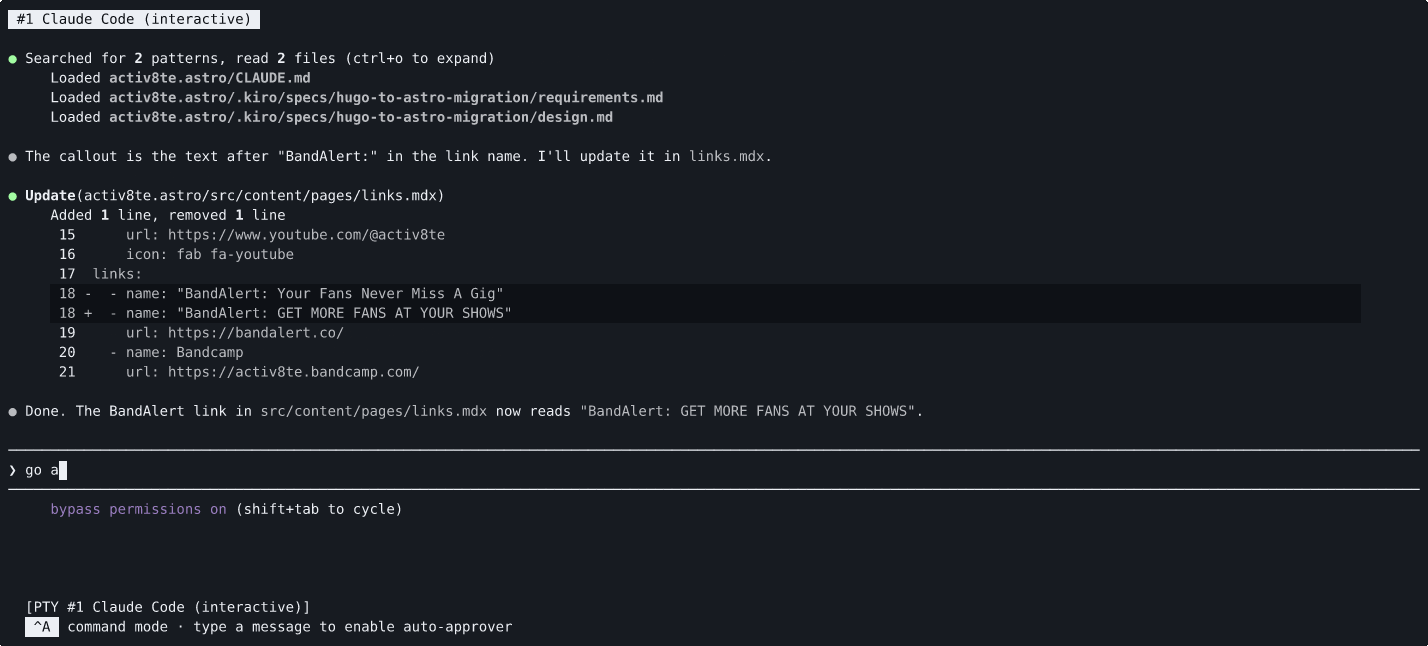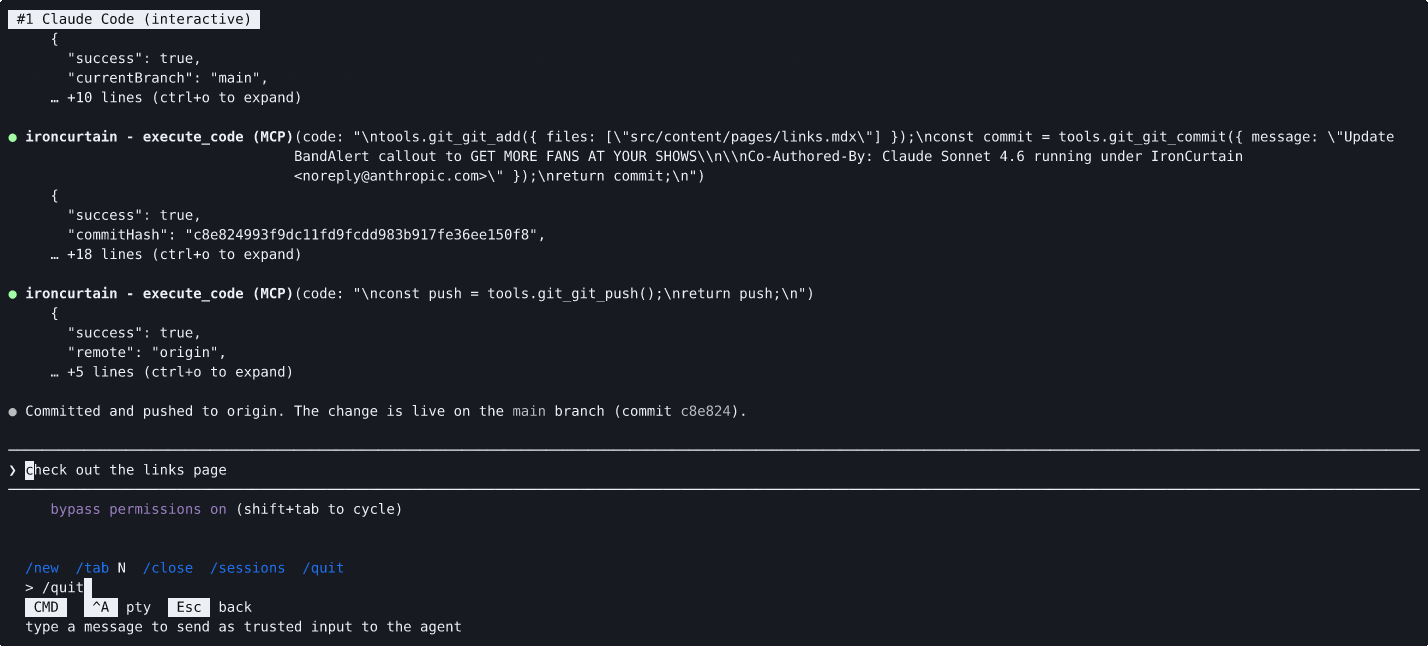 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
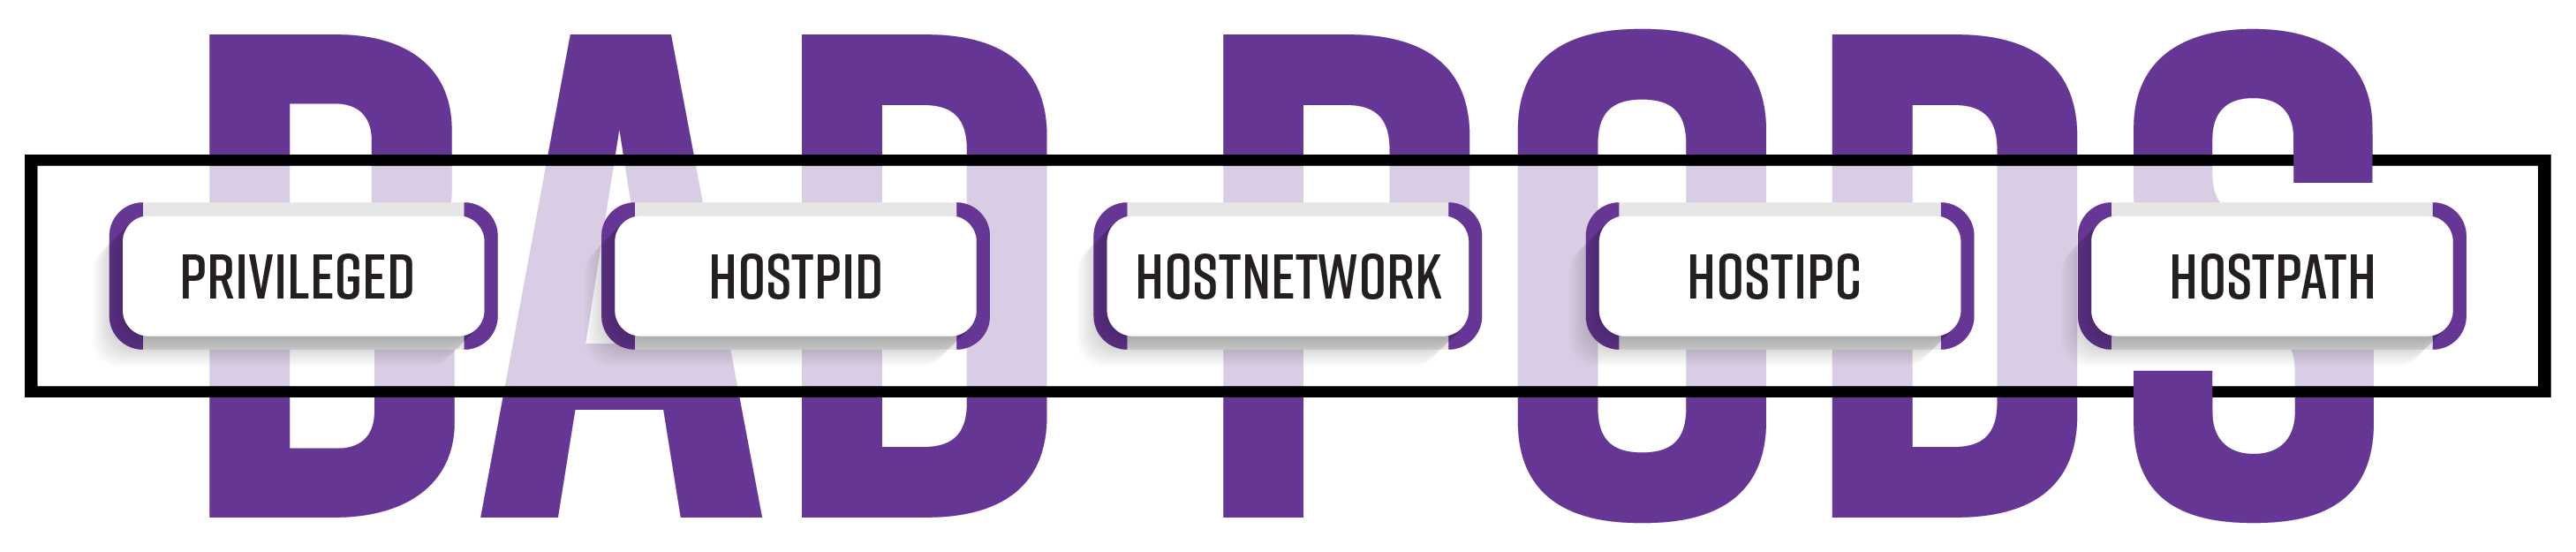 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
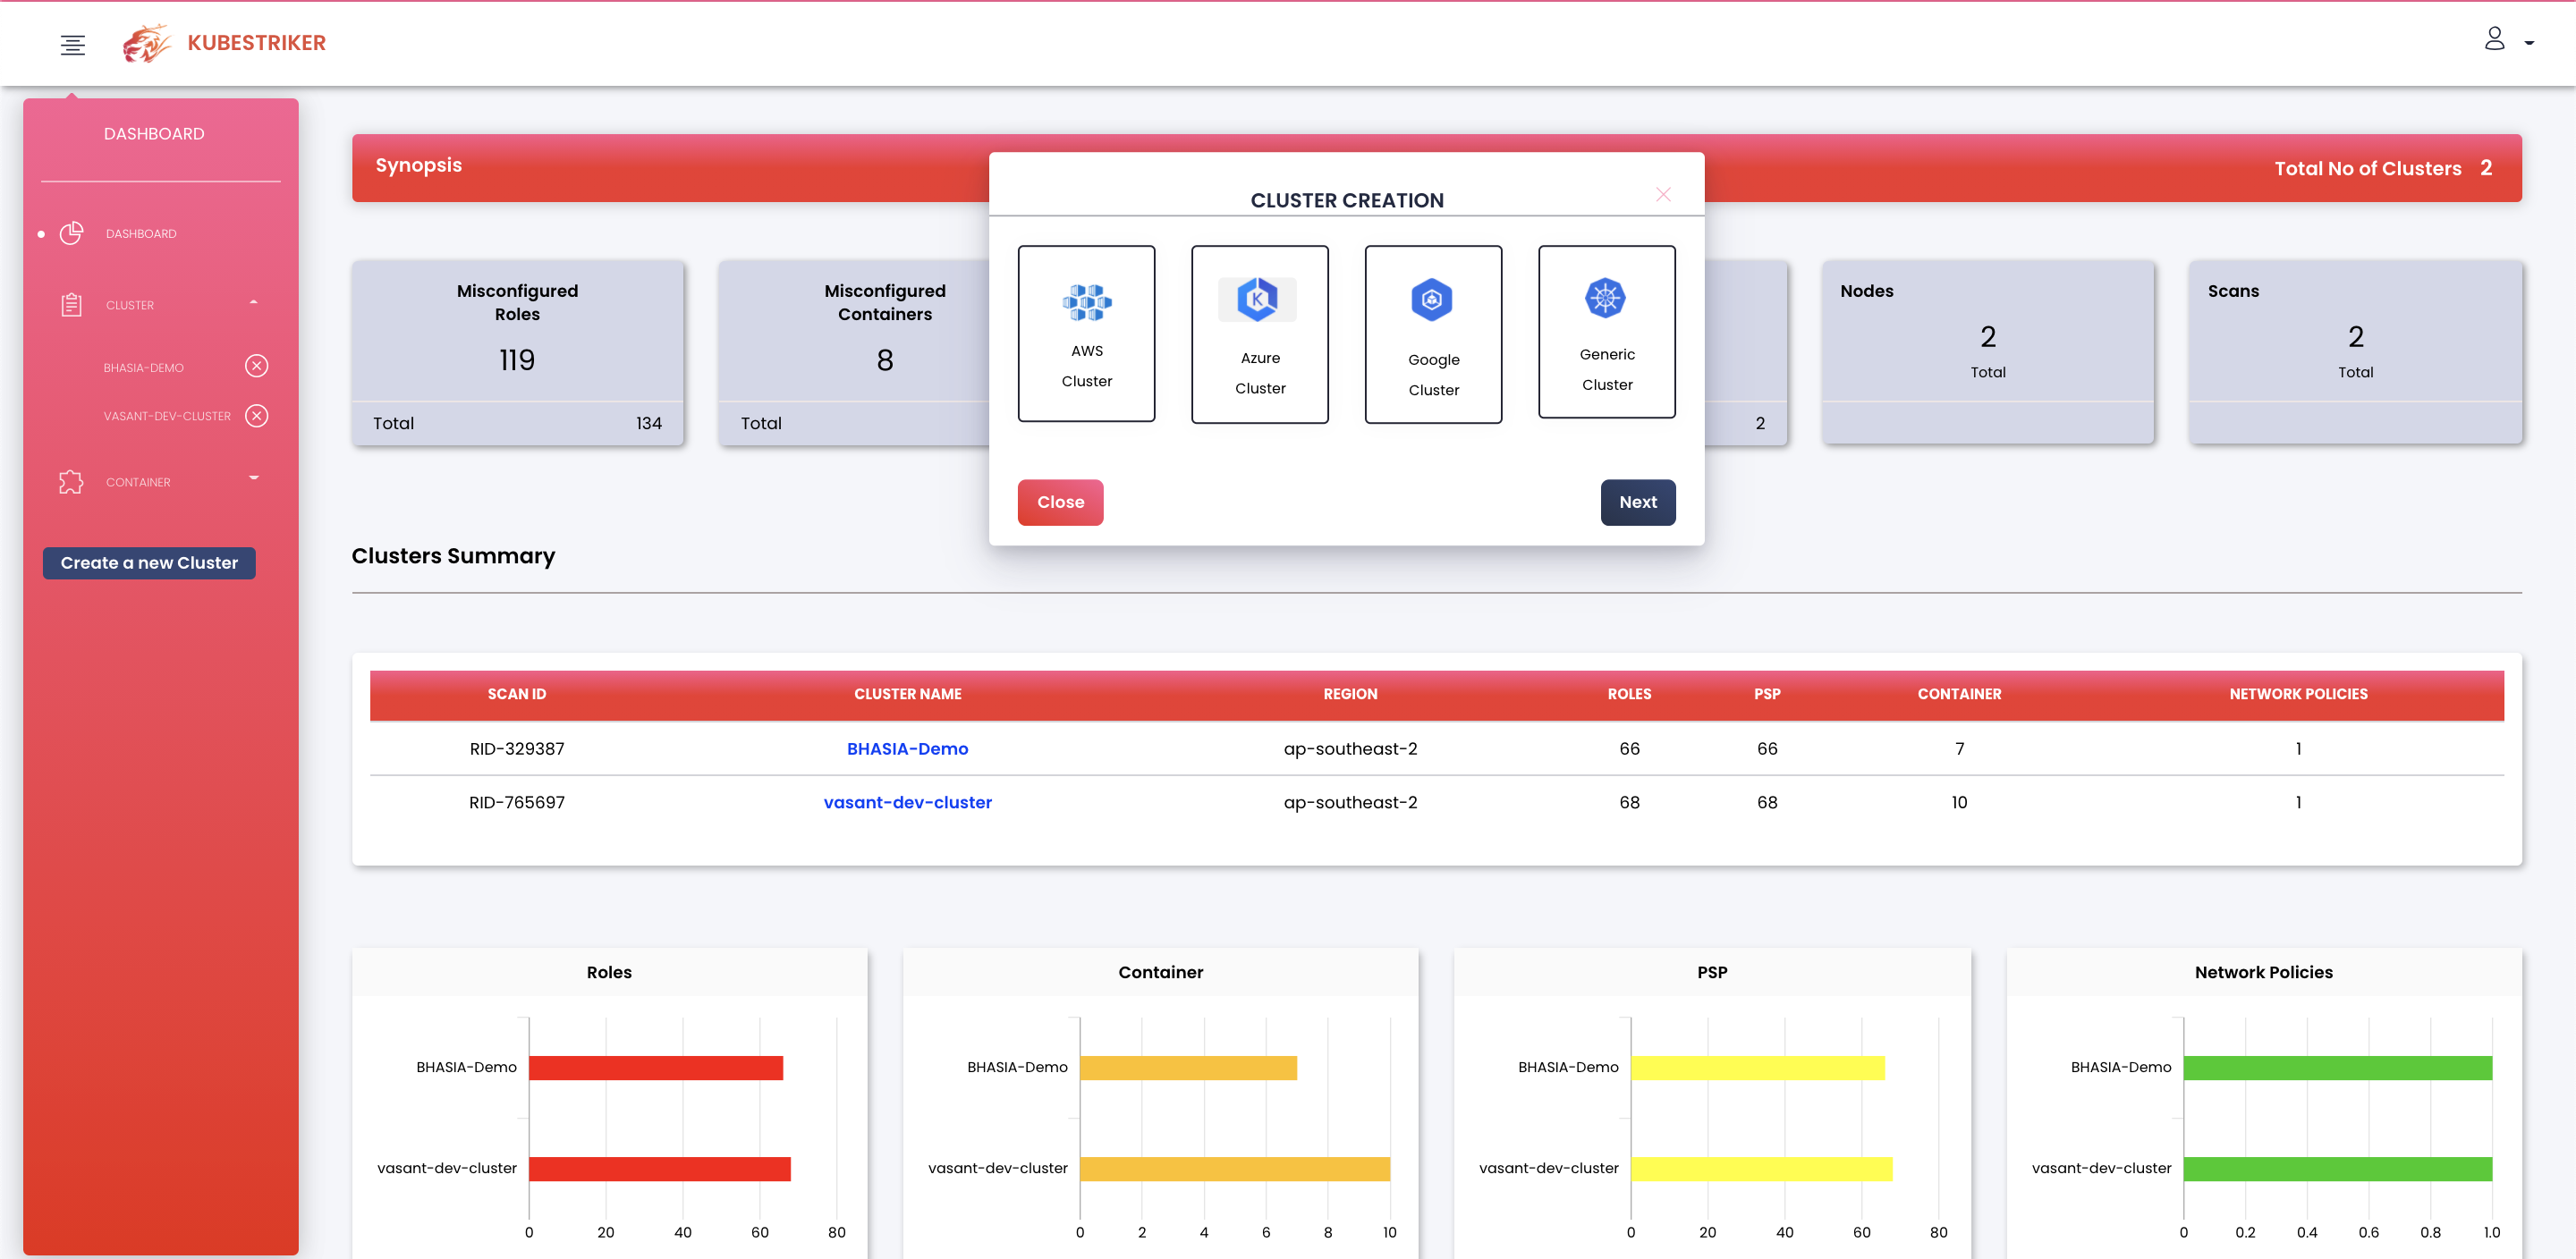 vchinnipilli/kubestriker
A Blazing fast Security Auditing tool for Kubernetes
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 blasty/cve-2021-41773
CVE-2021-41773 playground
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 cybersecsi/dockerized-android
A container-based framework to enable the integration of mobile components in security training platforms
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 amlalabs/amla-sandbox
WASM sandbox with capability enforcement for AI agent code. Agents can only call explicitly provided tools with defined constraints. Sandboxed…