Dirty-Frag-Research-CVE-2026-43284-

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…

Study on CVE-2020-13401 vulnerability of containers in dockers older than 19.03.11

Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…

Container escape on any docker container with healthcheck enabled via CVE-2026-31431

This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…

Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…

CVE: 2021-42013 Tested on: 2.4.49 and 2.4.50 Description: Path Traversal or Remote Code Execution vulnerabilities in Apache 2.4.49 and 2.4.50

Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.

CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…

CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…

Ansible playbooks to check and mitigate CVE-2026-31431 on Linux hosts, with scripts for local, remote, and containerized environments, including…

based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516

Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…

This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…

My view on IngressNightmare vulnerability (CVE-2025-1974)

A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…

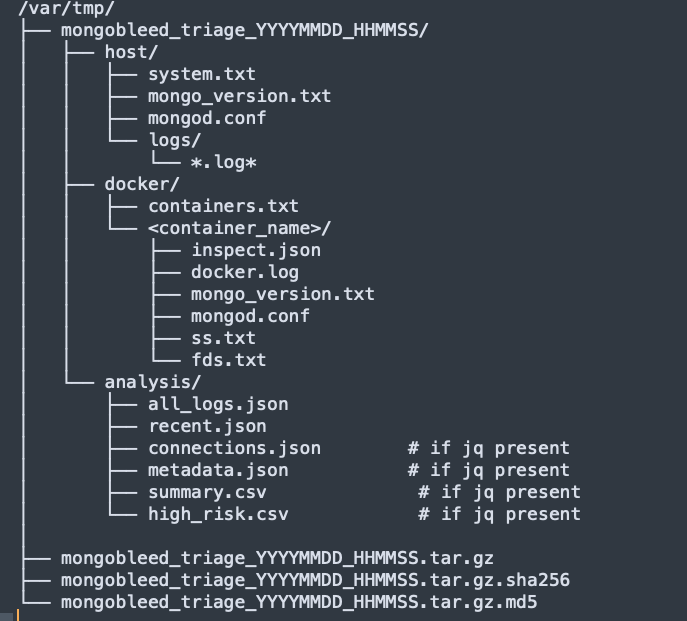
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC